
cve-2026-0300-audit
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
cloud-infrastructure-securityconfiguration-auditingdevsecops+3
tailwindrg/cve-2026-0300-auditRead-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
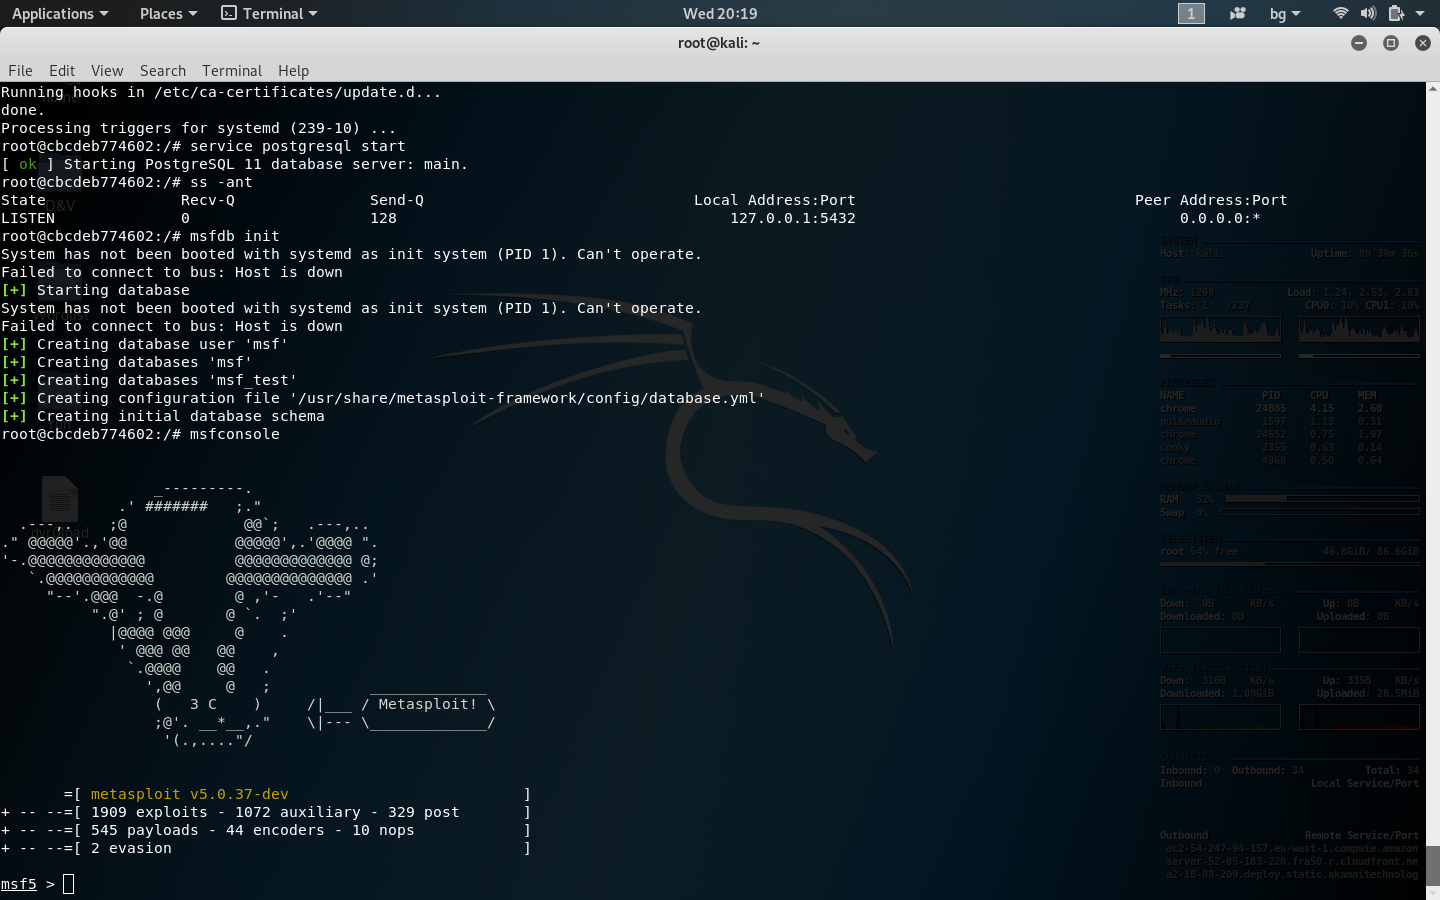 nu11secur1ty/kali-linux-docker
kali-linux-docker
 dolutech/patch-manual-cve-2025-26465-e-cve-2025-26466
Patch Manual para a correção das CVE-2025-26465-e-CVE-2025-26466, para sistemas sem update do OpenSSH
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
 nrnw/cve-2026-24061-gnu-inetutils-telnet-detector
A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations
 p4x1s/ansible-cve-2023-36845
Ansible Playbook for CVE-2023-36845(Juniper Networks Junos OS 远程代码执行漏洞)
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
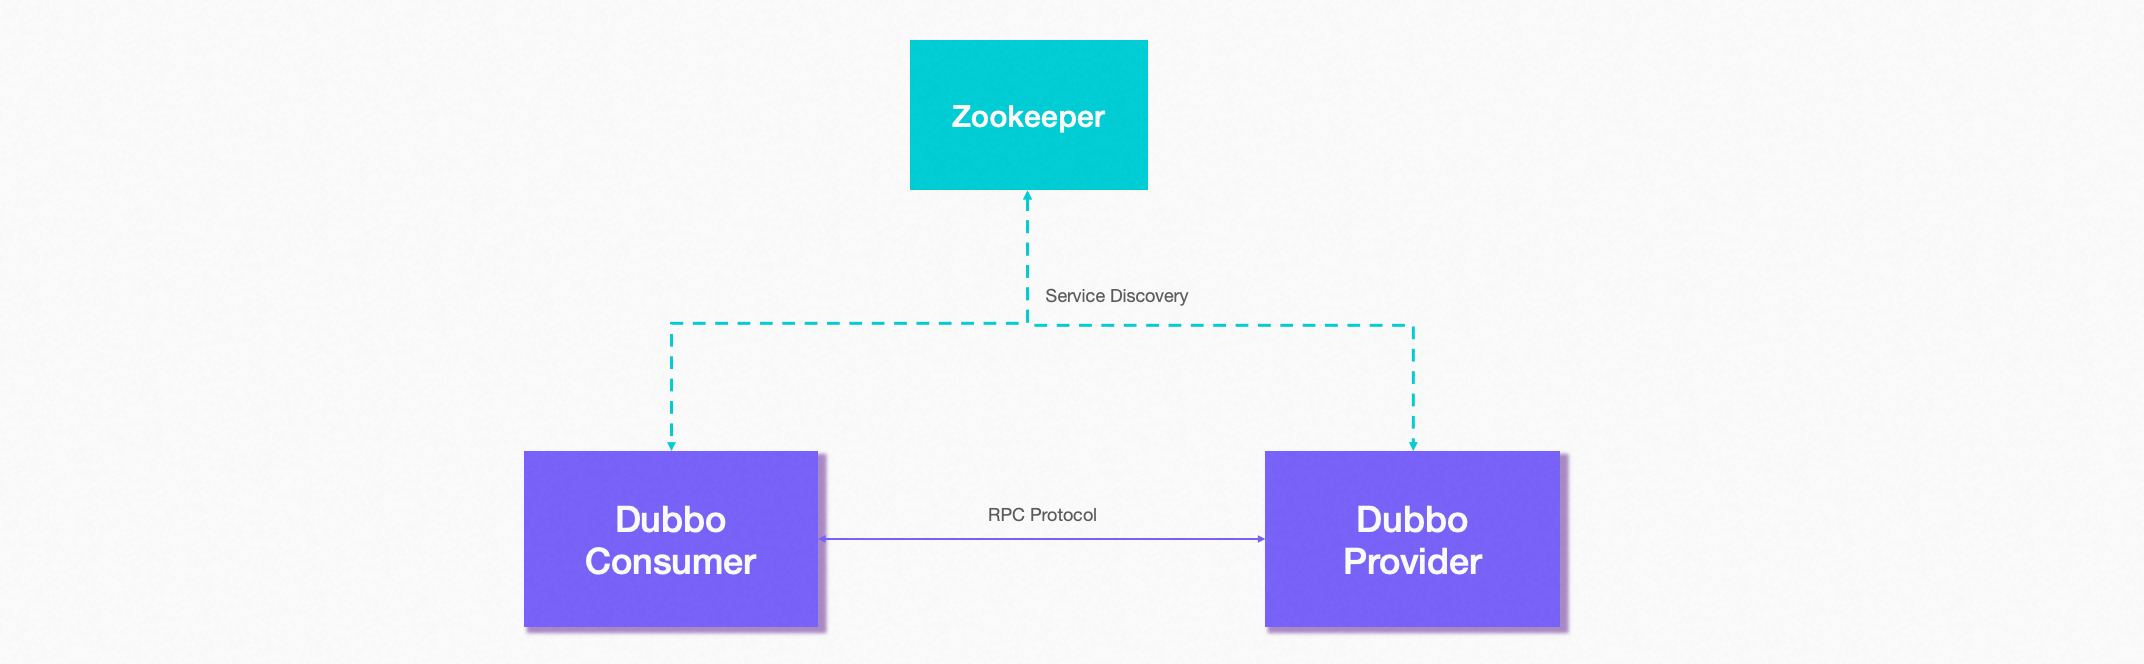 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
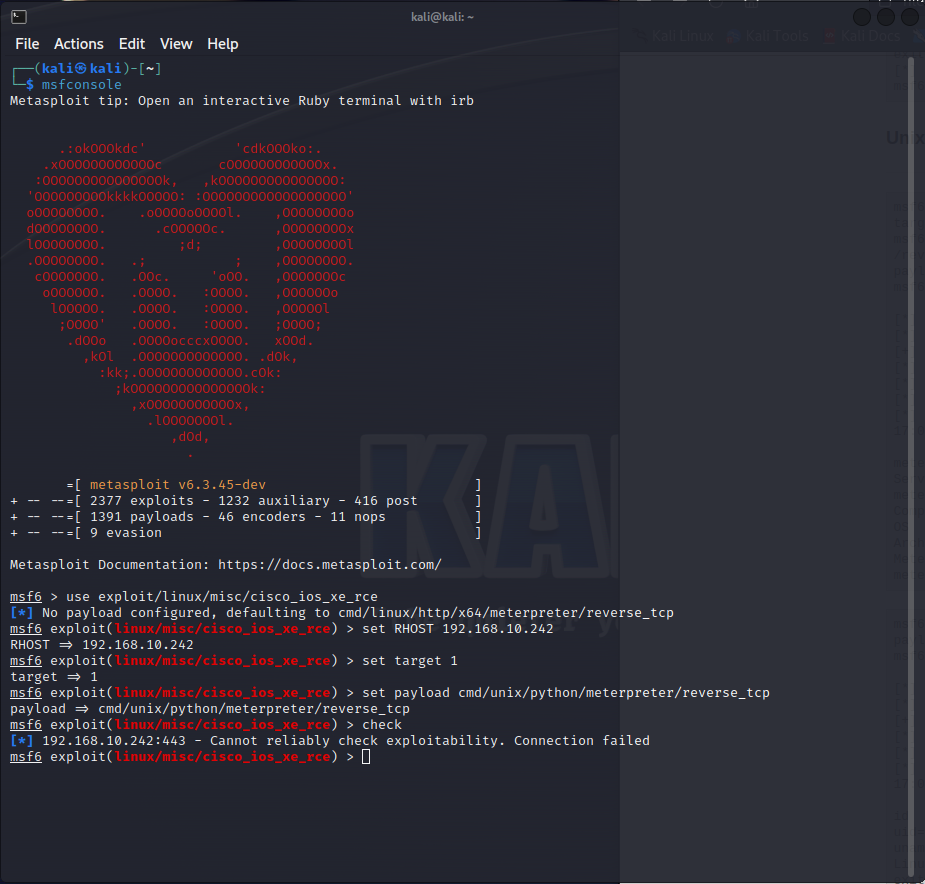 netbell/cve-2023-20198-fix
Check for and remediate conditions that make an IOS-XE device vulnerable to CVE-2023-20198
 zenzue/cve-2024-6387-mitigation
Mitigation Guide for CVE-2024-6387 in OpenSSH
 teedeedubya/bash-fix-exploit
Ansible role to check the CVE-2014-6271 vulnerability
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.