
raven
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
code-analysisdevsecopseducation+3
7461 year ago
cycodelabs/ravenScans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 mhaggis/package-inferno
A Public Package Scanner for The Community
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)

 skyscanner/whispers
Identify hardcoded secrets in static structured text
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
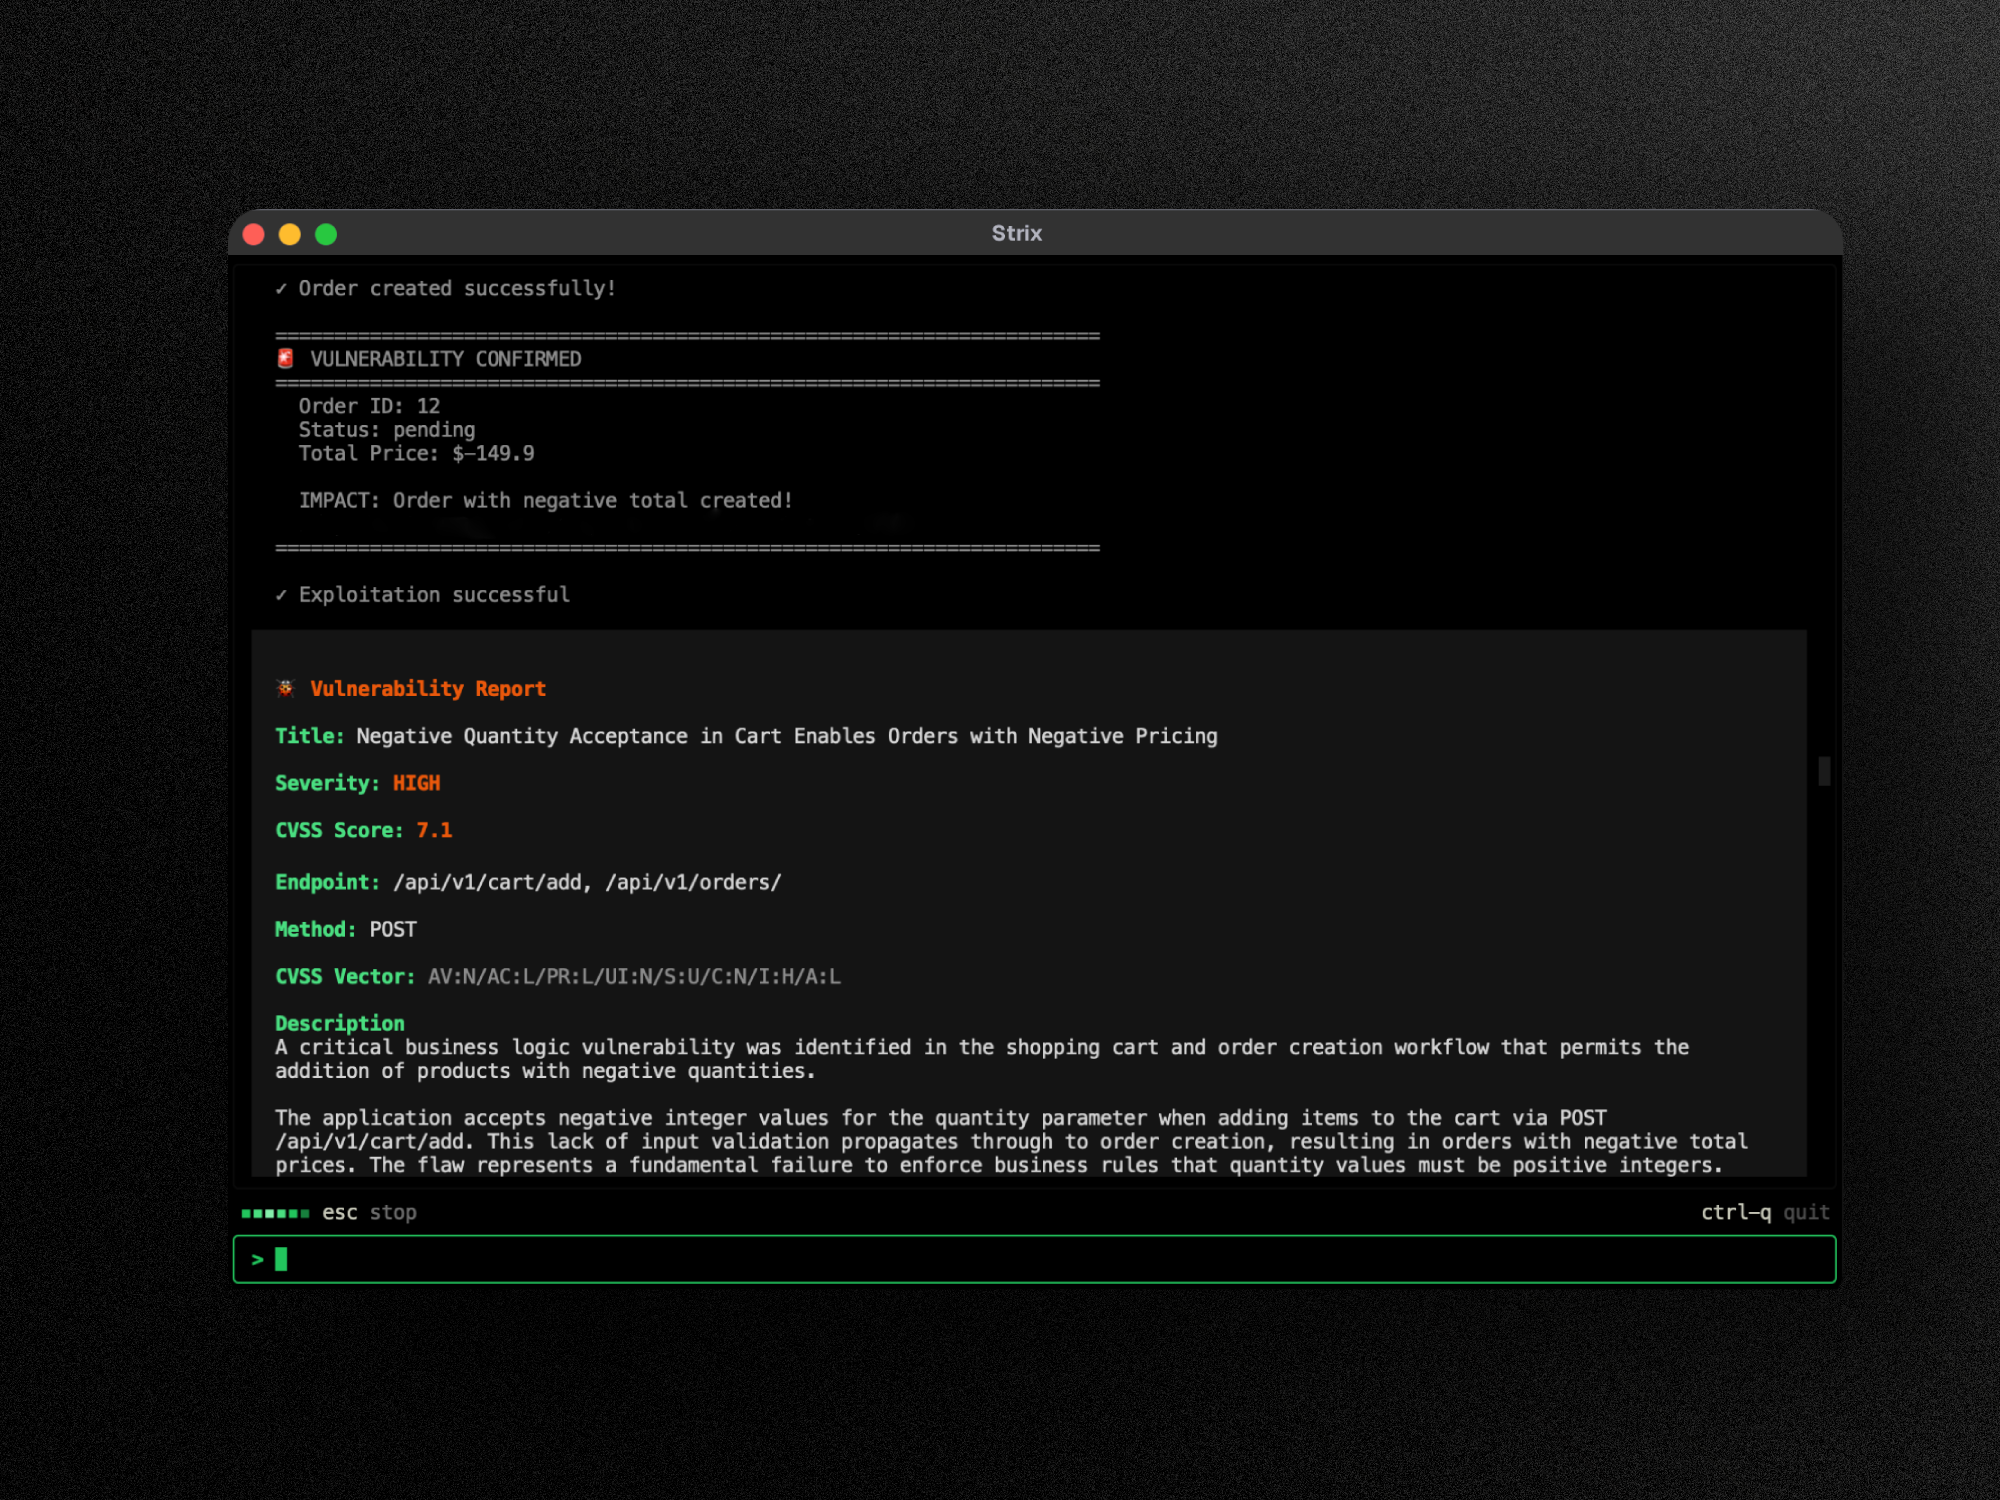 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 shieldfy/api-security-checklist
Checklist of the most important security countermeasures when designing, testing, and releasing your API
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…