jenkinsci__workflow-cps-plugin_CVE-2022-25173_2646-v6ed3b5b01ff1

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.

Remediation task for CVE-2018-15686, CVE-2018-16866, and CVE-2018-16888 affecting SystemD in EL7

CVE-2021-44228 log4j mitigation using aws wafv2 with ansible

Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.

Stage two containers

Workaround for disabling the CLI to mitigate SECURITY-3314/CVE-2024-23897 and SECURITY-3315/CVE-2024-23898

A service that analyzes docker images and scans for vulnerabilities

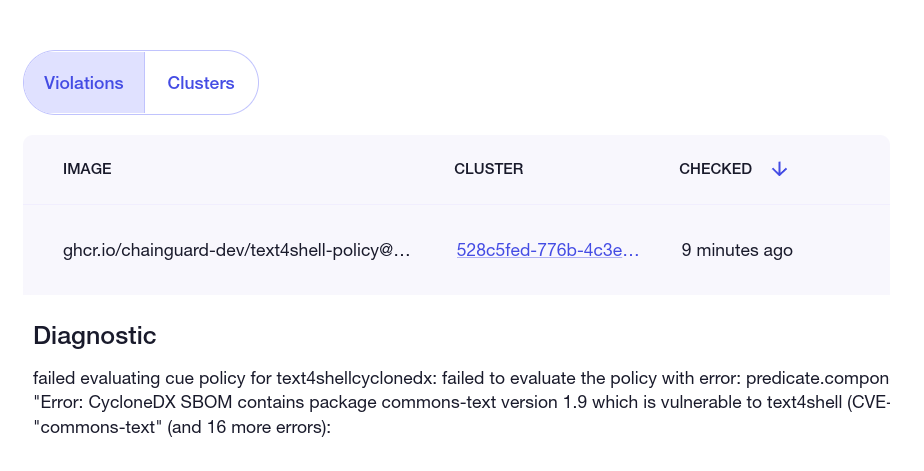
ClusterImagePolicy demo for cve-2022-42889 text4shell

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Static code analysis plugin for Android project. (Checkstyle, PMD)

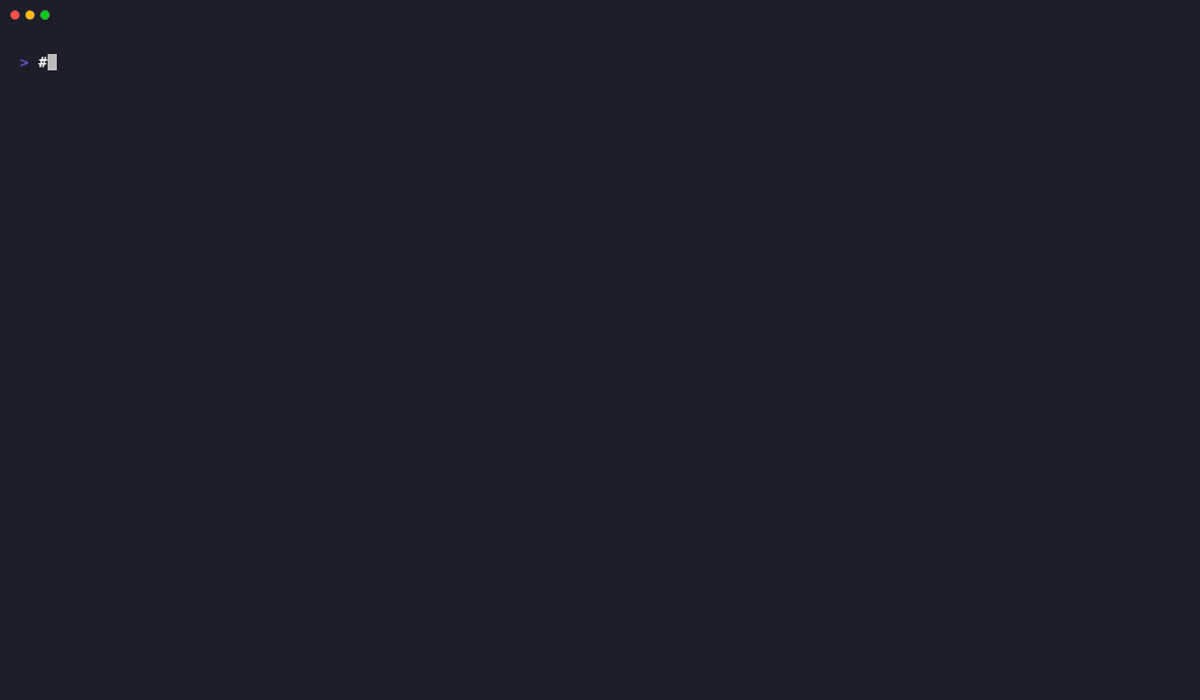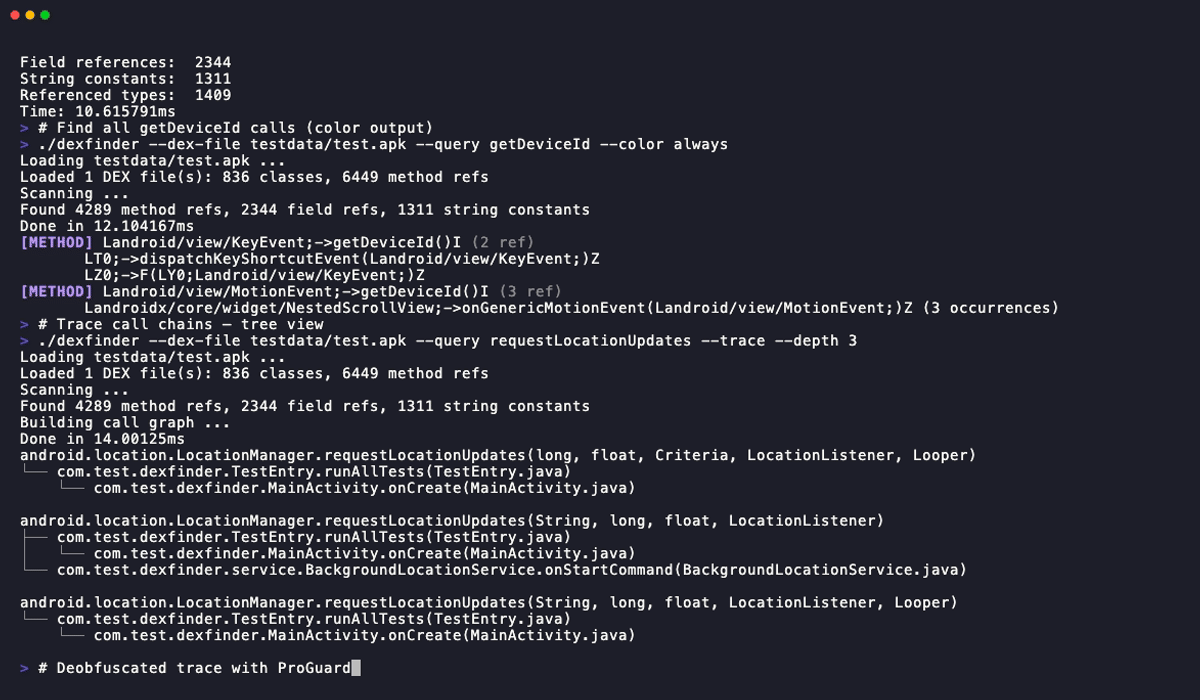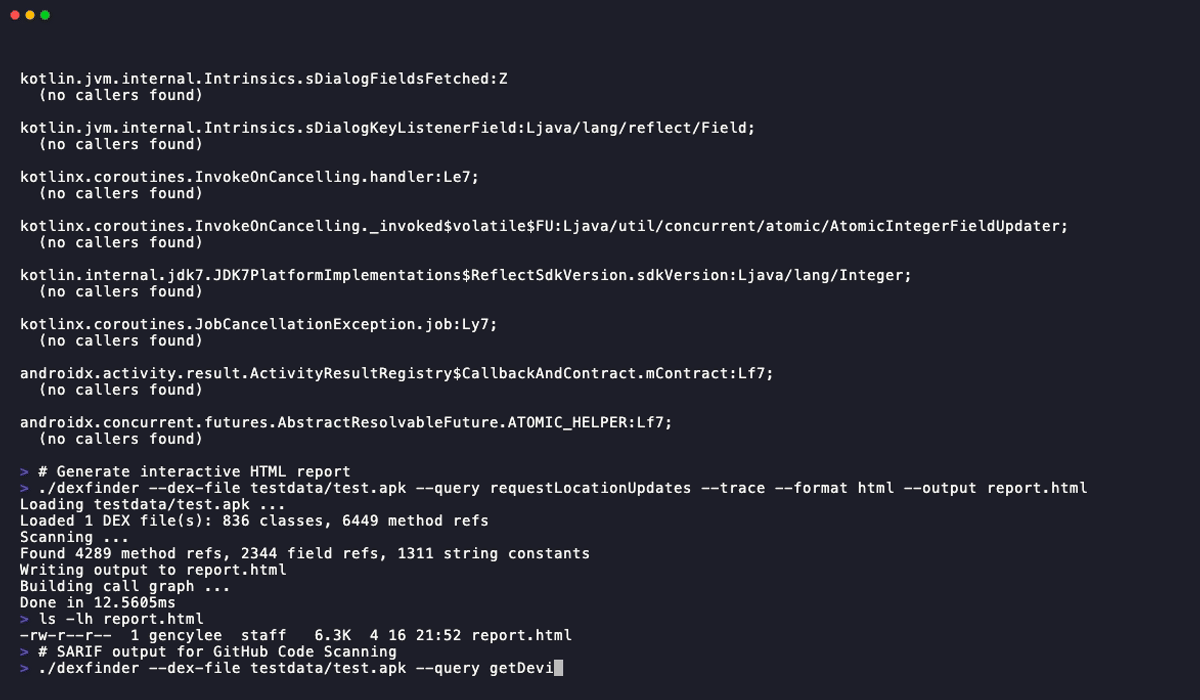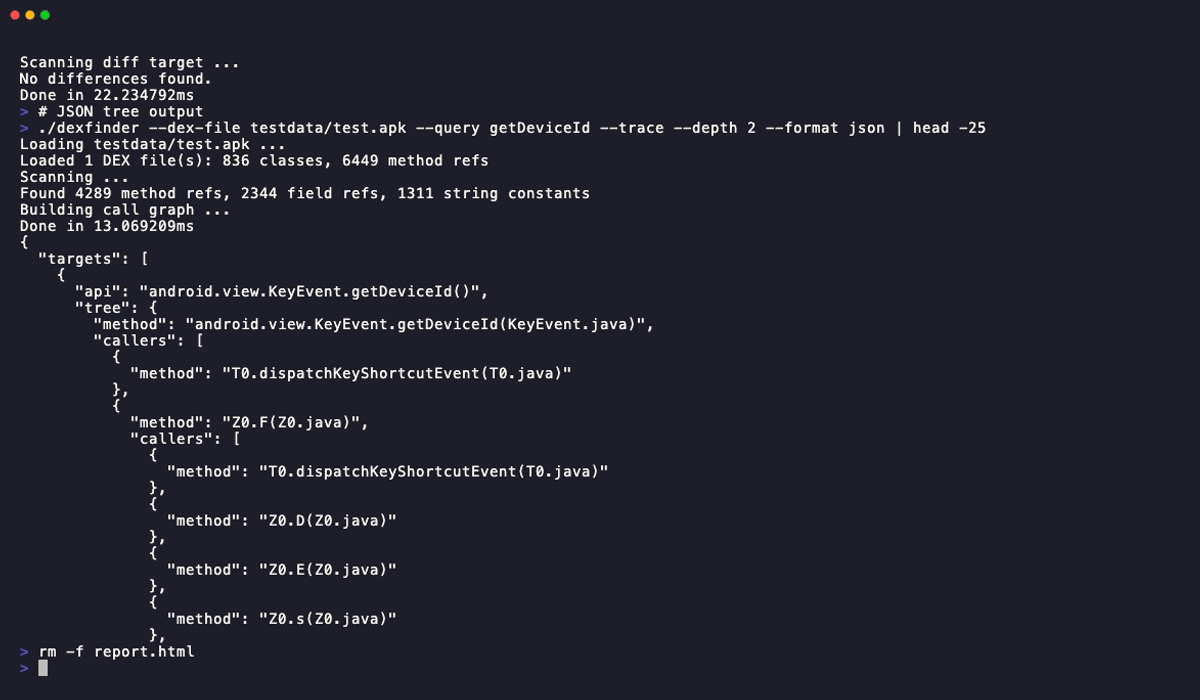
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection

Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…

Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı

Easy setup of static analysis tools for Android and Java projects.