
dotenv-diff
 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
code-analysisconfiguration-auditingdevsecops+3
chrilleweb/dotenv-diffValidate environment variable usage in codebase
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
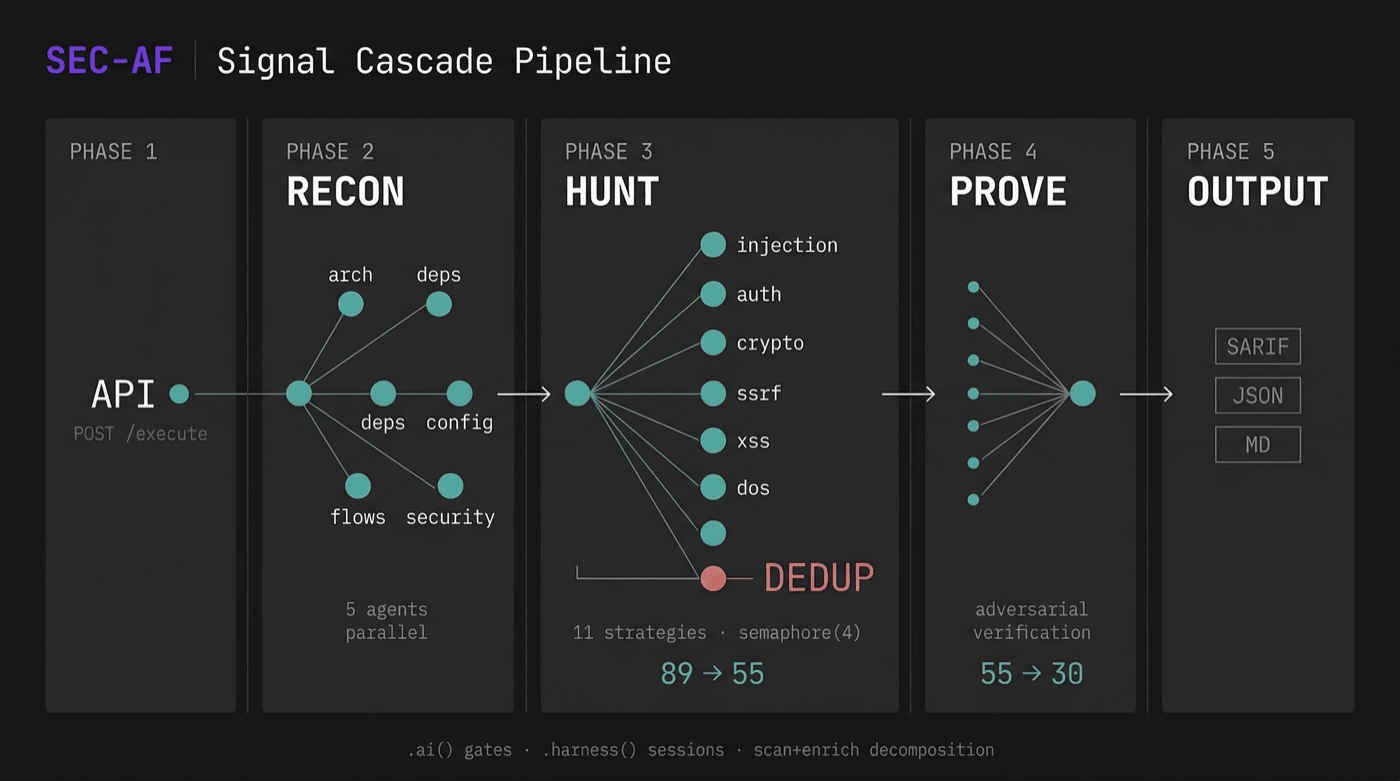 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
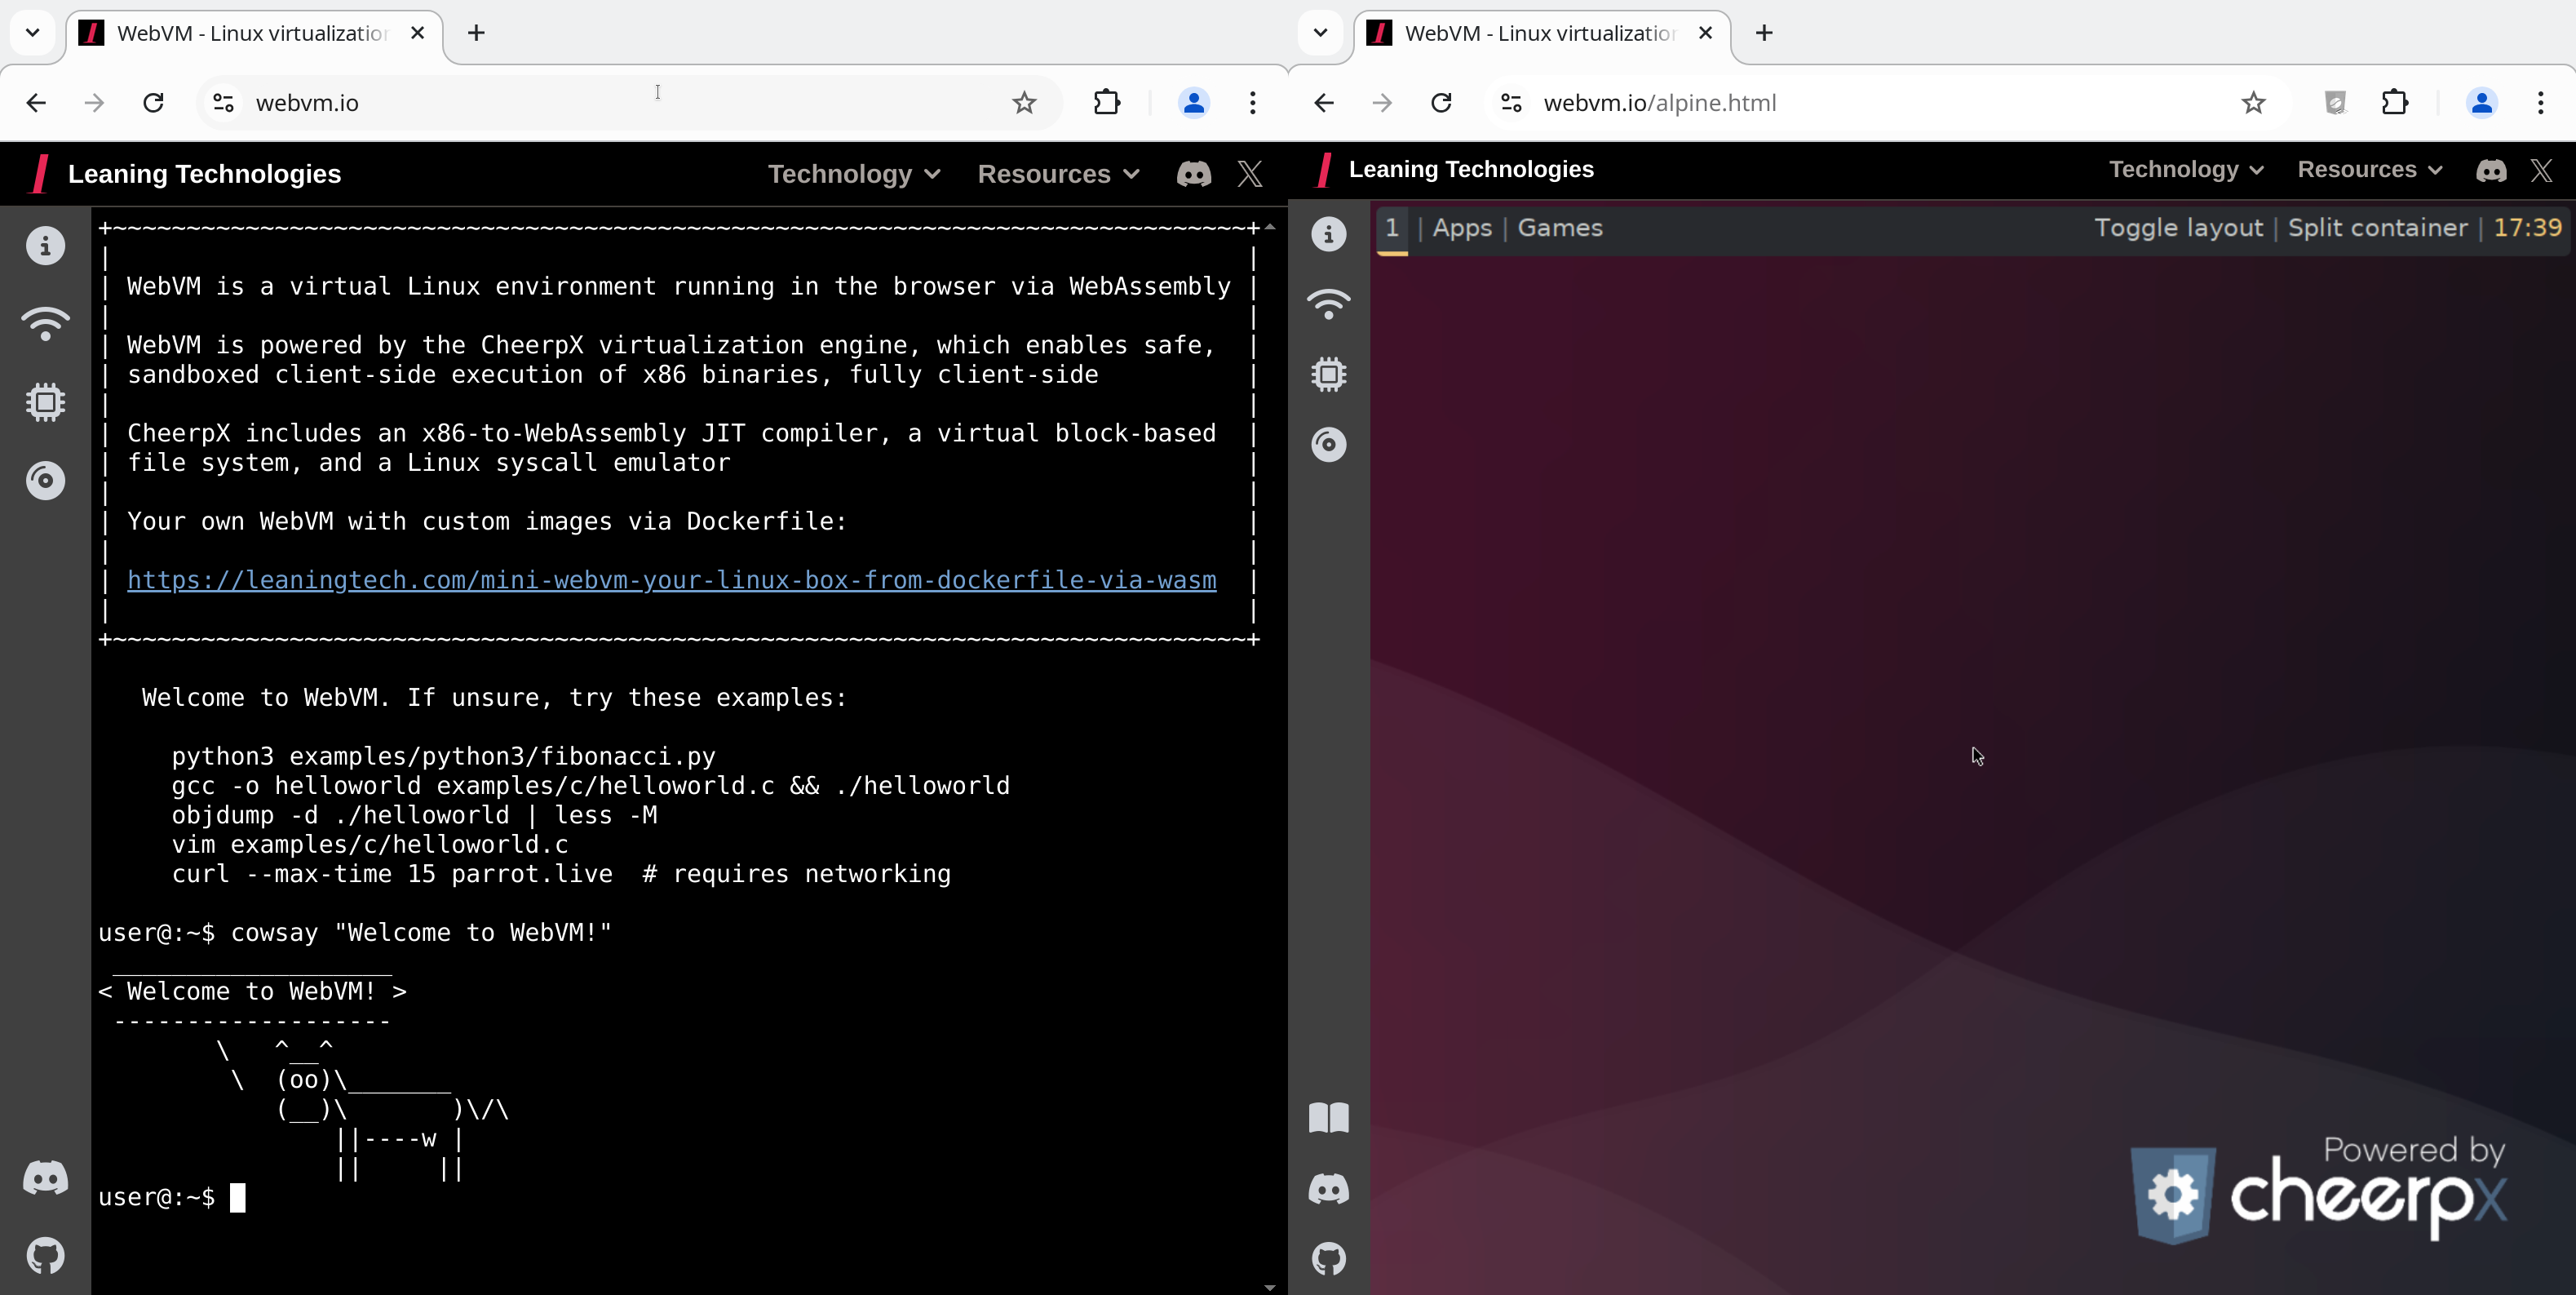 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…