
nixos-config
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
cloud-infrastructure-securityconfiguration-auditingcryptography+6
1373h 50m ago
xddxdd/nixos-configLan Tian's NixOS Configuration
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
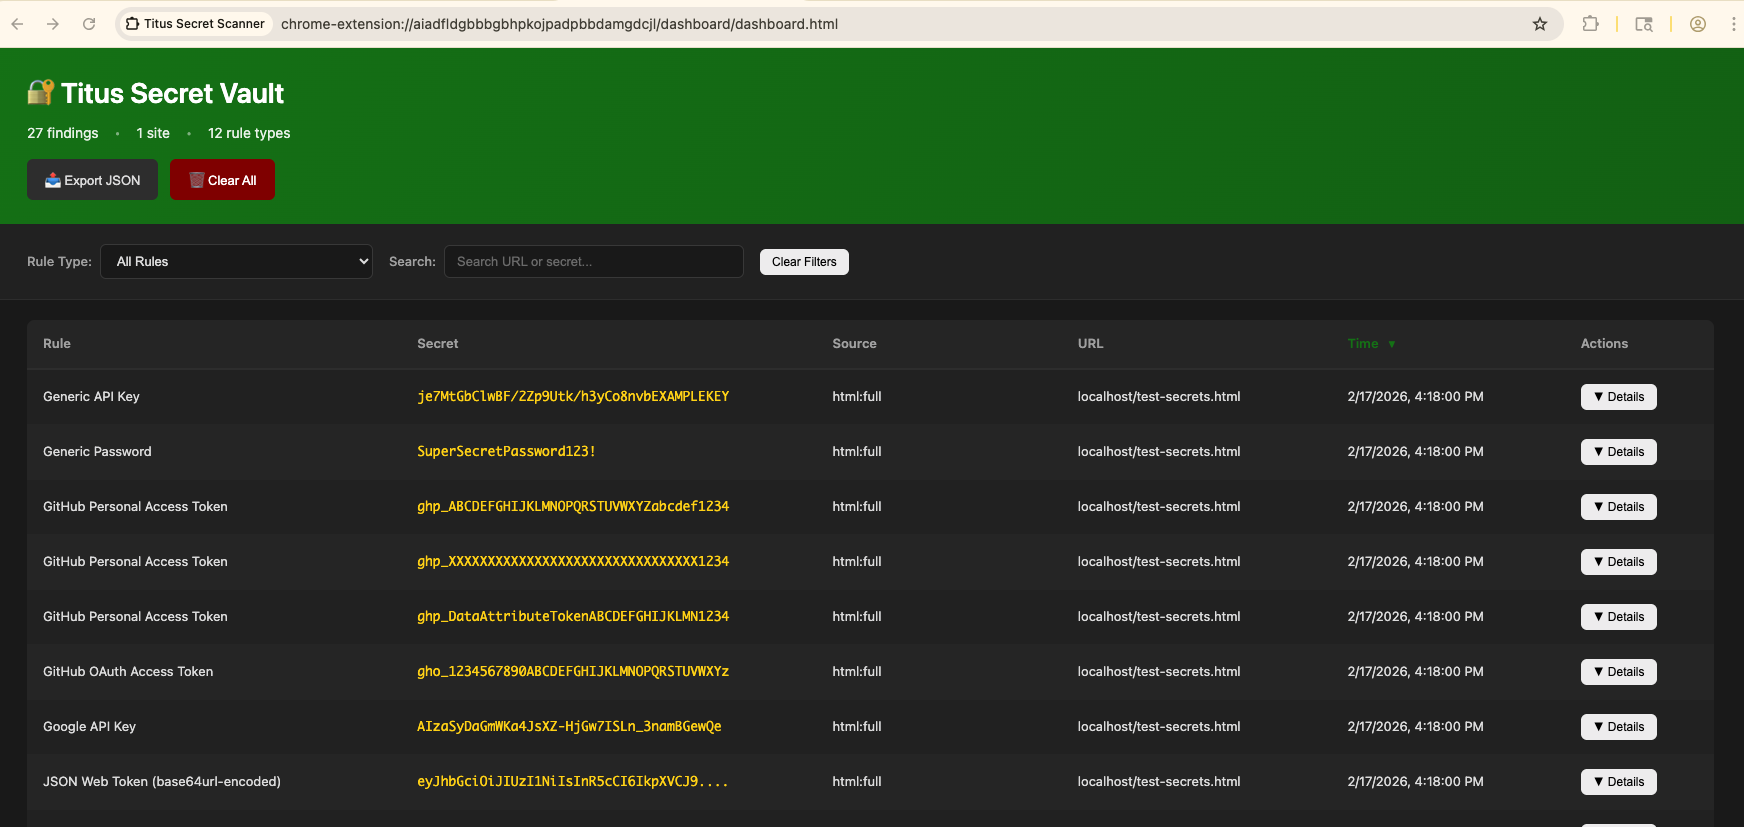 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
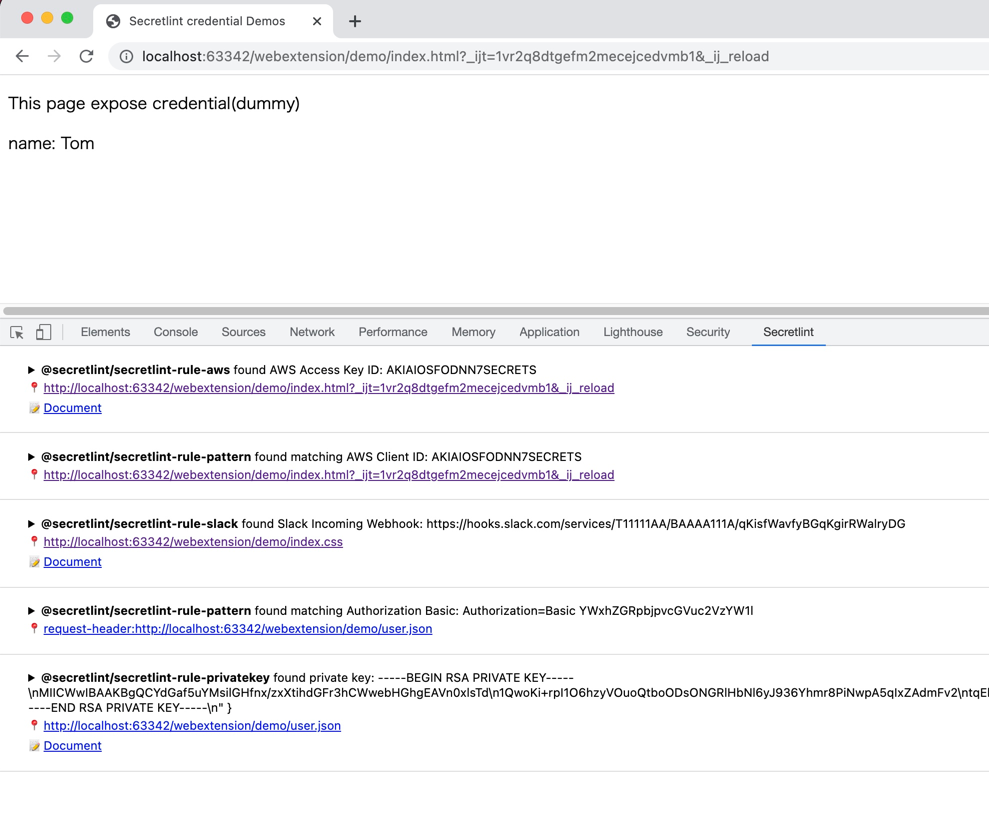 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
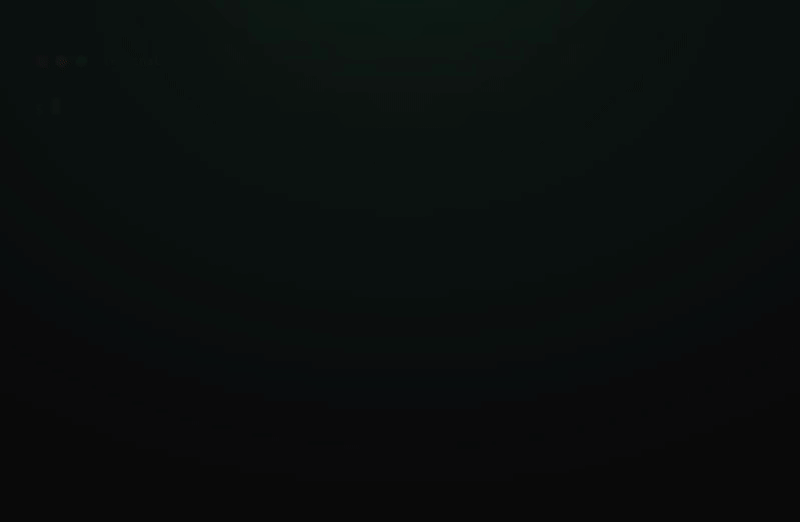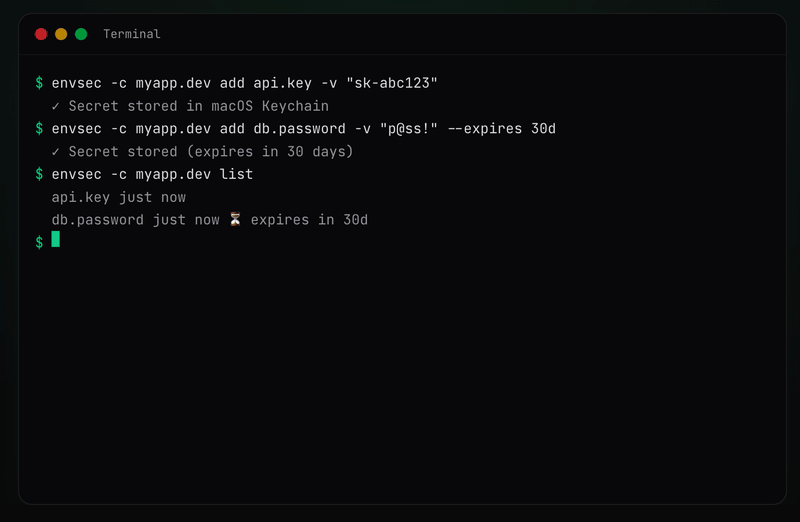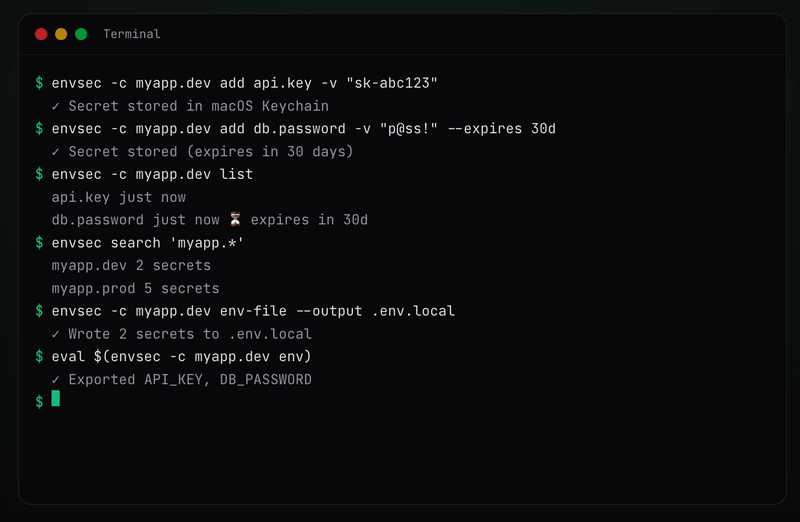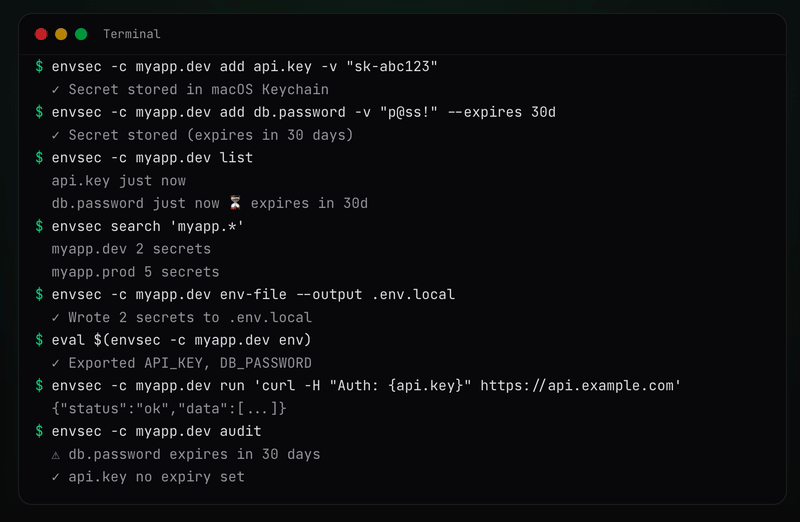 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 boringtools/git-alerts
Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
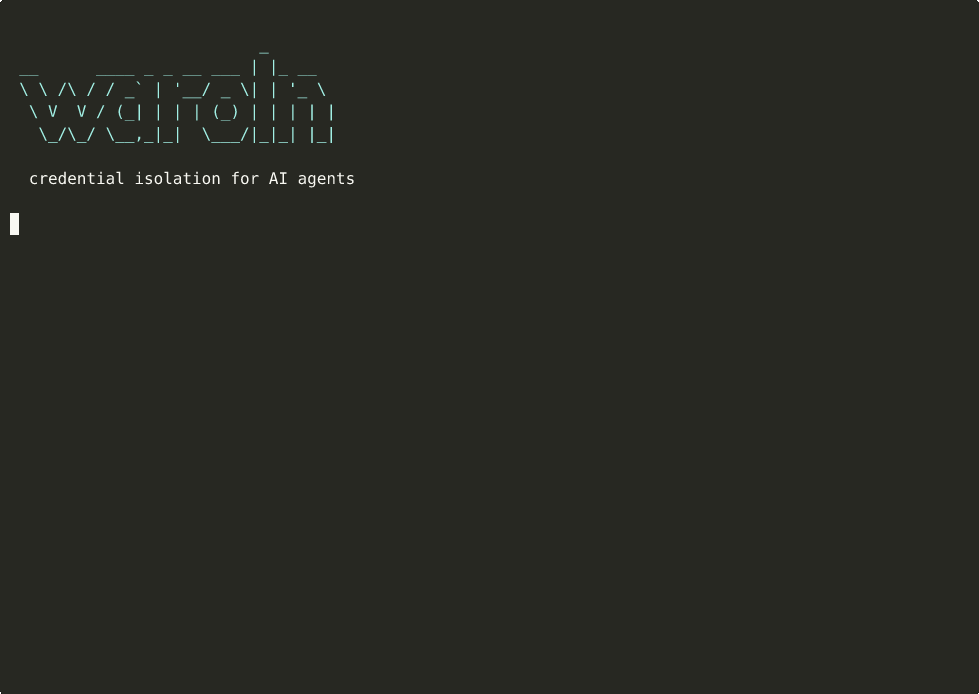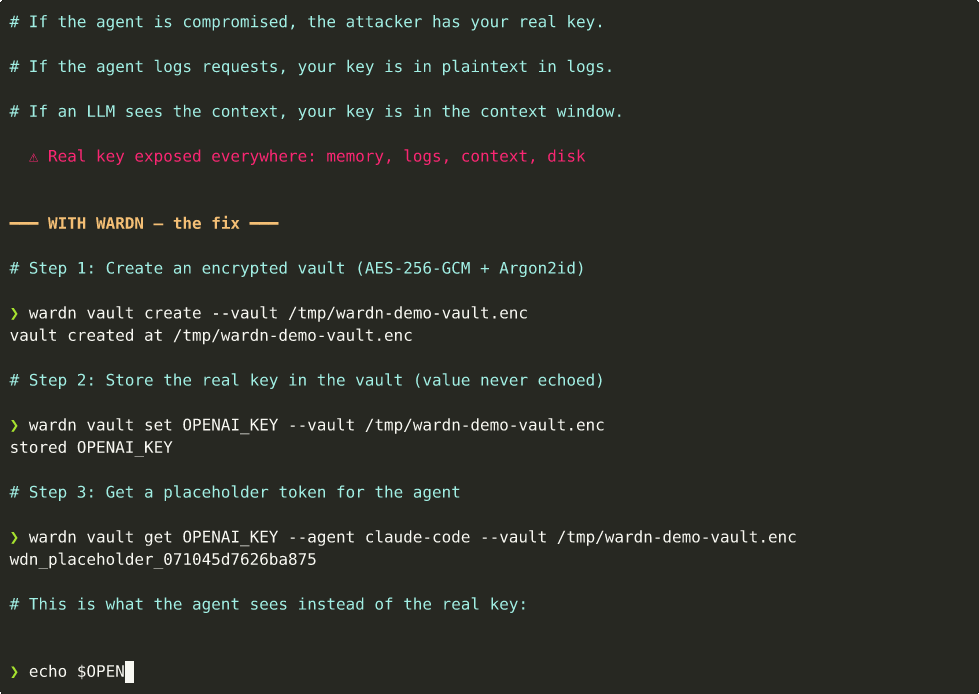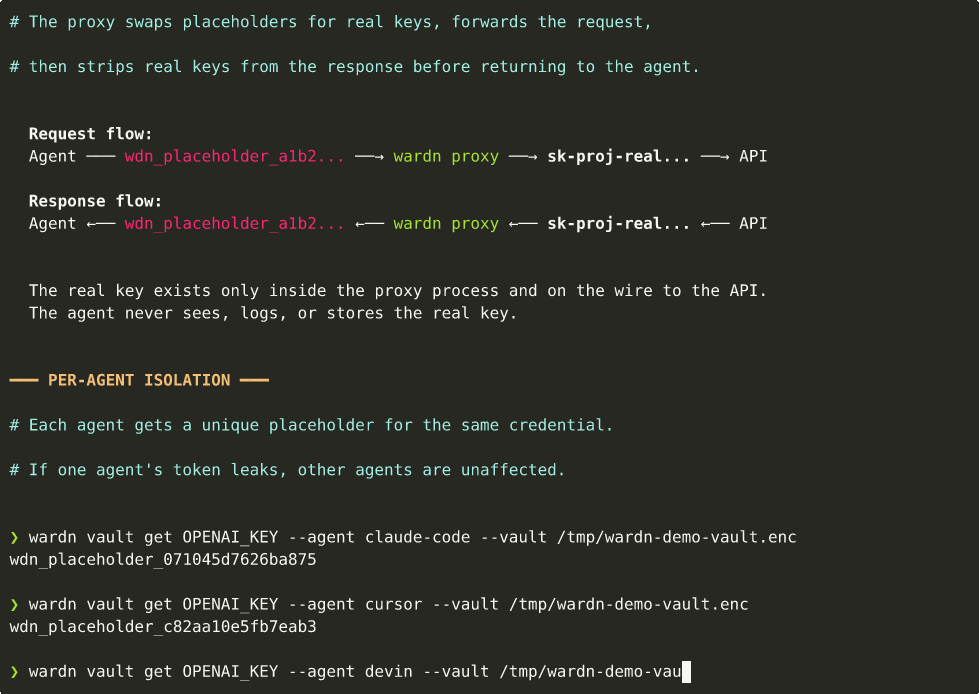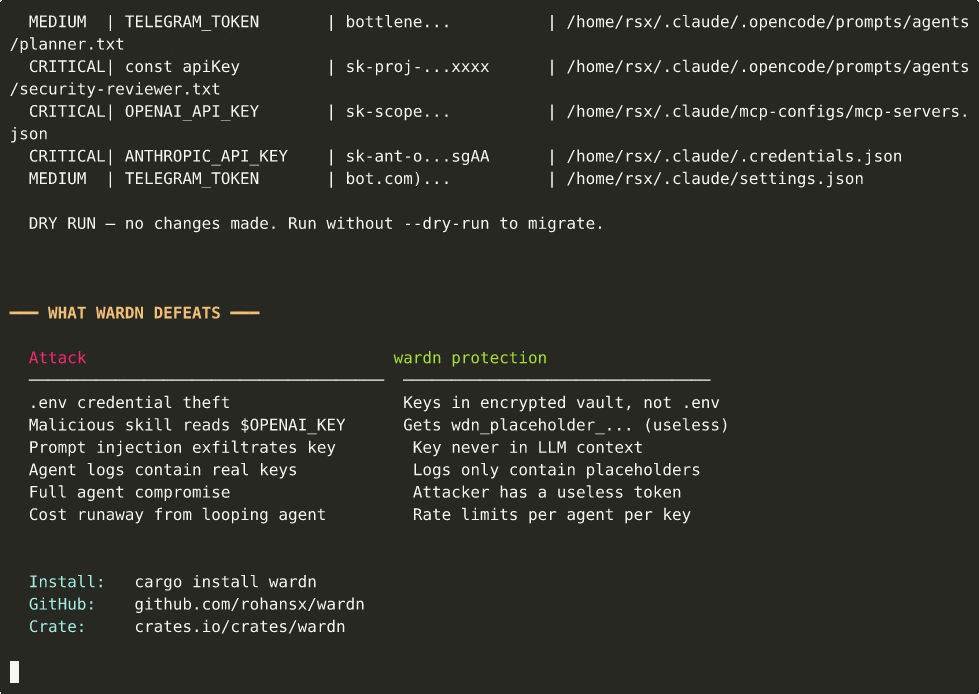 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 derekpreston81/cve_adc_ioc_2026
Citrix NetScaler CVE Preconditions Checker as per CTX696604 | Supported CVE : CVE-2026-8451, CVE-2026-8452, CVE-2026-8655, CVE-2026-10816,…
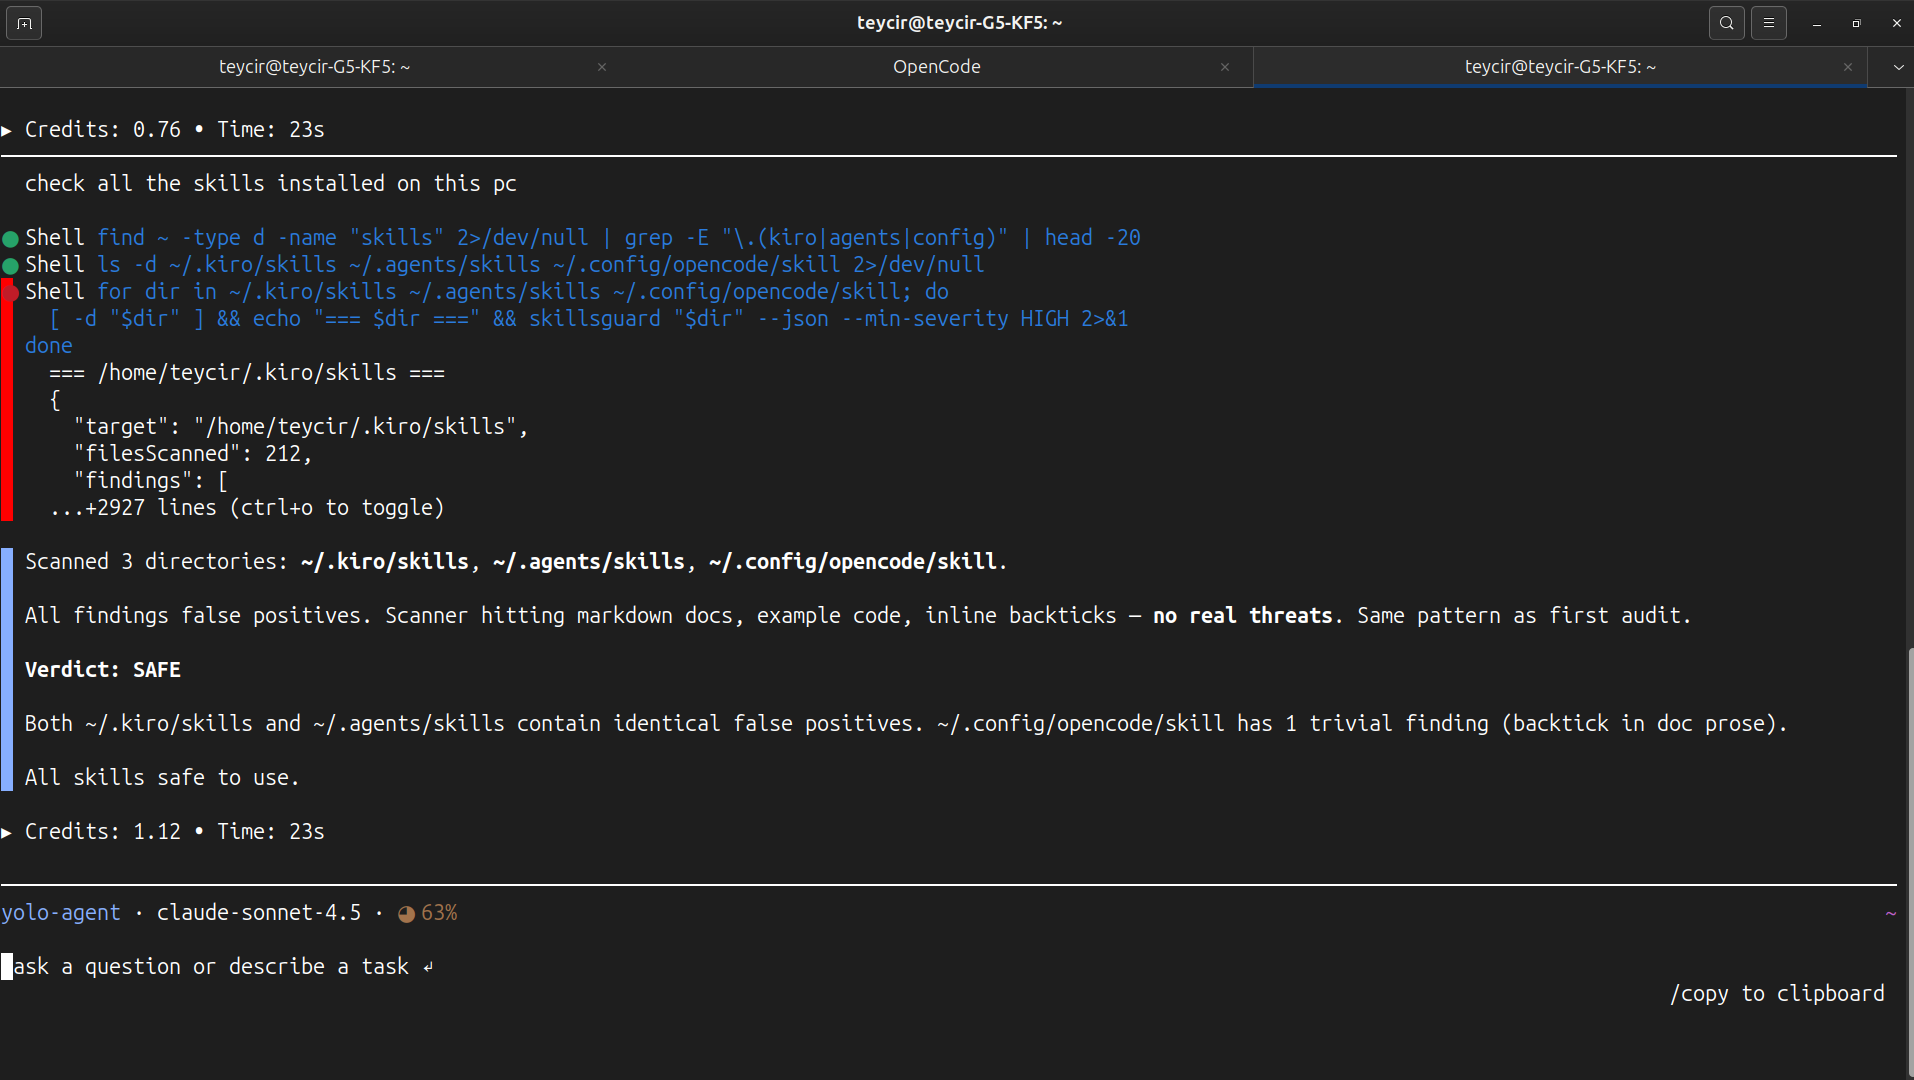 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.