
smolvm
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
cloud-infrastructure-securitycontainer-securitydevsecops+2
6.7k29 minutes ago
smol-machines/smolvmAn embeddable, portable, branchable virtual machine to safely run Agents locally.
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 captain4554/cve-2025-55182-scanner
🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
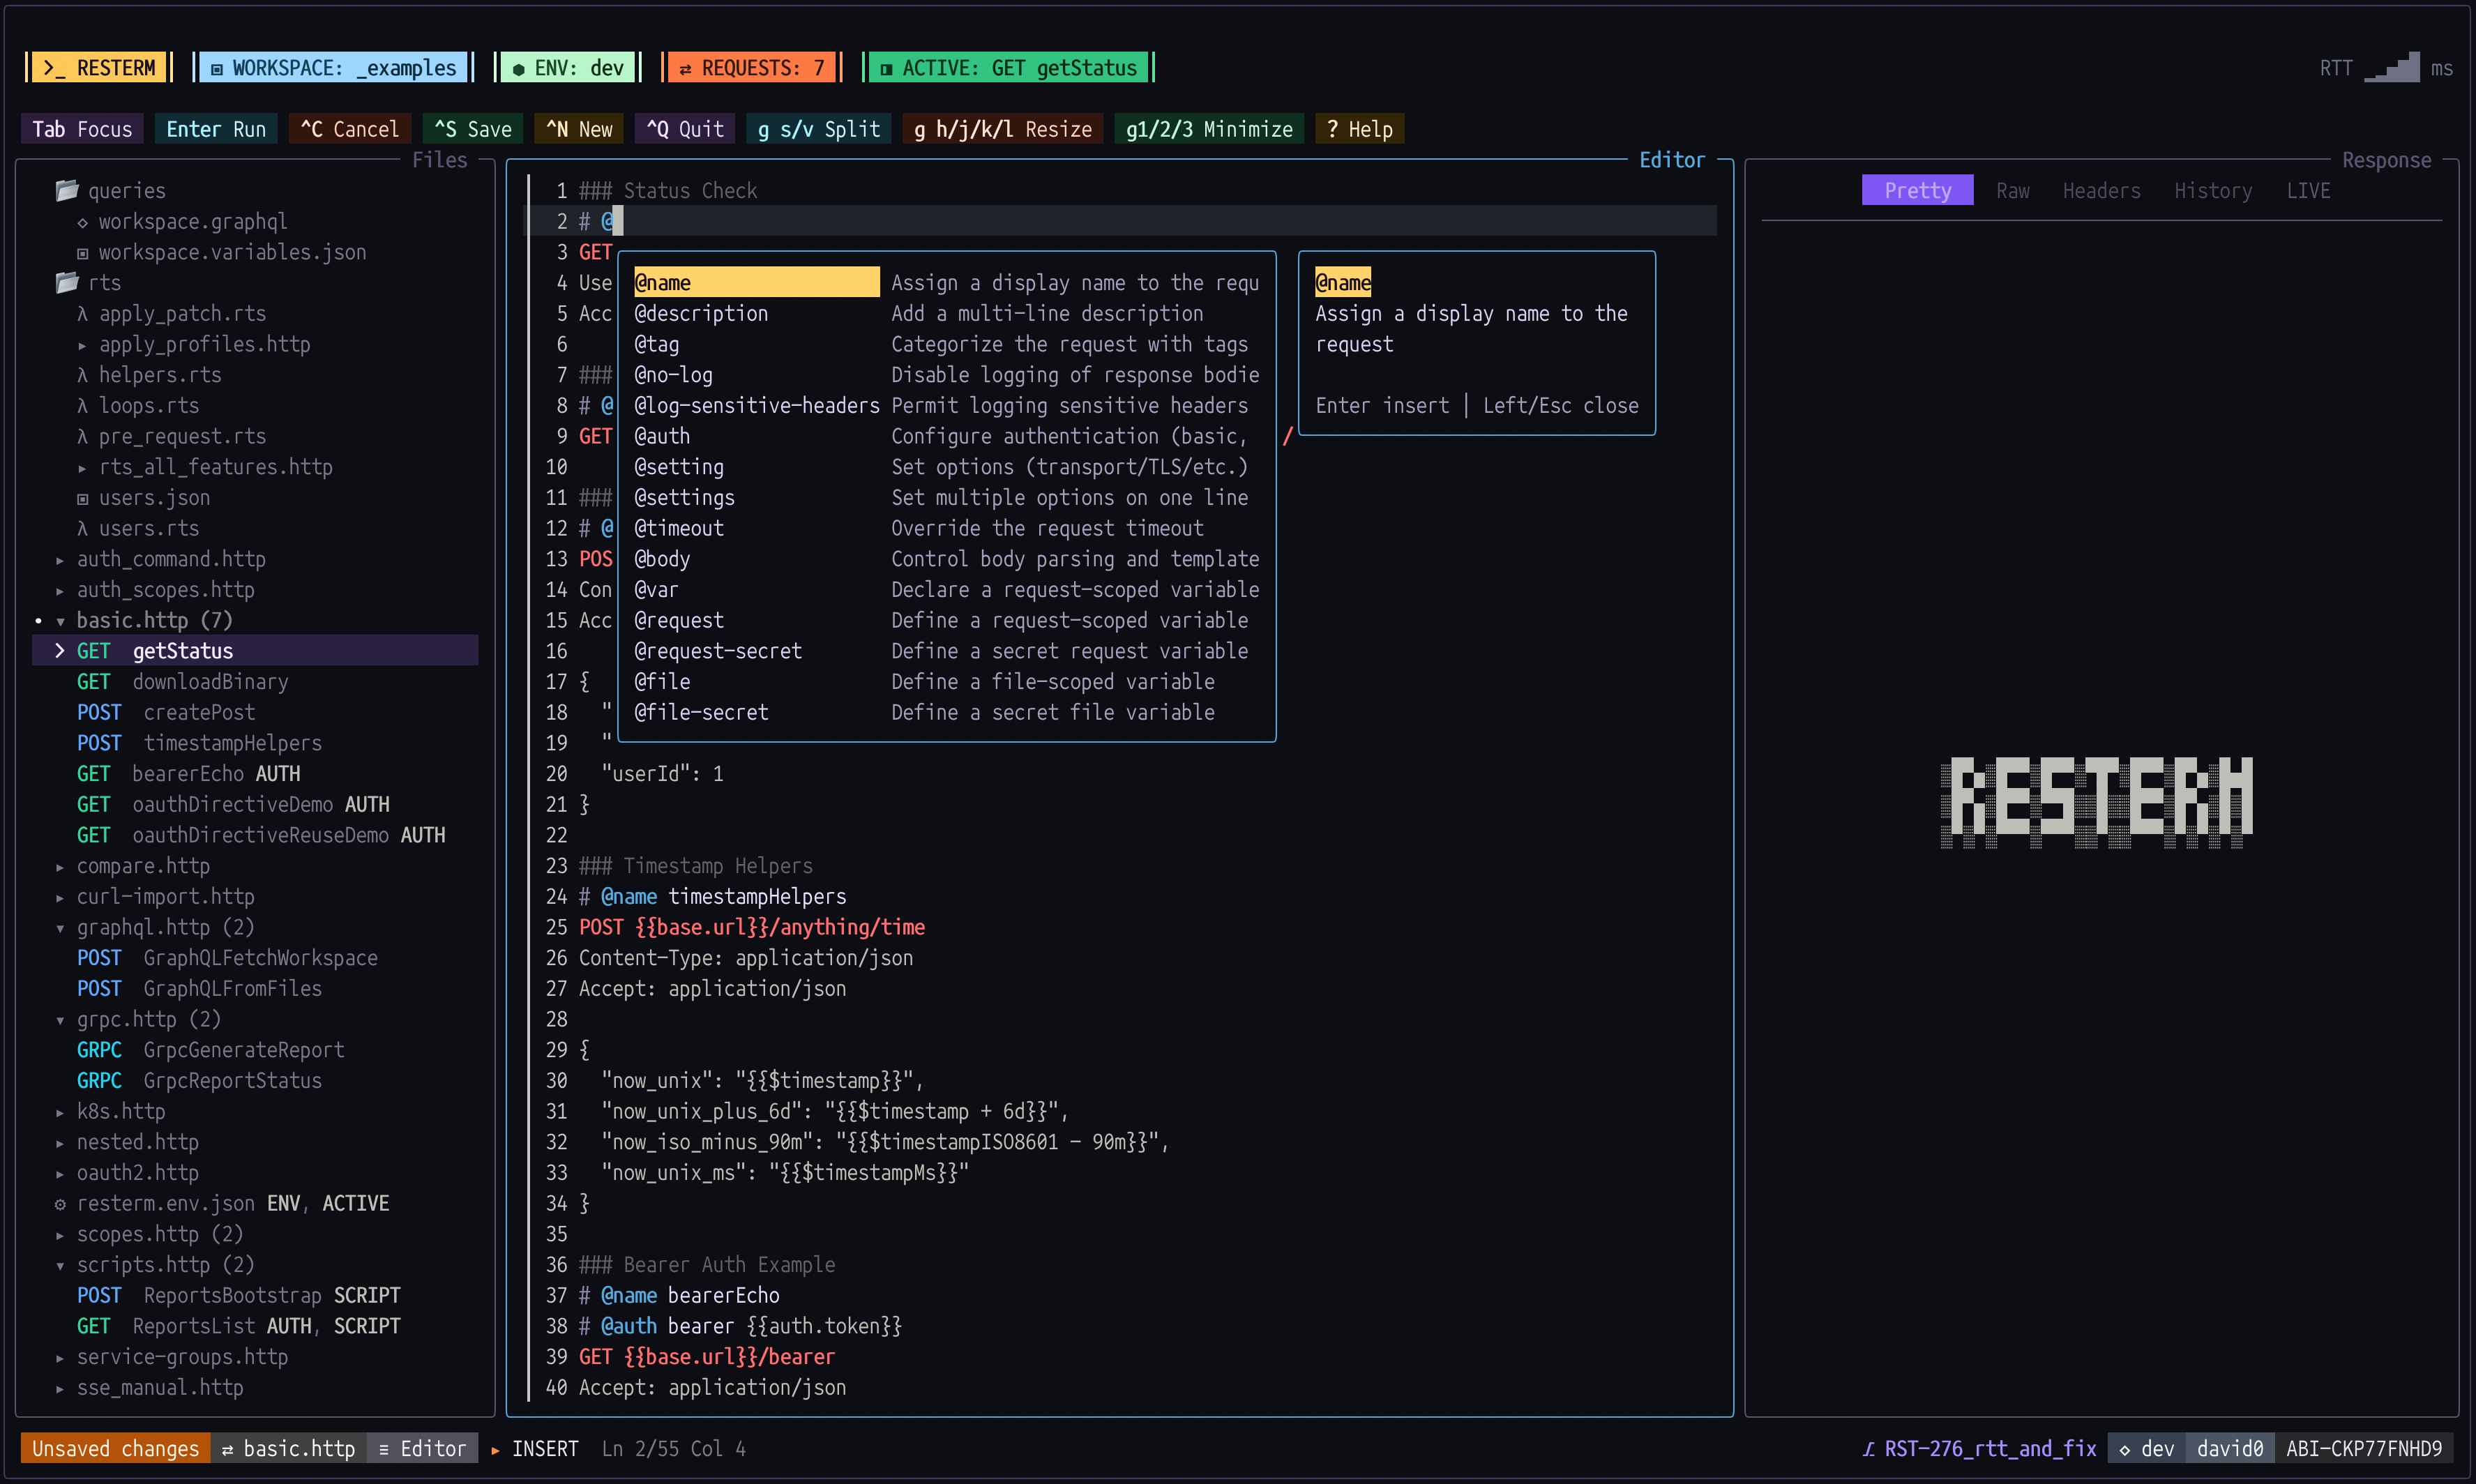 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 rtvkiz/minimal
Minimal CVE Hardened container image collection
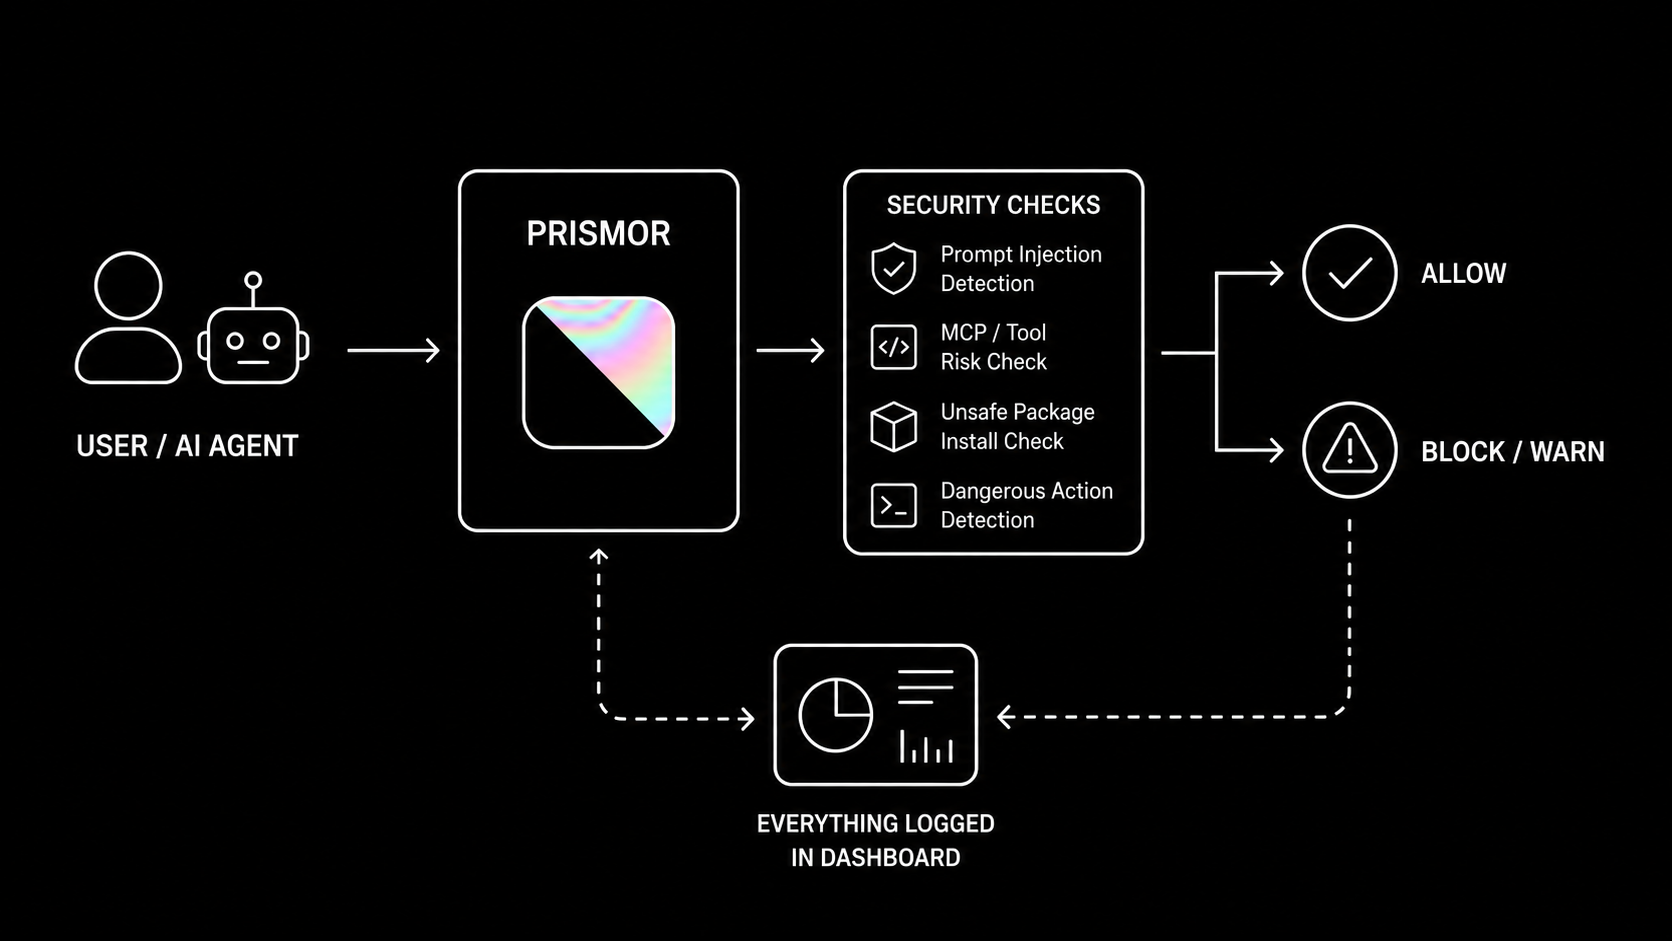 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…