Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

Burp Extension for collaboration in Faraday

YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…

Deploy your own lab of web application penetration testing with docker and docker-compose, webgoat, dvwap, bwapp and Juice Shop

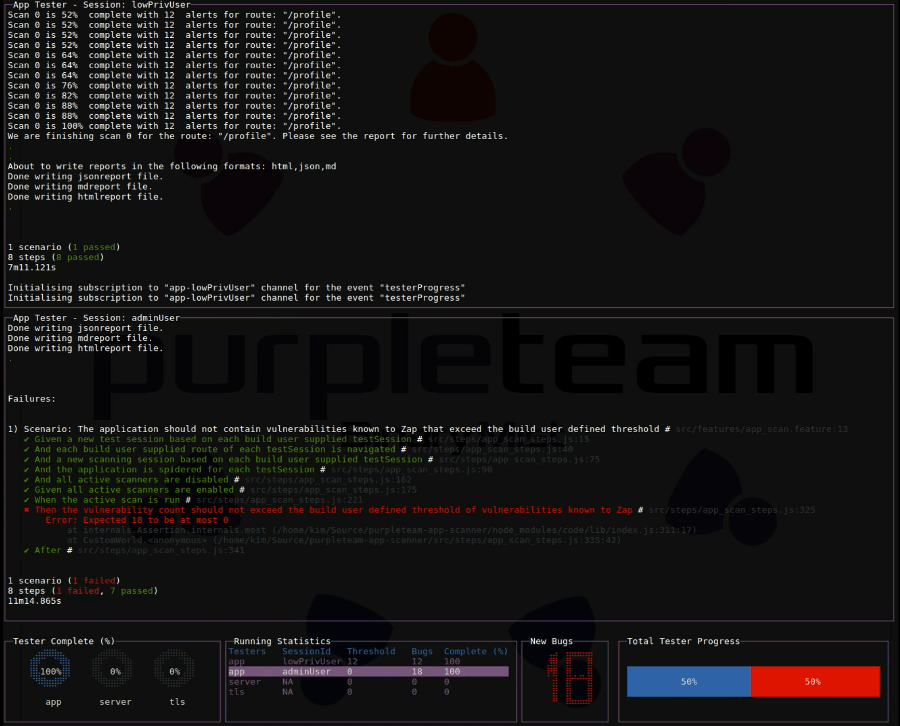
Application scanning component of purpleteam

TLS checking component of purpleteam

Server scanning component of purpleteam

Stage two containers

Orchestration component of purpleteam

CLI component of purpleteam

Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…