cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

TrustedRouter.com repo for secure LLM proxying

CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

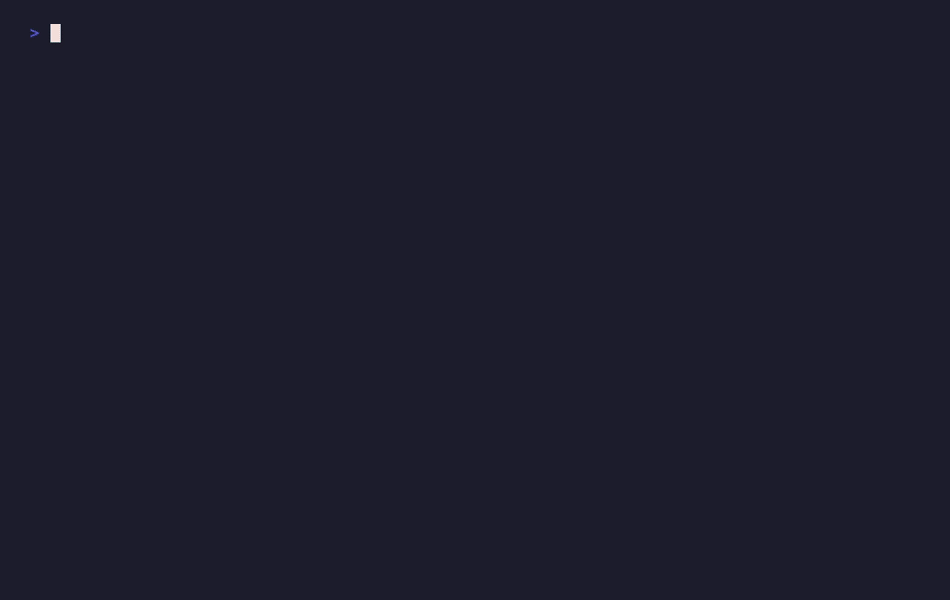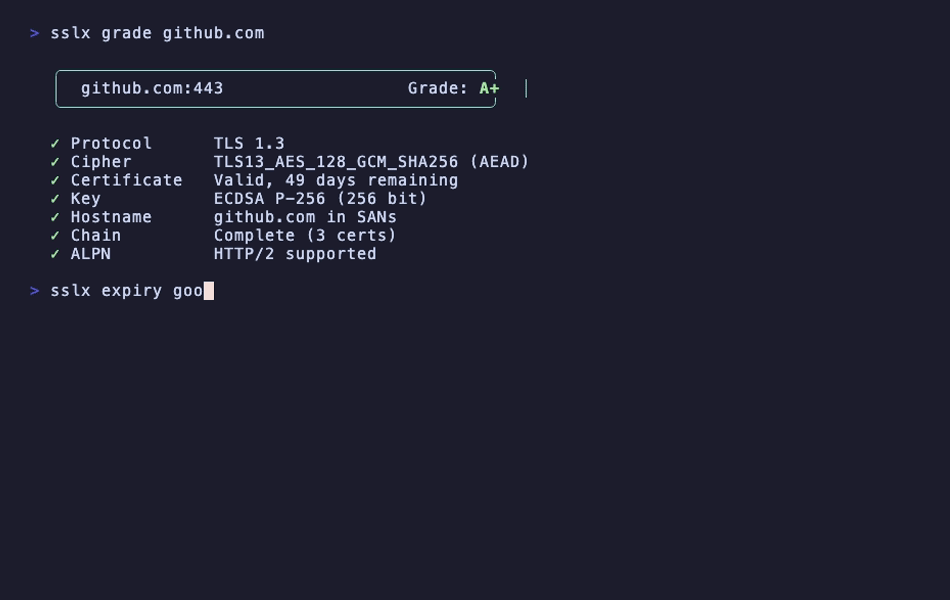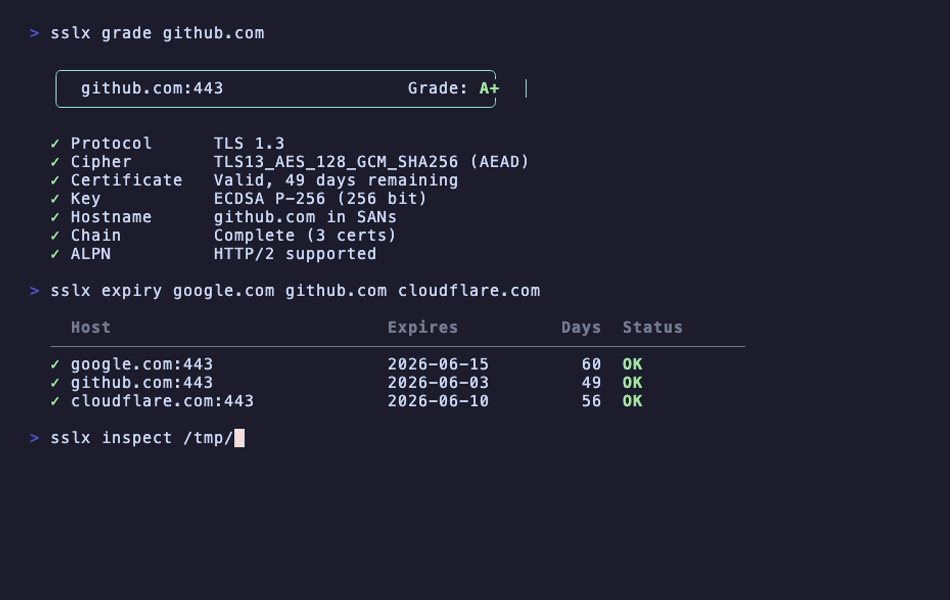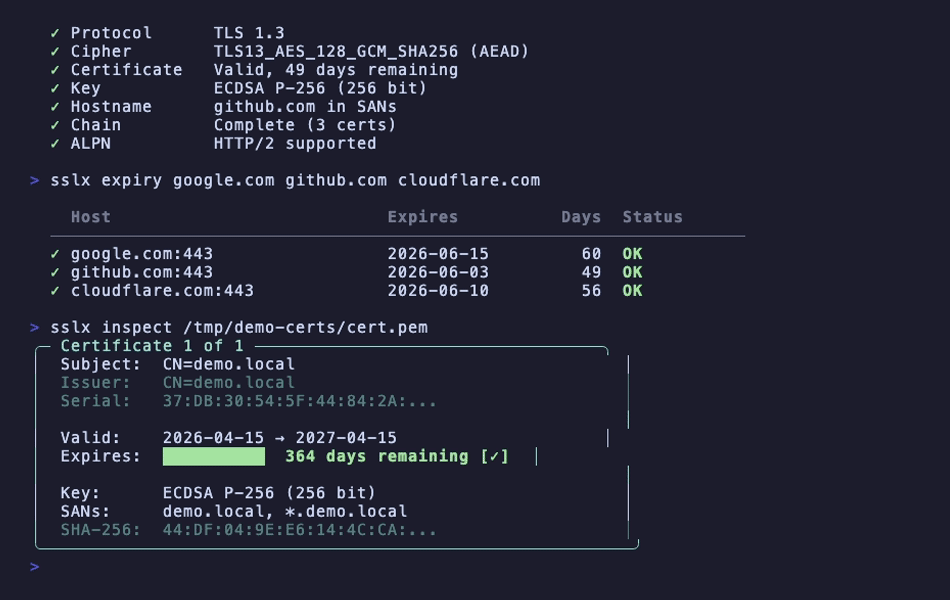
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.

WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…

Fast and powerful SSL/TLS scanning library.

A static analyzer for Java, C, C++, and Objective-C

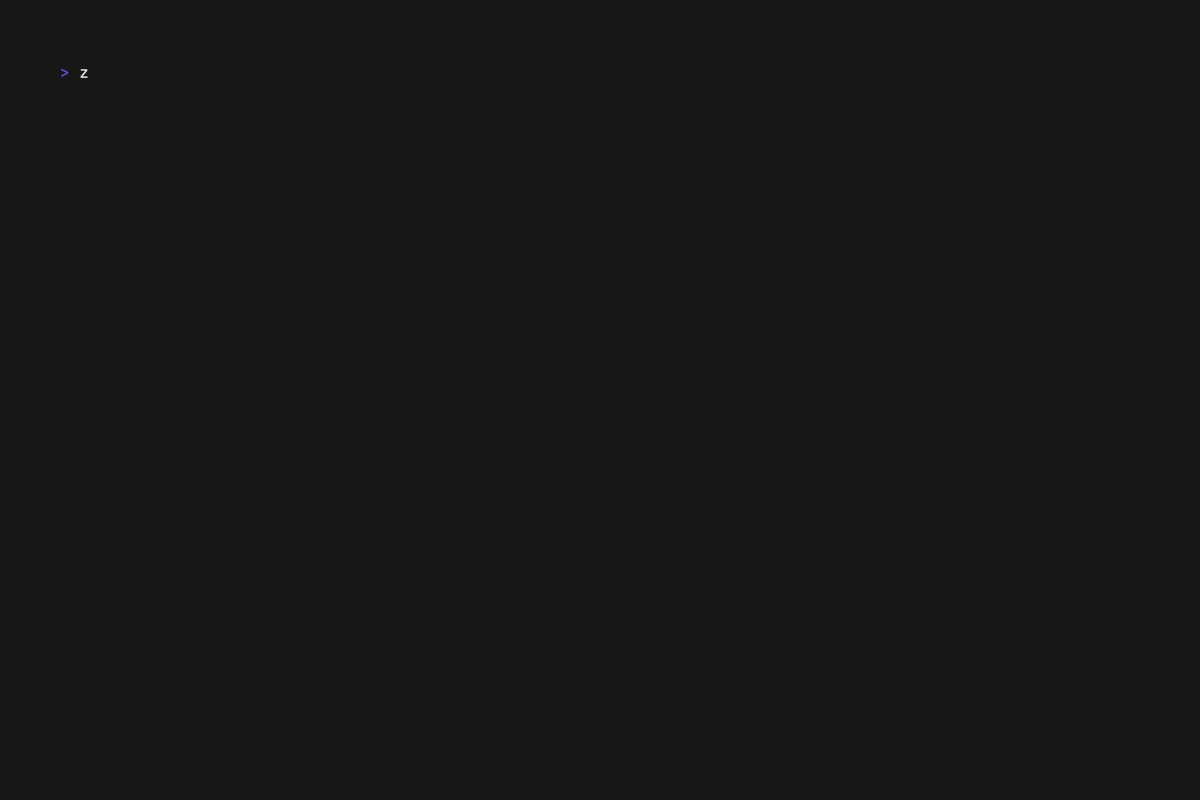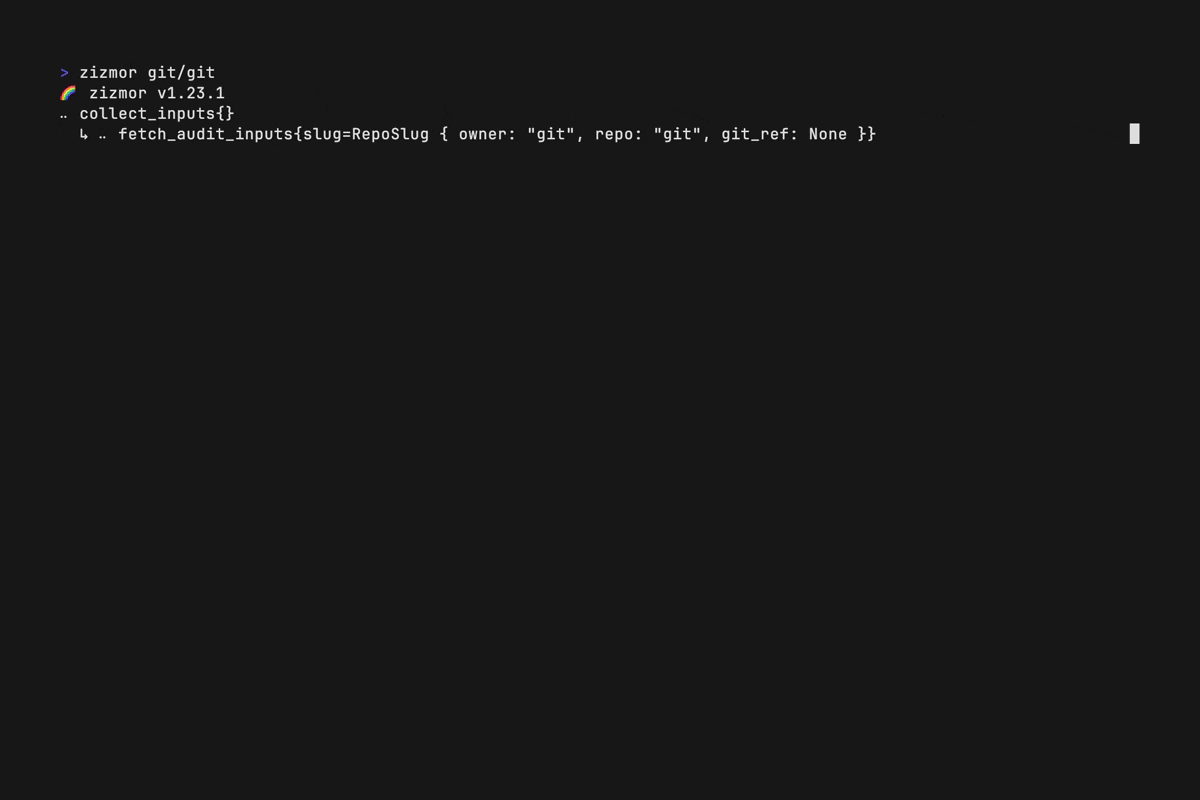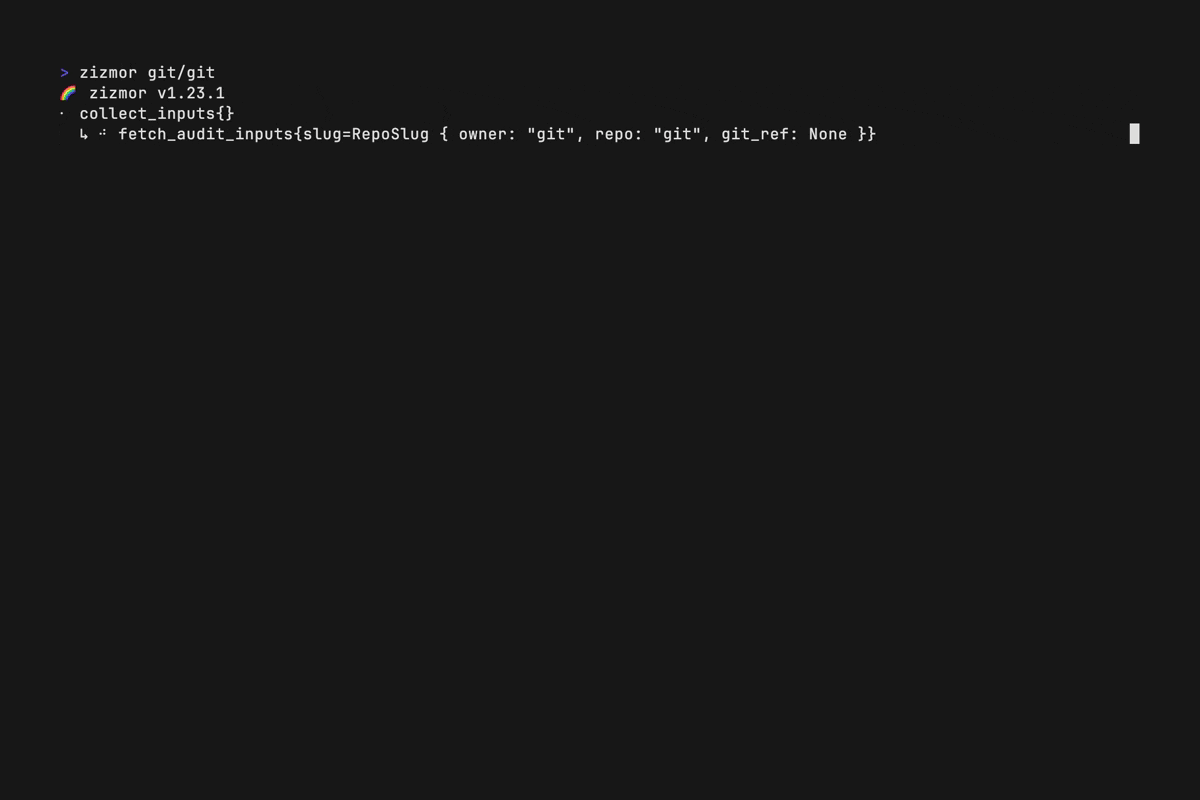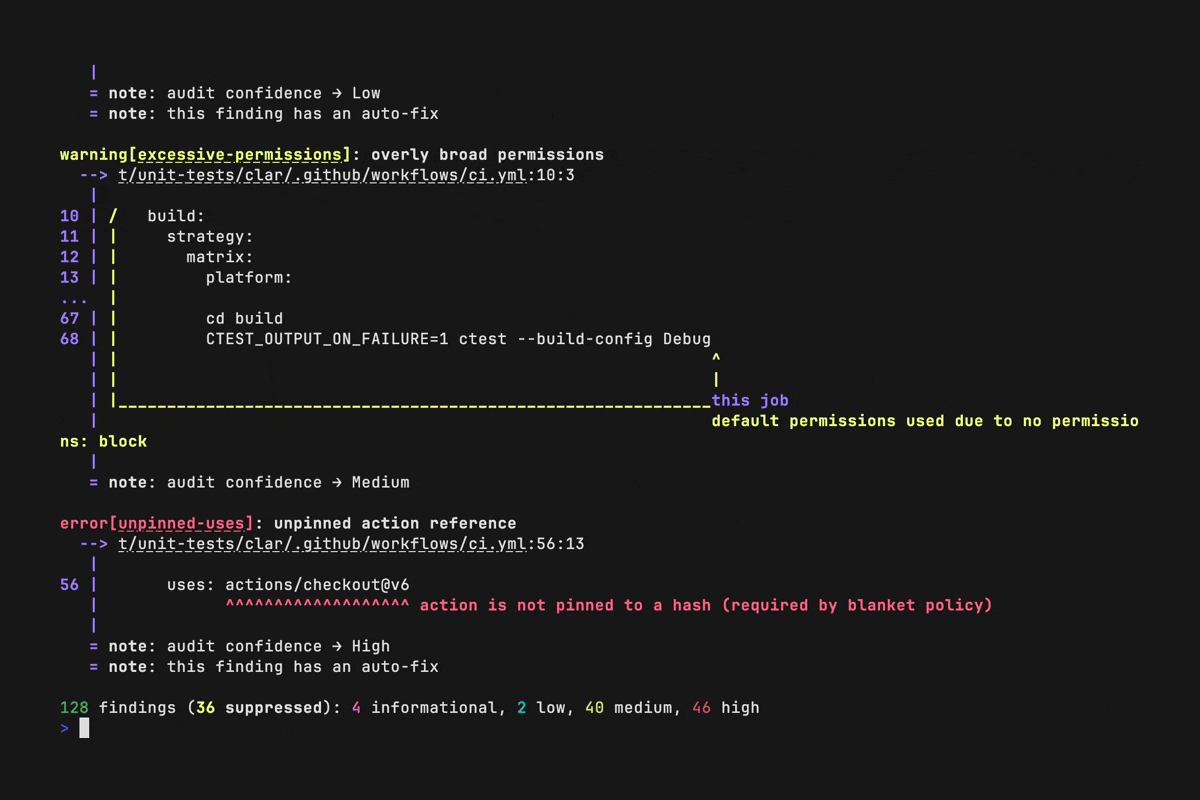
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…

HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis

Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

A vulnerability scanner for container images and filesystems

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…