
push-guard
 dragon-lady/push-guard
Local Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…
configuration-auditingdefensive-toolsdevsecops+4
dragon-lady/push-guardLocal Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 m14r41/scan4secrets
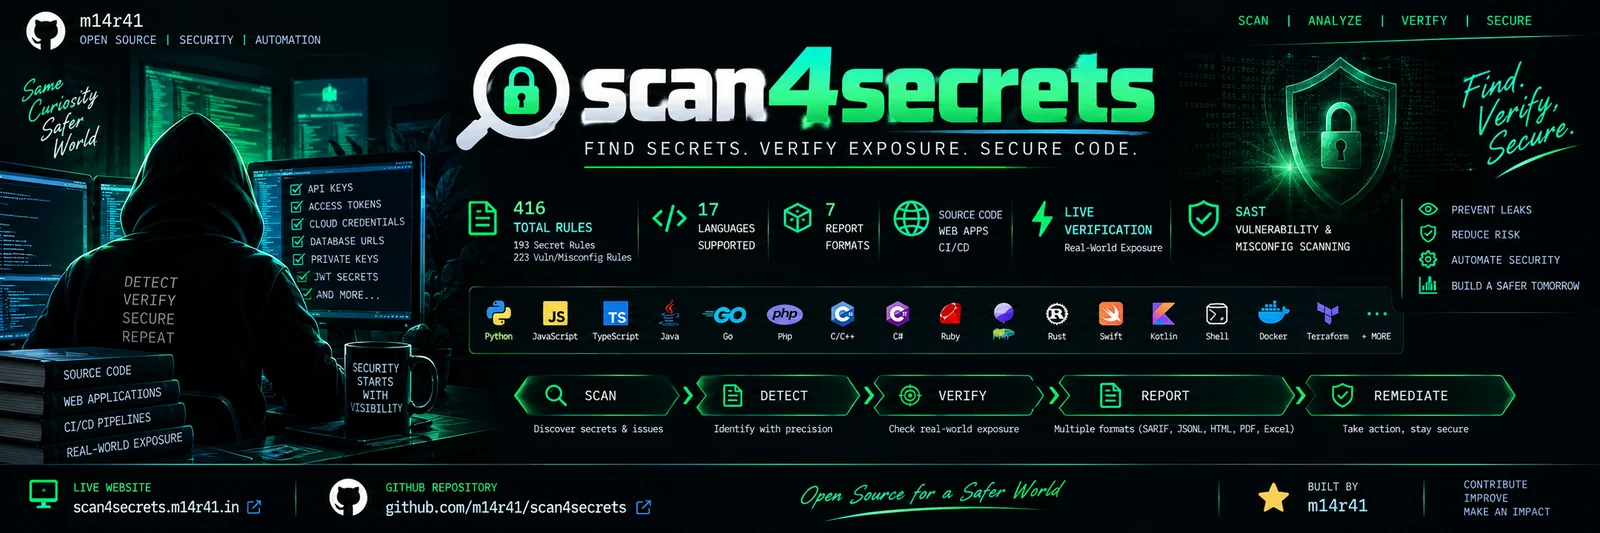
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 soufianecyber/quantum-safe-migration
Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).
 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…