Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).



A Post-Quantum Cryptography Migration Toolkit for Nginx and OpenSSH.
QSM is an open-source toolkit that audits legacy cryptographic configurations and migrates them to hybrid post-quantum cryptography (PQC). It targets the "Harvest Now, Decrypt Later" (HNDL) threat vector by simulating Shor's Algorithm impact and automating hybrid migrations on Debian-based systems.
⚠️ Strict Architectural Principle: QSM never permits pure post-quantum deployment. All operations enforce a Hybrid Paradigm combining classical and PQC algorithms (ECDSA P-256 + ML-DSA-65 for authentication; X25519 + ML-KEM-768 for key exchange).
QSM is a functional proof-of-concept, not a certified production tool. Please read this section carefully before relying on it in critical environments.
The --simulate command uses a simplified analytical model for Shor's
Algorithm resource estimation — not a compiled quantum circuit:
O(bits³)logical_qubits × 1000 (surface code assumption)This produces order-of-magnitude estimates, not precise predictions. Real-world CRQC resource requirements depend on circuit depth, gate fidelity, error-correction overhead, and hardware architecture. These remain active research areas.
The output figures (e.g., "~99 days for ECC-256") represent a theoretical lower bound under stated assumptions, not a measurement on any existing machine. No Cryptographically Relevant Quantum Computer (CRQC) exists today.
The --migrate command patches configuration files to inject hybrid
cipher suites. It does not:
liboqs or oqs-providerYou must ensure oqs-provider is installed and loaded for the injected
cipher names to be honored. Test all migrations in a non-production
environment first.
QSM has been verified on:
tests/)It has not been stress-tested at scale, under load, or across diverse environments. Treat it as a reference implementation and adapt it to your infrastructure.
QSM targets the finalized NIST standards:
| FIPS | Algorithm | QSM Usage |
|---|---|---|
| FIPS 203 | ML-KEM | Key exchange (ML-KEM-768) |
| FIPS 204 | ML-DSA | Authentication (ML-DSA-65) |
Terminology: "Kyber" and "Dilithium" were the pre-standard codenames used during the NIST competition. The finalized standards use ML-KEM and ML-DSA respectively. QSM uses the standardized names throughout.
QSM is built to run adaptively across environments:
liboqs system
integration to patch configuration layers atomically with
checksum-verified rollback logic.# Clone and enter the vault
git clone https://github.com/soufianecyber/Quantum-Safe-Migration
cd Quantum-Safe-Migration
# Initialize virtual environment
python3 -m venv venv
source venv/bin/activate
# Install dependencies
pip install -r requirements.txt
python3 qsm.py --preflight
# 1. Run Quantum Attack Simulation on target assets
python3 qsm.py --simulate --target example.com
python3 qsm.py --simulate --keyfile ./test_legacy_key.pem

# 2. Preview Hybrid Migration Block (Safe Dry-Run)
python3 qsm.py --migrate --target nginx --config ./dummy_nginx.conf --dry-run

# 3. Apply Production Migration (Requires Sudo)
sudo venv/bin/python3 qsm.py --migrate --target nginx --config /etc/nginx/nginx.conf
sudo venv/bin/python3 qsm.py --migrate --target sshd --config /etc/ssh/sshd_config

# 4. Atomic Rollback Checksum Restoration
sudo venv/bin/python3 qsm.py --rollback --target /etc/nginx/nginx.conf
sudo python3 qsm.py --preflight
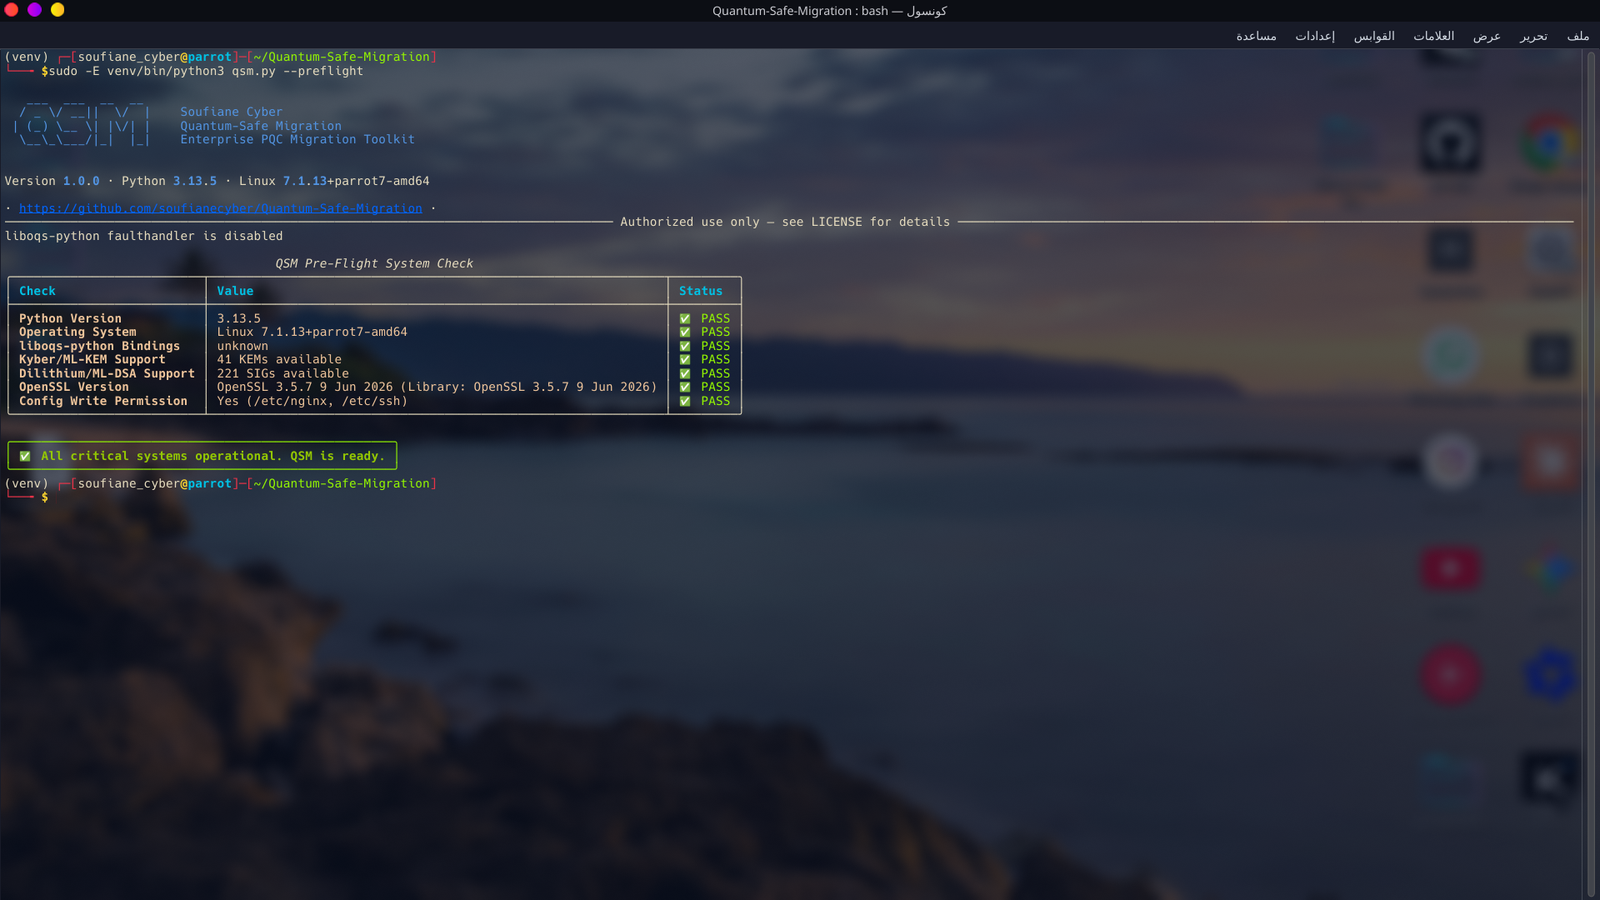
Validates Python version, liboqs bindings, ML-KEM/ML-DSA availability, and OpenSSL.
python3 qsm.py --simulate --target google.com
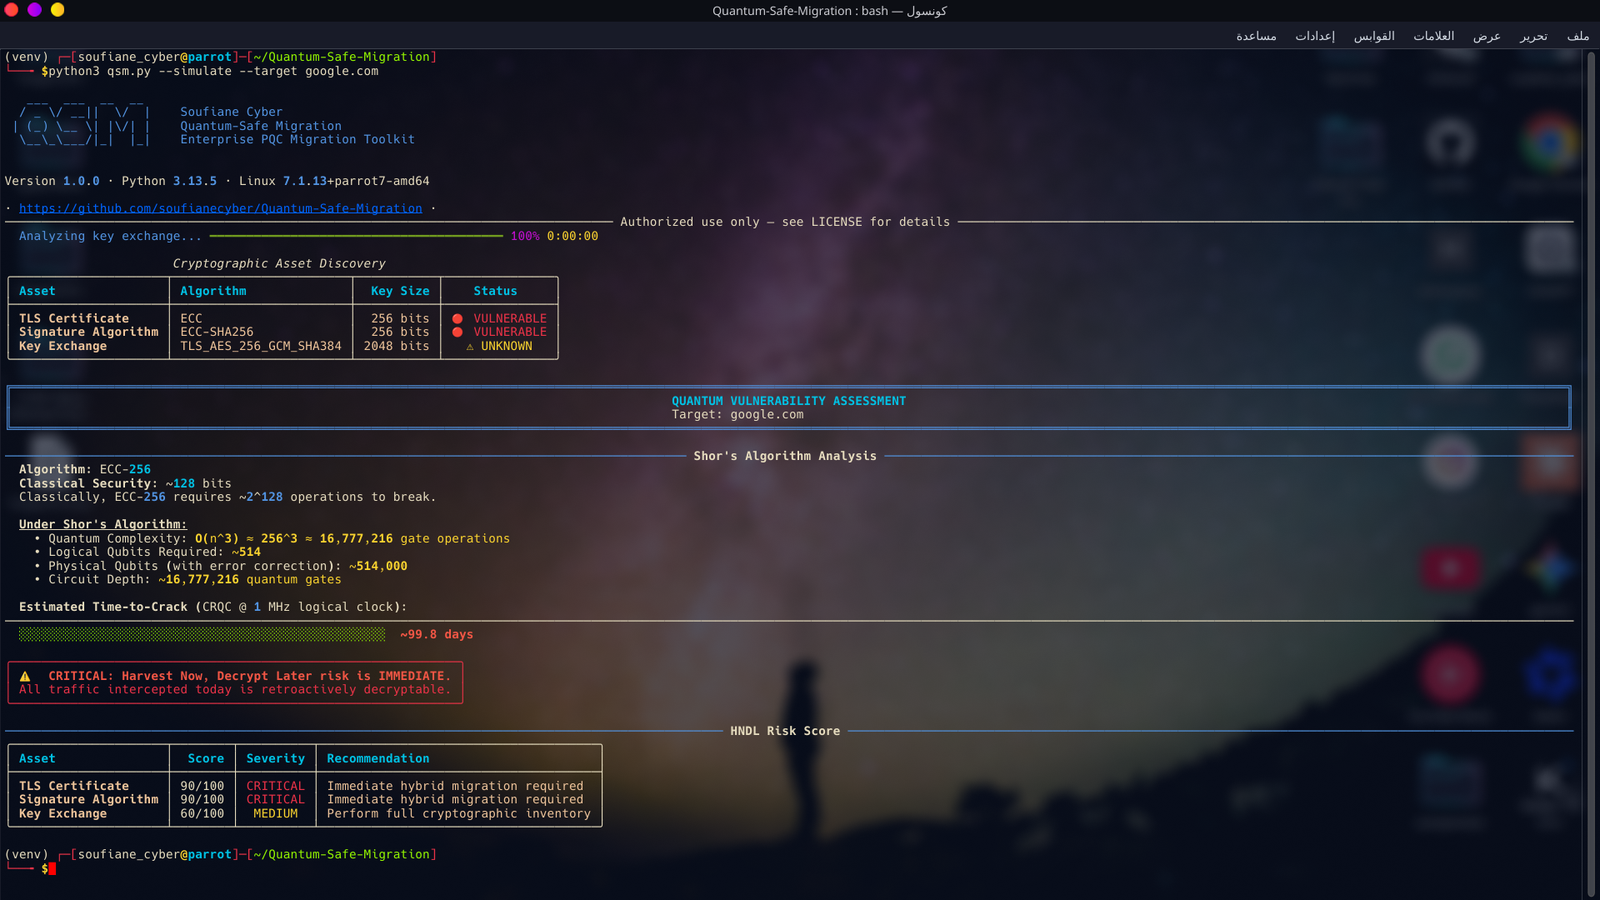
Detects ECC-256 on google.com and computes Shor's Algorithm time-to-crack.
sudo python3 qsm.py --migrate --target nginx --config /etc/nginx/nginx.conf --dry-run
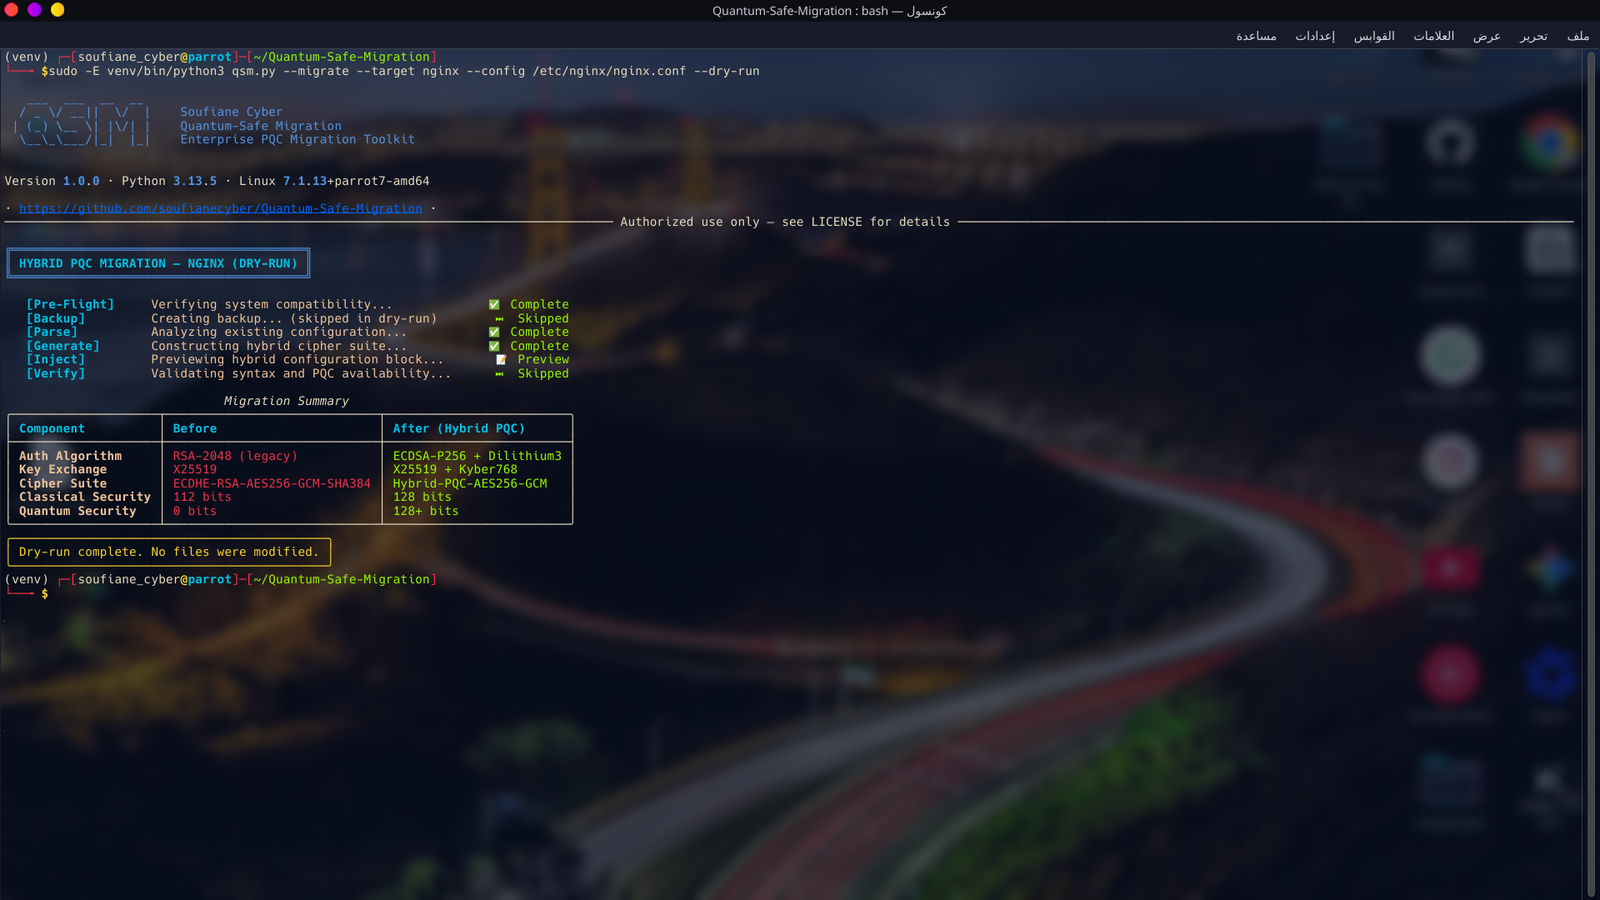
Preview of hybrid cipher suite injection — no files modified.
Distributed under the MIT License. See LICENSE for details.
Disclaimer: This toolkit is built exclusively for authorized testing and infrastructure migration verification purposes.
Soufiane Cyber
liboqsIf QSM helps you secure your infrastructure against quantum threats, please consider giving it a star on GitHub. It helps the project gain visibility and reach more security teams who need it.