
push-guard
 dragon-lady/push-guard
Local Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…
configuration-auditingdefensive-toolsdevsecops+4
dragon-lady/push-guardLocal Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
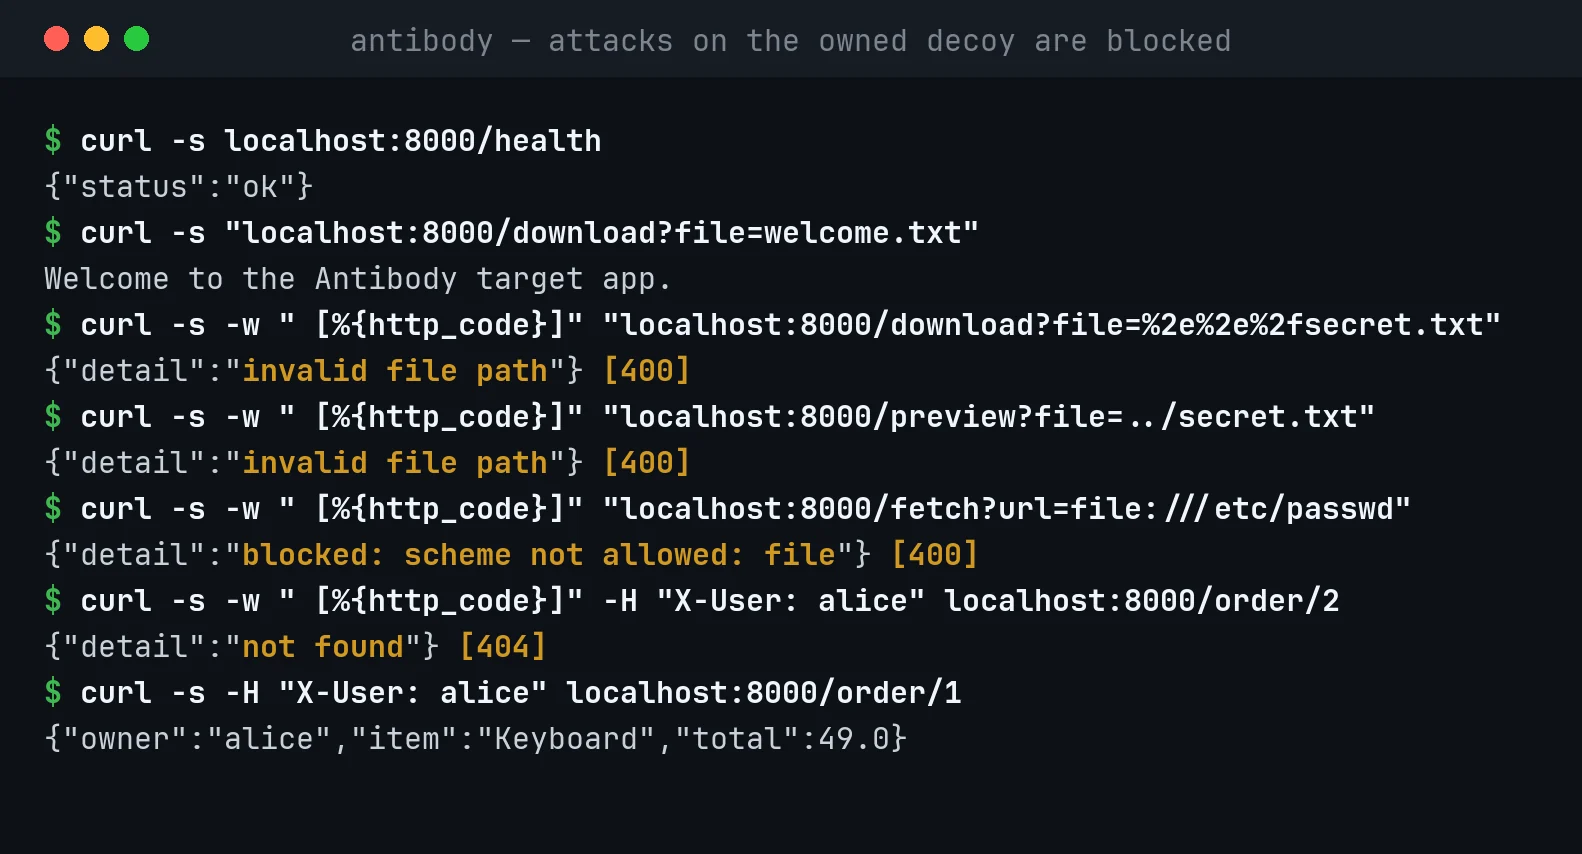
 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 owasp/blt
Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 soufianecyber/quantum-safe-migration
Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…