
kingfisher
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
cloud-securitycontainer-securitydevsecops+7
1.3k
mongodb/kingfisherDetect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 soufianecyber/quantum-safe-migration
Enterprise-grade toolkit to audit and migrate legacy infrastructure to hybrid post-quantum cryptography (PQC).

 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
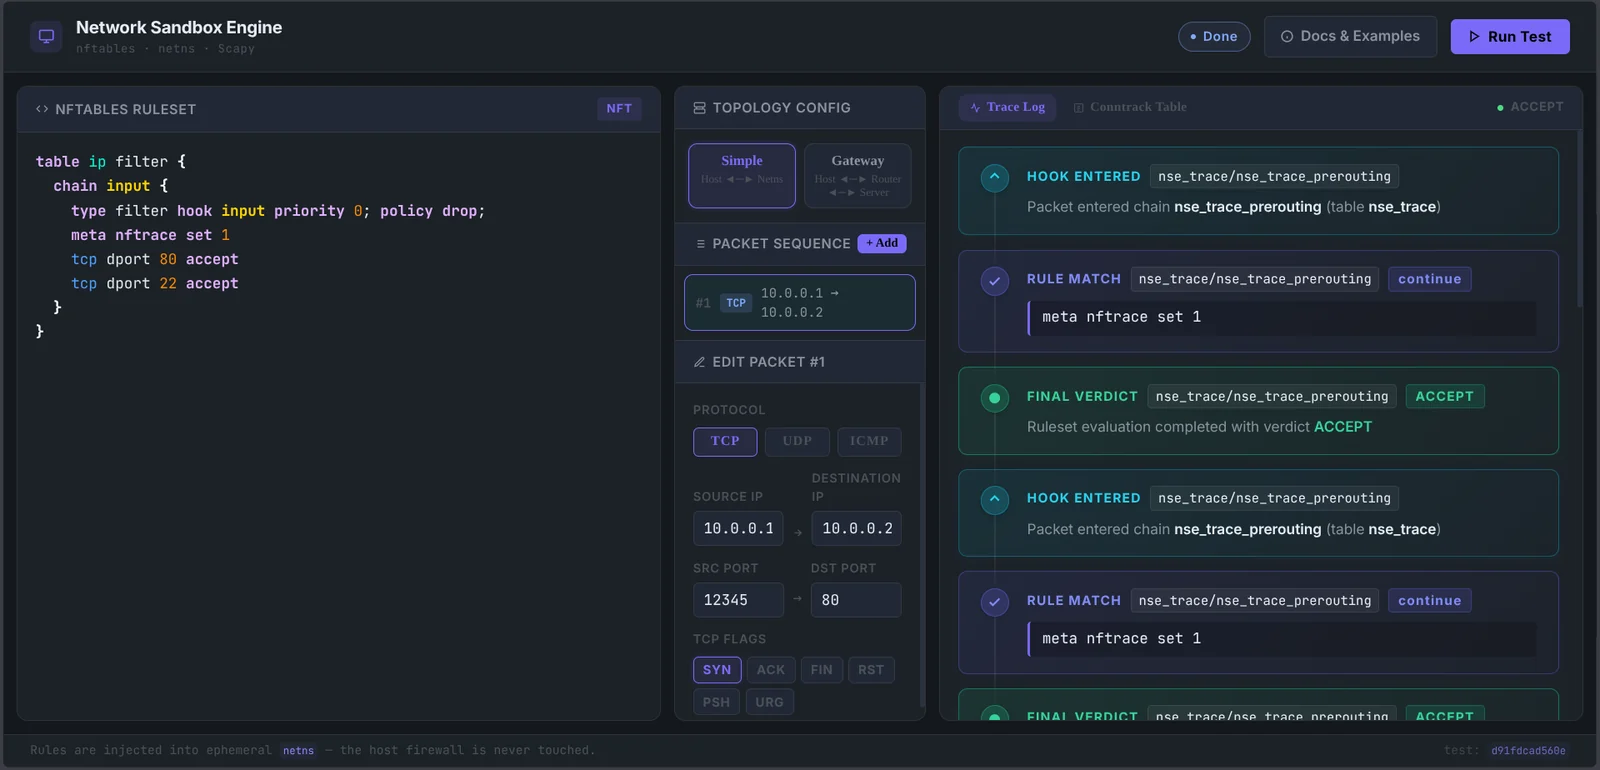 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…