
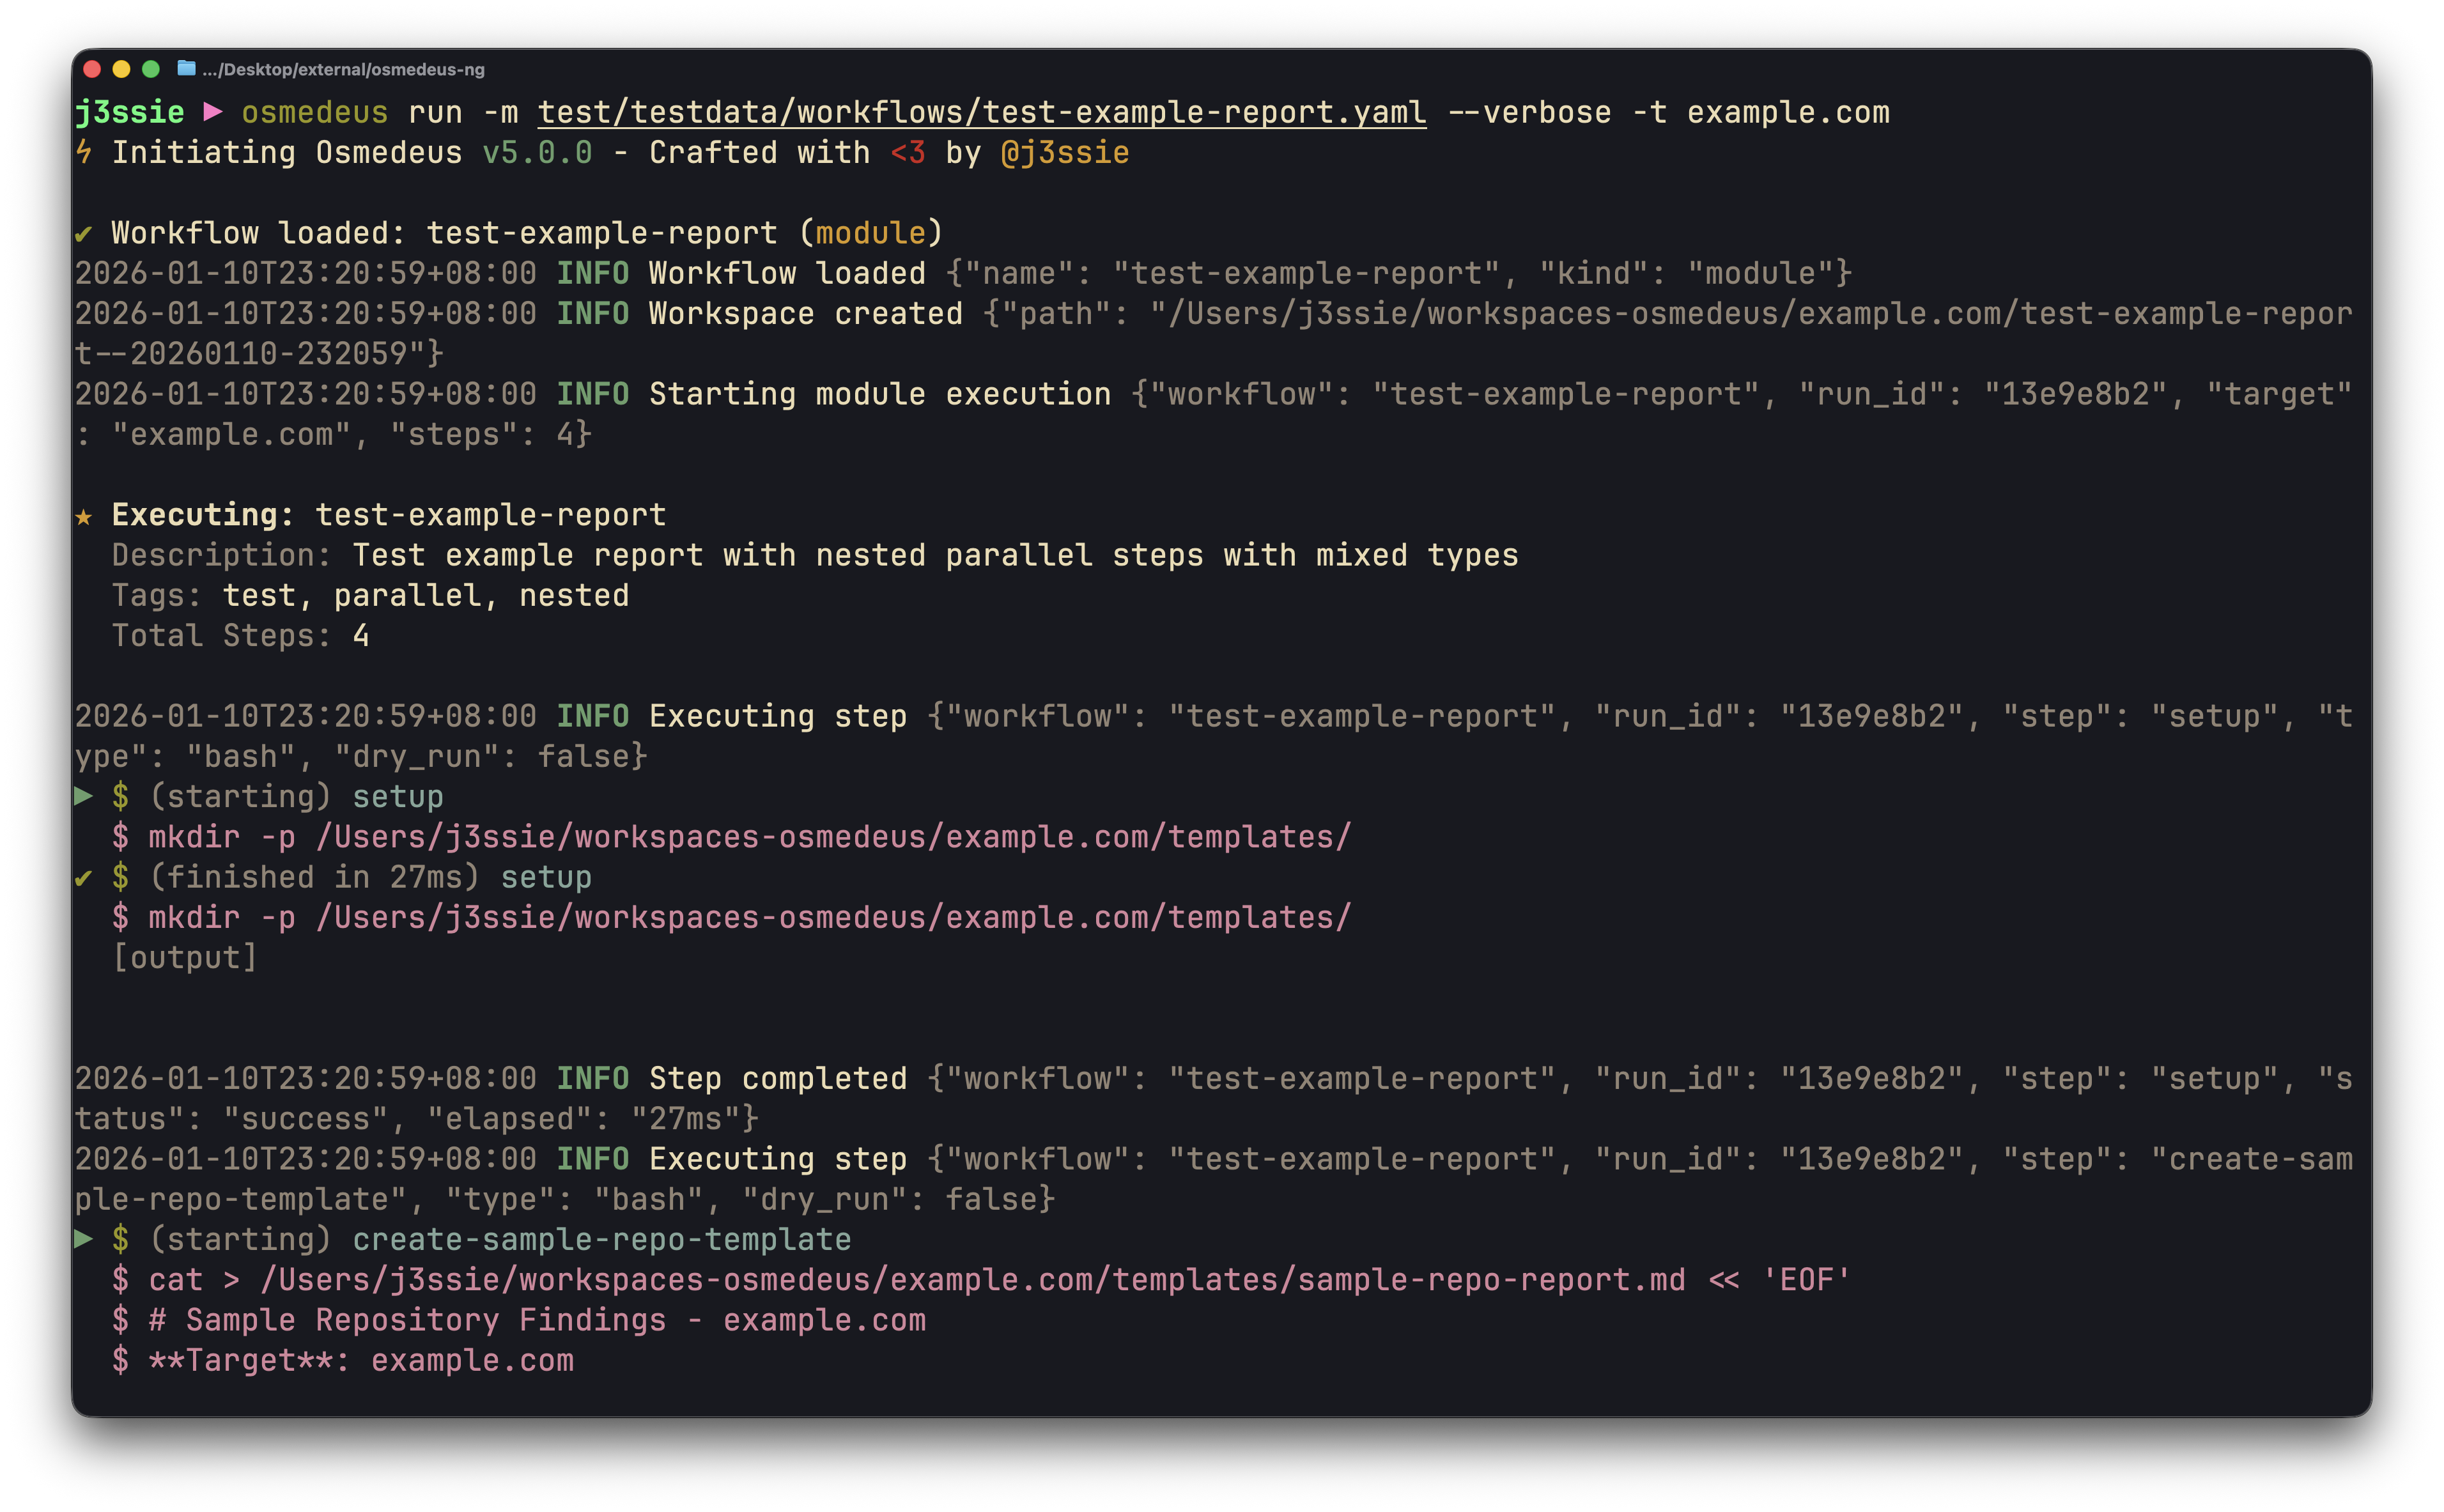
osmedeus
 j3ssie/osmedeus
A Modern Orchestration Engine for Security
cloud-securitydevsecopsinformation-gathering+5
j3ssie/osmedeusA Modern Orchestration Engine for Security
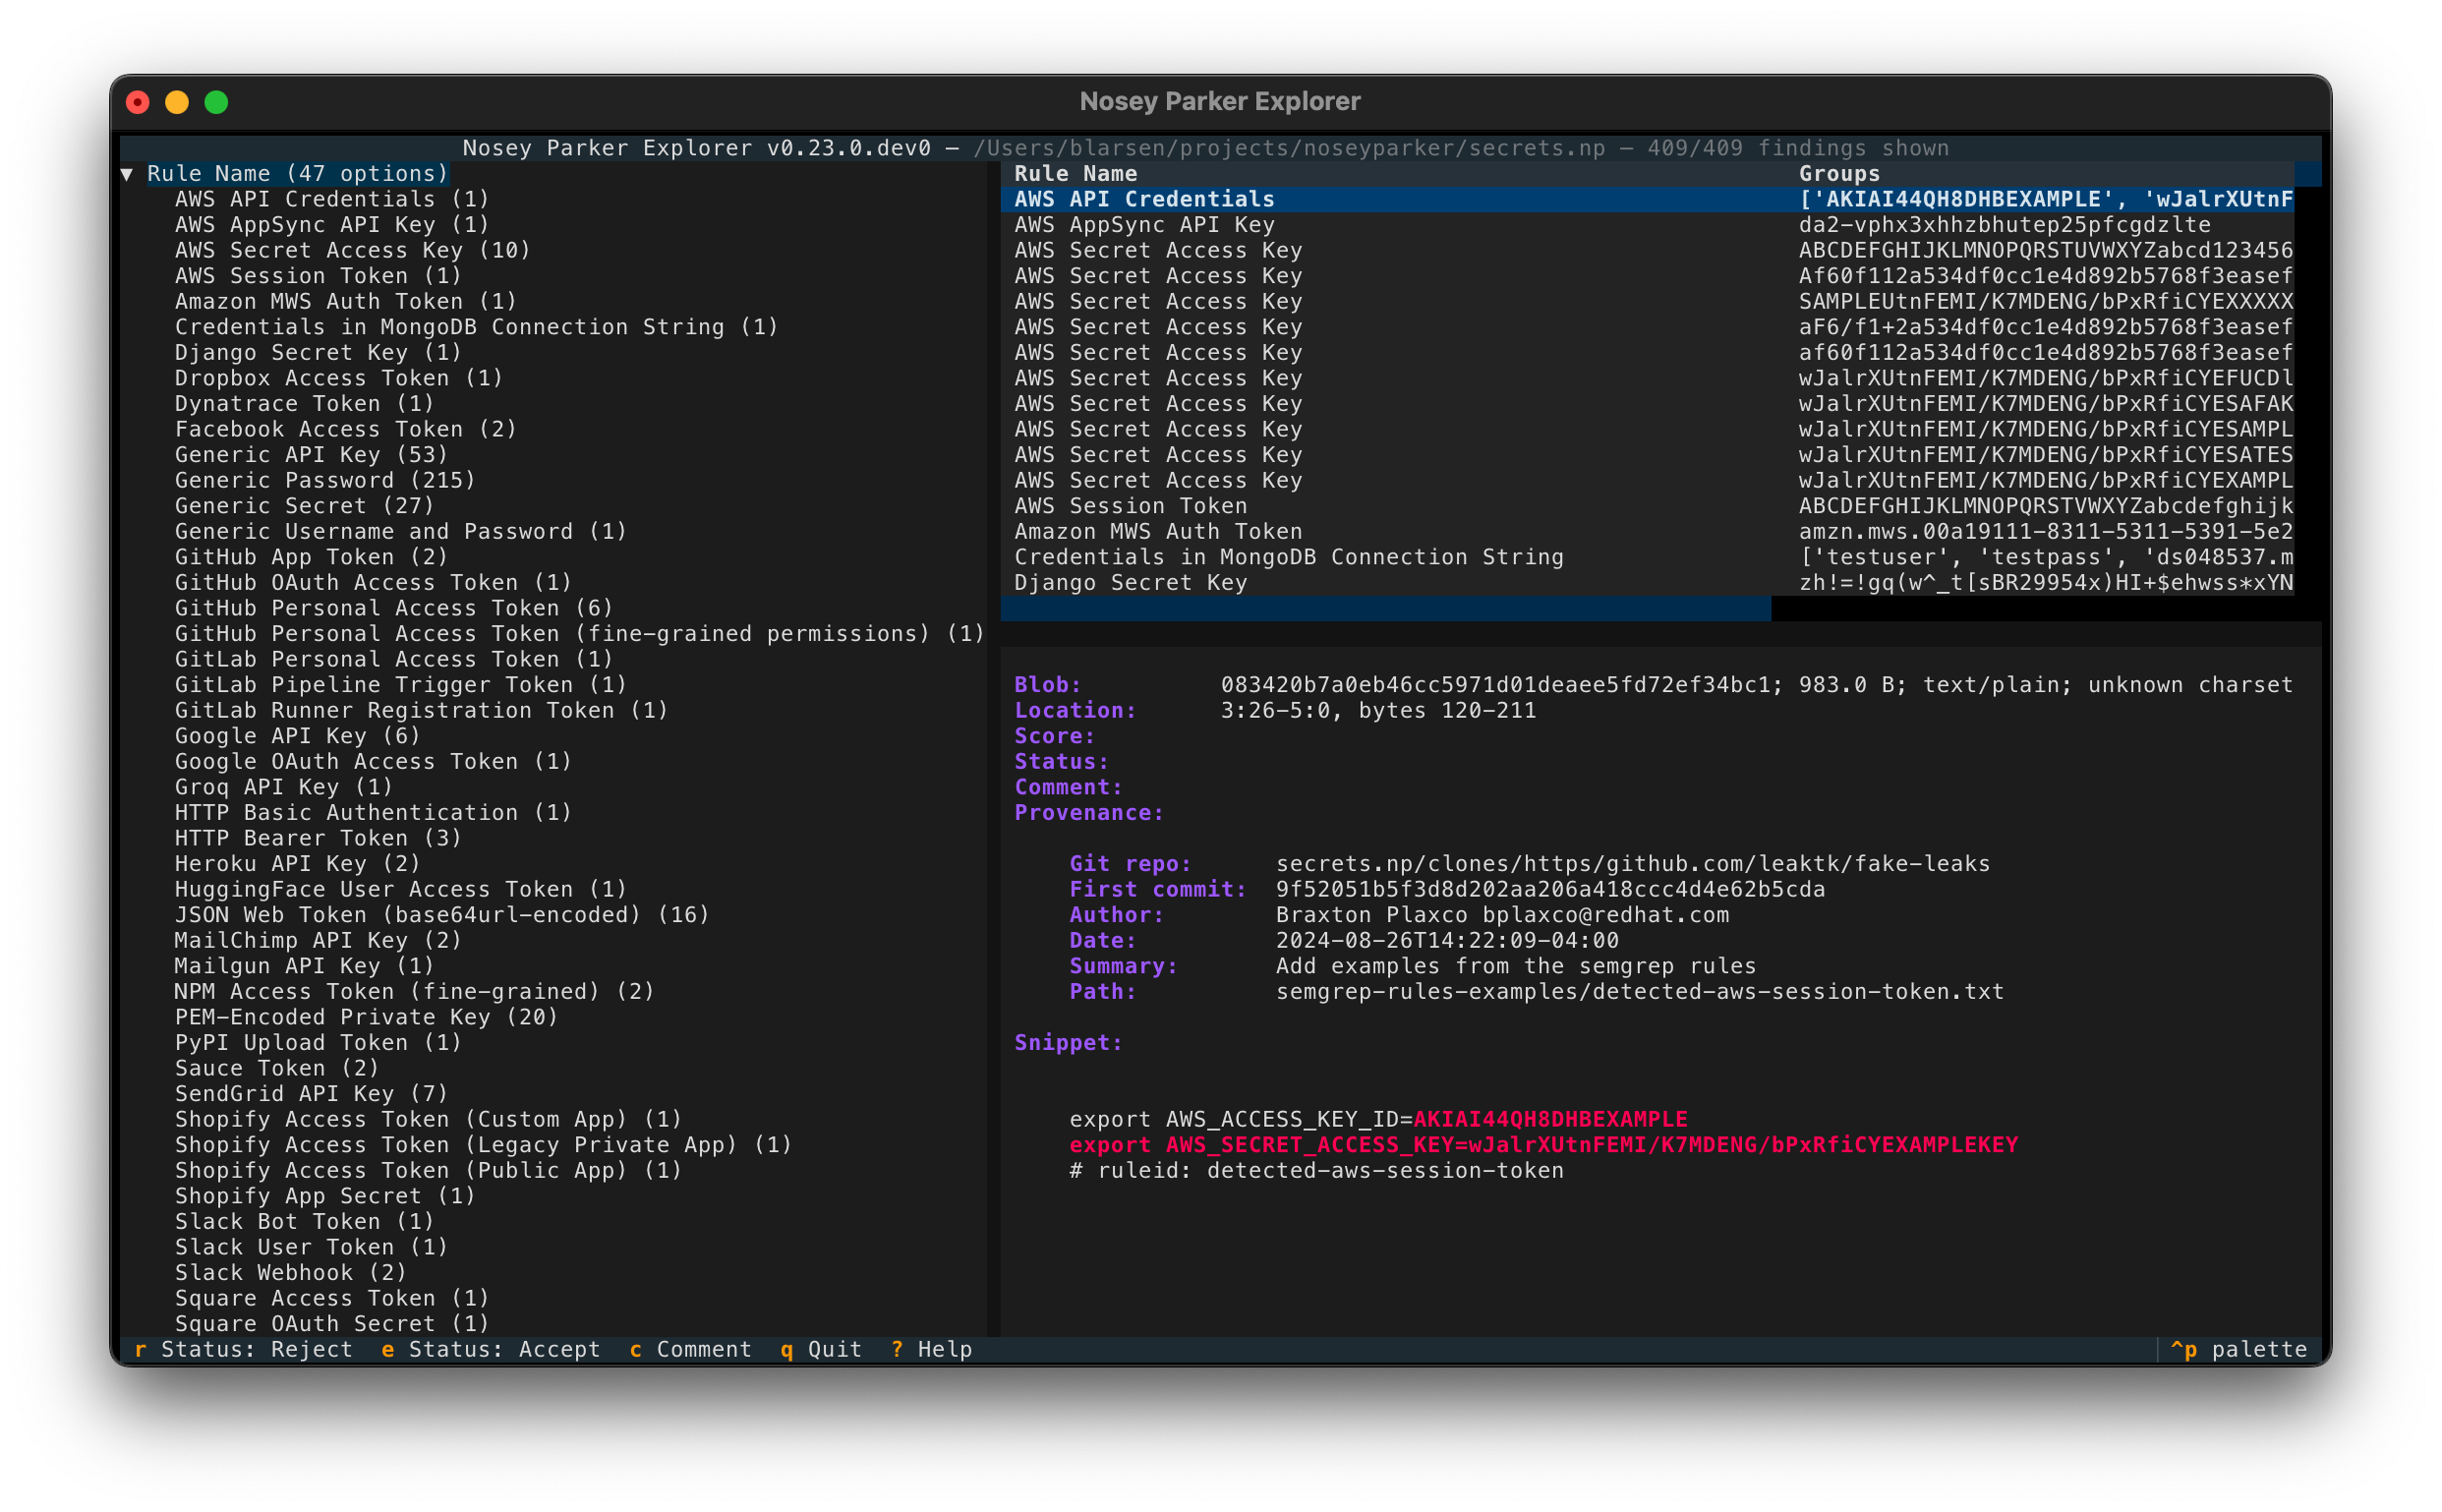 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 fazmin/cve-intel
Local security intelligence for CVE triage — 31 tools, 25 sources, risk scores and an MCP server for AI agents, all in native Rust. Private by…
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 eth0izzle/shhgit
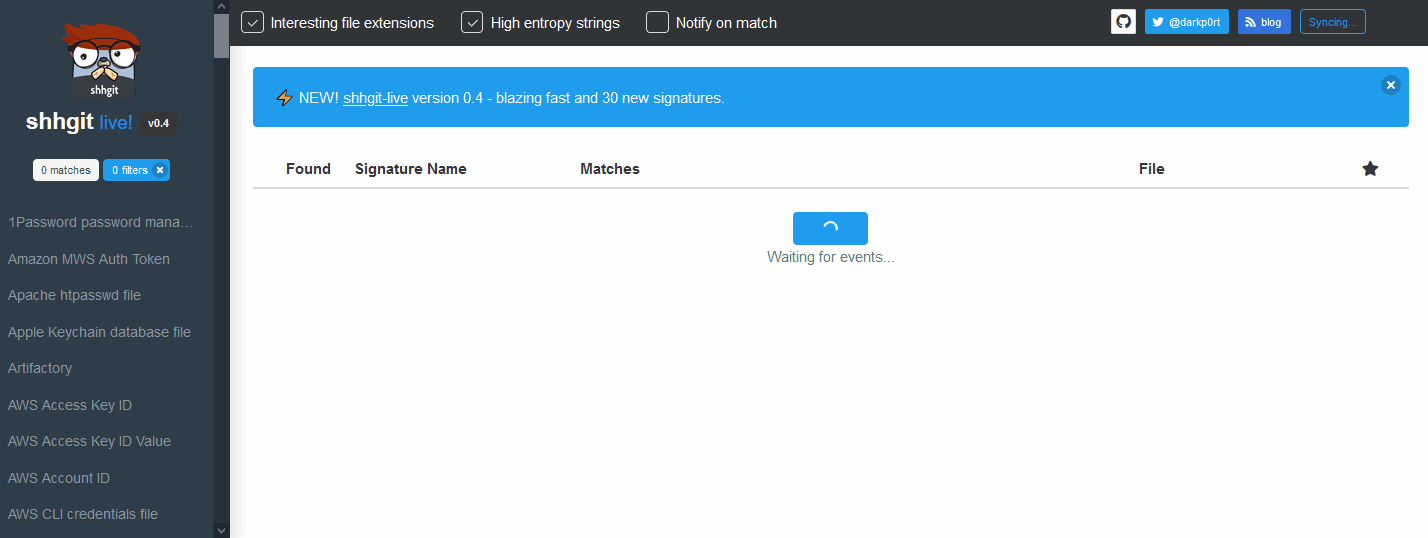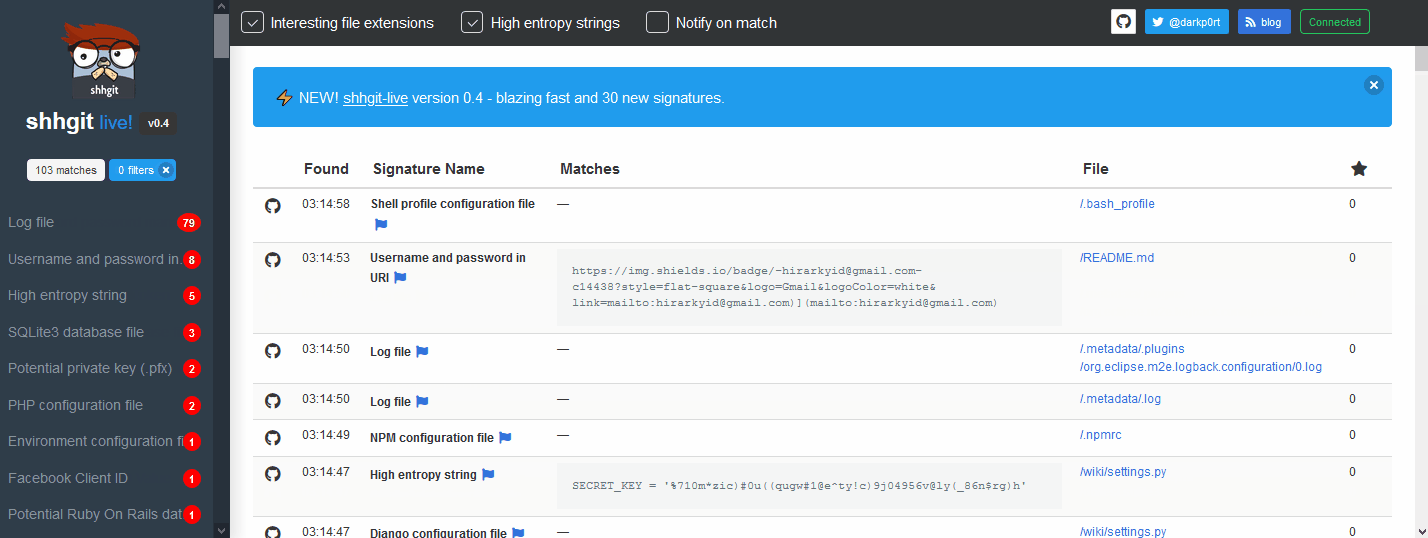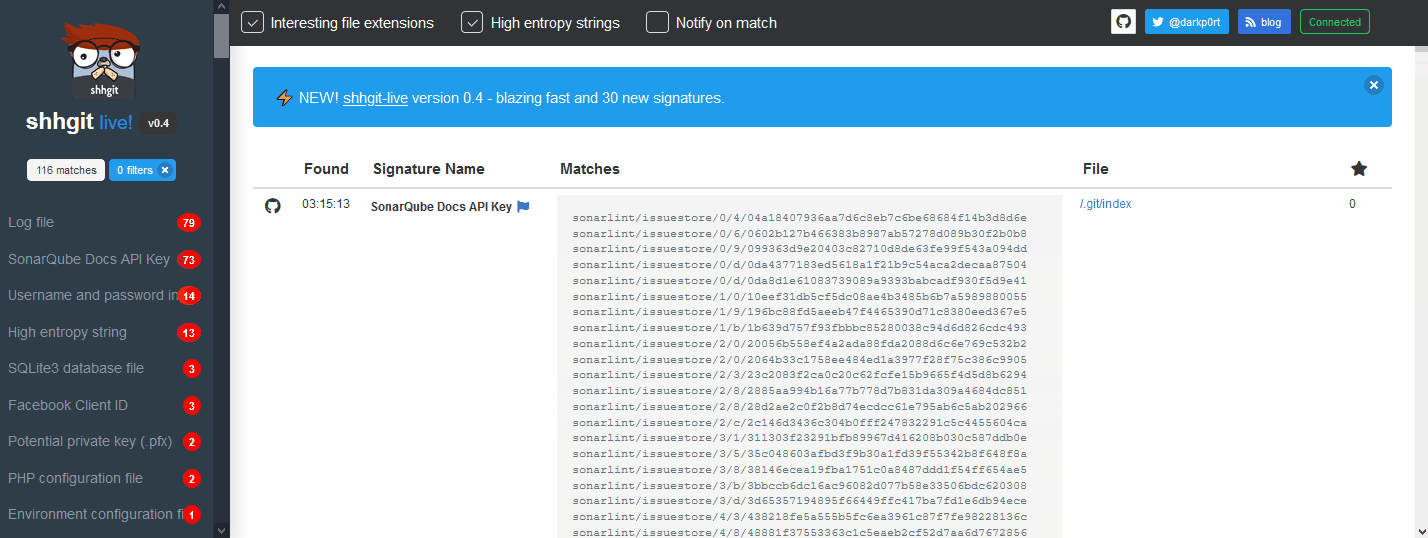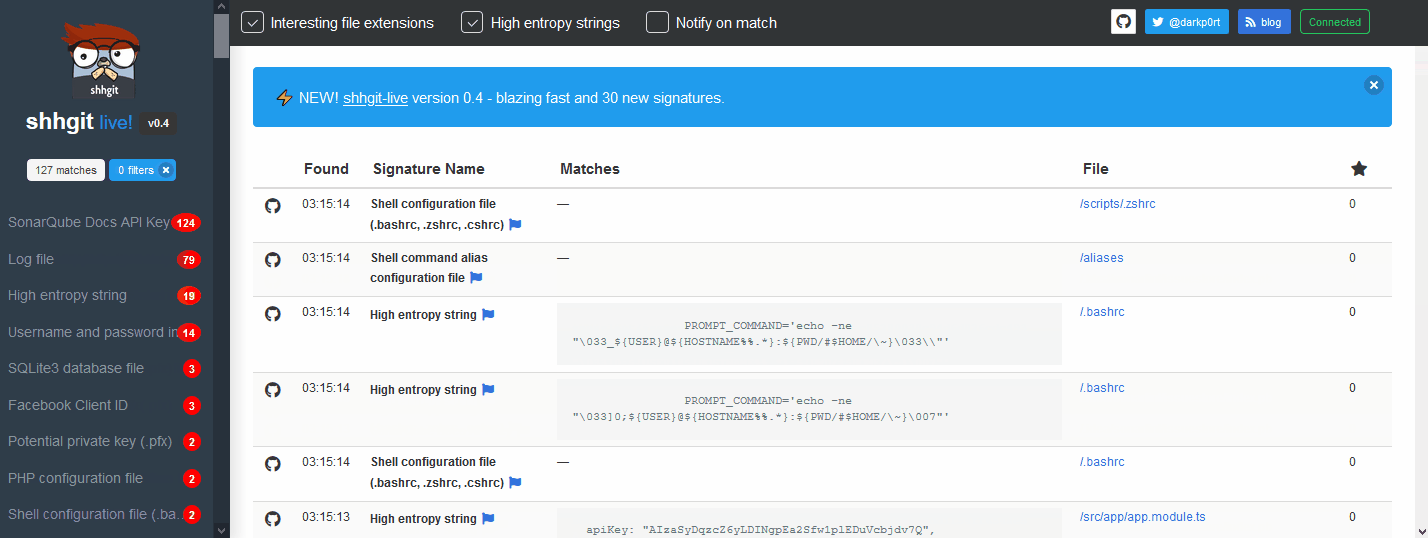
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 infobyte/faraday_agent_dispatcher
Faraday Agent Dispatcher launches any security tools and send results to Faradaysec Platform.
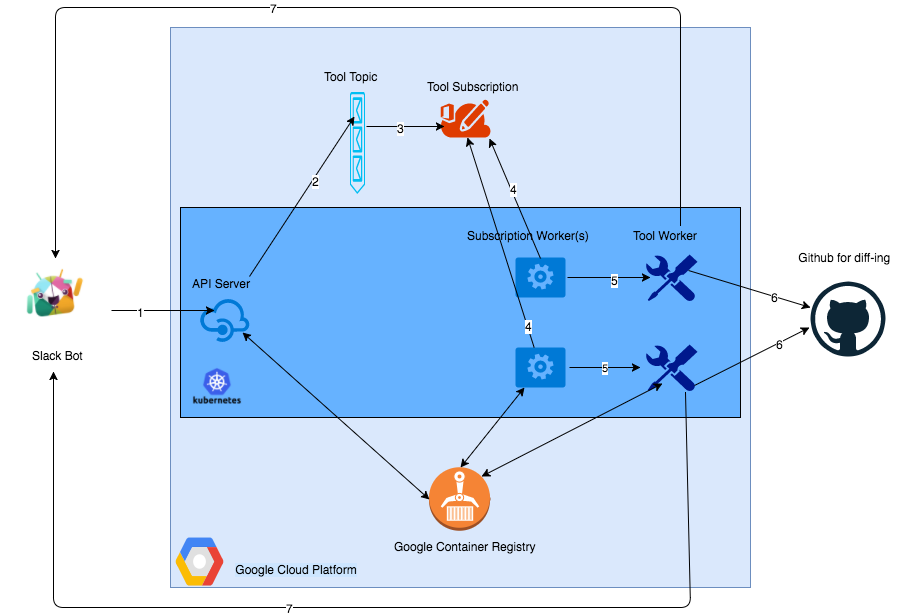 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
 projectdiscovery/httpx-action
HTTP Web Server probing
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.