

faraday
 infobyte/faraday
Open Source Vulnerability Management Platform
api-securitydevsecopspenetration-testing+1
infobyte/faradayOpen Source Vulnerability Management Platform
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
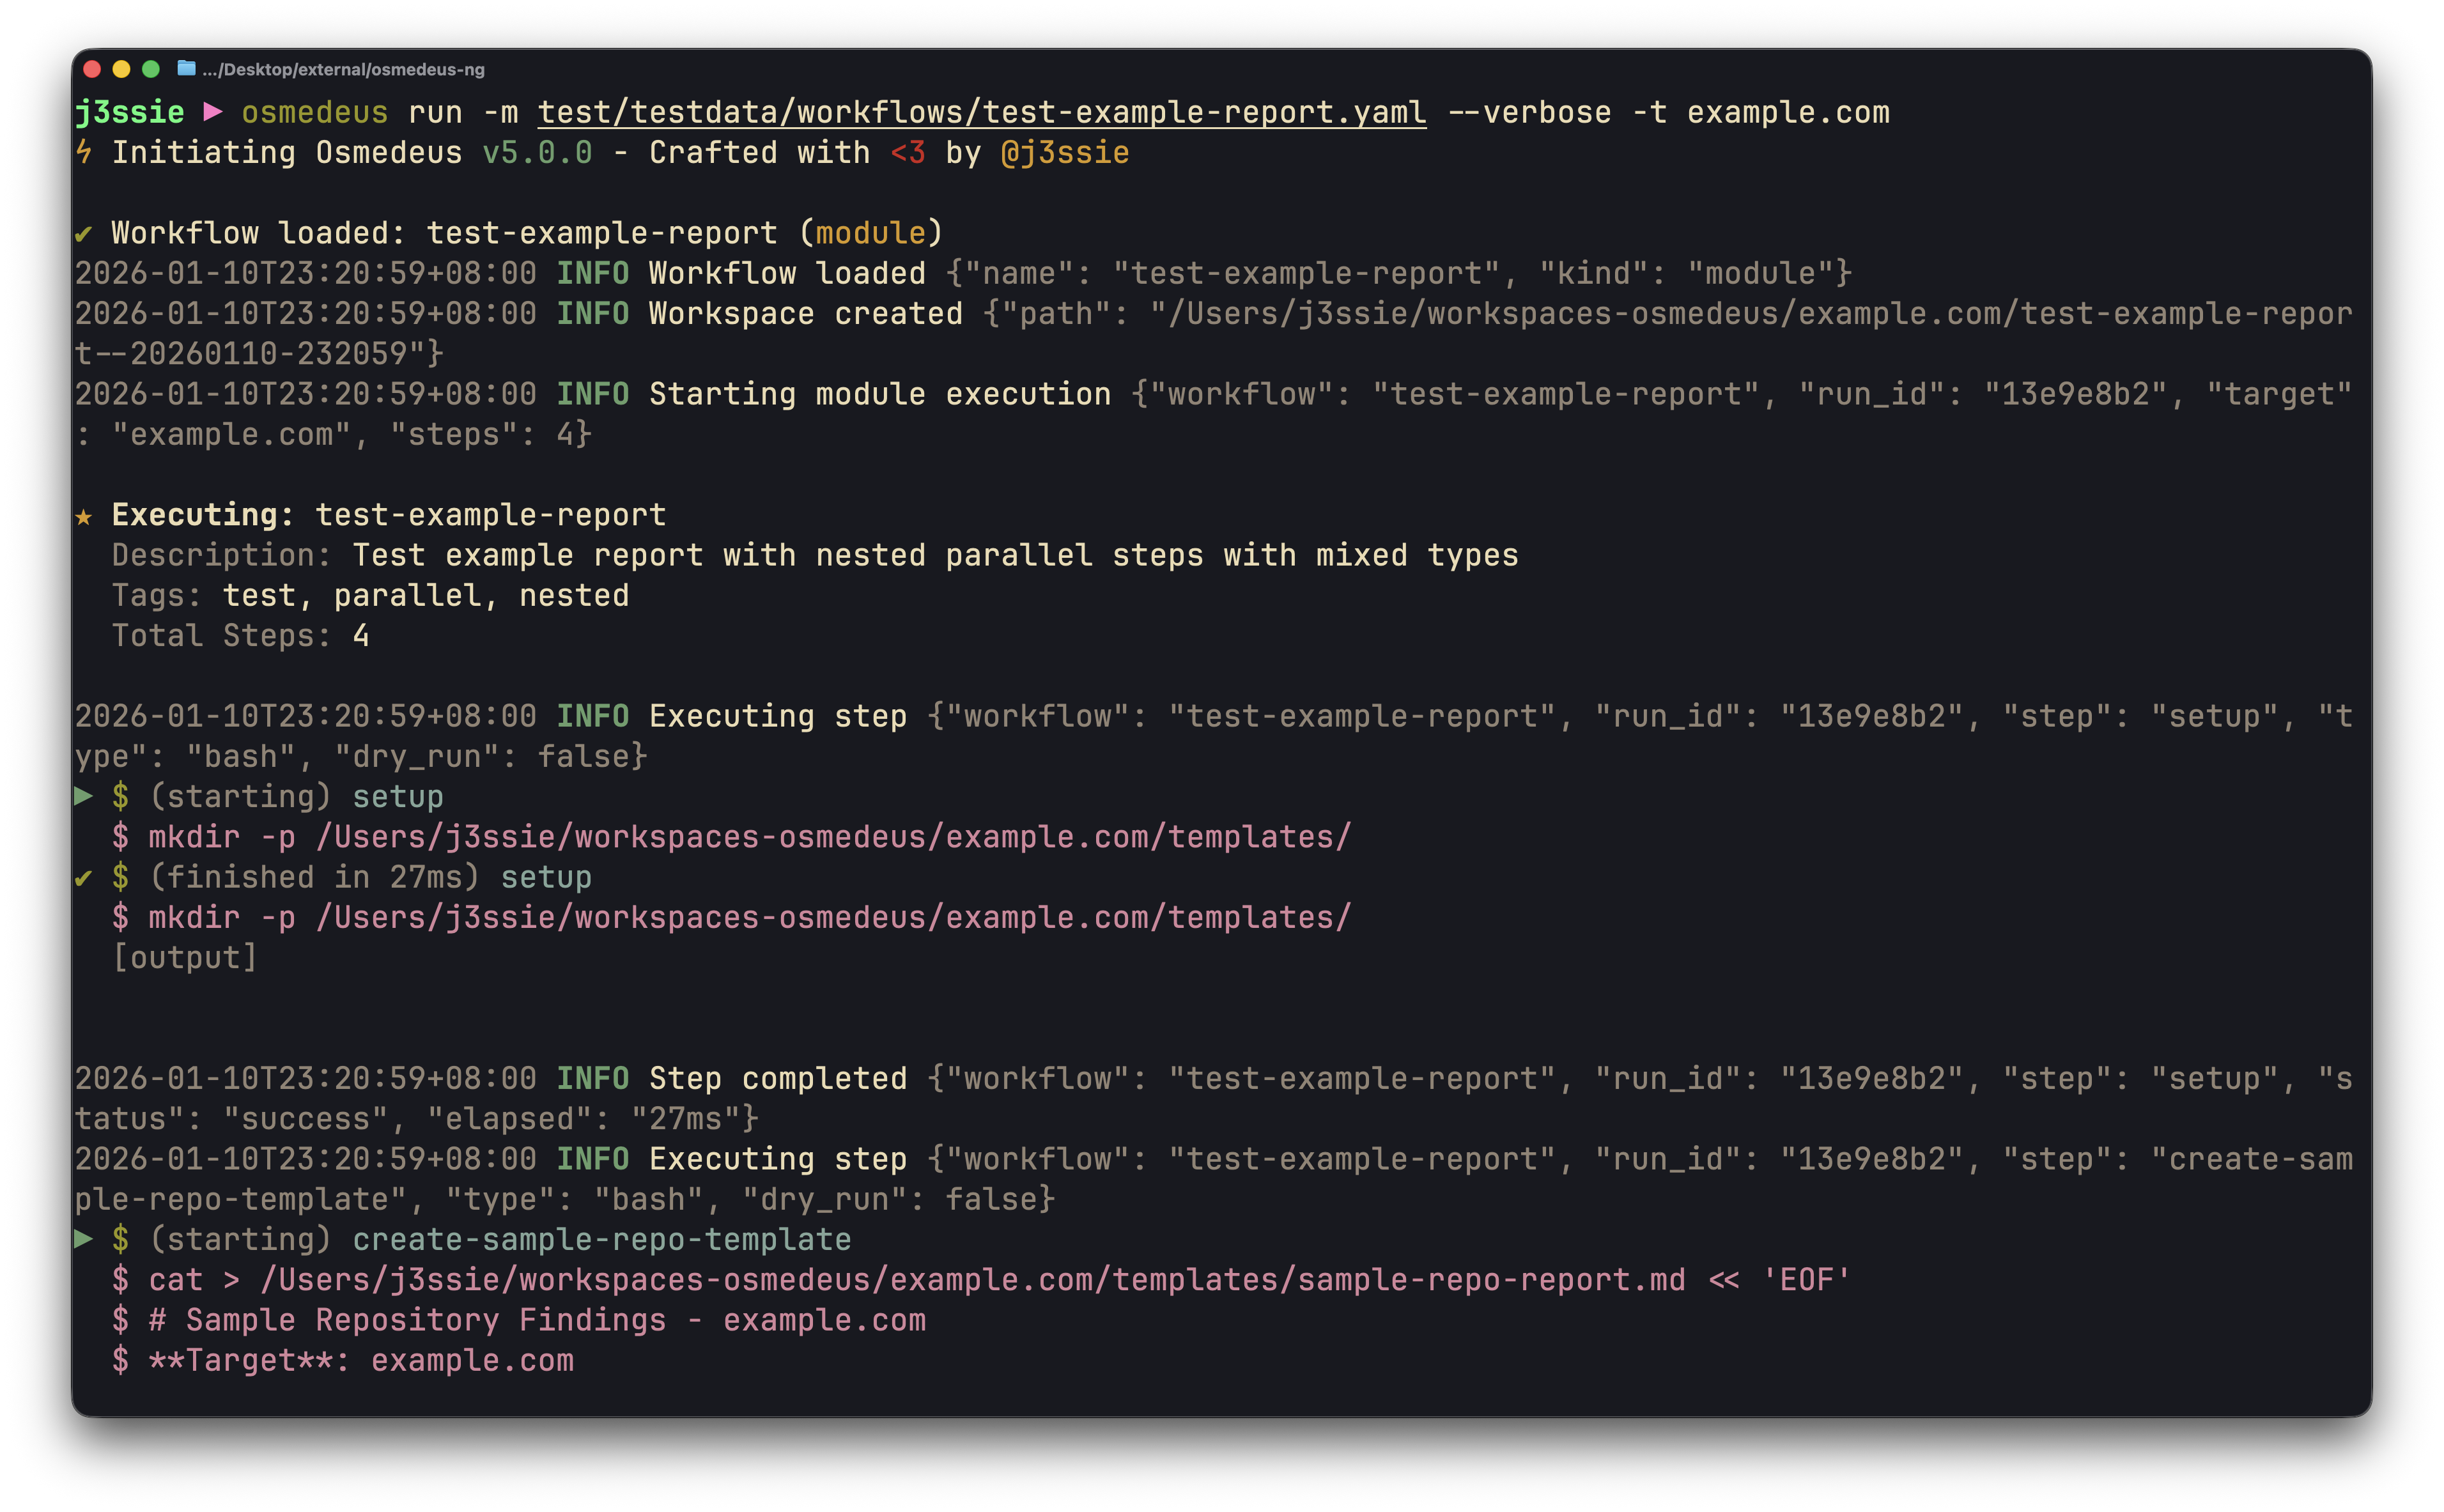 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
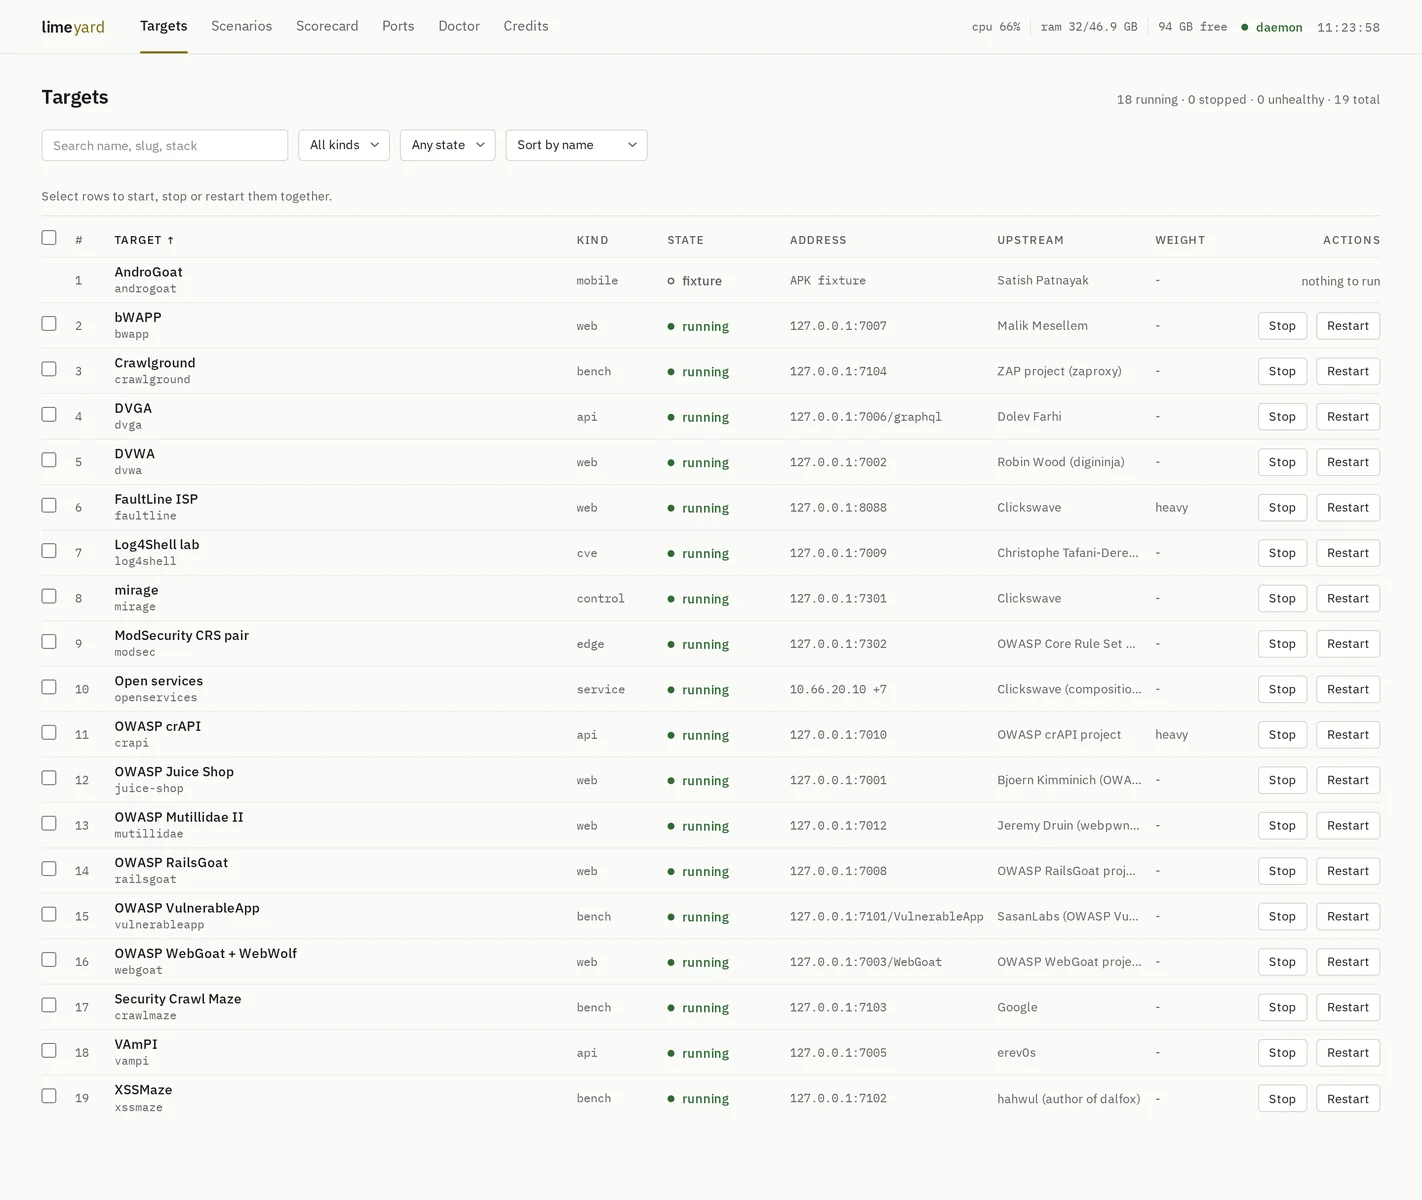 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
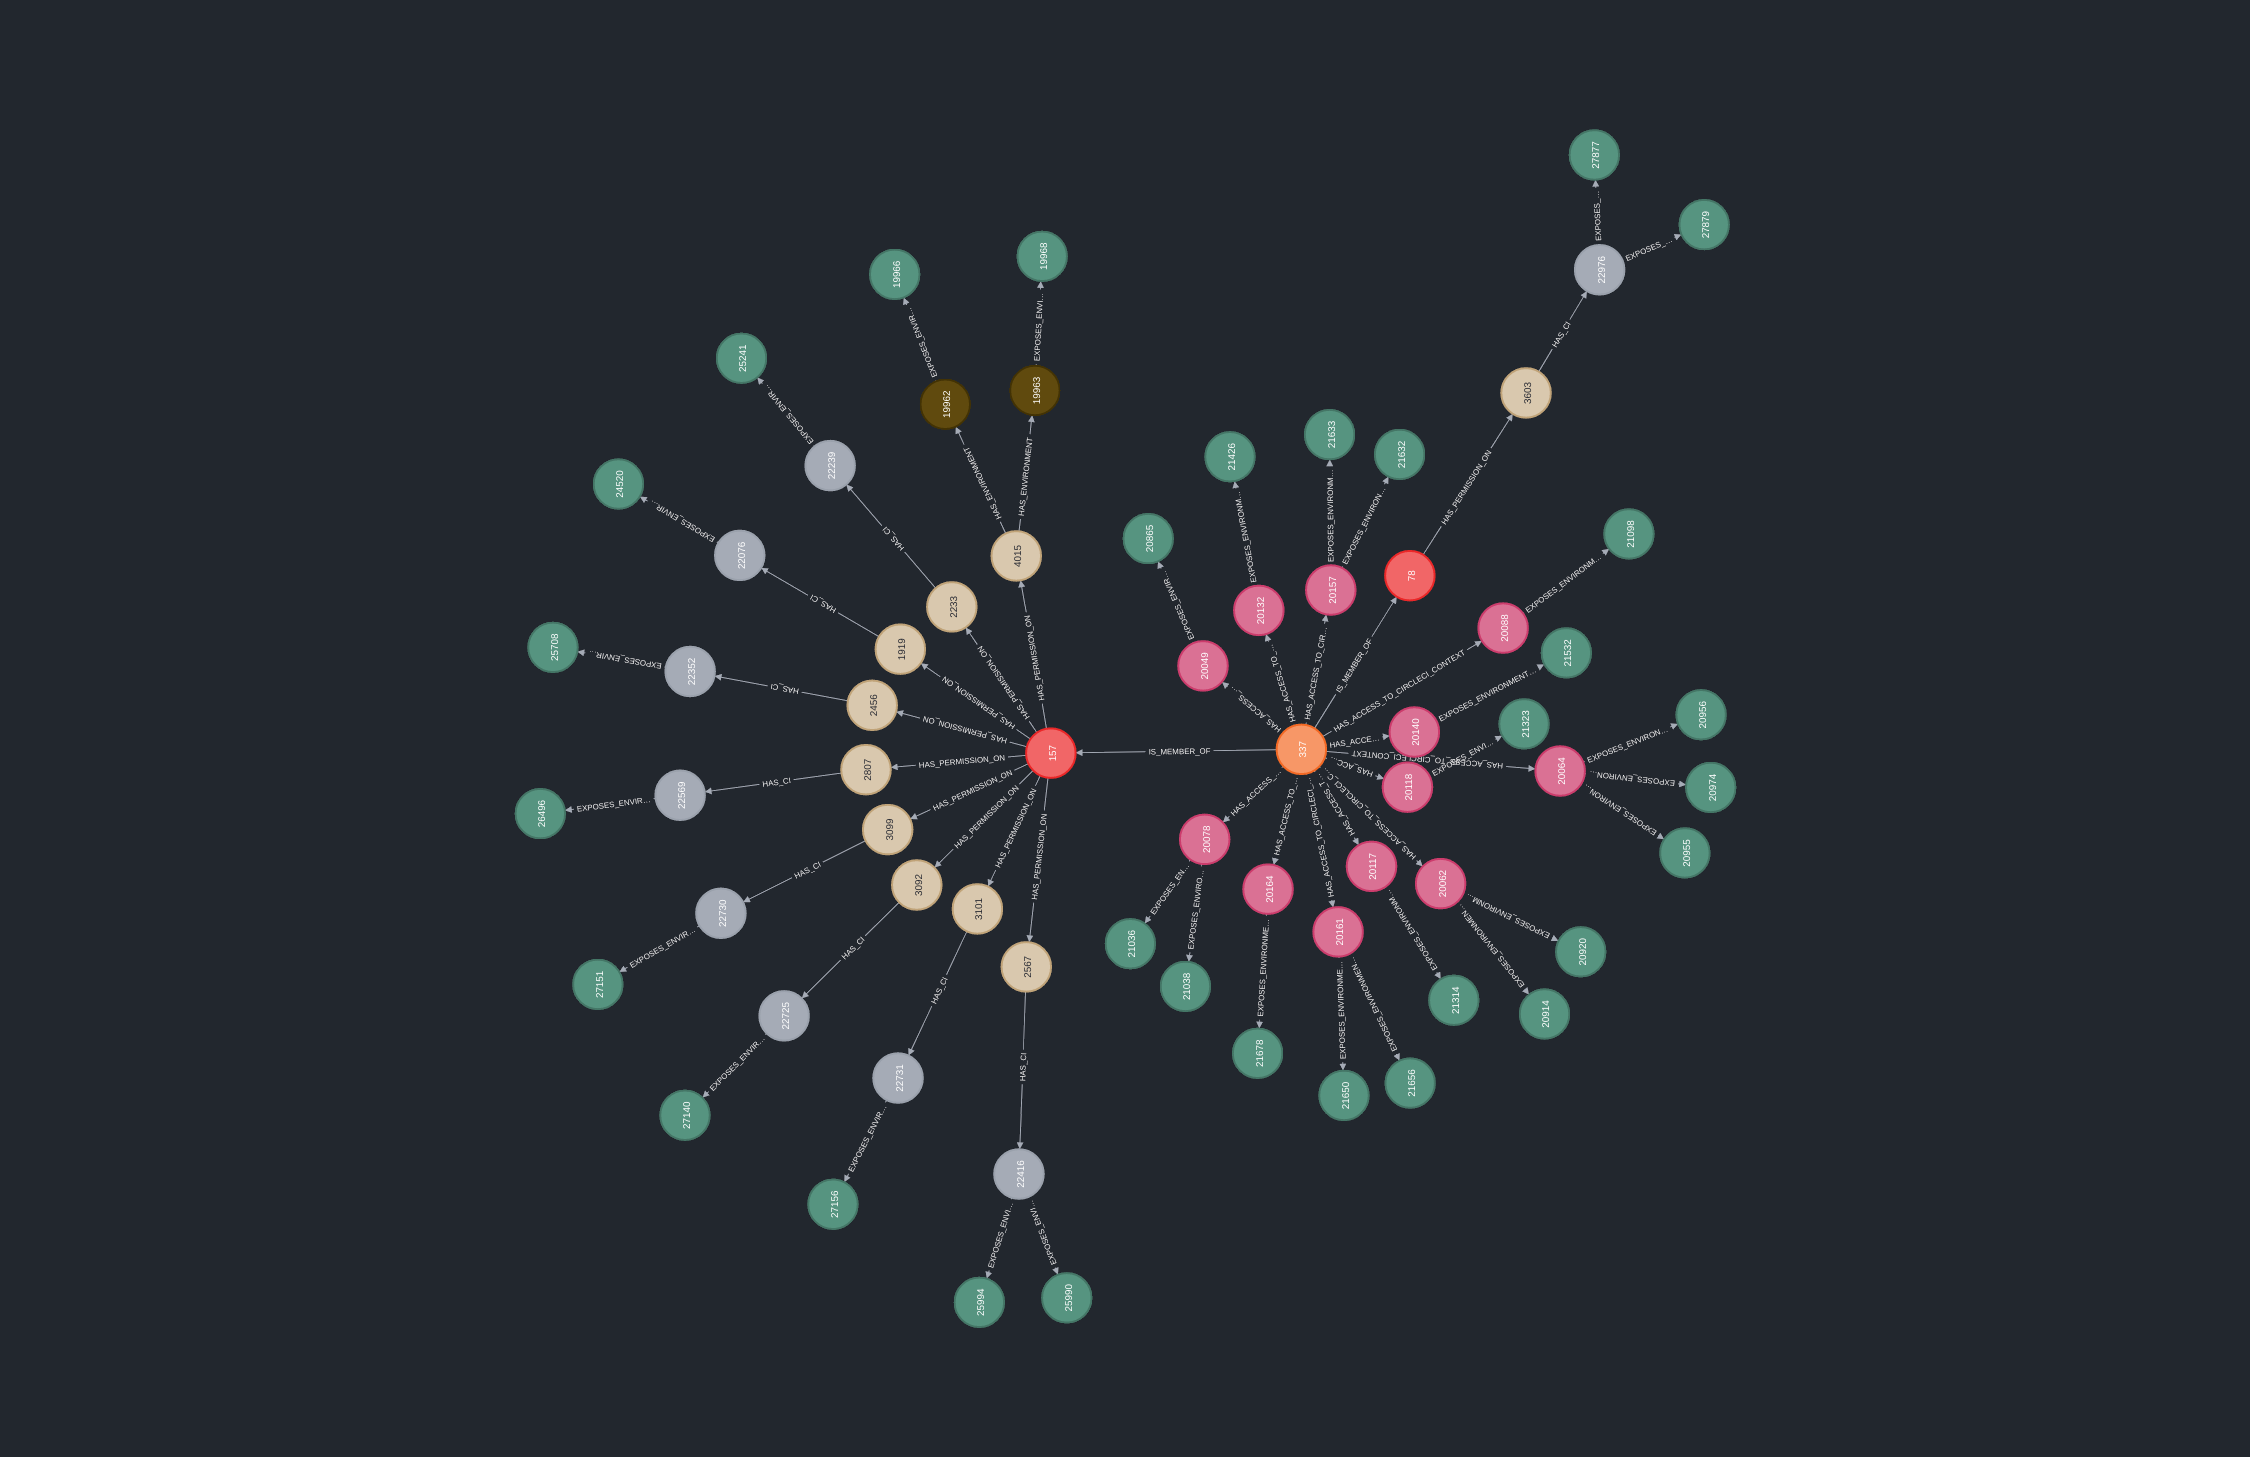
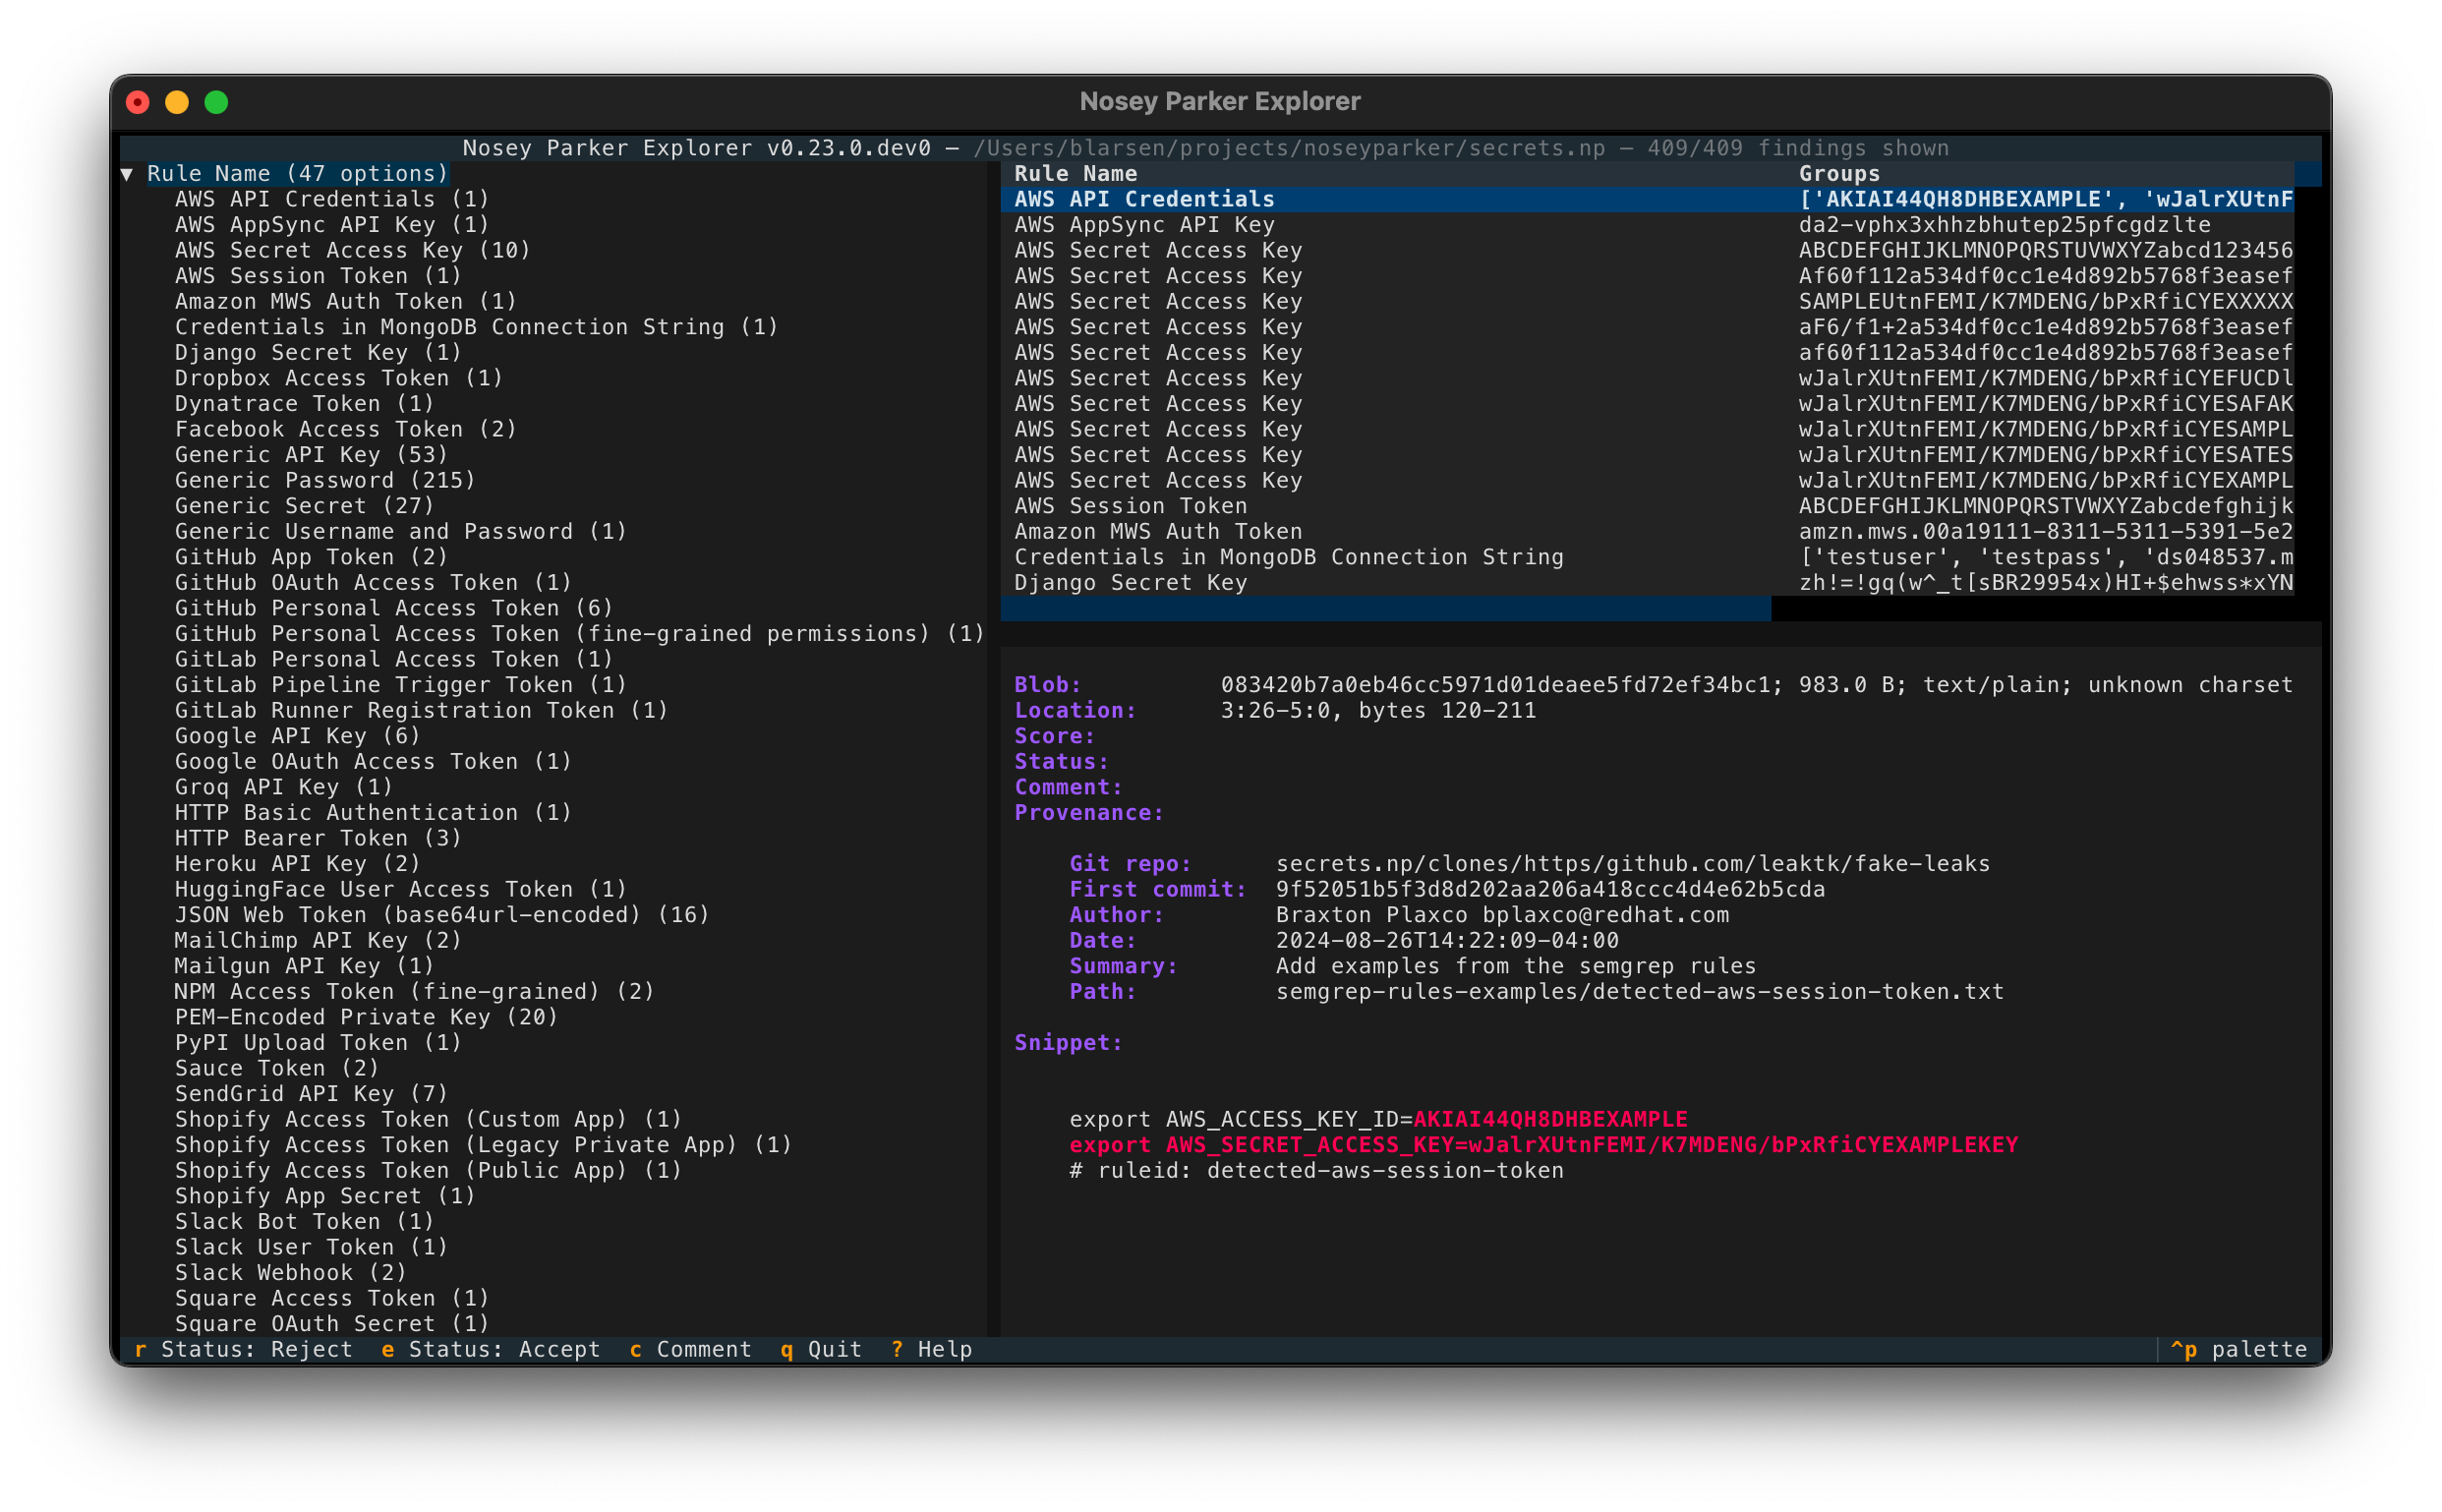 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
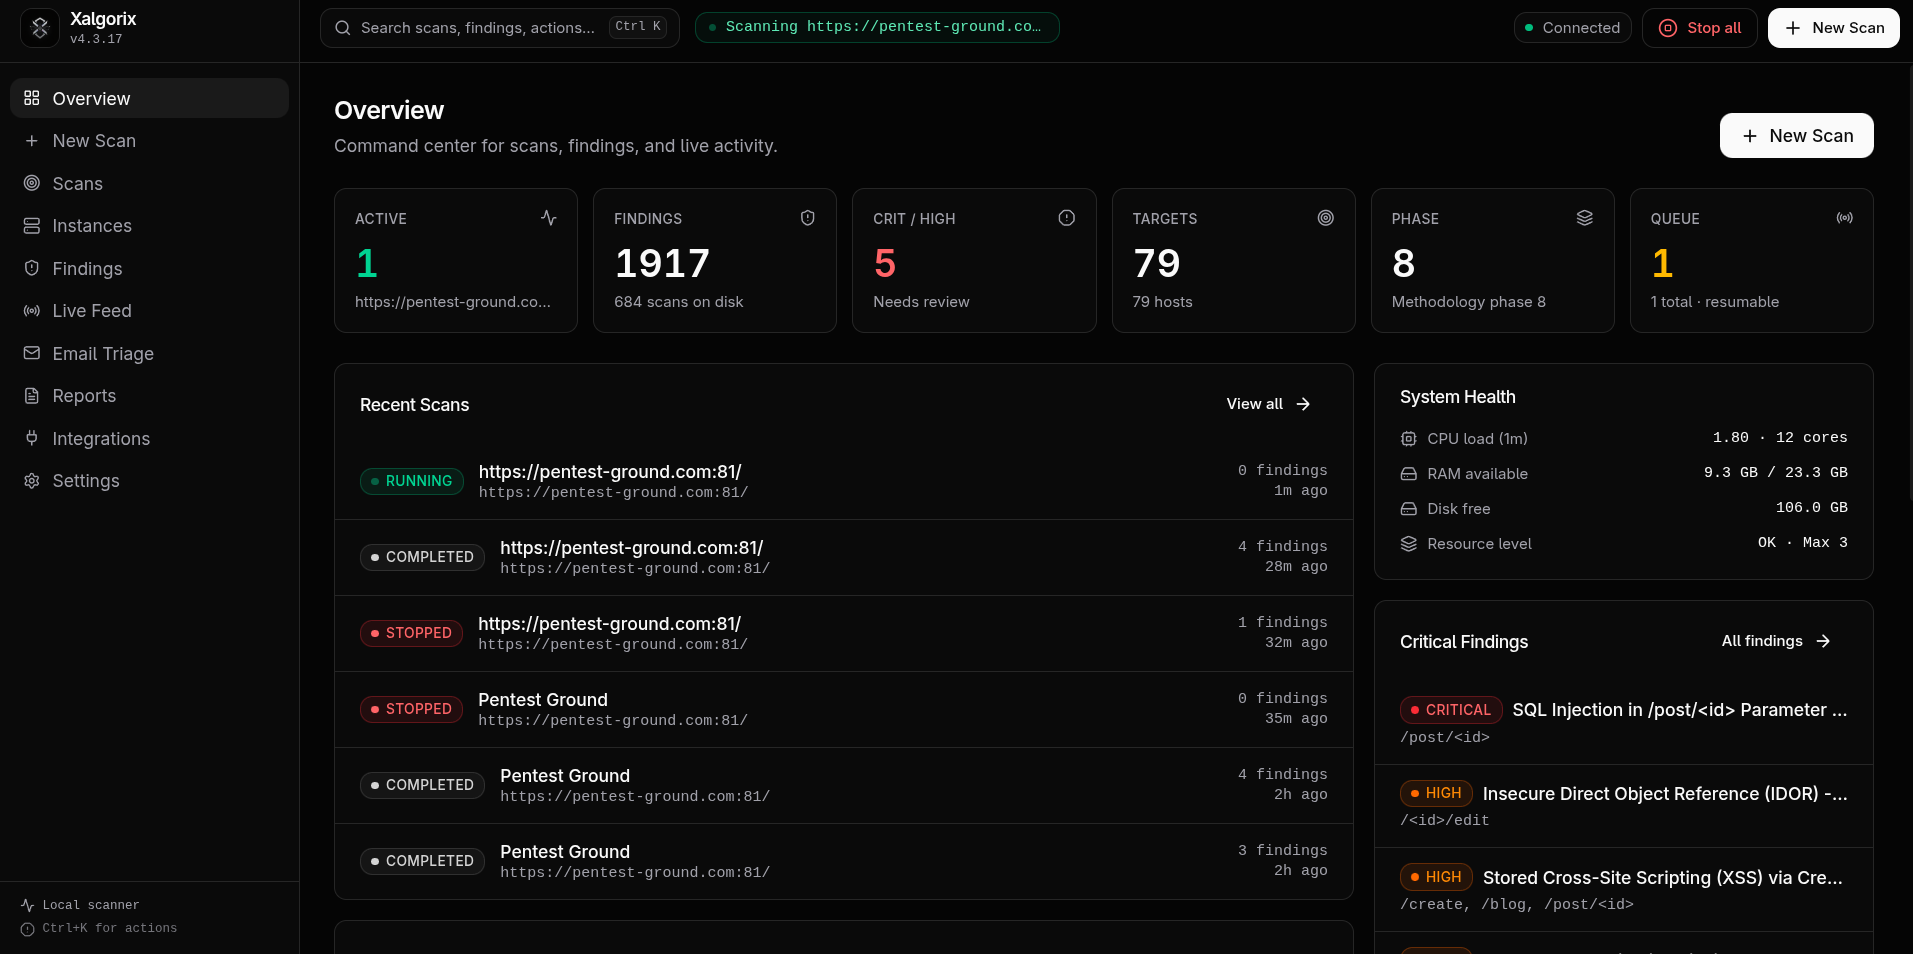 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…