

DakshSCRA
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
code-analysisdevsecopseducation+7
45
coffeeandsecurity/dakshscraFramework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
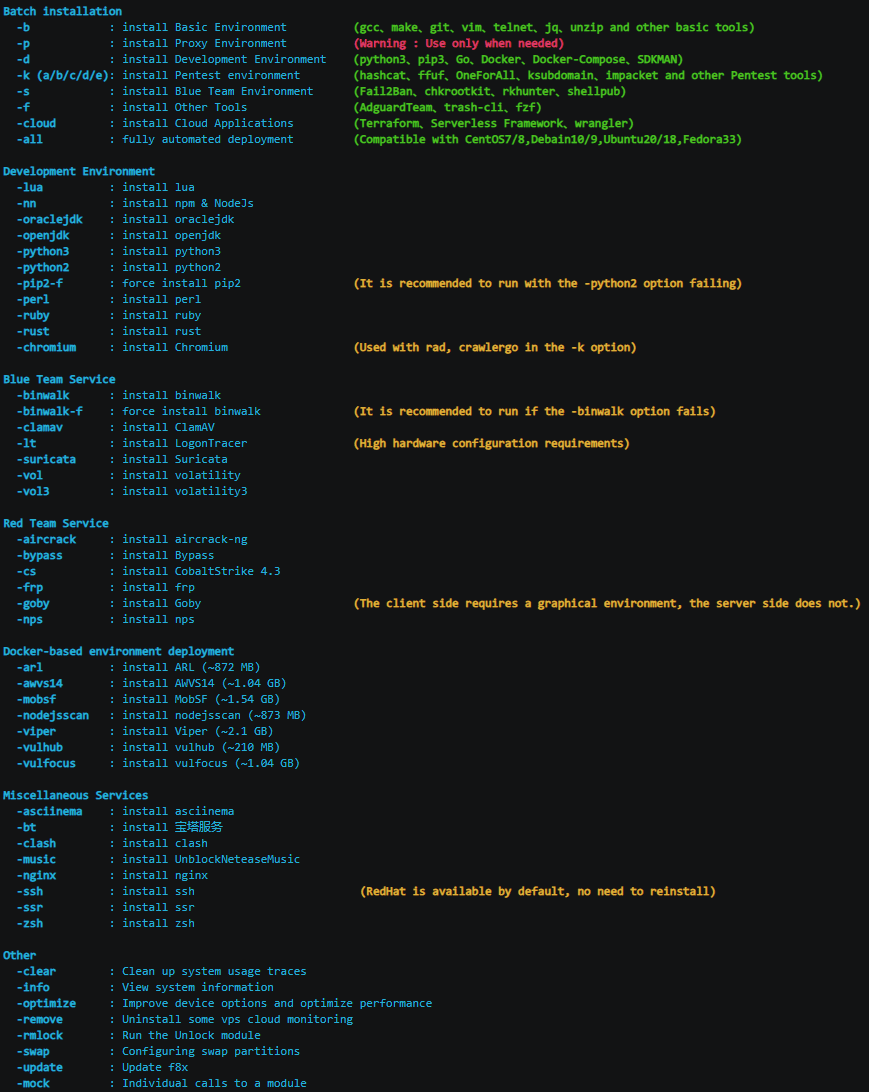 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 threatspec/threatspec
threatspec - continuous threat modeling, through code
 bridgecrewio/terragoat
Intentionally vulnerable Terraform infrastructure for learning cloud misconfiguration detection and DevSecOps practices across AWS, Azure, and GCP.
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 threatcl/threatcl
Documenting your Threat Models with HCL
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
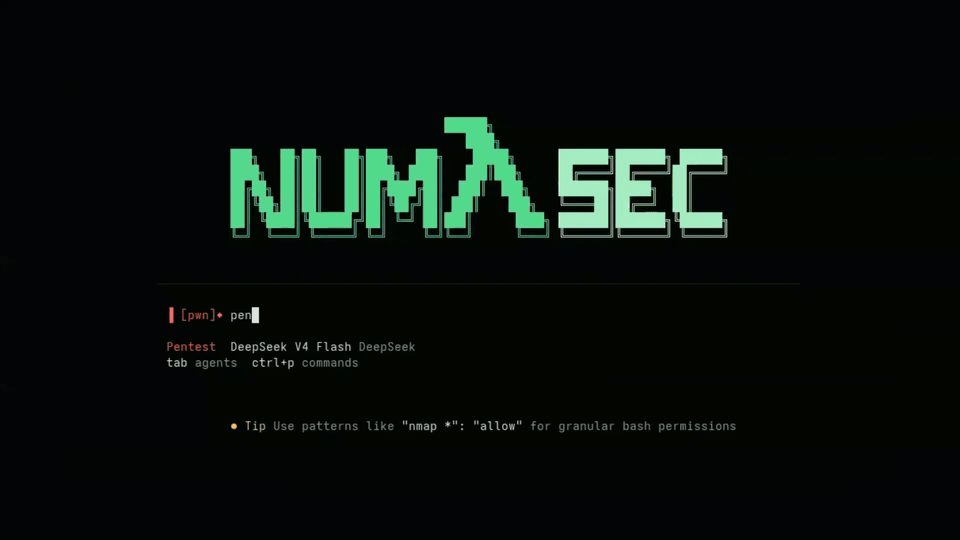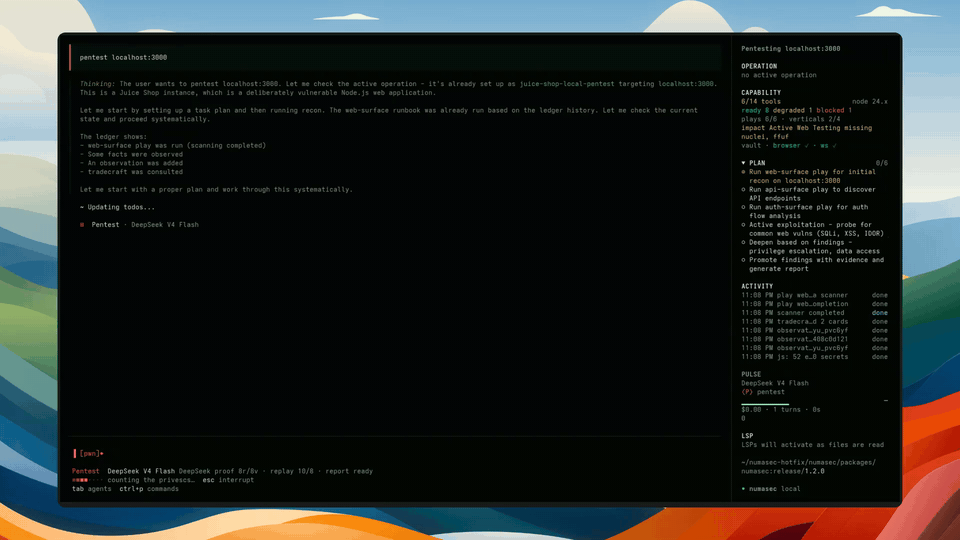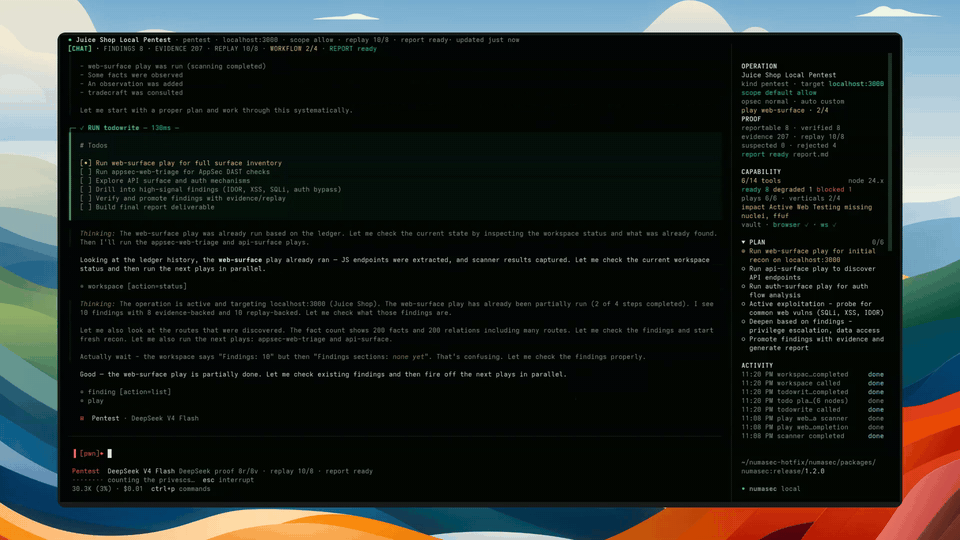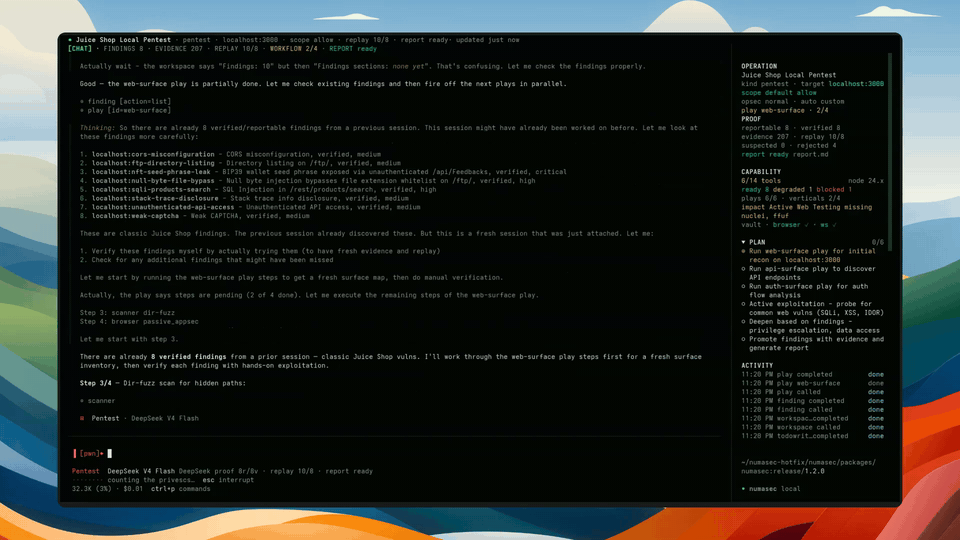 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…