
mzap
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
api-security-testingdevsecopsdynamic-analysis-sandboxing+3
hahwul/mzap⚡️ Multiple target ZAP Scanning
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
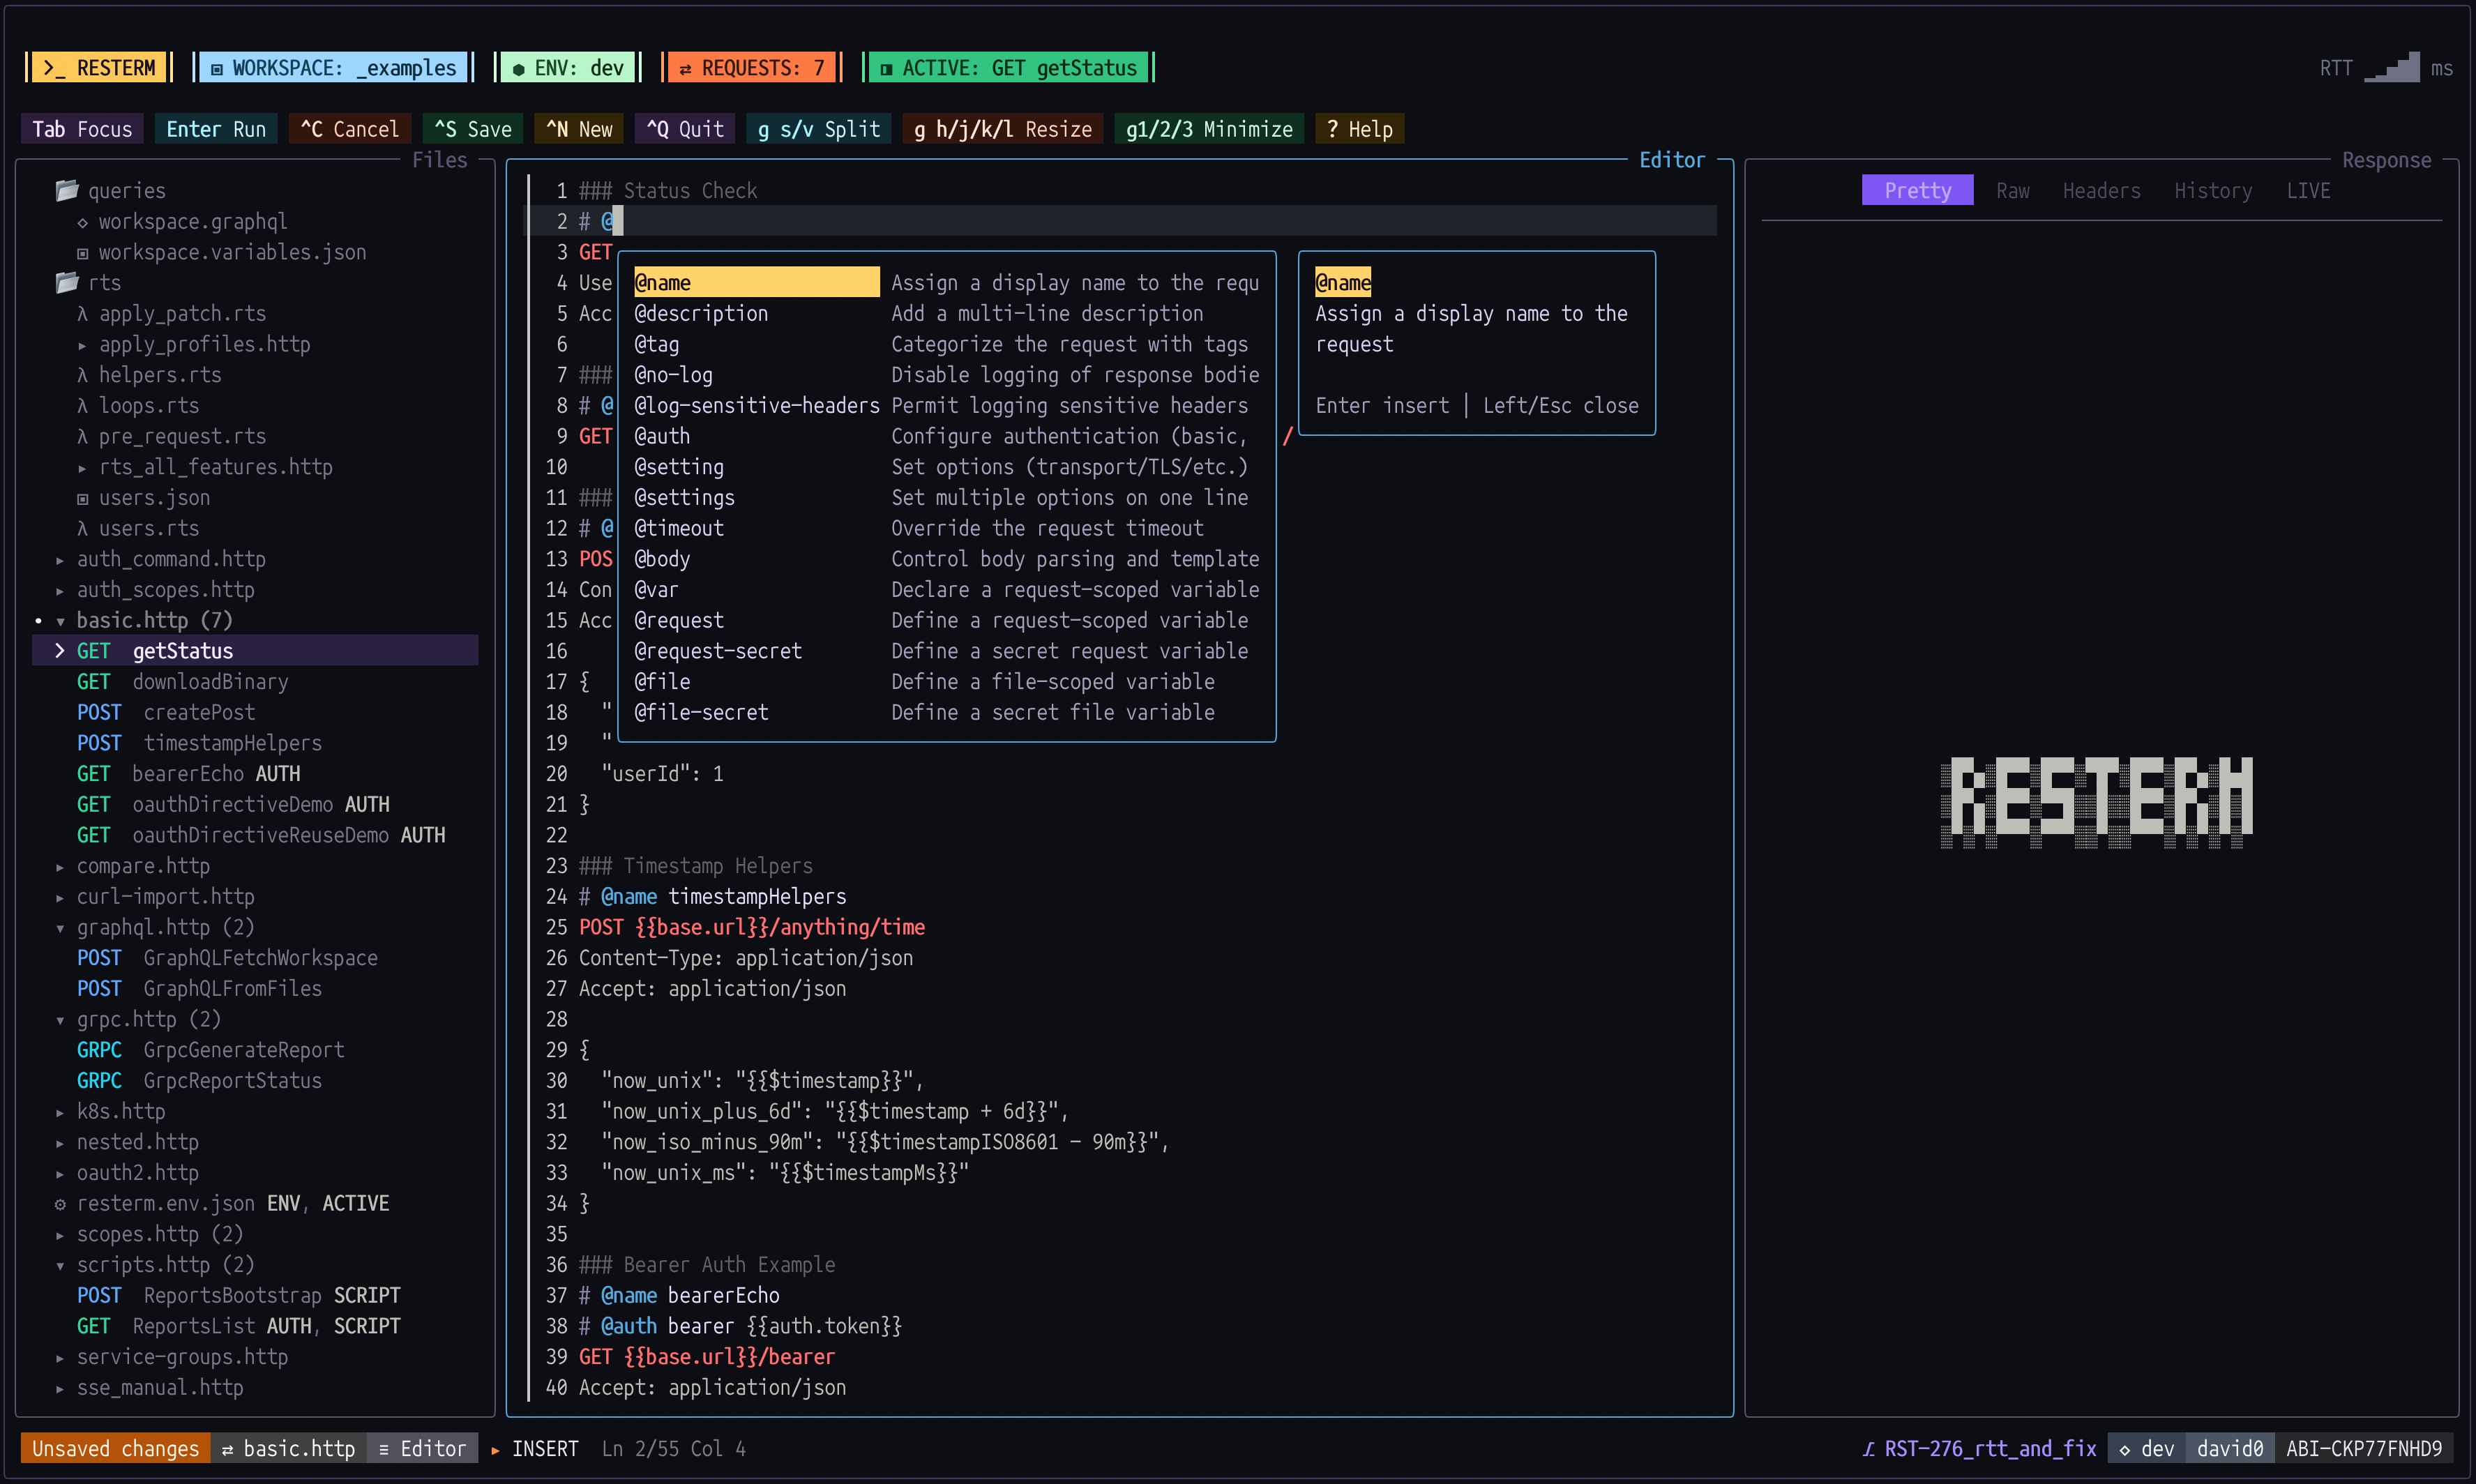 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
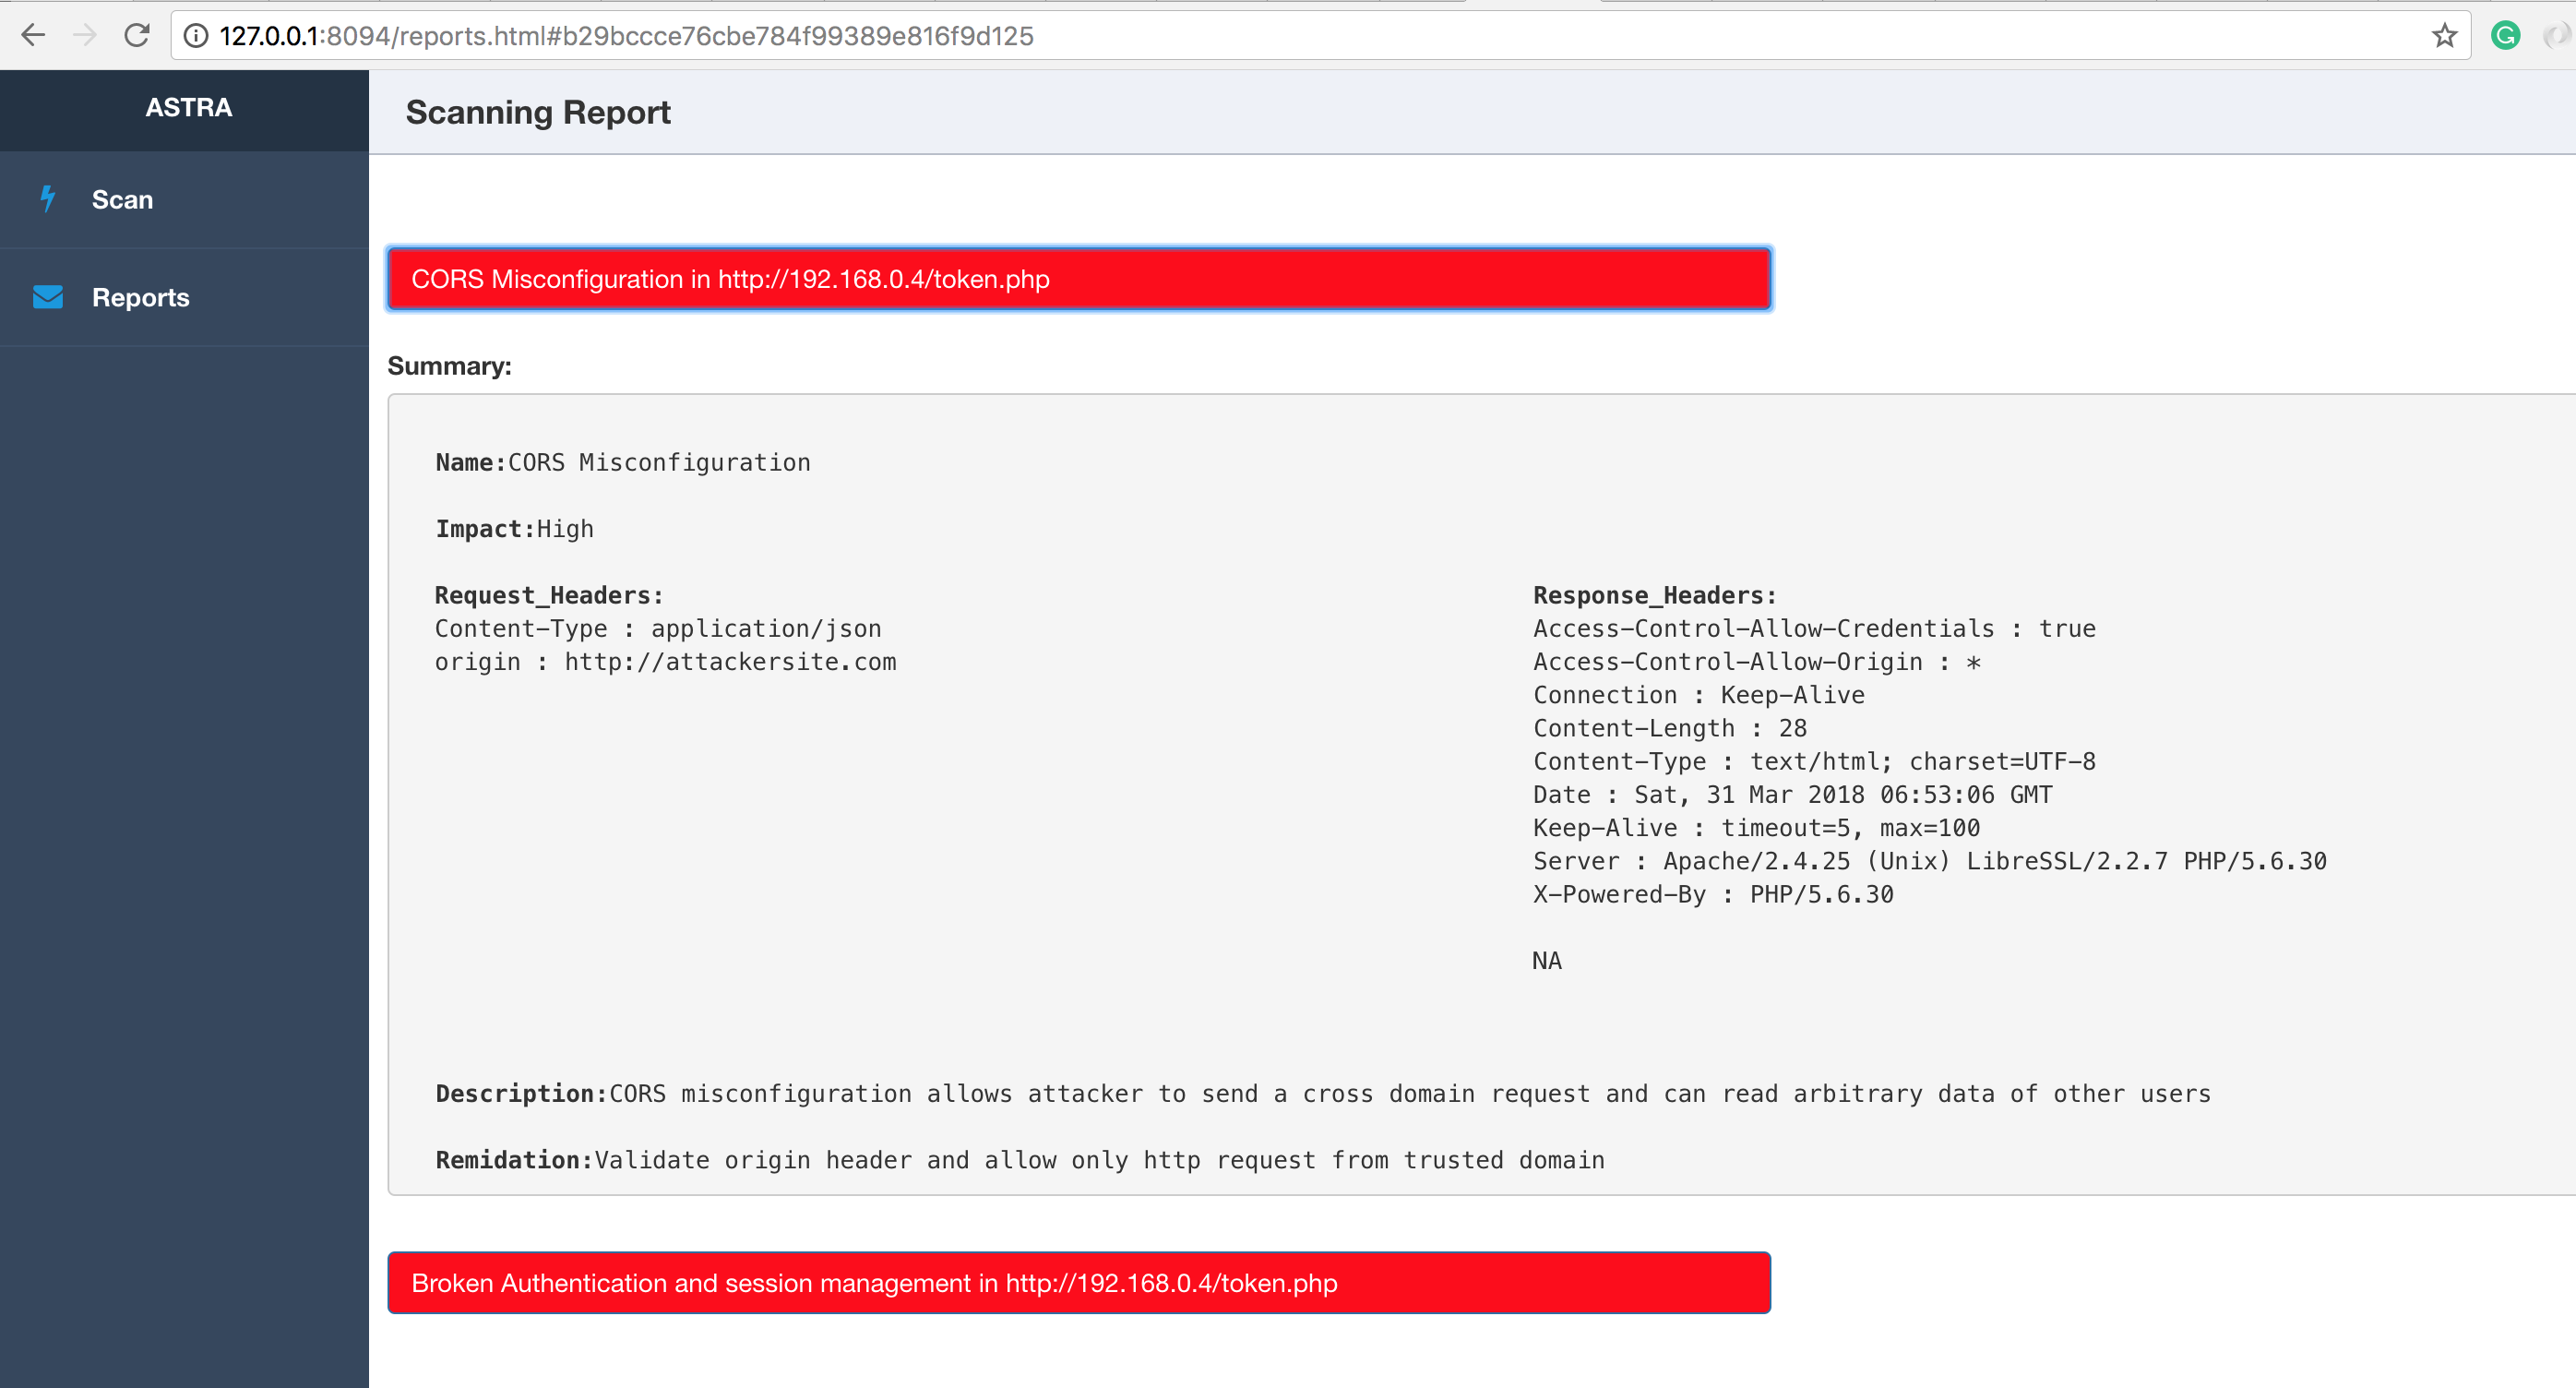 flipkart-incubator/astra
Automated Security Testing For REST API's
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
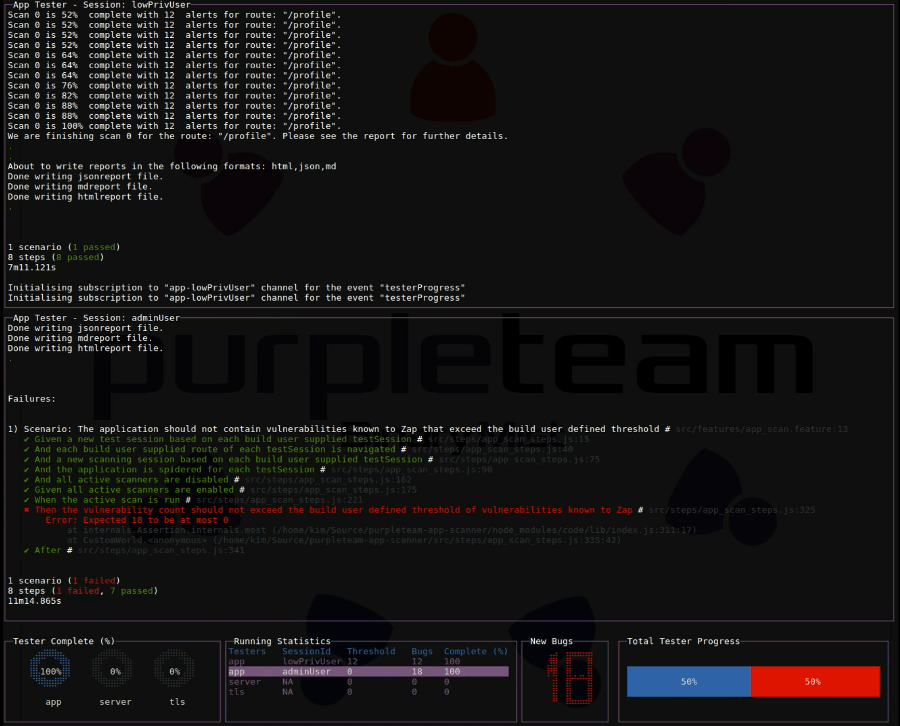
 purpleteam-labs/purpleteam
CLI component of purpleteam
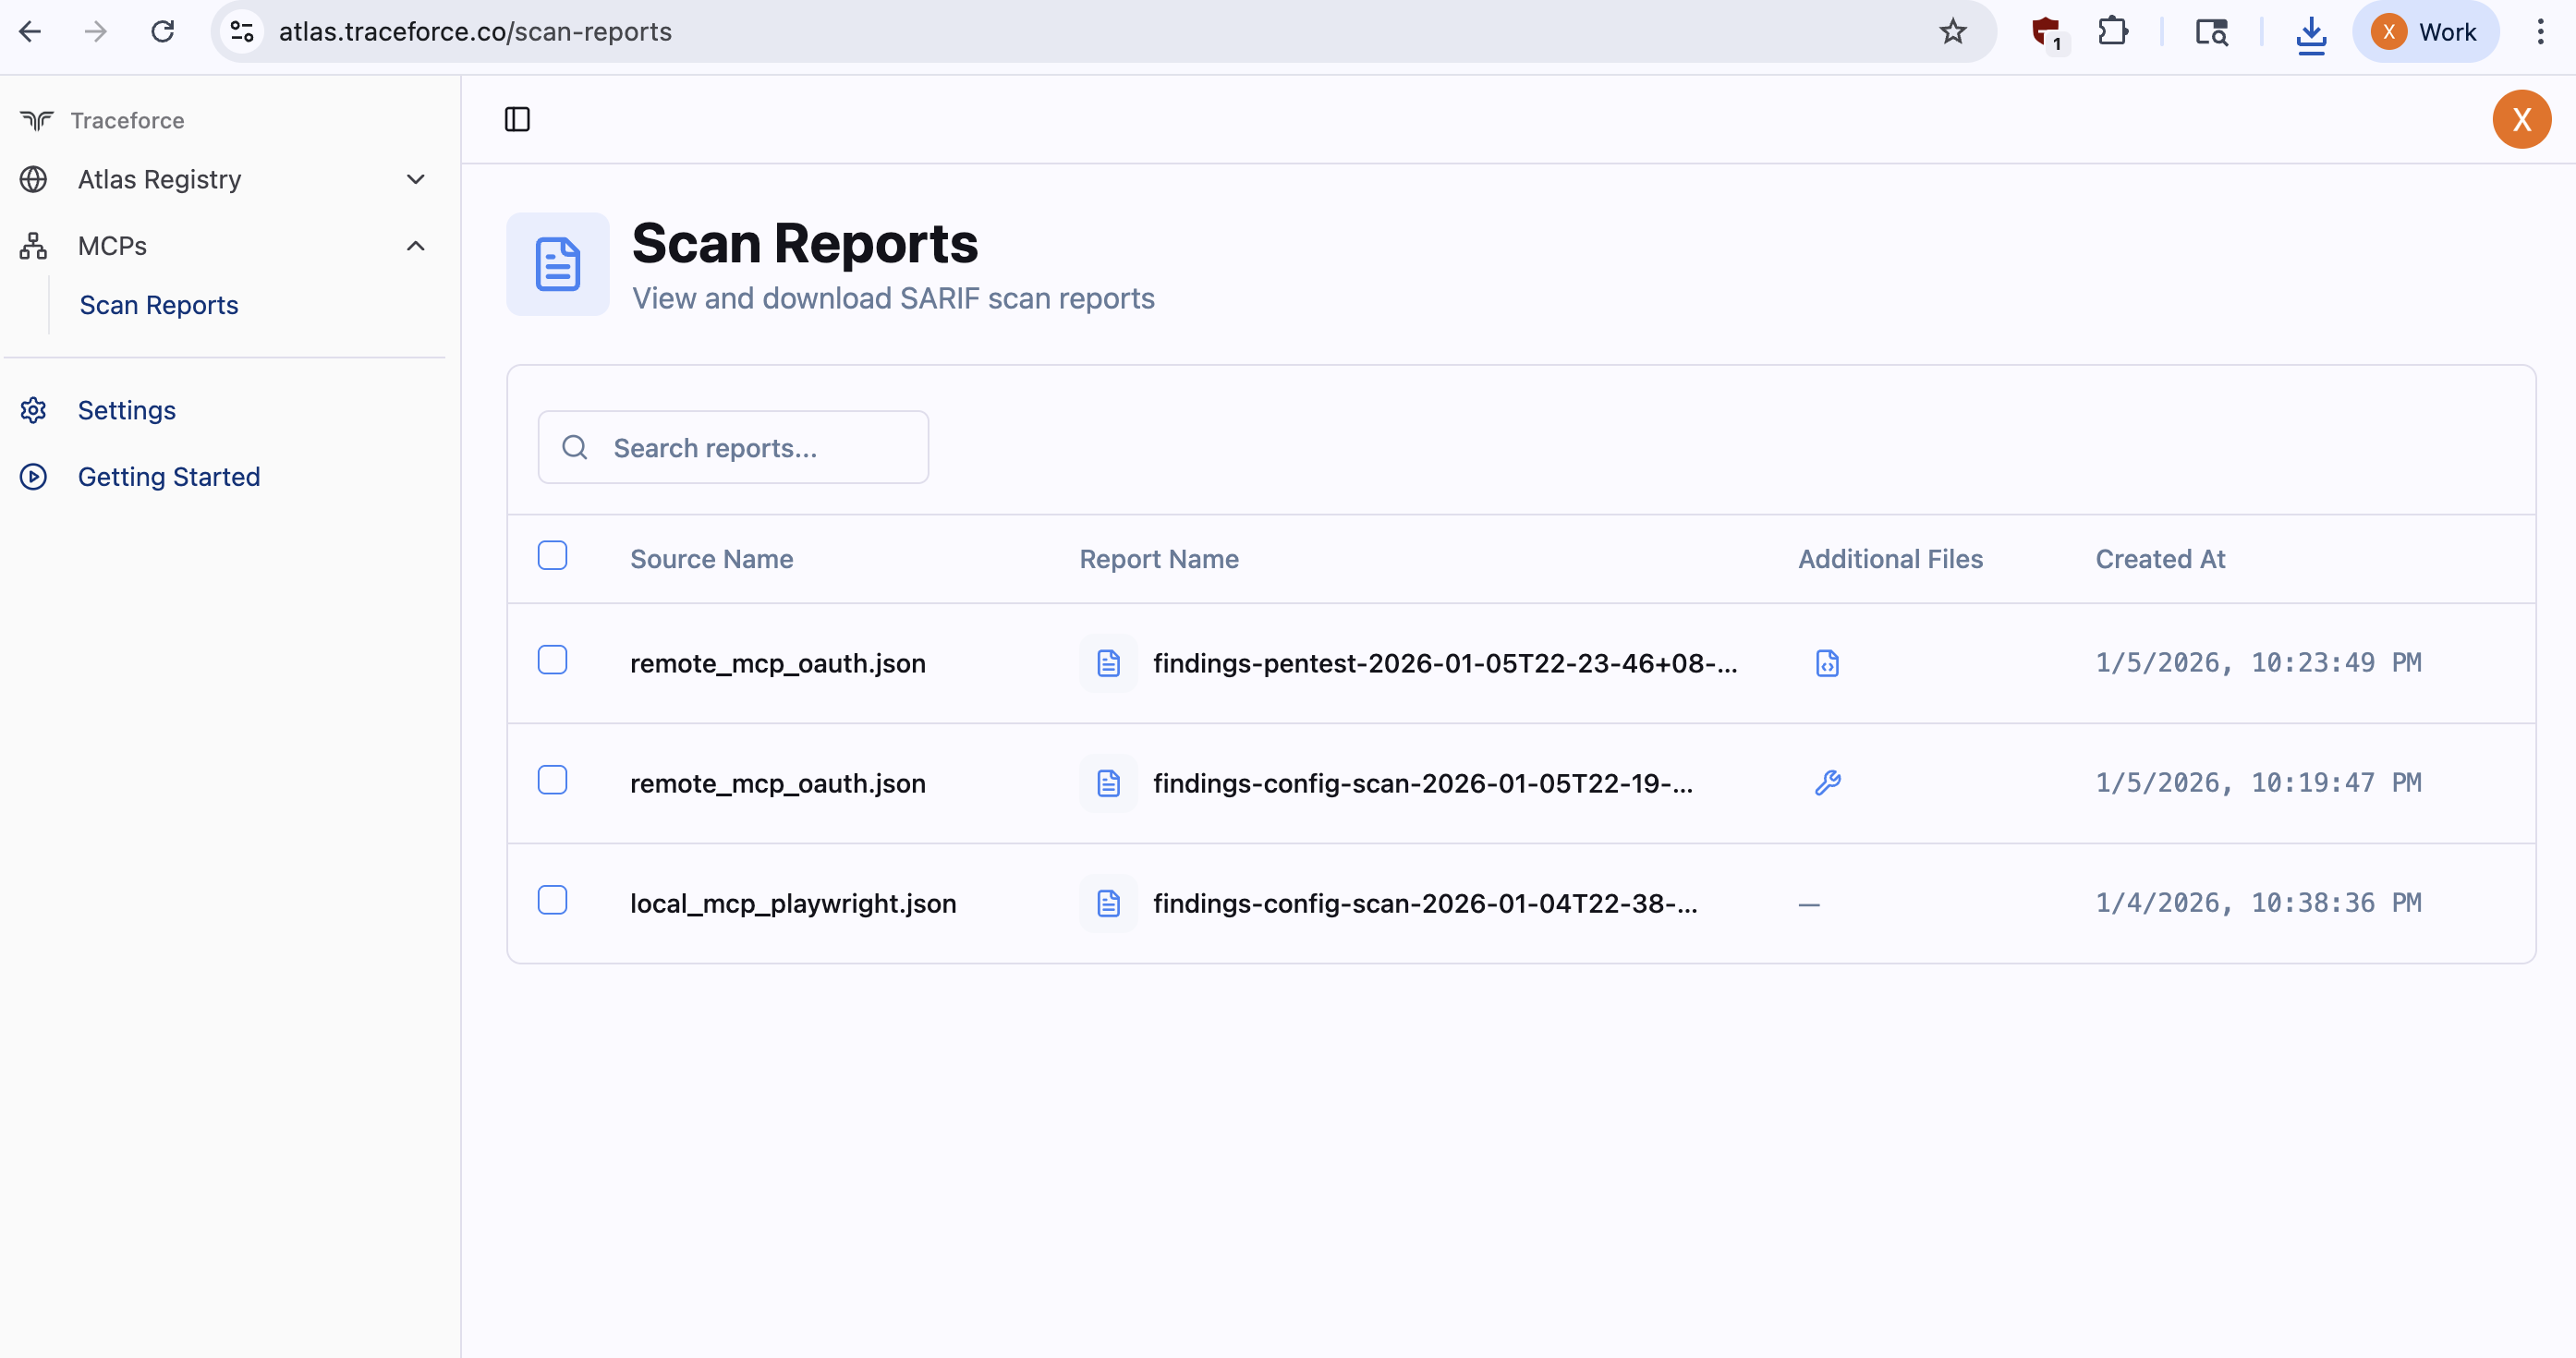 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.