
teller
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
cloud-infrastructure-securitycloud-securitycode-analysis+2
3.2k
tellerops/tellerCloud native secrets management for developers - never leave your command line for secrets.
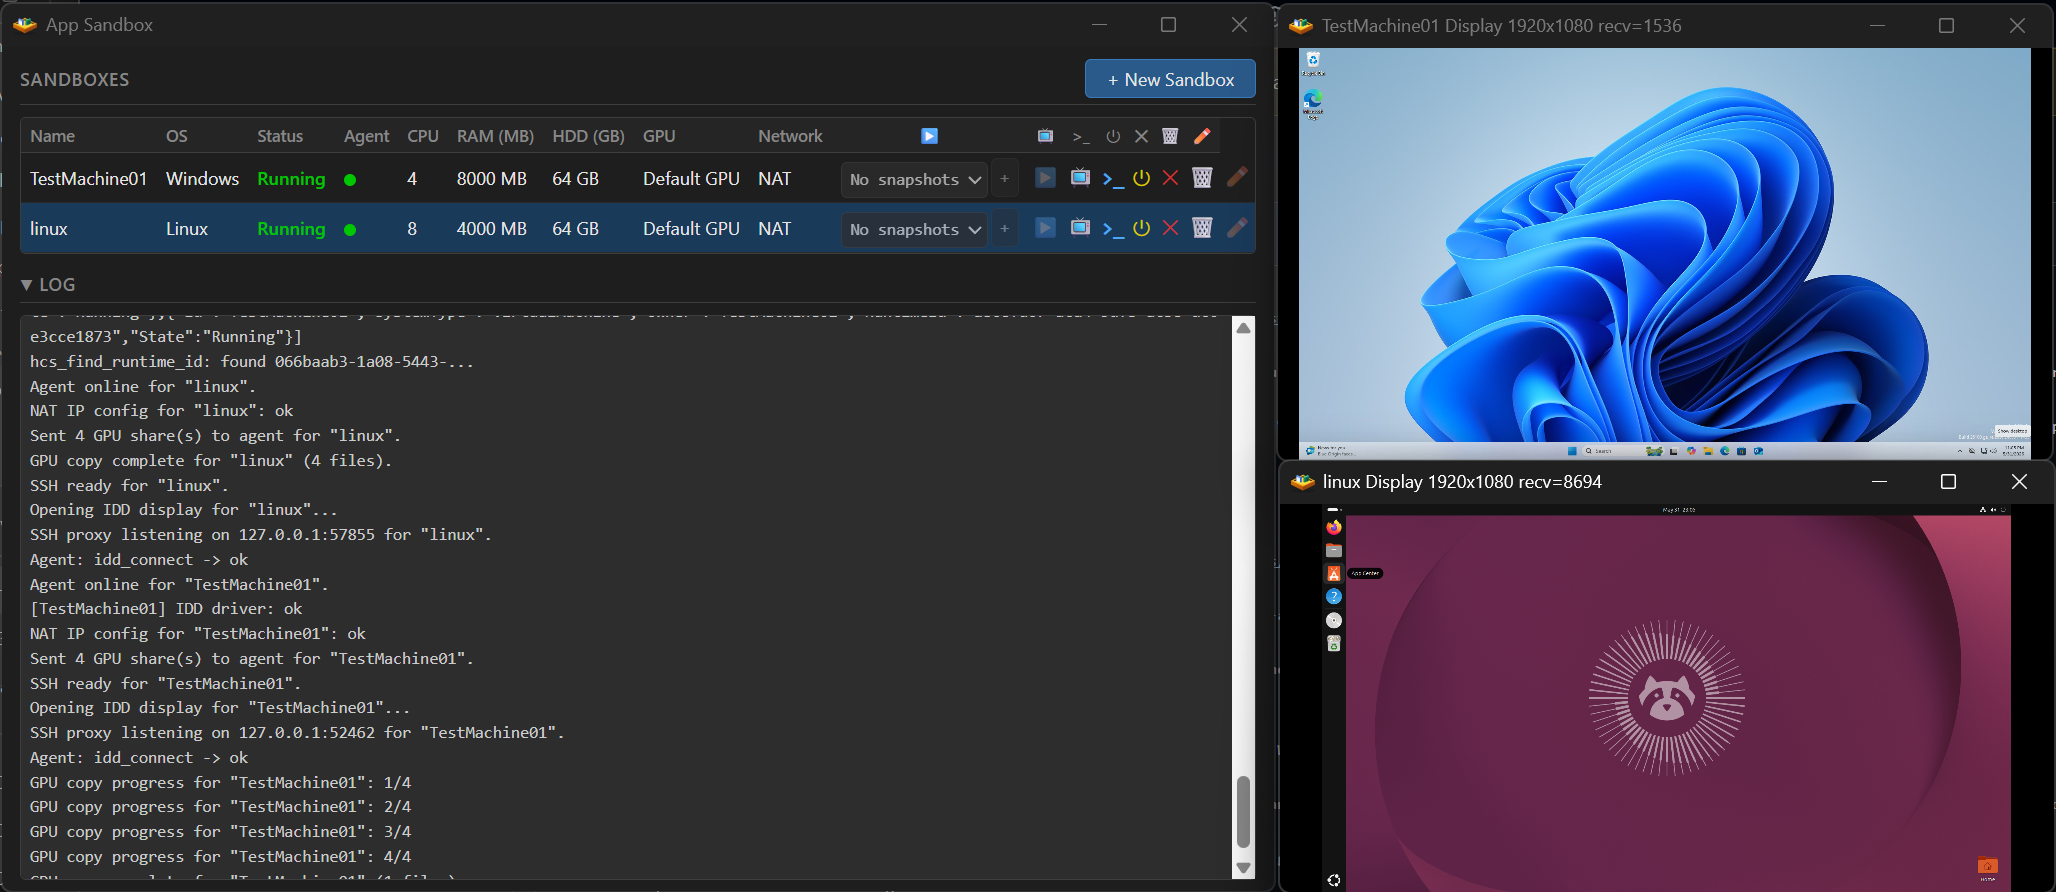 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
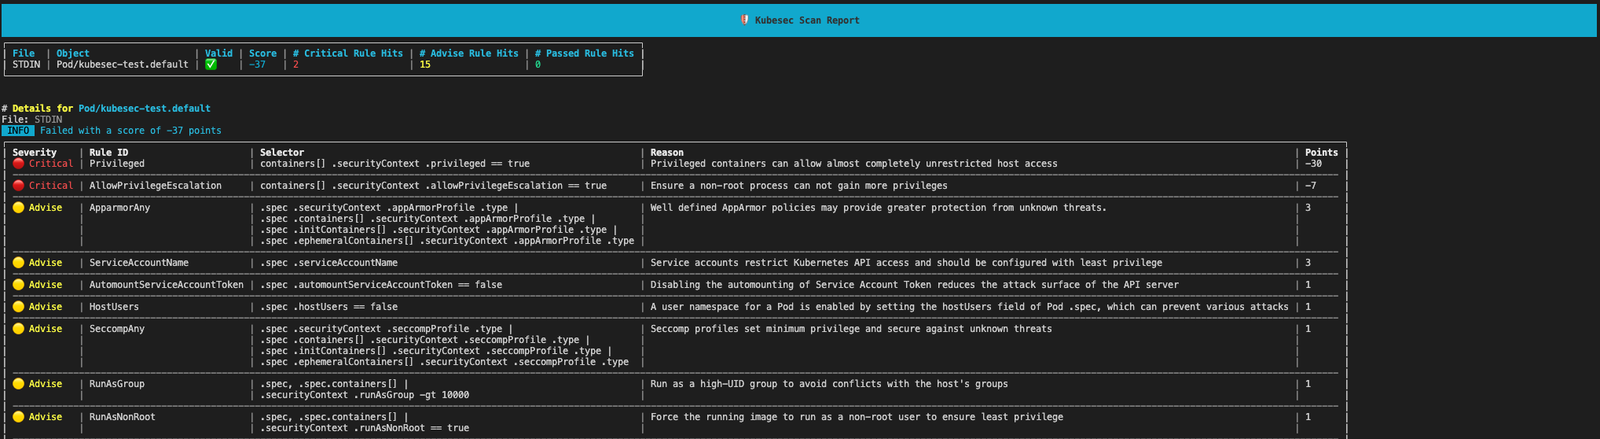 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
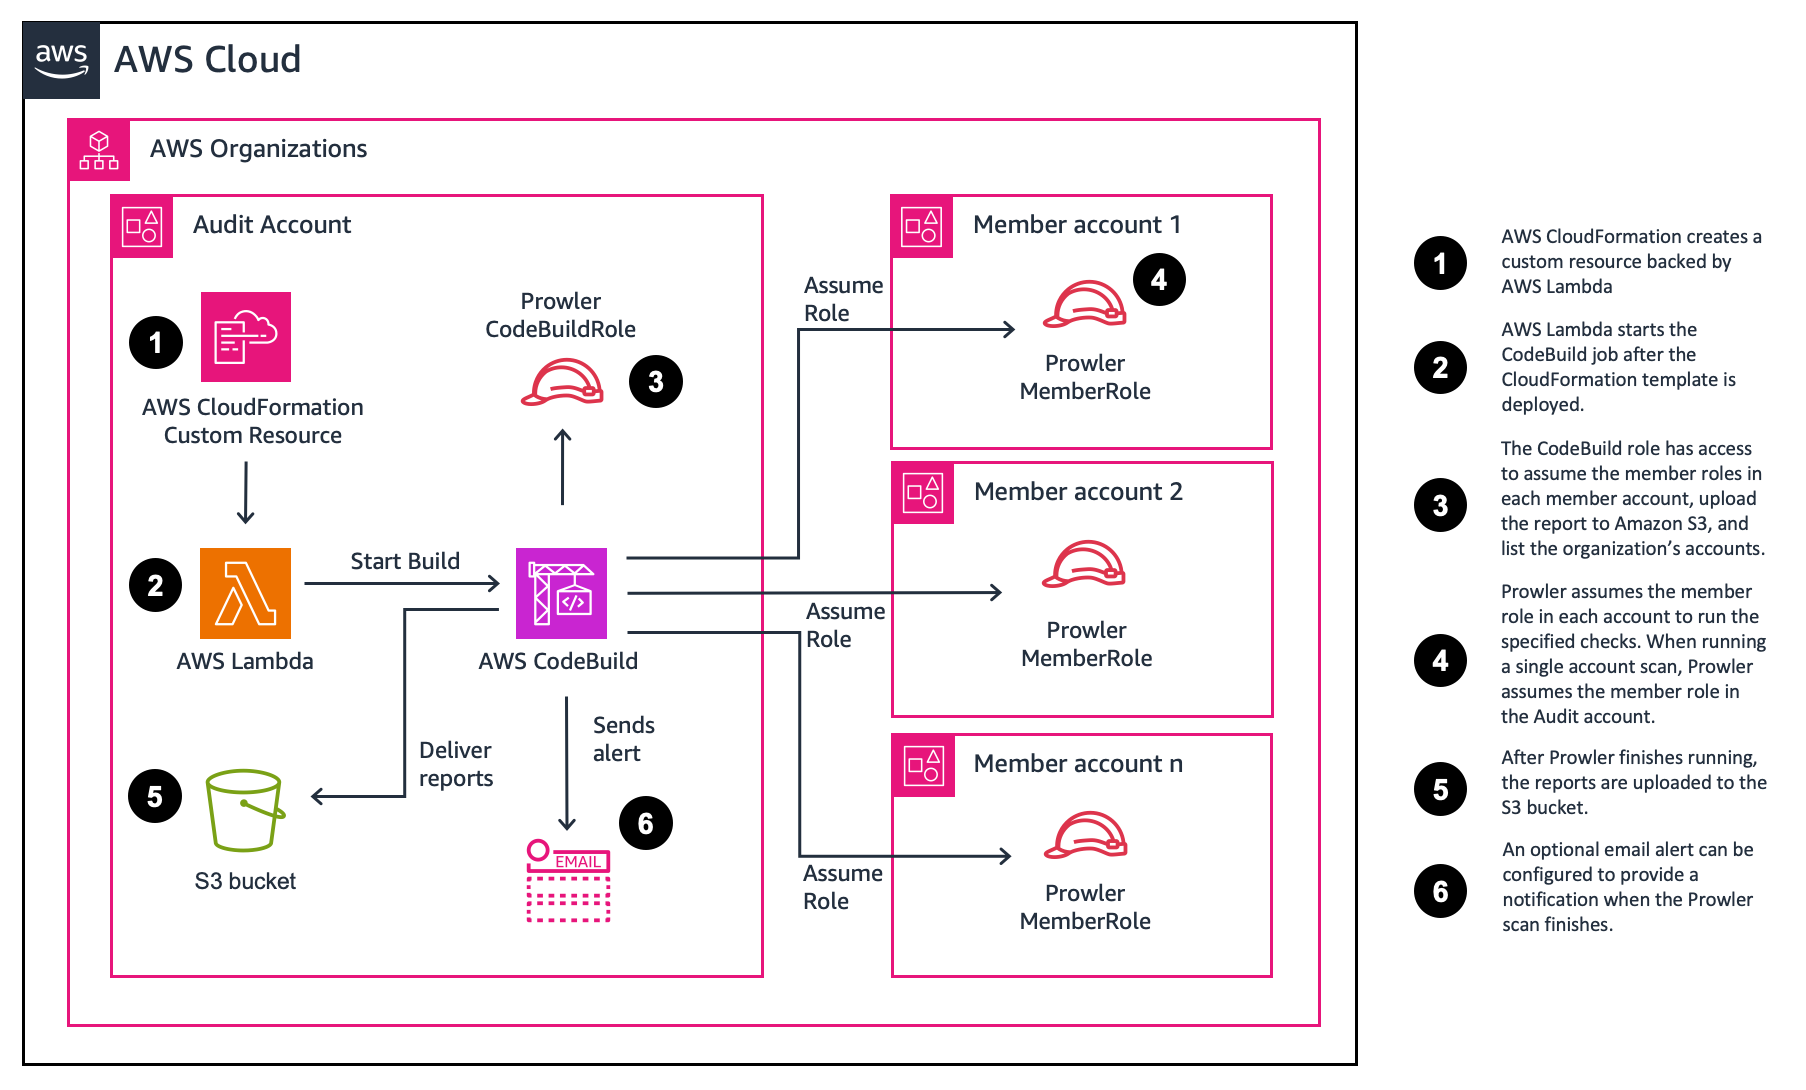 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
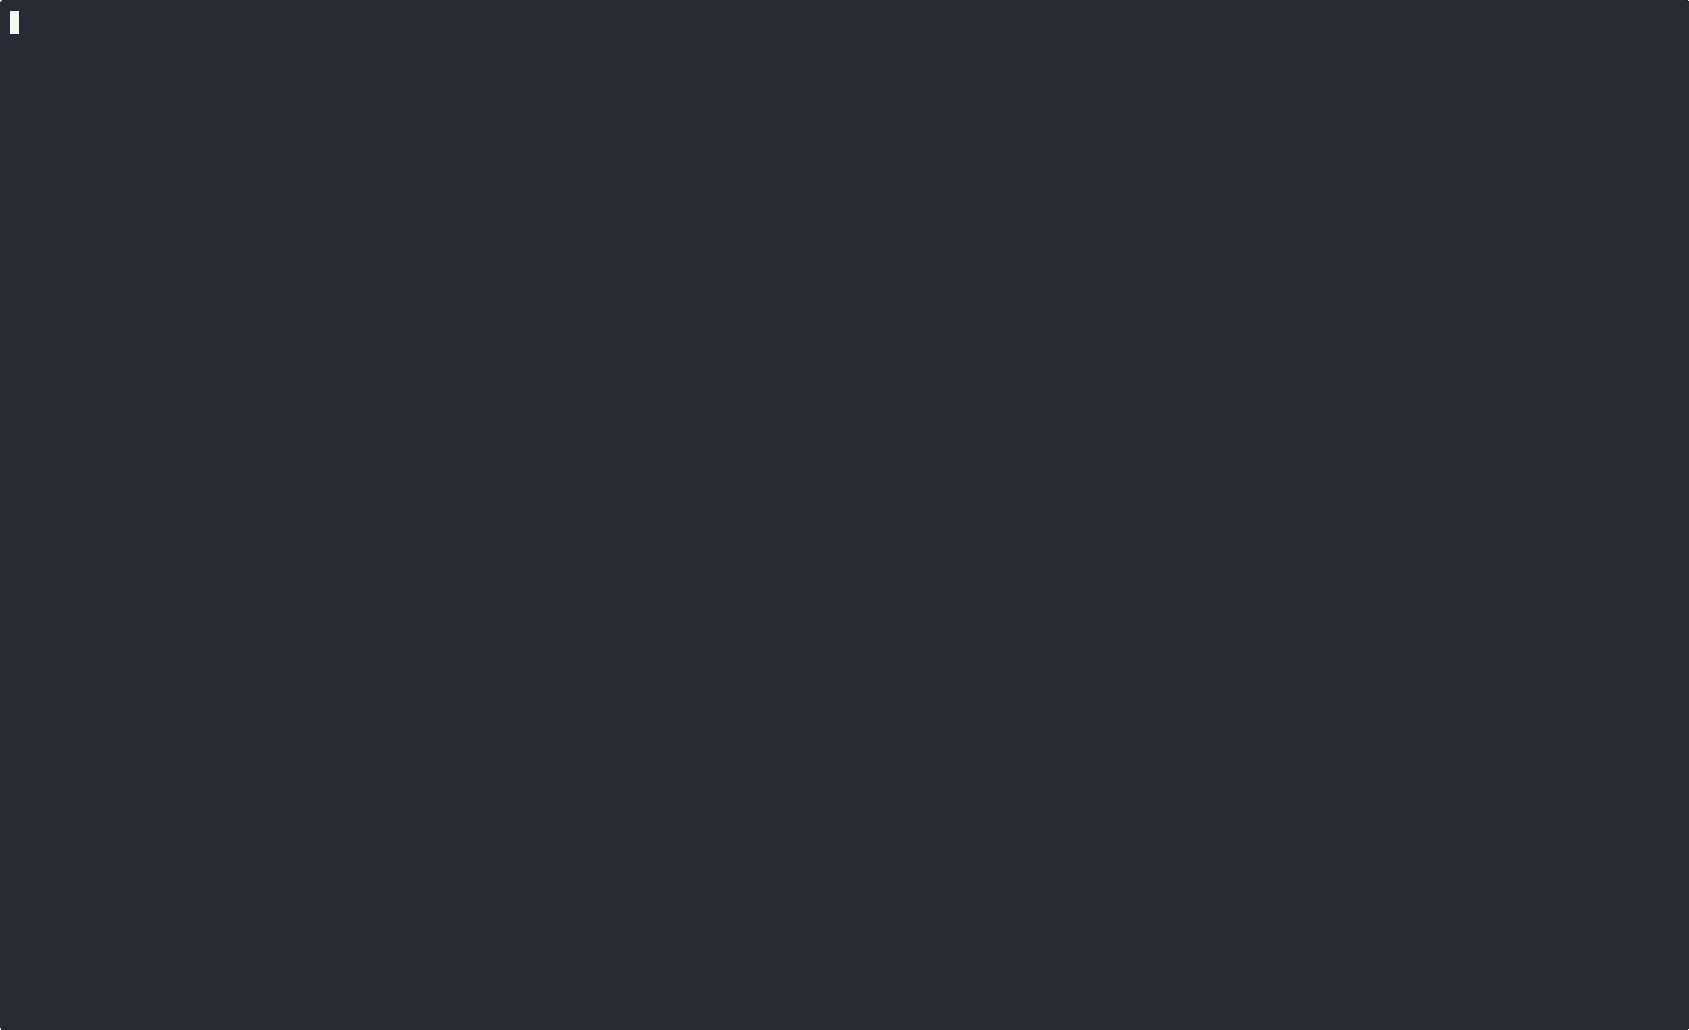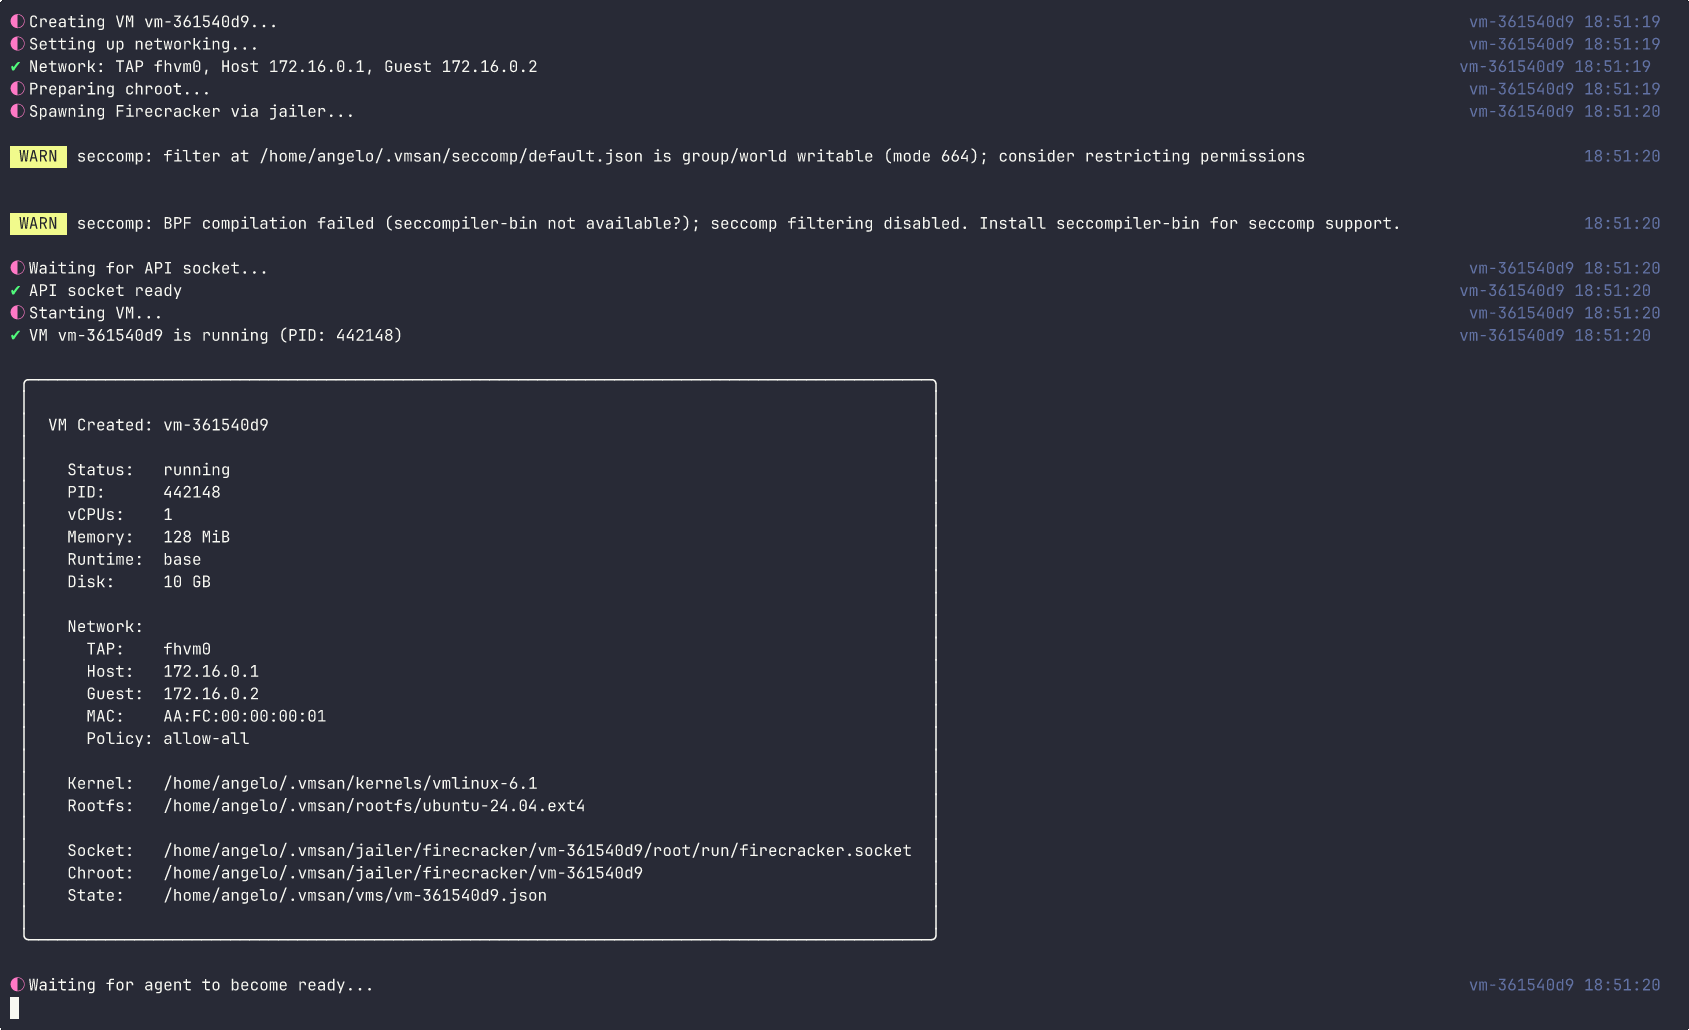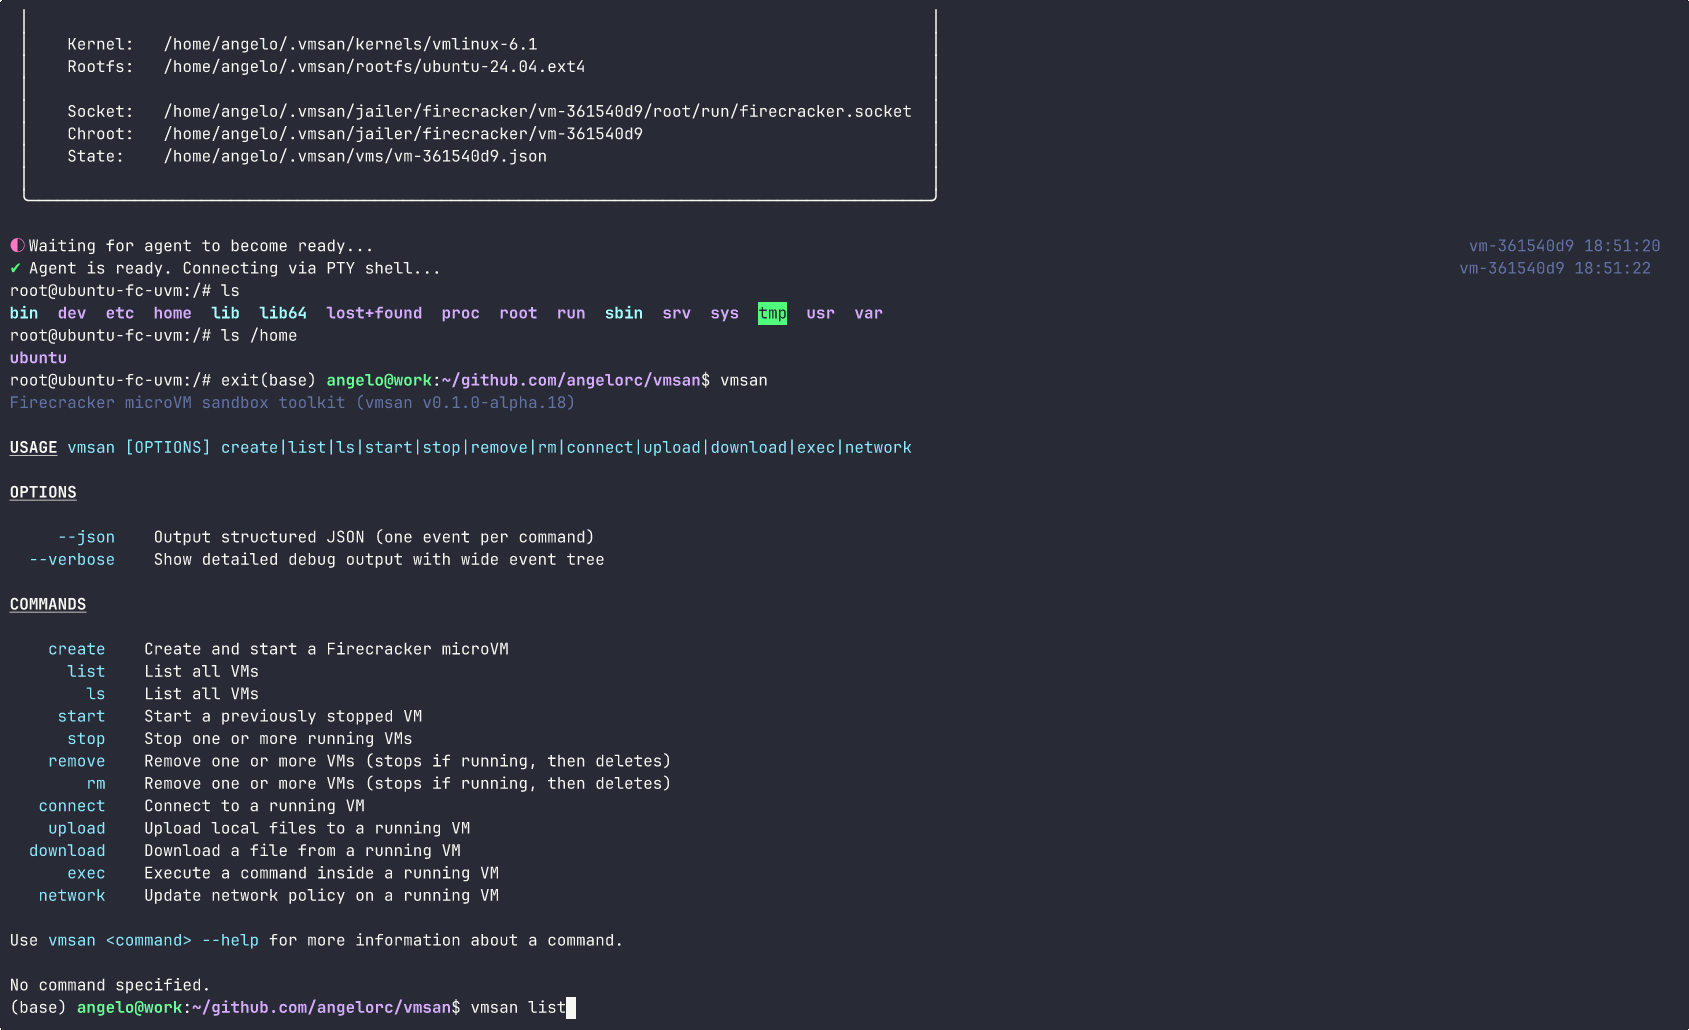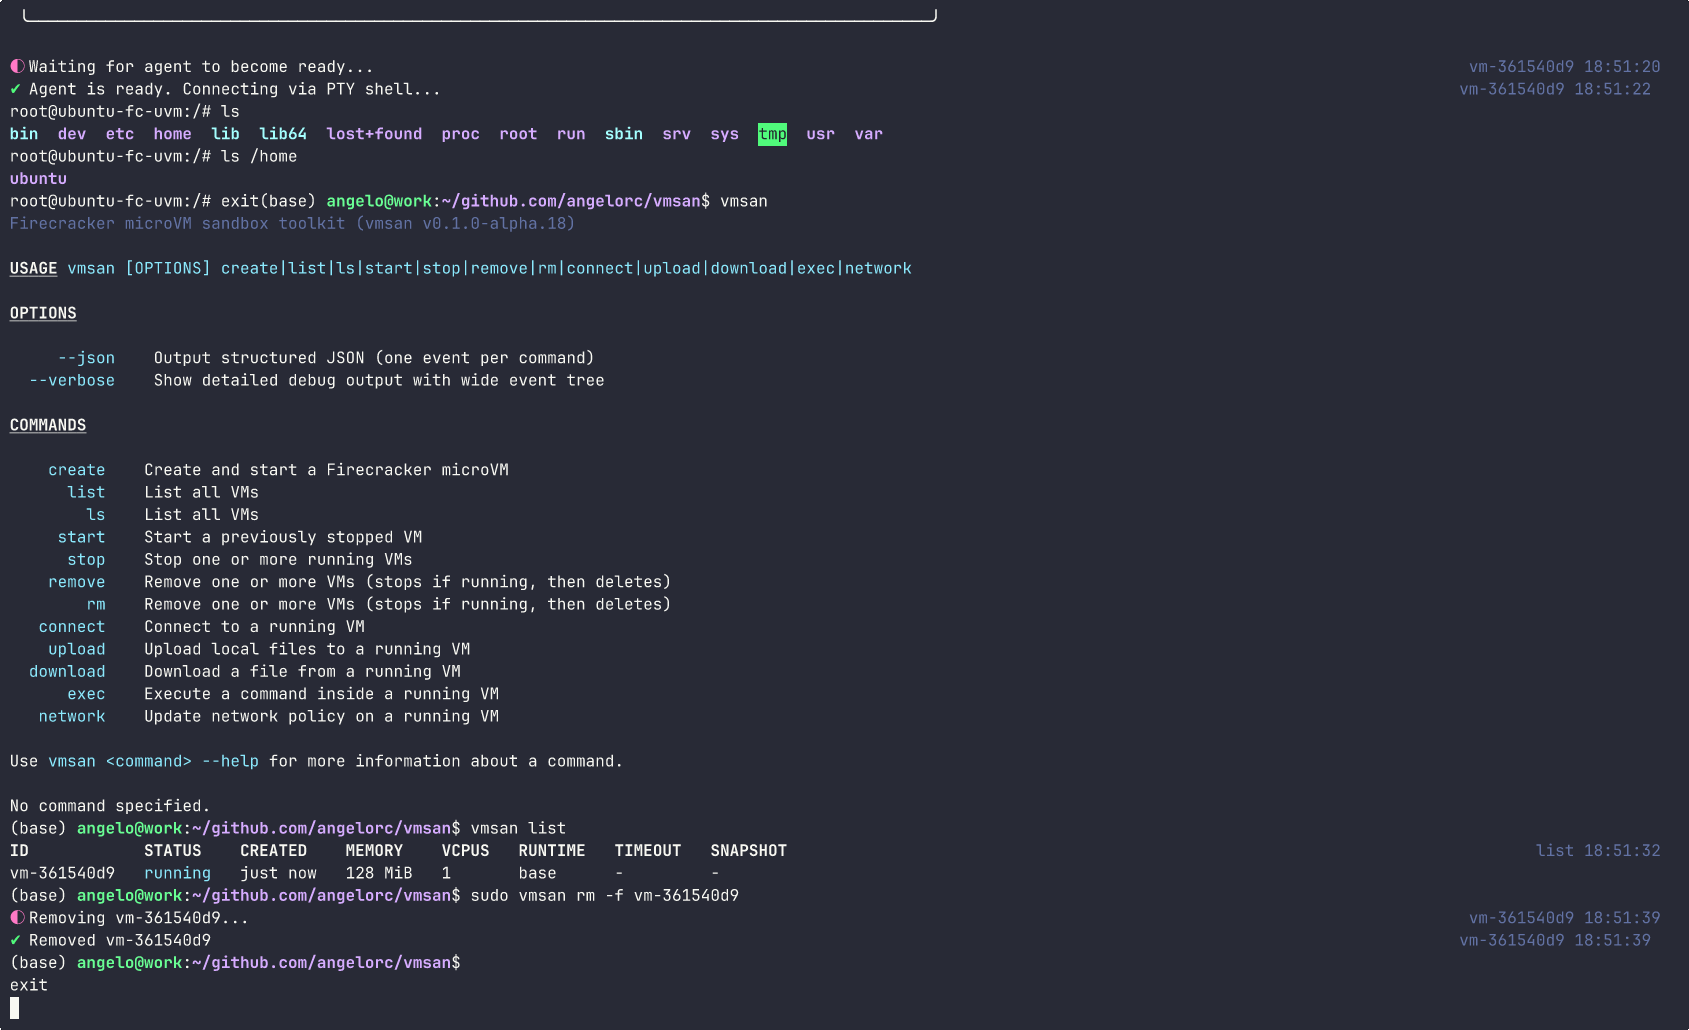 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 dracondev/dracon-utilities
Invisible infrastructure for Dracon developer workspaces: git sync, system guard, and warden encryption utilities.
 p0ssuidao/terraguard
🛡️ 🔒 This project's goal is to be simple to create and destroy your own VPN service using WireGuard.
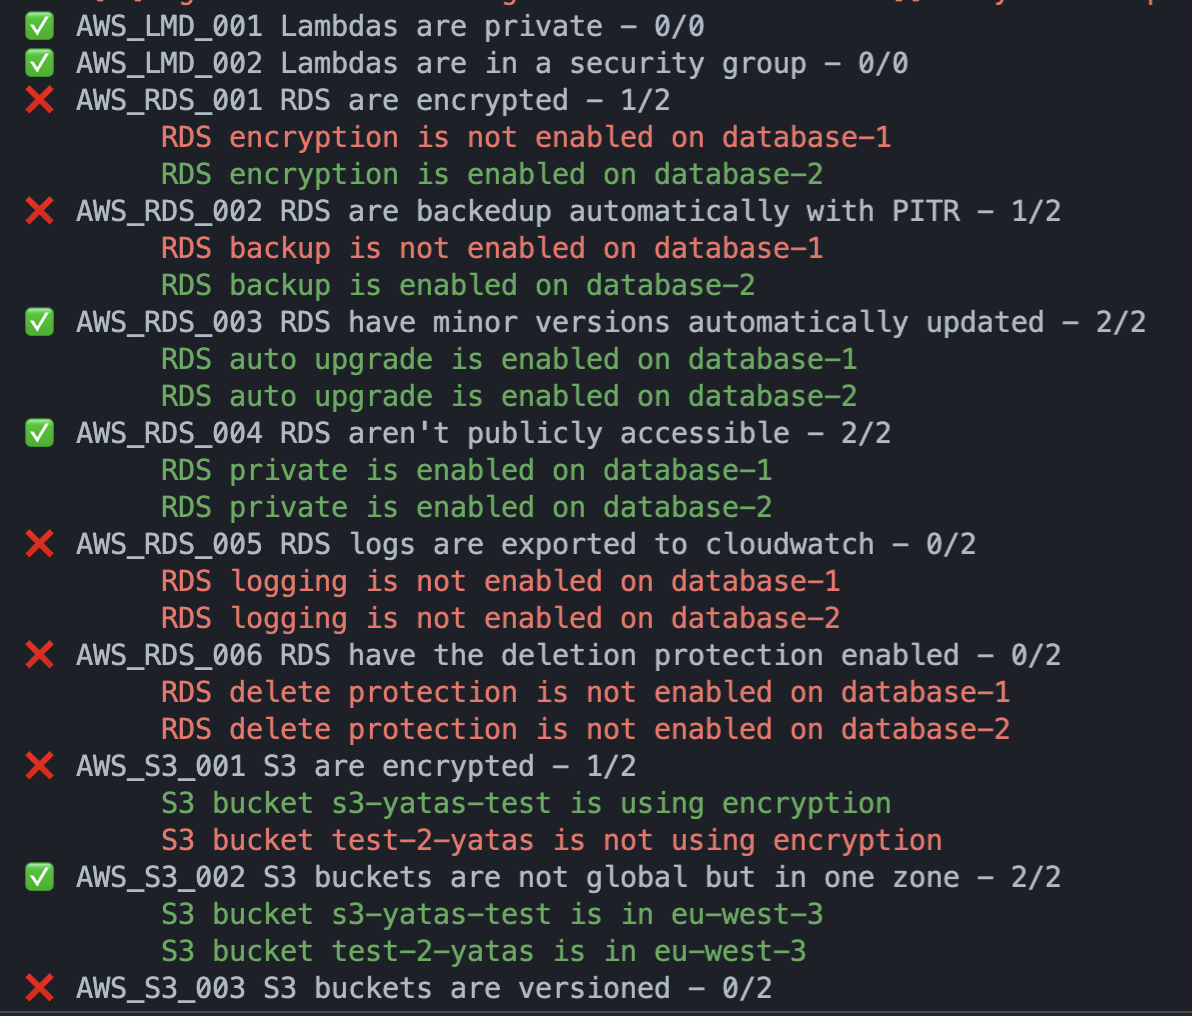 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
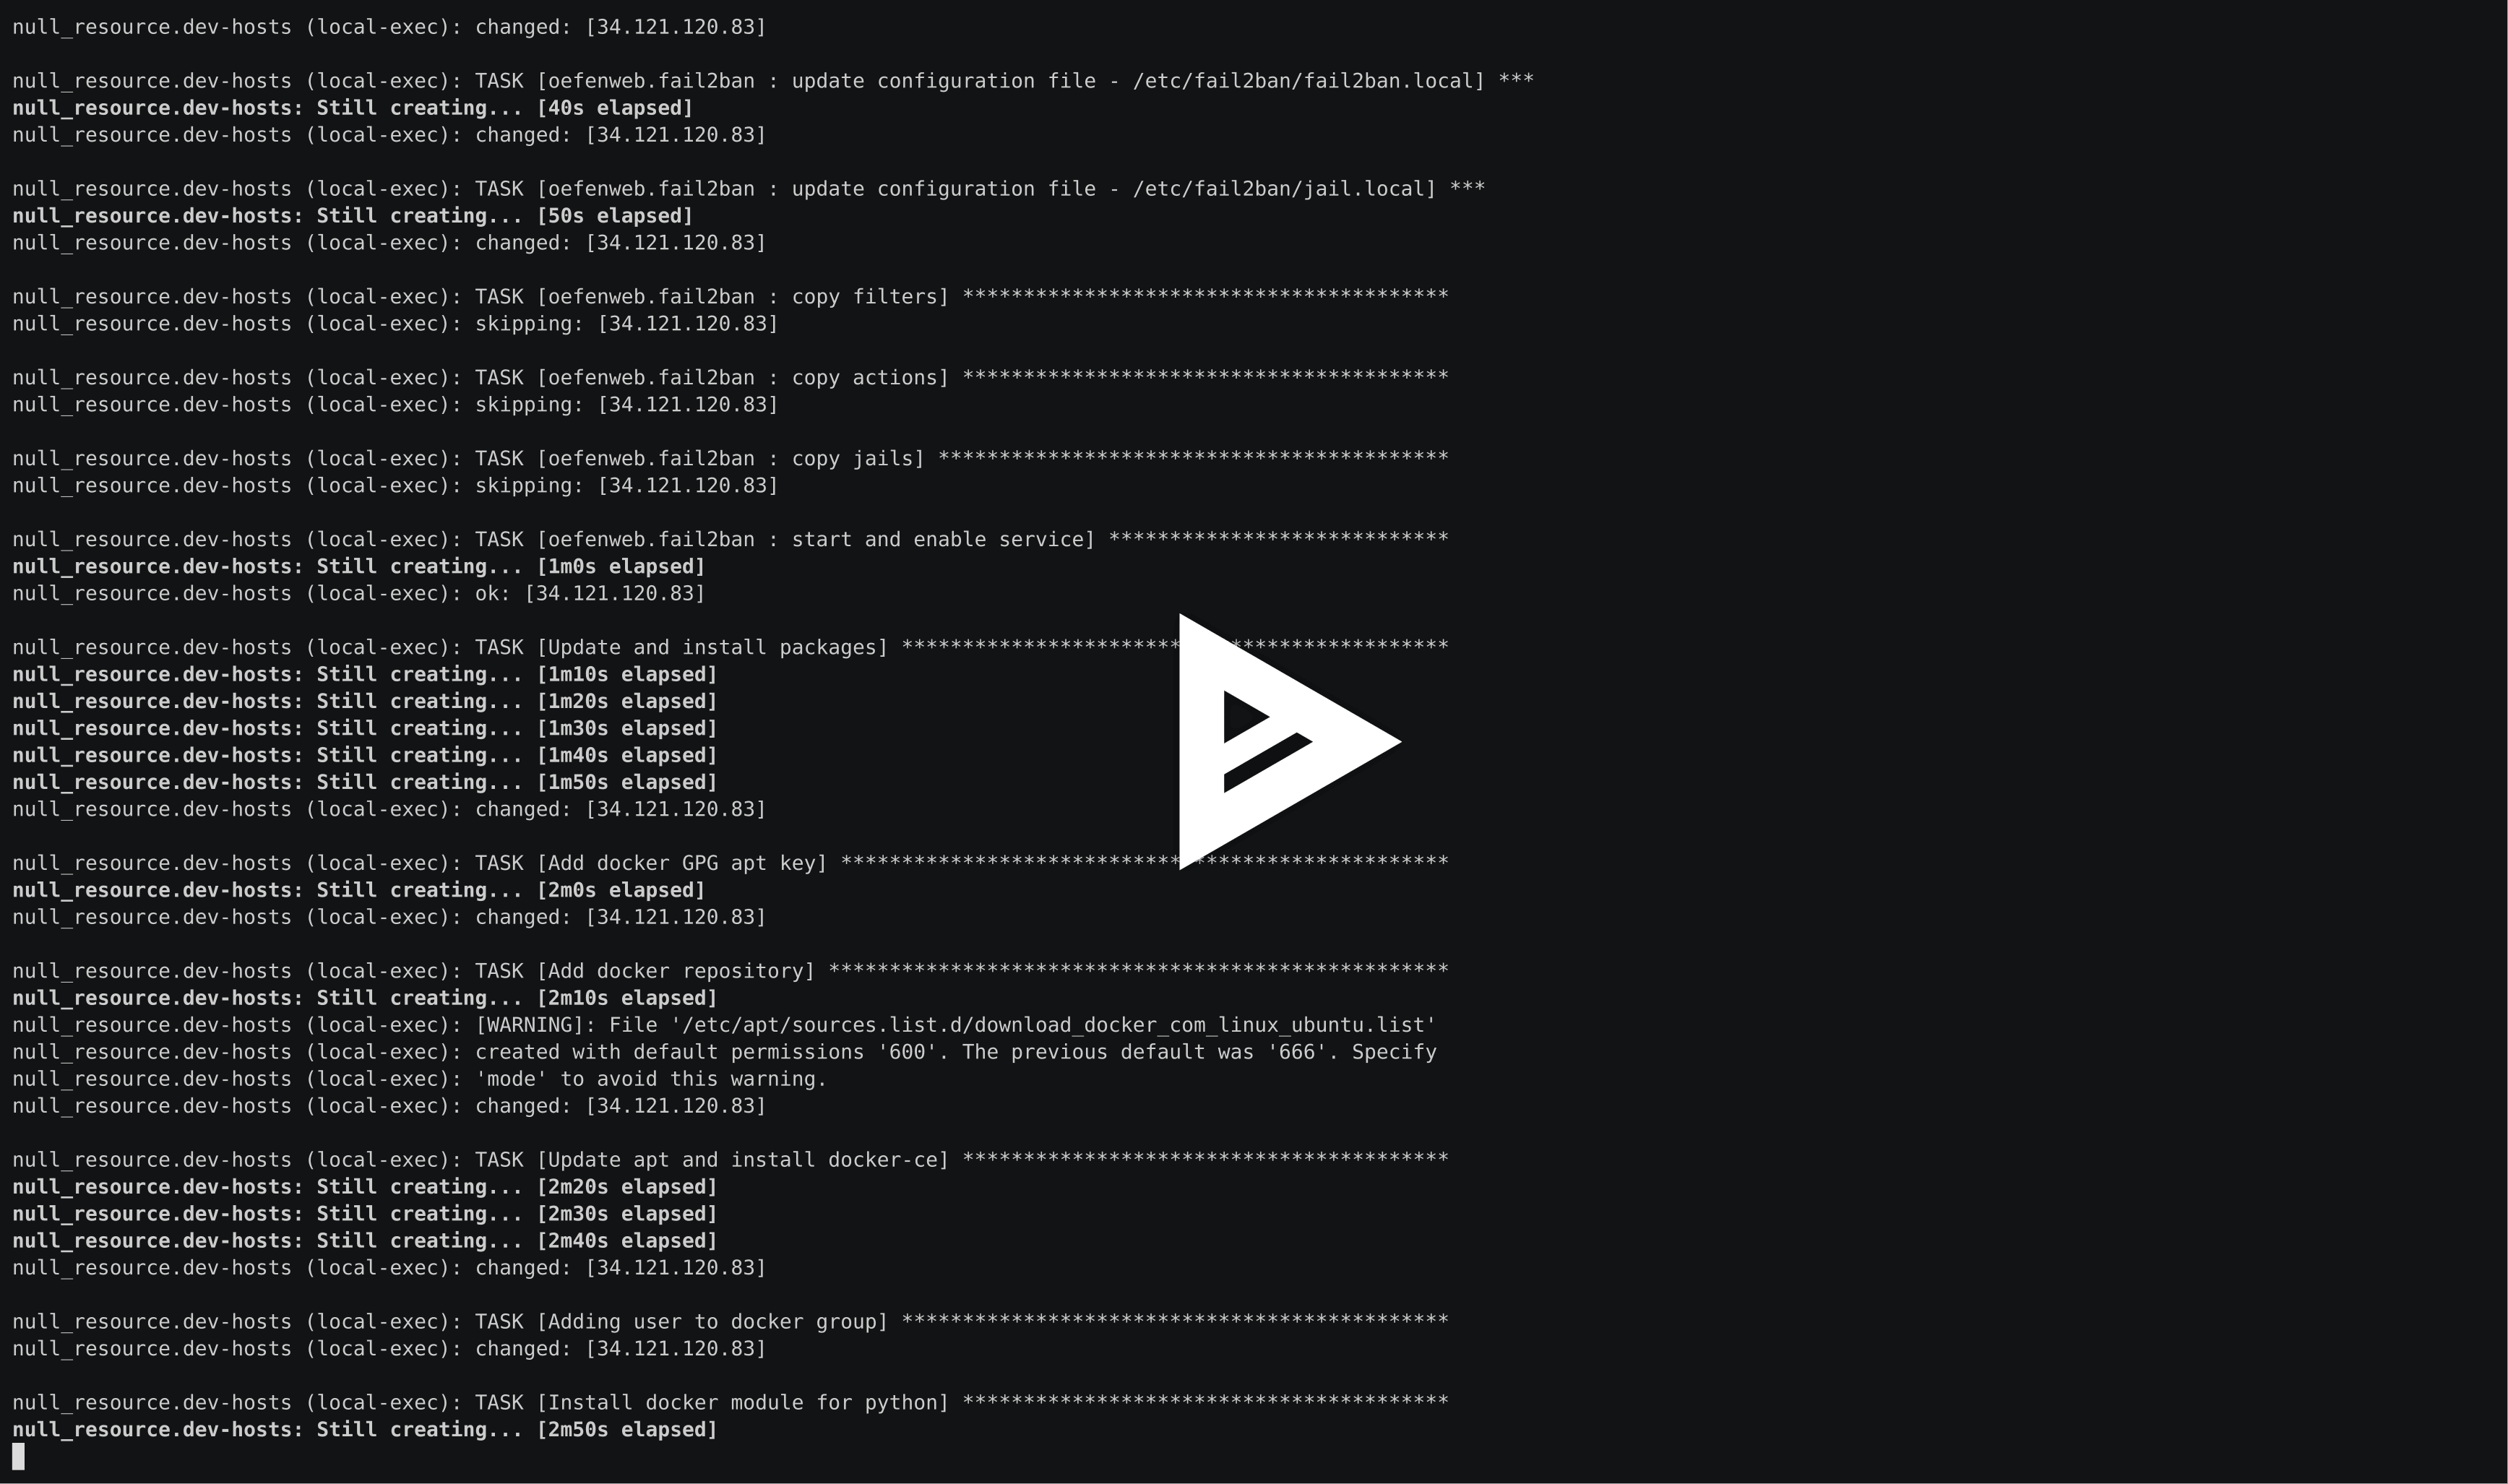 aaaguirrep/offensive-docker-vps
Create a VPS on Google Cloud Platform or Digital Ocean easily with Offensive Docker included to launch assessment to the targets.
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)