defender-privilege-escalation-scanner

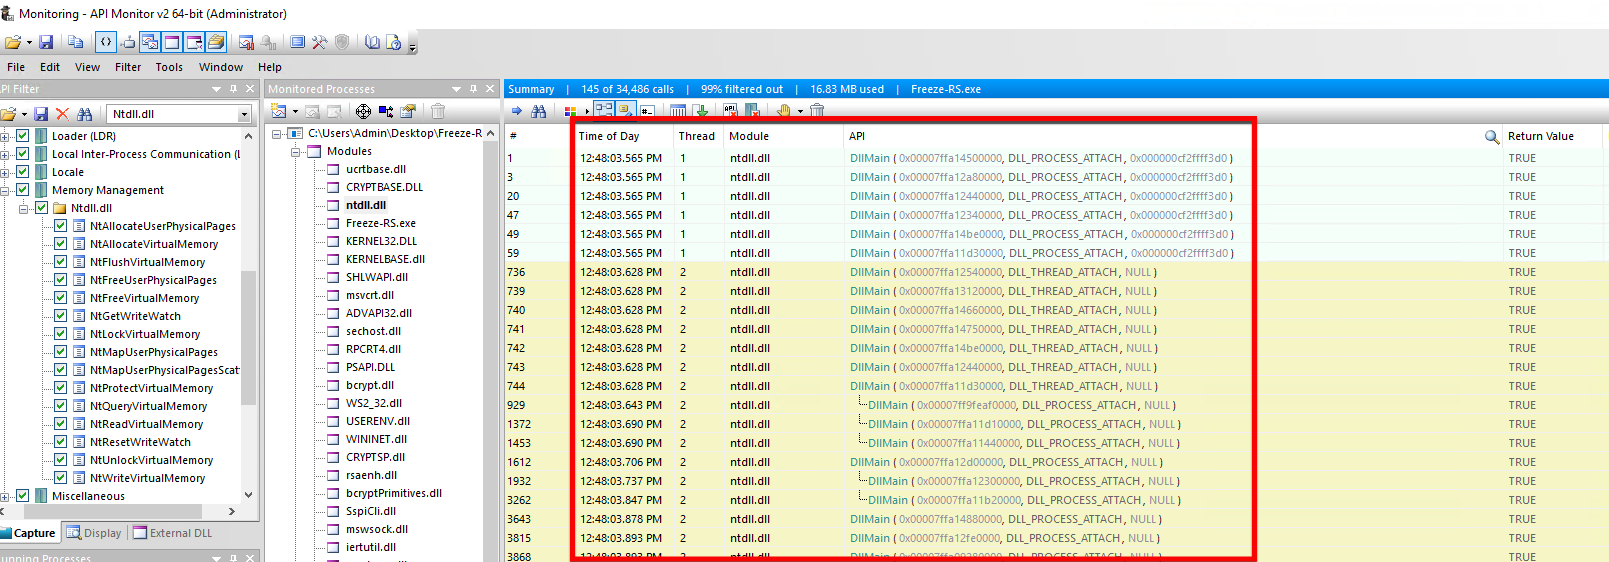
Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)

Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)

Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.

a Fedora remix focused on pentesting and purple hat tooling

One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️

Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

Cyber Range including Velociraptor + HELK system with a Windows VM for security testing and R&D. Azure and AWS terraform support.

Specter — passive 13.56 MHz NFC reader/skimmer bug-sweep for Flipper Zero. Counter-surveillance EMF meter using the onboard NFC chip. No extra…

BadExclusionsNWBO is an evolution from BadExclusions to identify folder custom or undocumented exclusions on AV/EDR

Quick WAF "paranoid" Doctor Evaluation | WAFPARAN01D3 Tool

Project that brings together several pentest tools

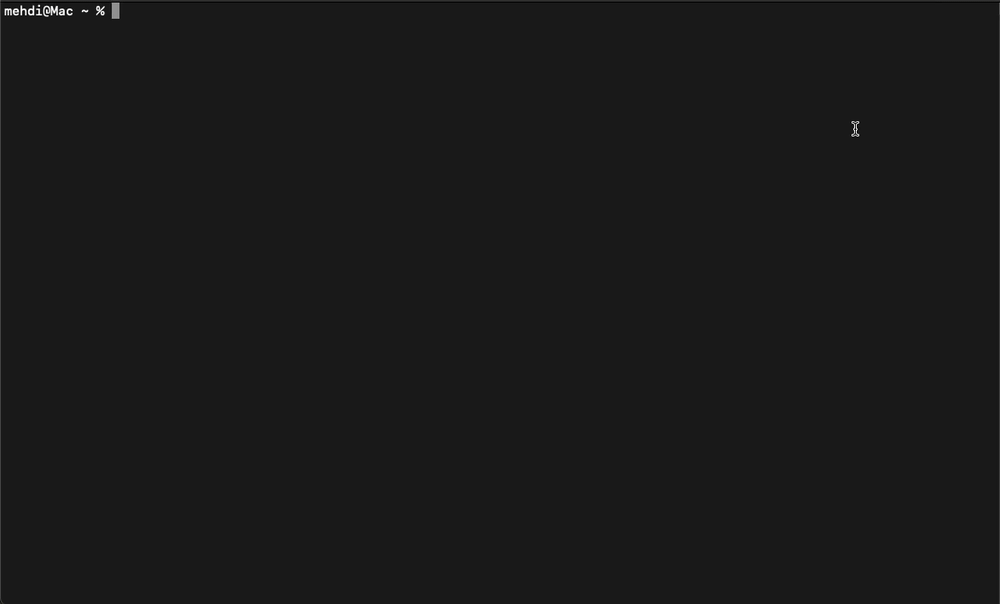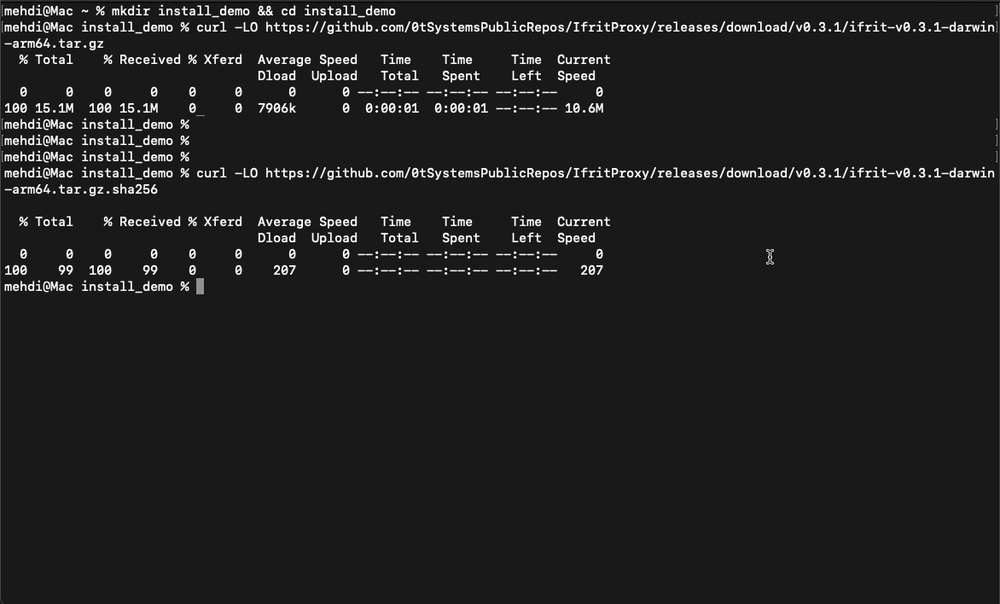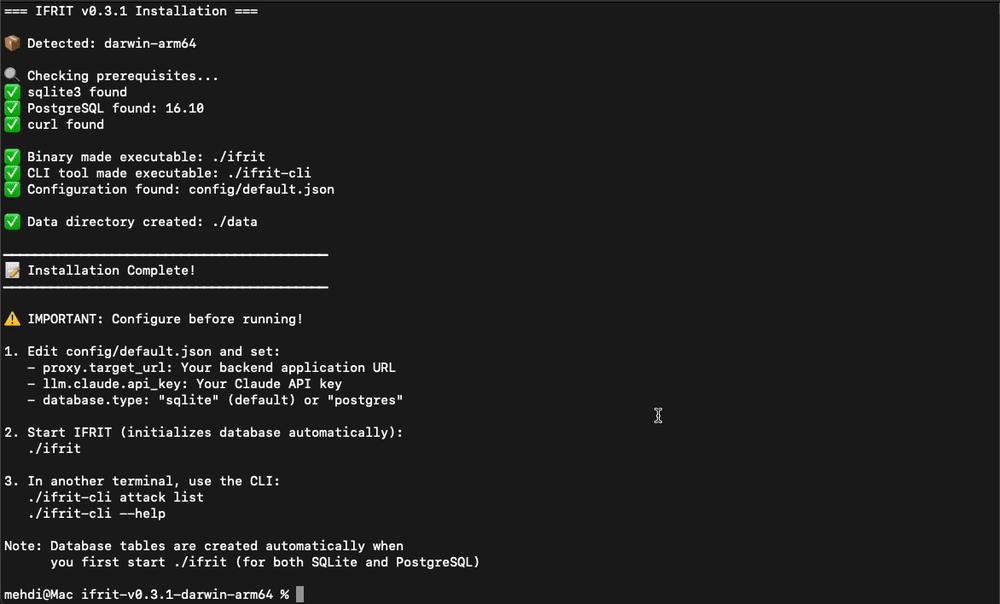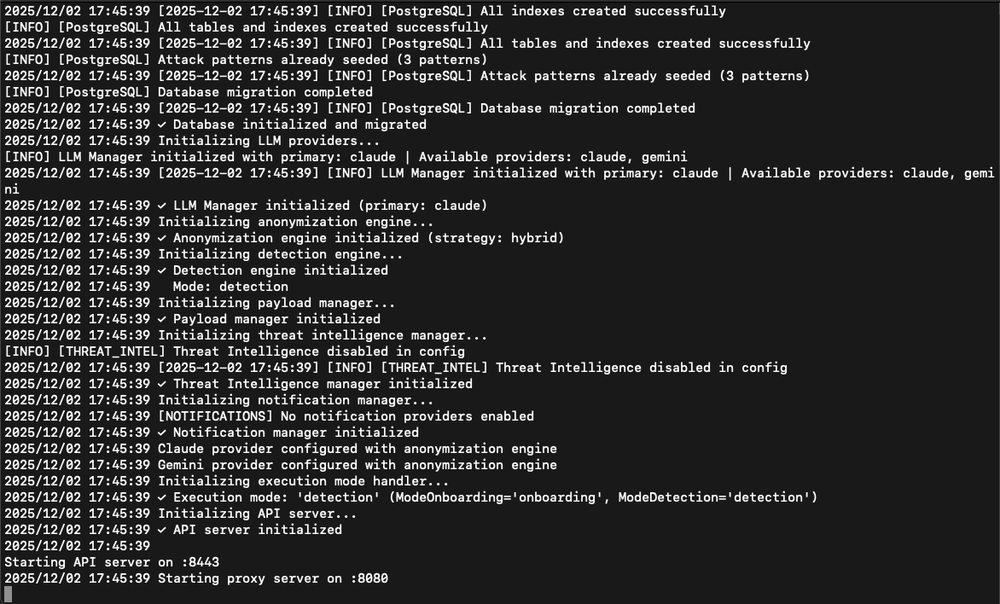
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…

Low Interaction Mobile Honeypot

Web Service write in Python for control and protect your android device remotely.

Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware

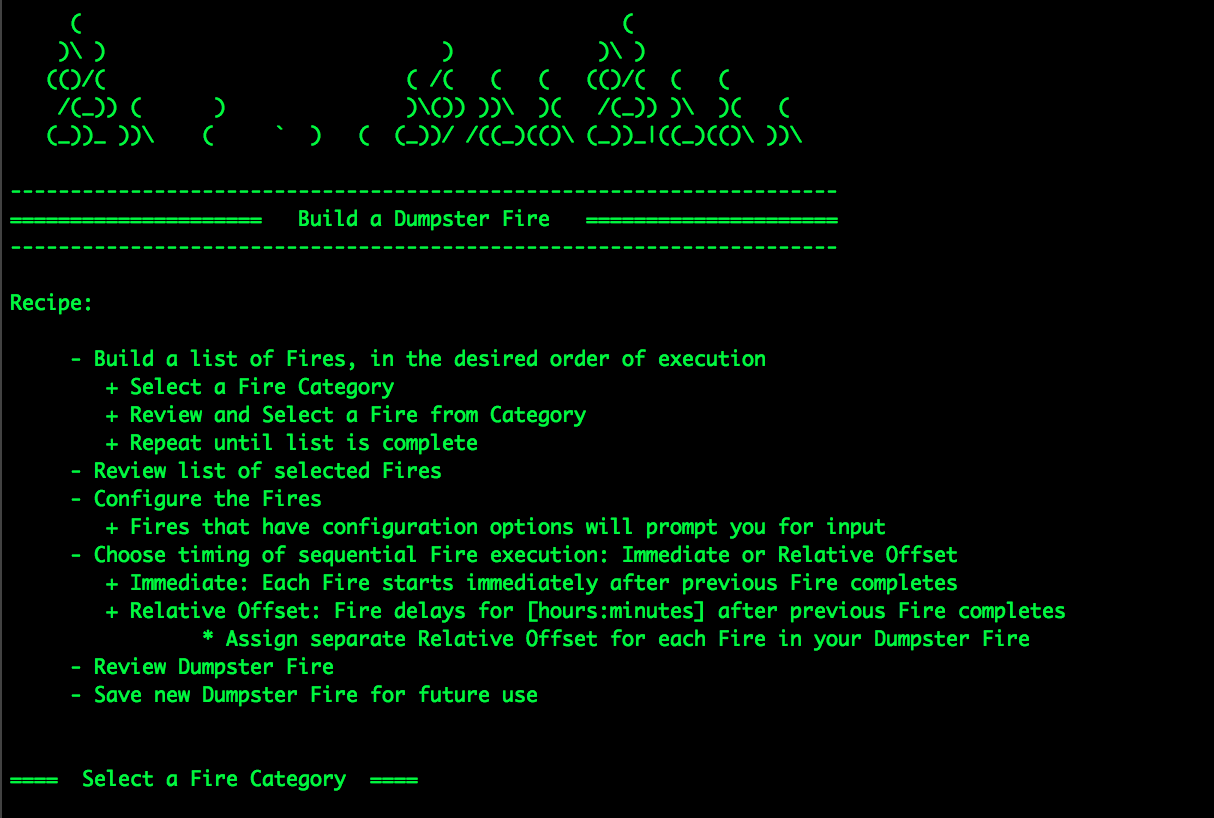
"Security Incidents In A Box!" A modular, menu-driven, cross-platform tool for building customized, time-delayed, distributed security events.…

Enhance your malware detection with WAF + YARA (WAFARAY)

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…