
untitledgoosetool
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
cloud-securitydefensive-toolsdigital-forensics+4
965
cisagov/untitledgoosetoolUntitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
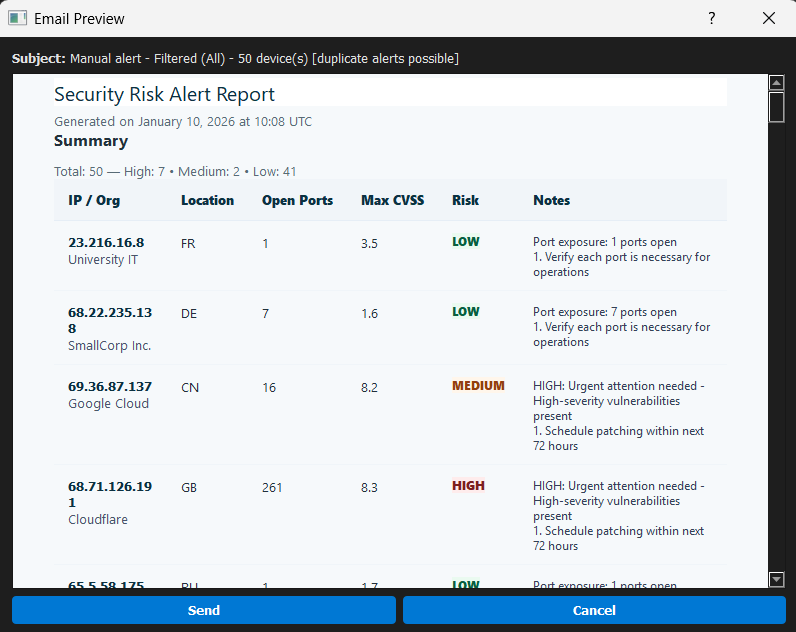 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
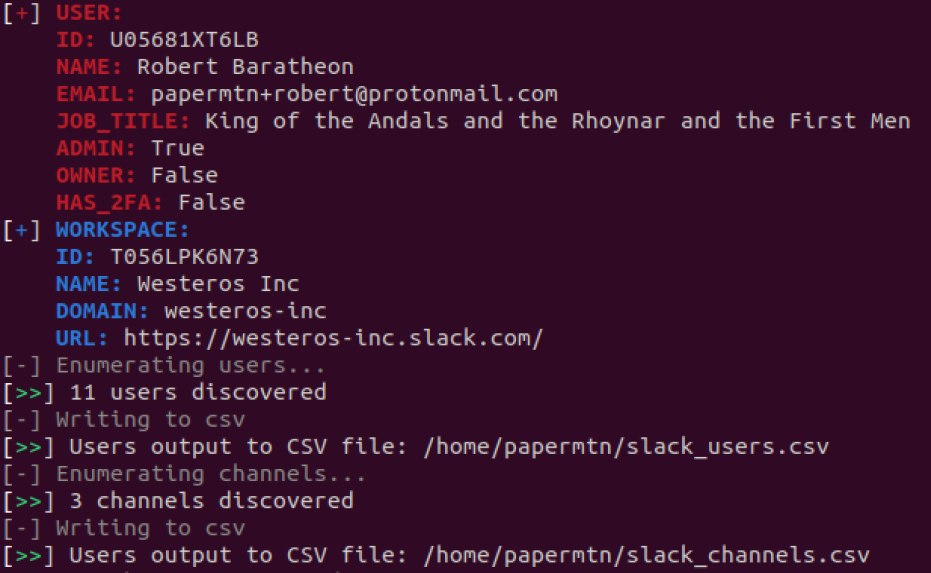 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool
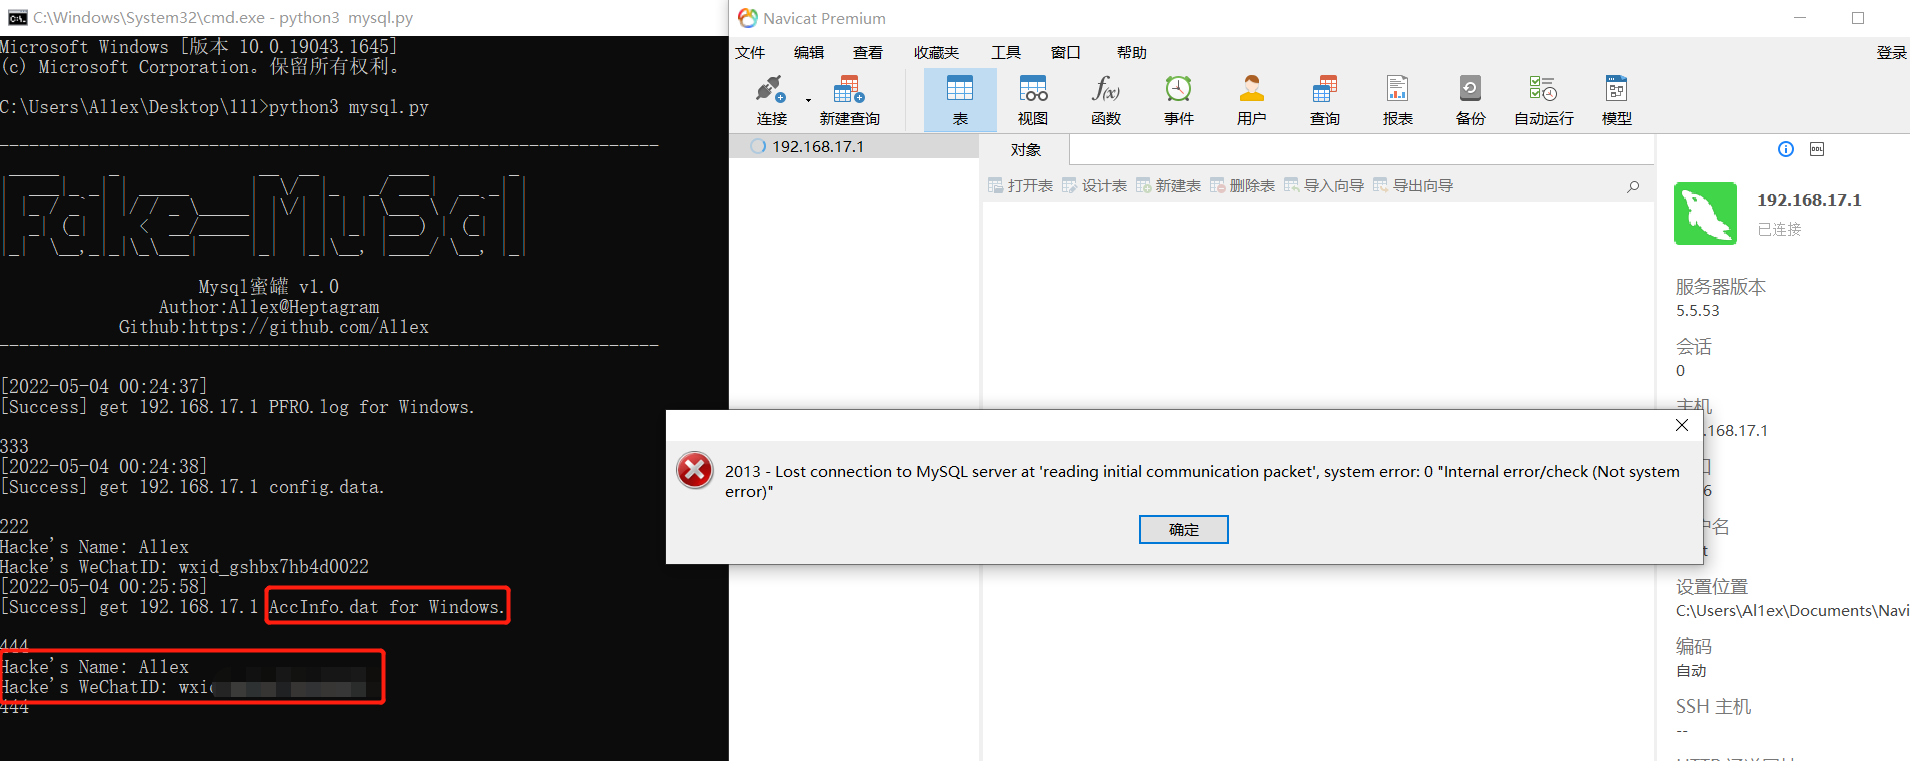 al1ex/mysqlhoneypot
MysqlHoneypot
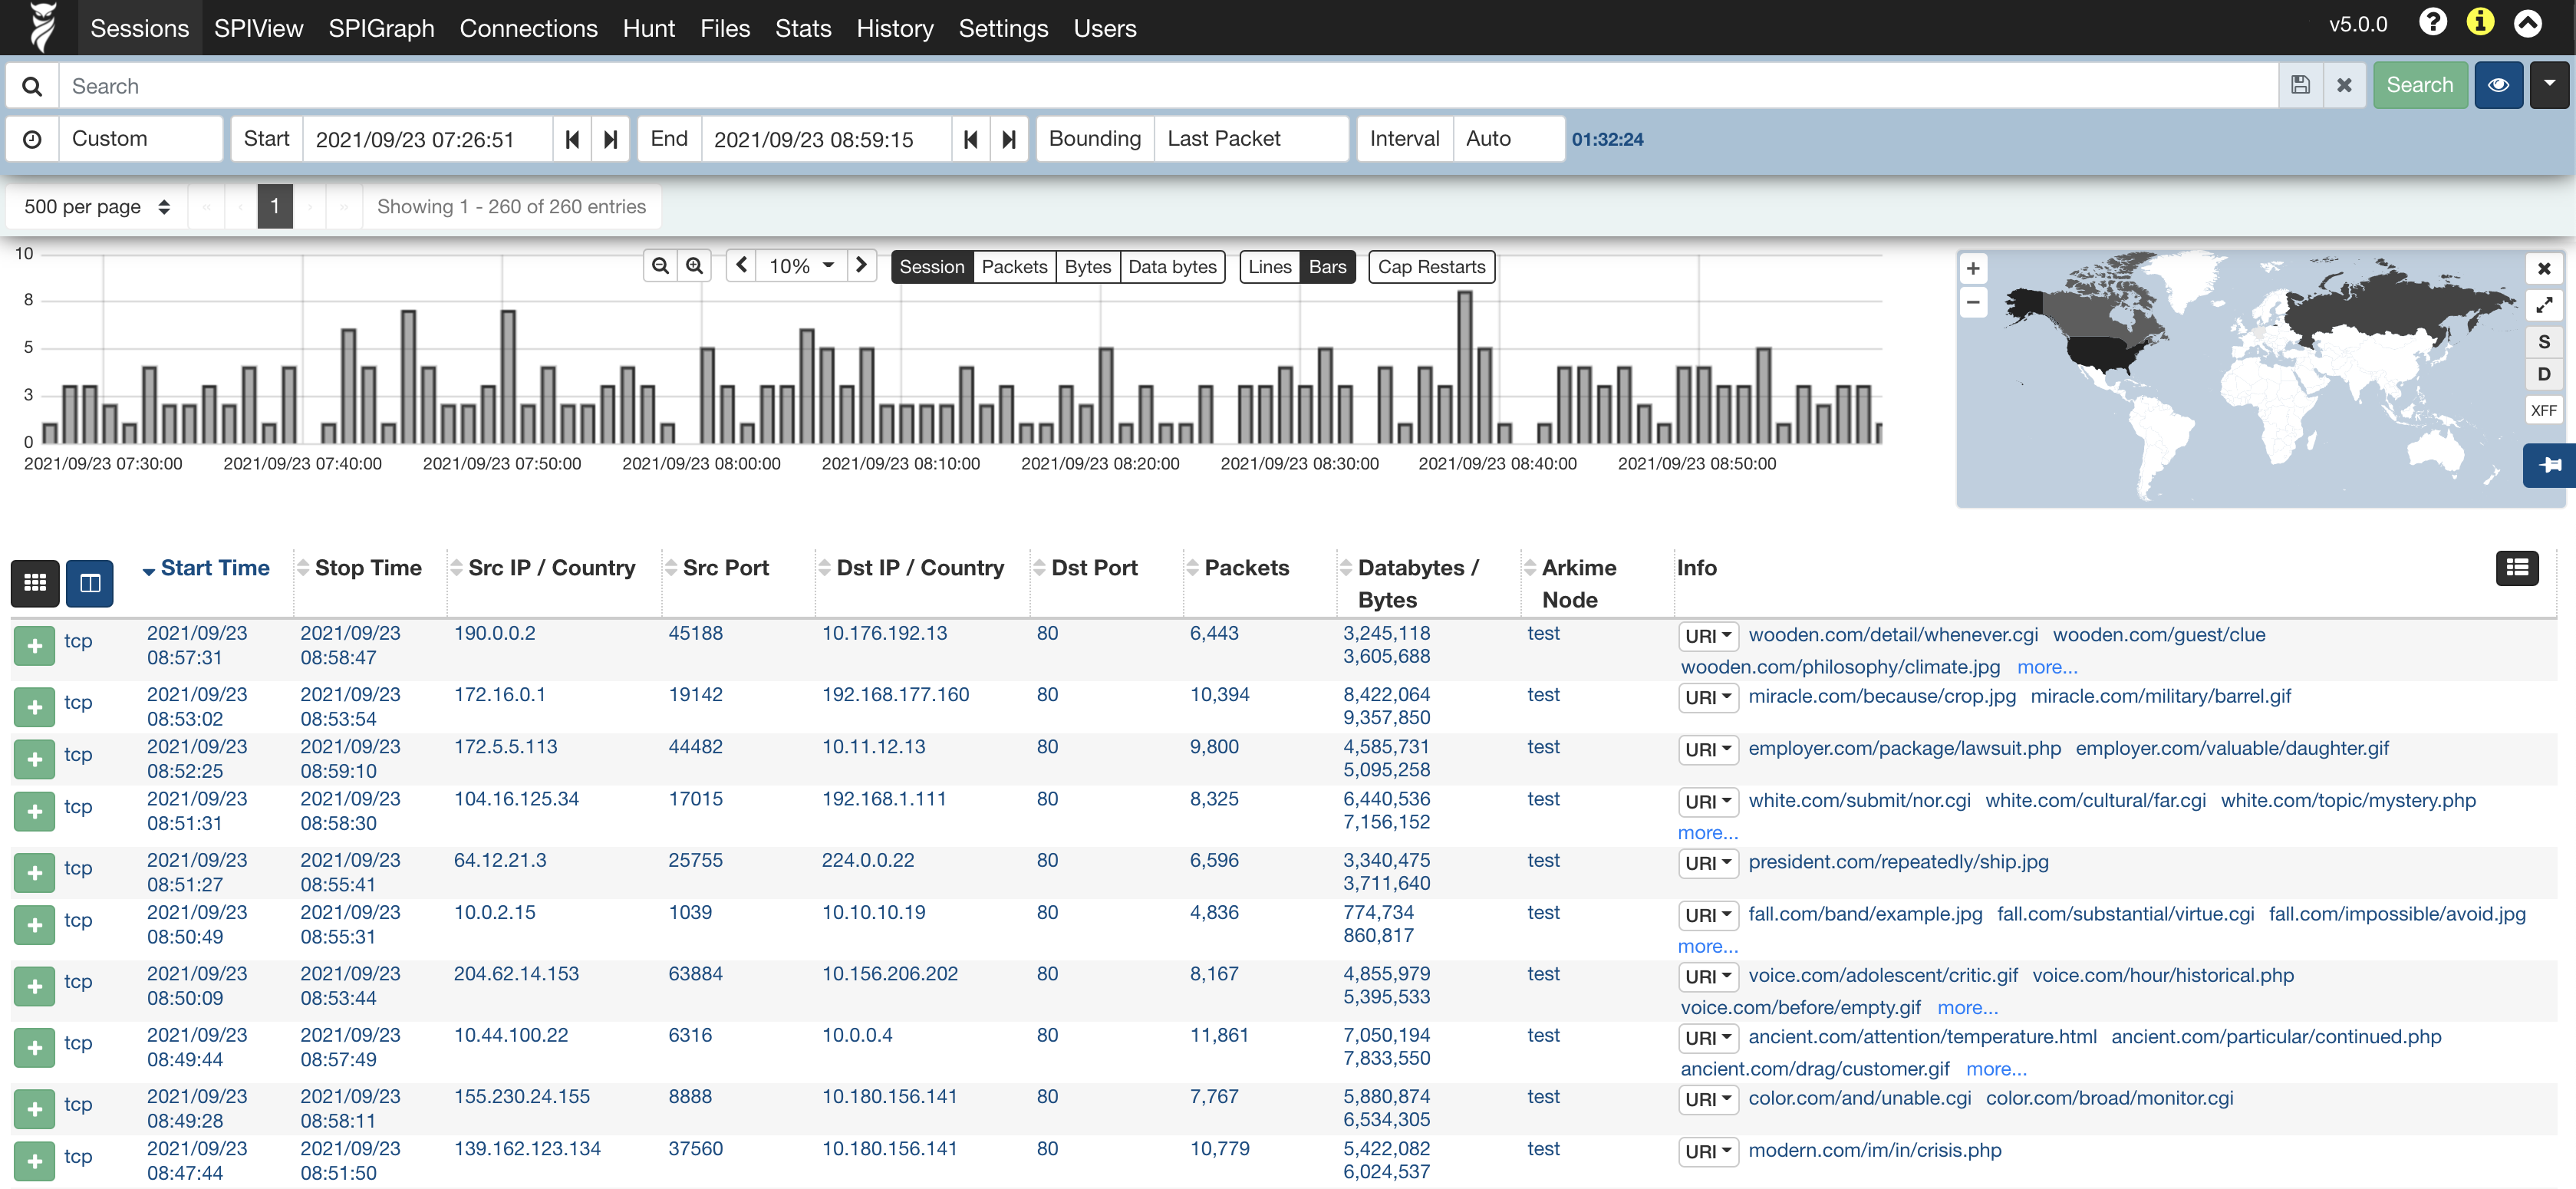 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 specterops/bloodhound
Six Degrees of Domain Admin
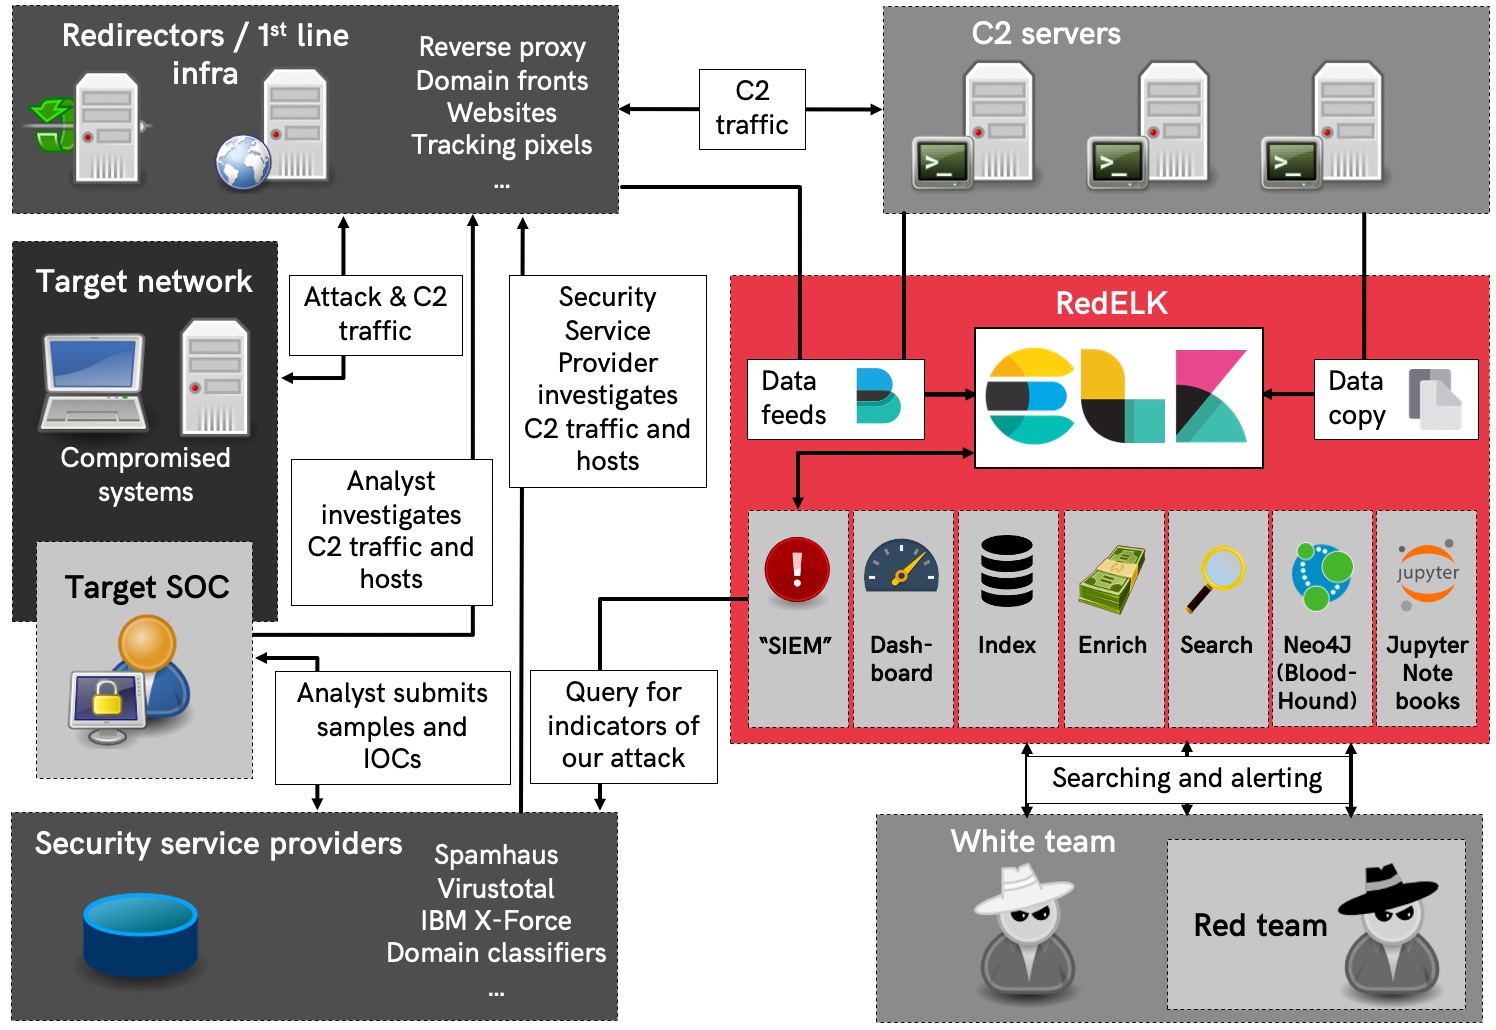 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 ransomlook/ransomlook
Yet another Ransomware gang tracker
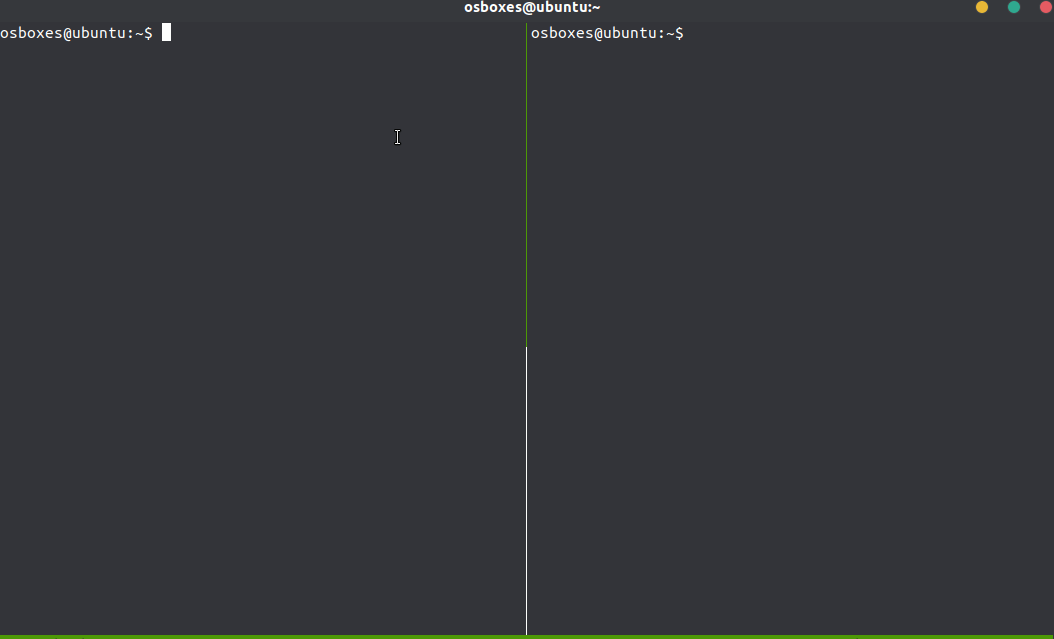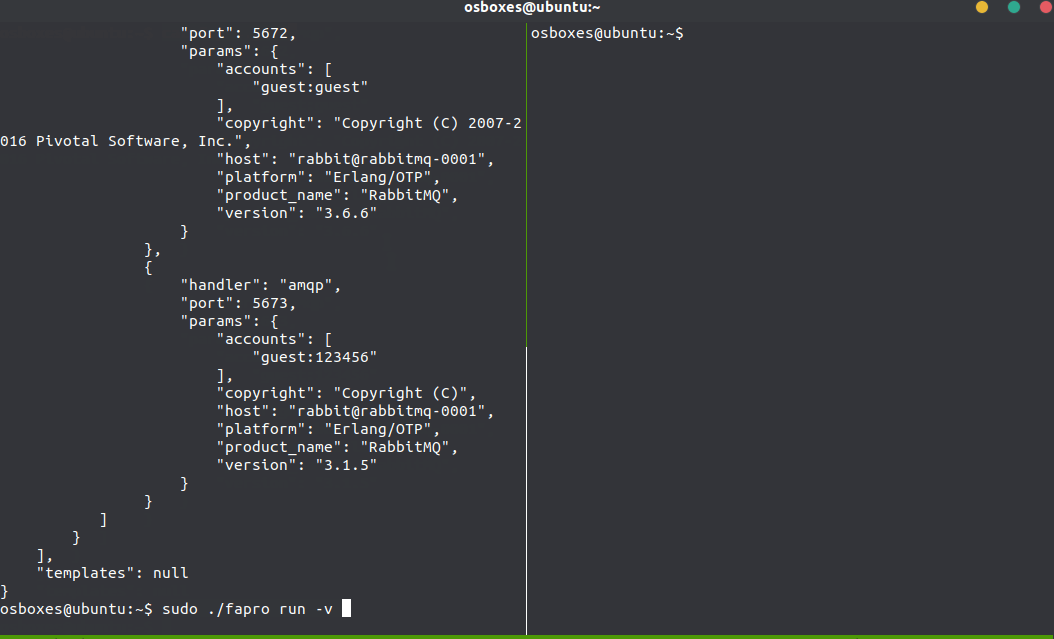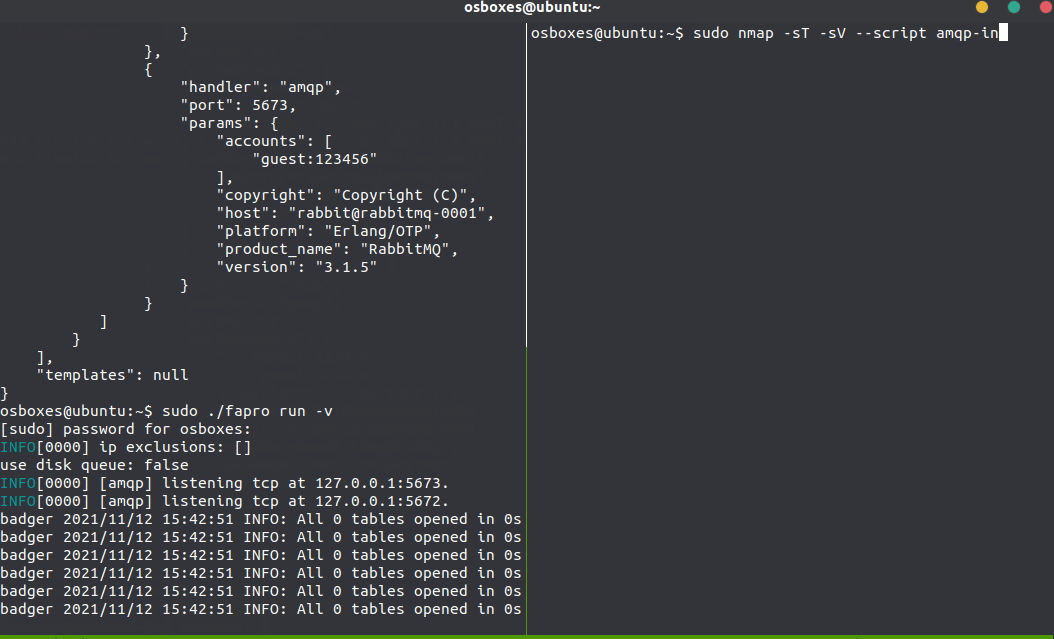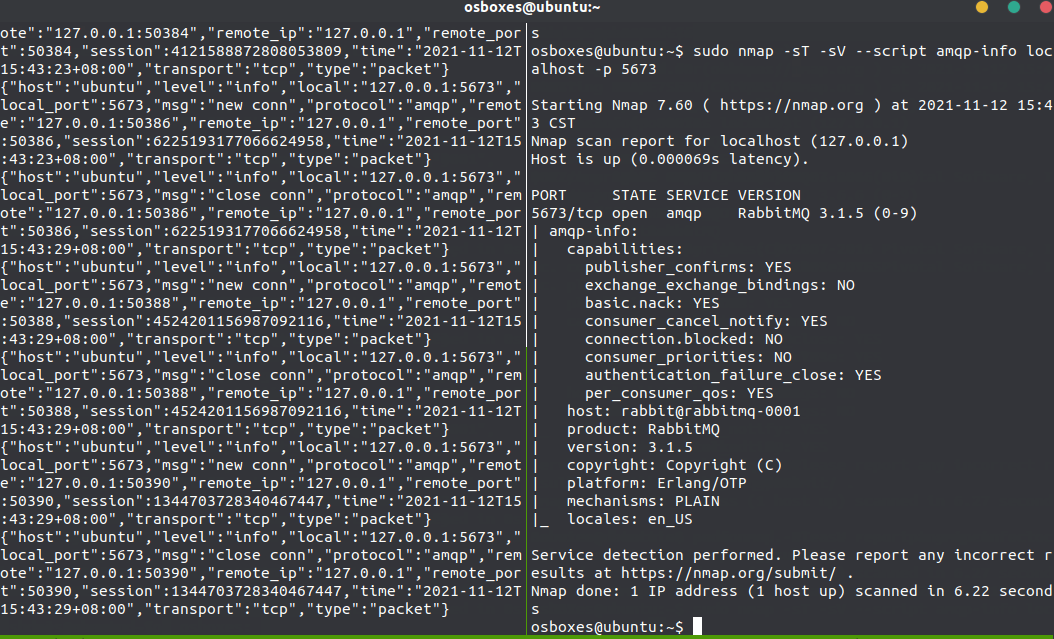 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 qeeqbox/chameleon
19 Customizable honeypots for monitoring network traffic, bots activities and username\password credentials (DNS, HTTP Proxy, HTTP, HTTPS, SSH, POP3,…
 spaceraccoon/manuka
A modular OSINT honeypot for blue teamers
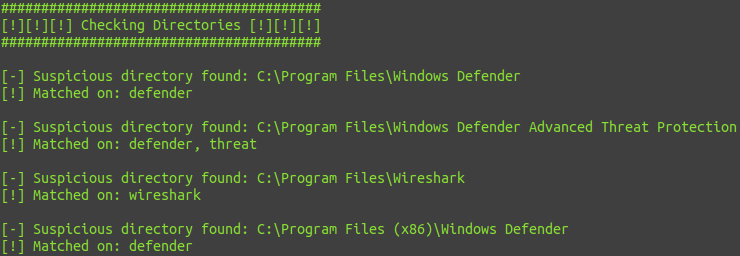 pwndexter/sharpedrchecker
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 fourcorelabs/edrhunt
Scan installed EDRs and AVs on Windows
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.