
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
62 results
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection

binary-analysisdebuggersdefensive-tools+1
231 month ago
ezEmu preview

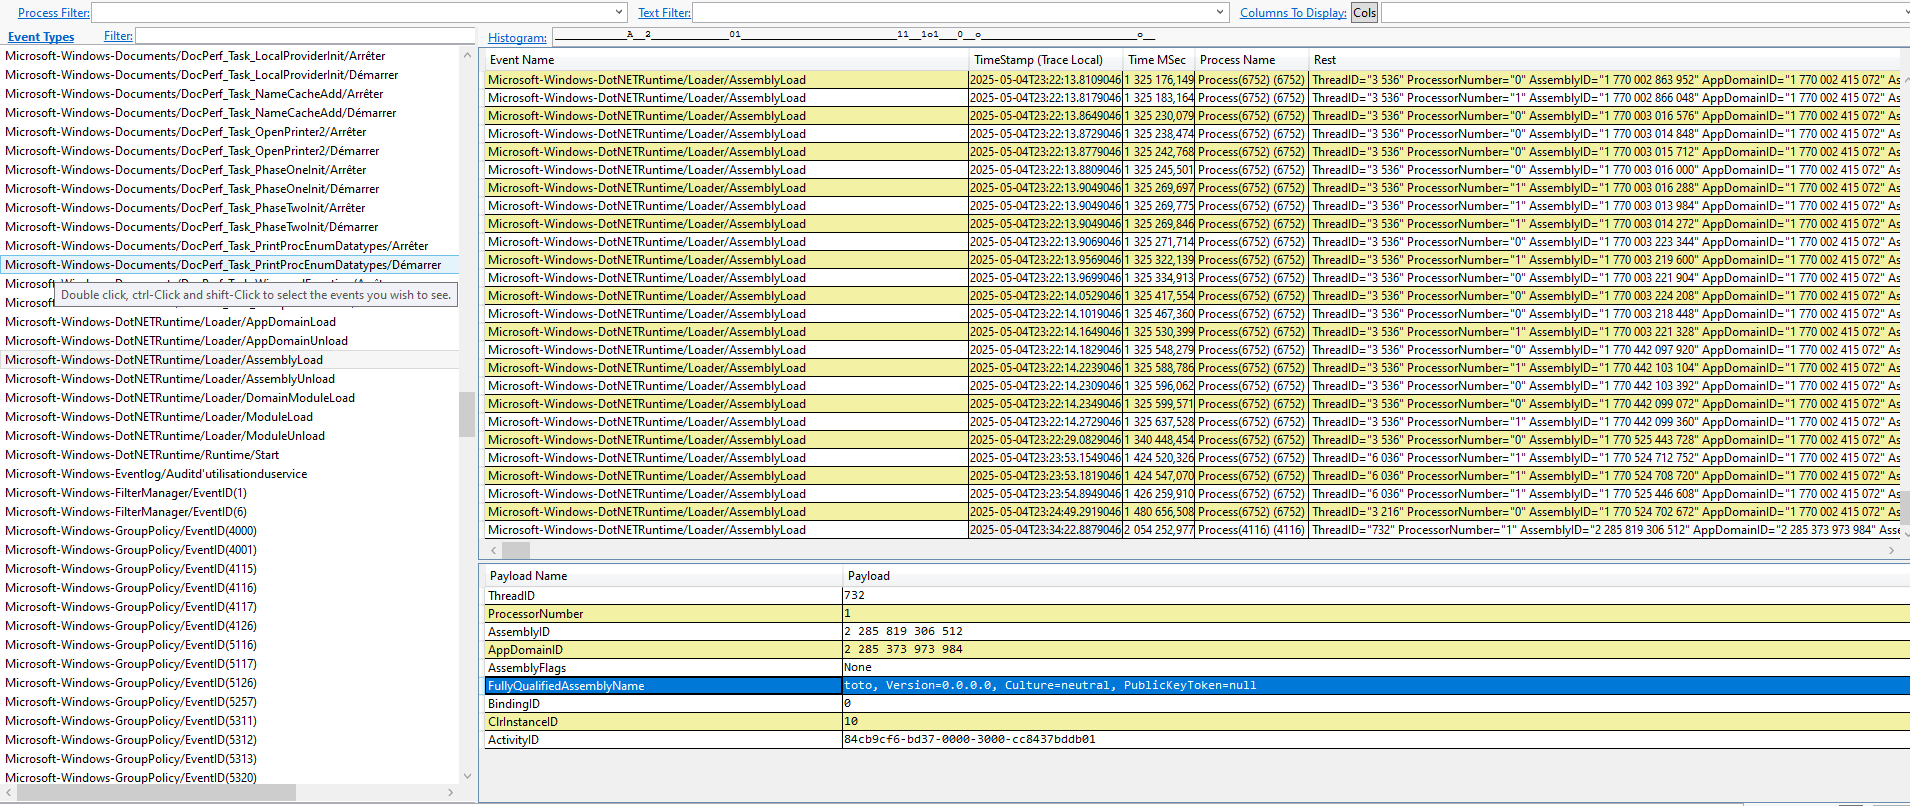
ezEmu

GitHubjwillyamz/ezemu

See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
adversarial-attackdefensive-toolseducation+3
1093 years ago
Metamorph preview

Metamorph

GitHubsynacktiv/metamorph

A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
defensive-toolsincident-responseinformation-gathering+3
84 months ago
sage preview

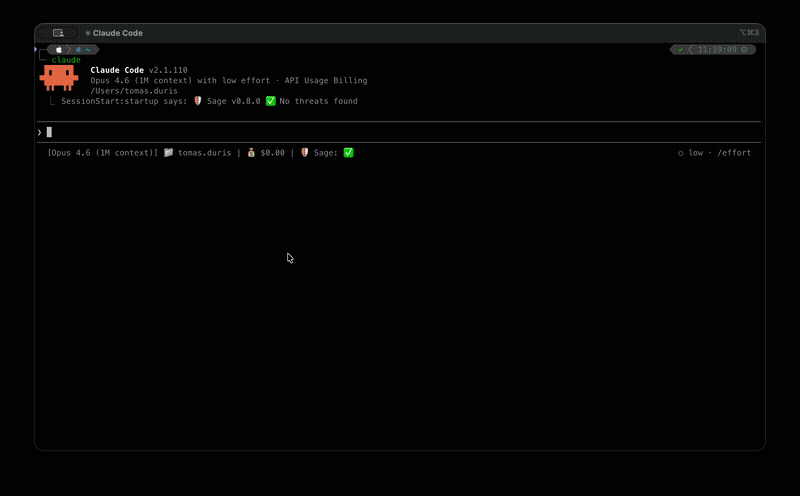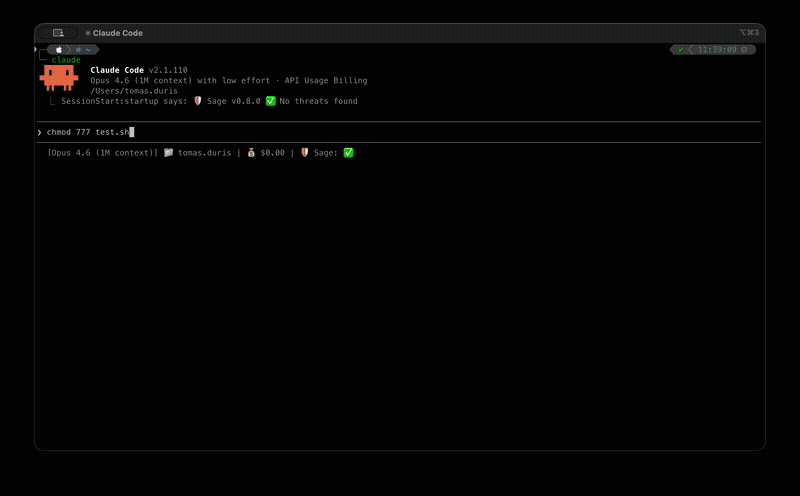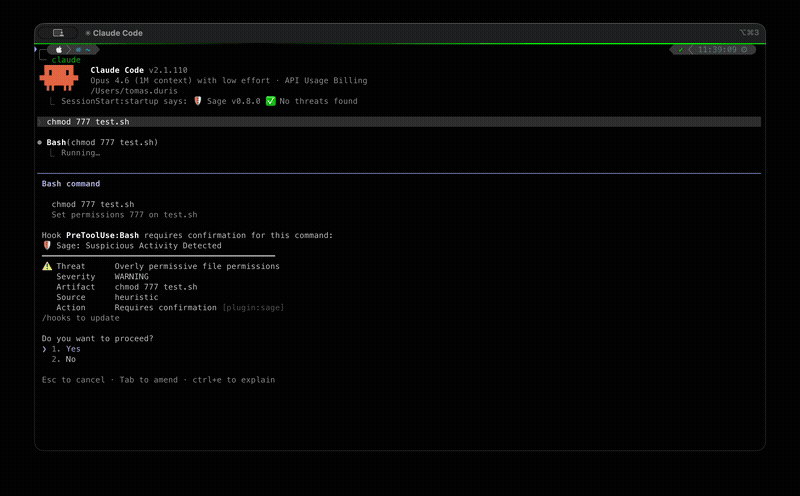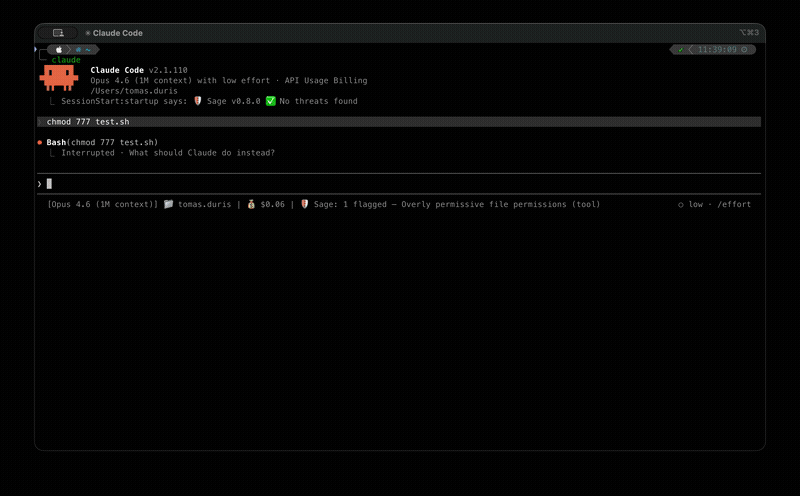
sage

GitHubgendigitalinc/sage

Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.

ai-securitycode-analysisdefensive-tools+6
31019 days ago
racketeer preview

racketeer

GitHubdsnezhkov/racketeer

Agent-based ransomware simulation toolkit for controlled detection testing across Windows endpoints and network assets, with a cross-platform…
command-and-controldefensive-toolsincident-response+1
705 years ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
defensive-toolsdigital-forensicsincident-response+3
196 years ago
sigma-cli preview

sigma-cli

GitHubsigmahq/sigma-cli

The Sigma command line interface based on pySigma
defensive-toolsintrusion-detectionlog-analysis+2
2161 day ago
Adrenaline preview

Adrenaline

GitHubatomiczsec/adrenaline

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.

command-and-controldefensive-toolsinformation-gathering+7
3191 month ago
Hack Tools preview

Hack Tools

GitLabedu0x01/hack-tools

Project that brings together several pentest tools

command-and-controlcurated-resourcesdefensive-tools+9
22 years ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1614 days ago
LOLSpoof preview

LOLSpoof

GitHubitaymigdal/lolspoof

An interactive shell to spoof some LOLBins command line
command-and-controldefensive-toolspenetration-testing+3
1882 years ago
hawkopsec preview

hawkopsec

GitHubemrekybs/hawkopsec

One-tap Linux OPSEC hardening & anonymity toolkit
configuration-auditingdefensive-toolsincident-response+2
323 days ago
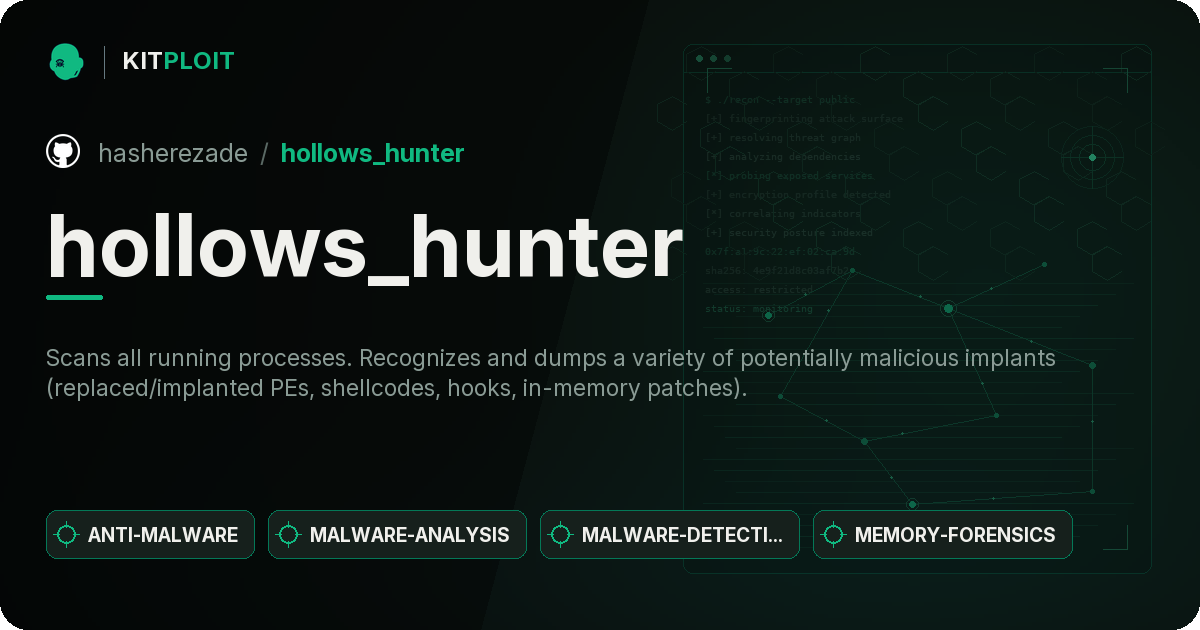
CVE-2026-73570 preview

CVE-2026-73570

GitHub0xblackash/cve-2026-73570

Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
defensive-toolseducationemail-security+6
15 days ago
hollows_hunter preview

hollows_hunter

GitHubhasherezade/hollows_hunter

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
defensive-toolsforensicsincident-response+2
2.4k4 months ago
BlackLotus preview

BlackLotus

GitHubldpreload/blacklotus

BlackLotus UEFI Windows Bootkit
command-and-controldefensive-toolsexploitation+8
2.2k2 years ago
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…

command-and-controldefensive-toolsexploitation+7
45311 months ago
Driver-hide-file preview

Driver-hide-file

GitHubgmh5225/driver-hide-file

choose and hide windows files/path from kernel space using this driver
defensive-toolspersistence-mechanisms
3 years ago
RedTeamSimmer preview

RedTeamSimmer

GitHubbreachsimrange/redteamsimmer

Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

adversarial-attackcommand-and-controldefensive-tools+7
81 month ago
Previous1234Next