
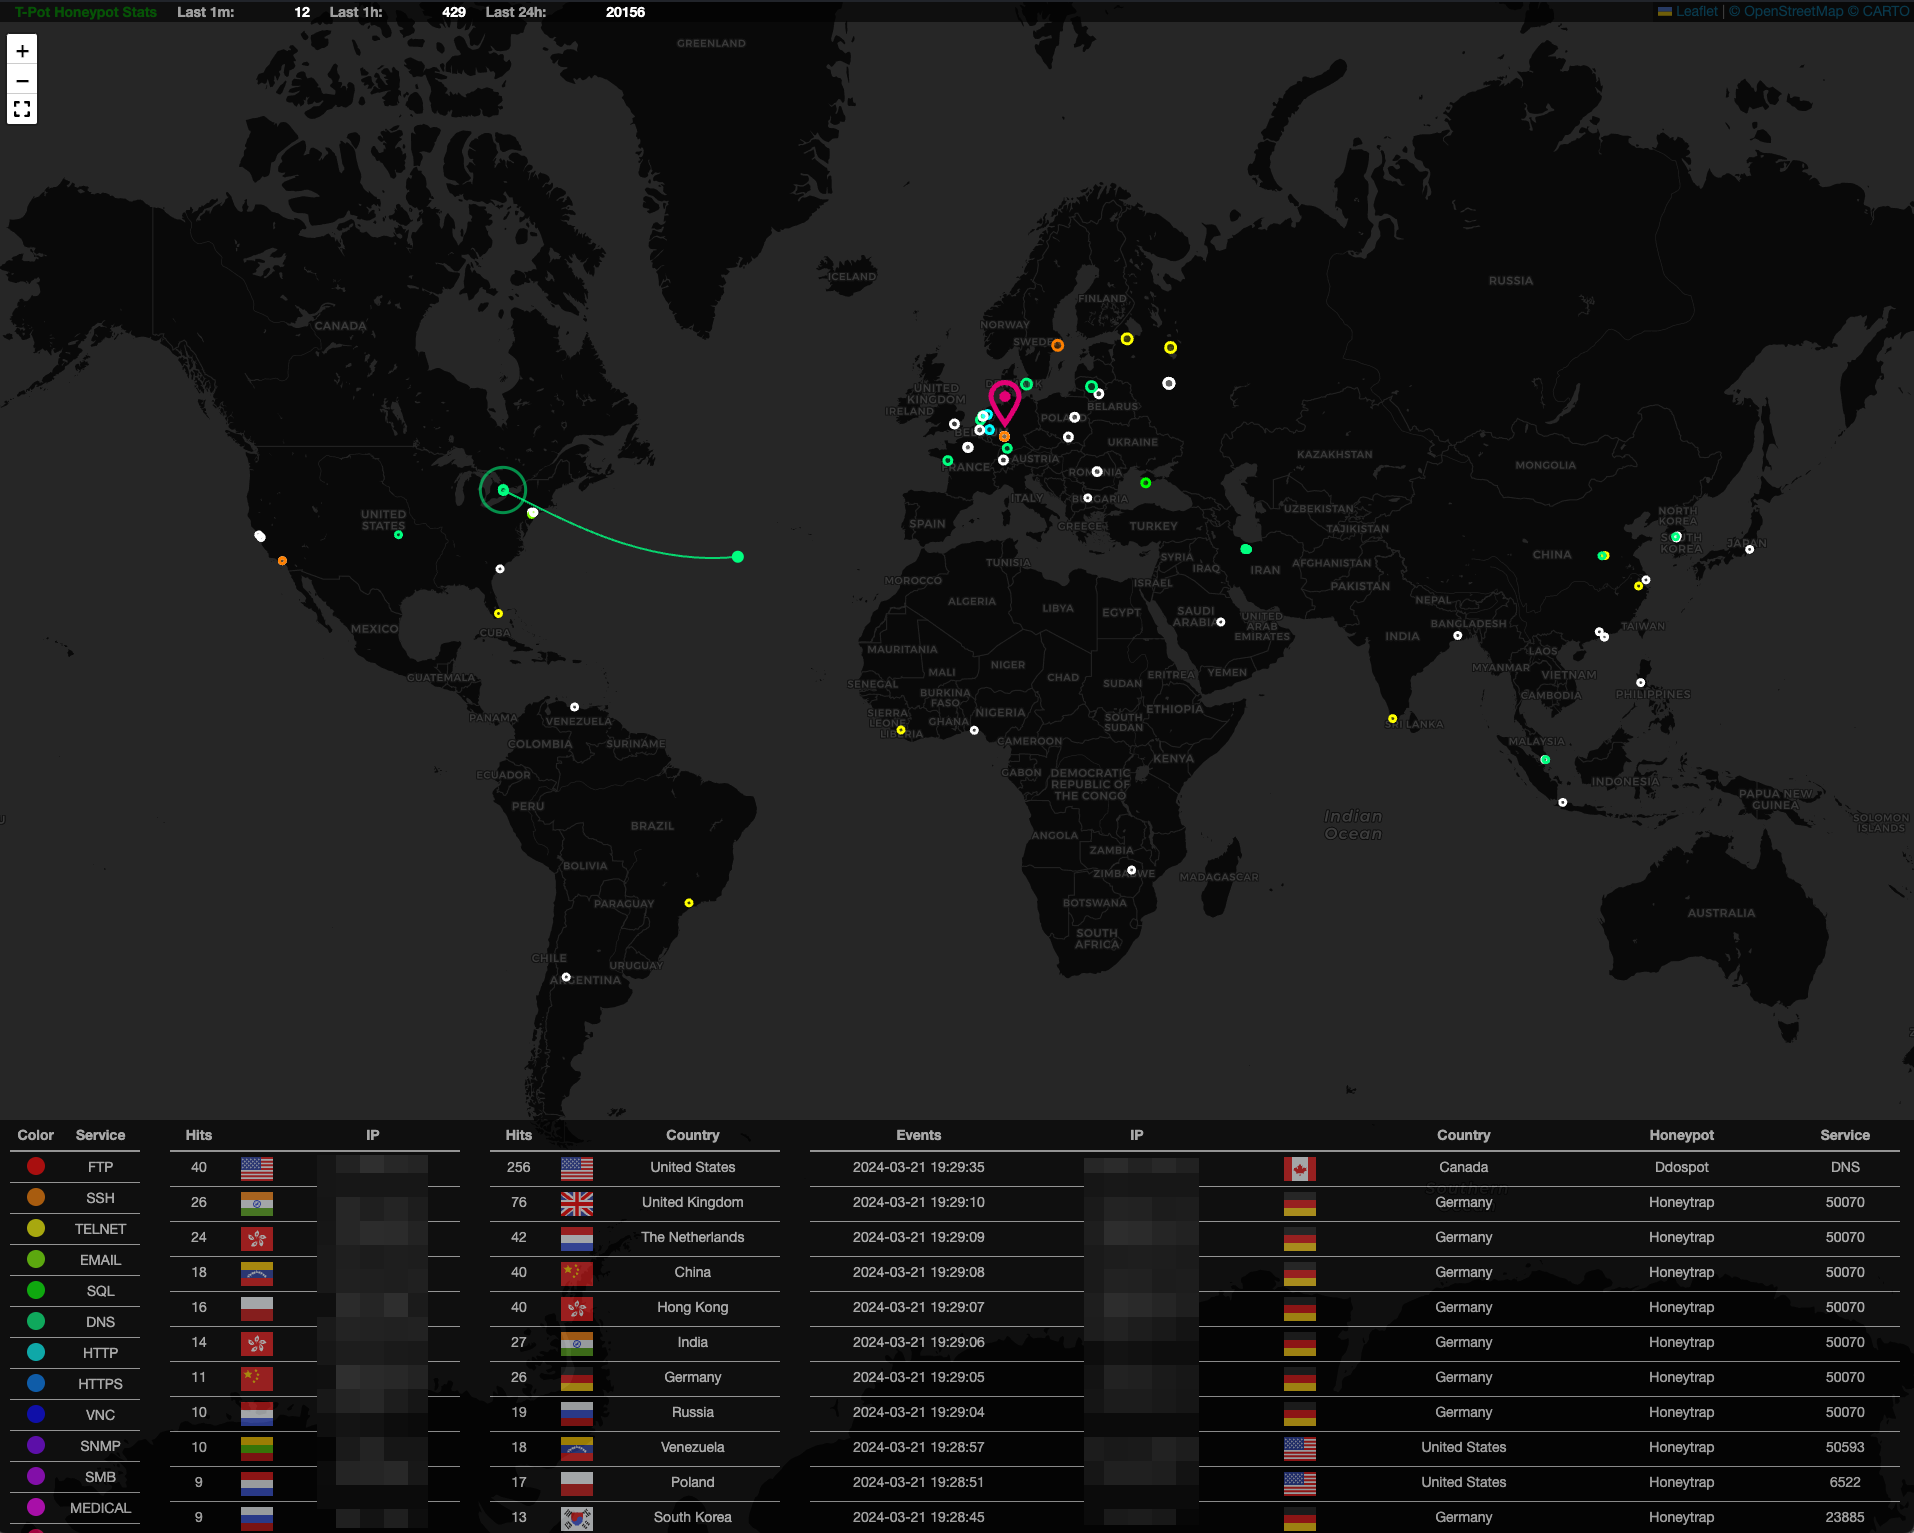
tpotce
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
telekom-security/tpotce🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 redcanaryco/chain-reactor
Generate Linux executables that simulate adversary behaviors and techniques for testing detection and response coverage. Consumes JSON for easy…
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
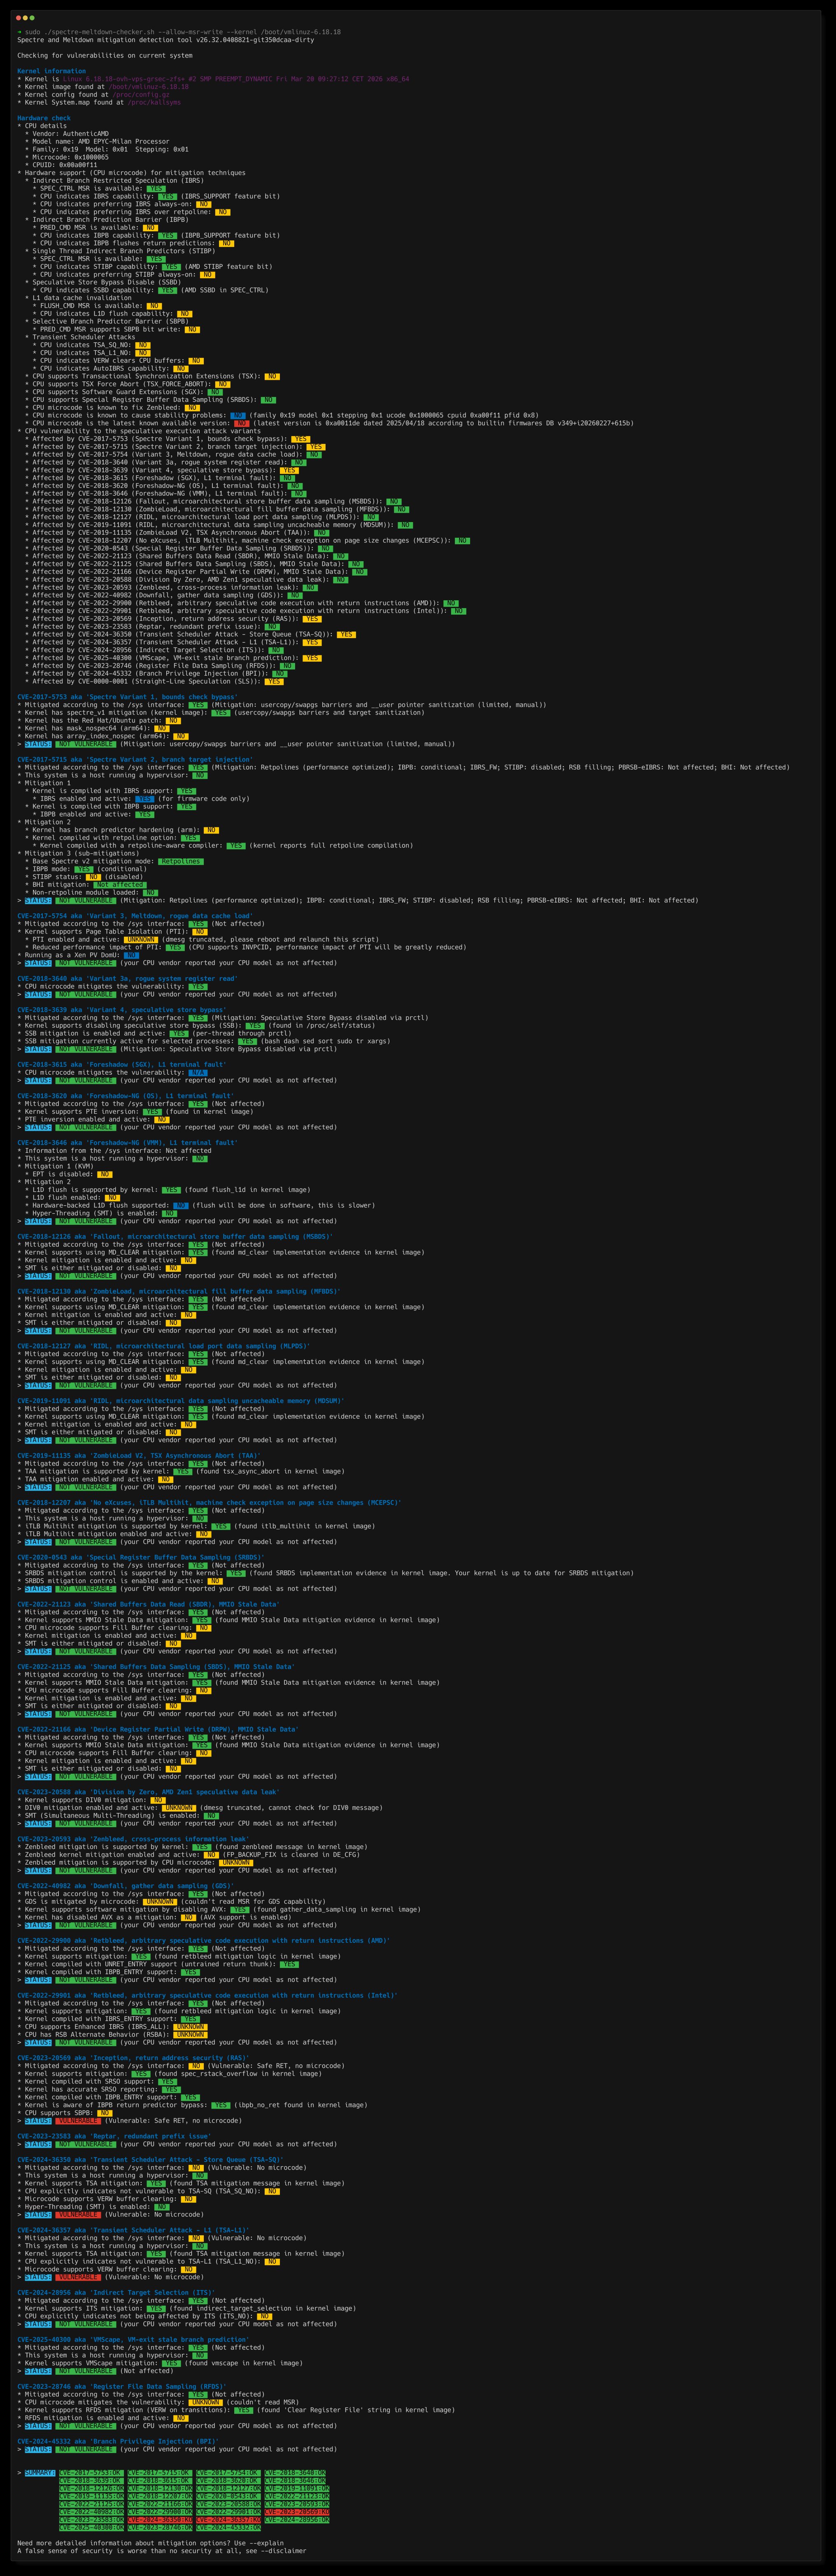 speed47/spectre-meltdown-checker
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 adeadukagi/cve-2023-32233-reproduction
Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 armircetaj/tetragon-dirtyfrag
Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
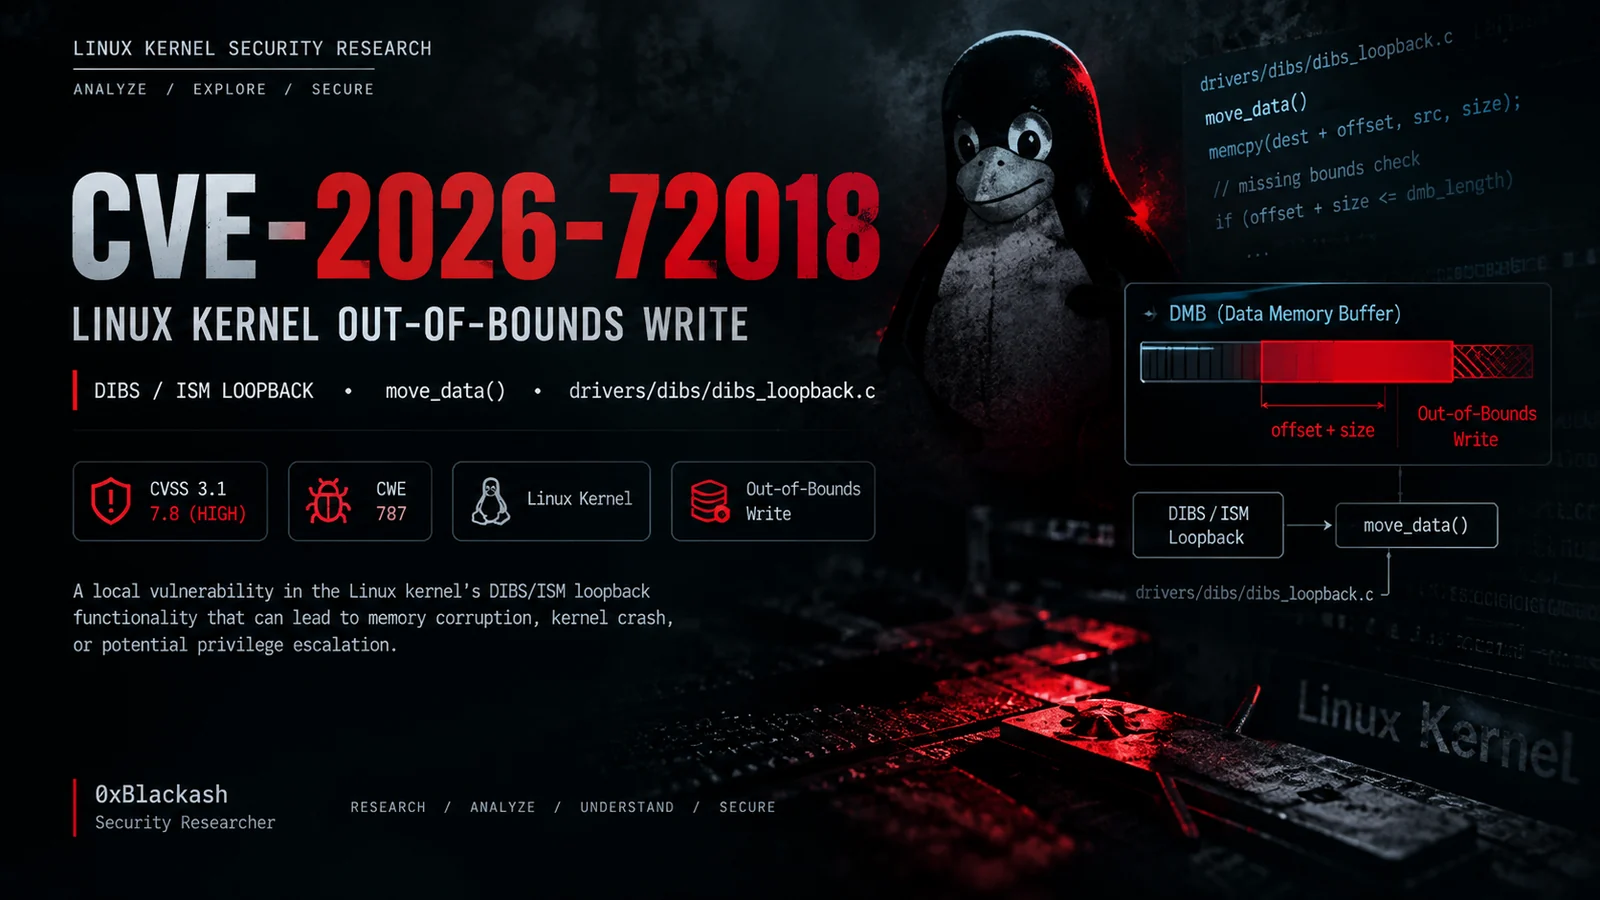 0xblackash/cve-2026-72018
Technical analysis of CVE-2026-72018, a Linux kernel out-of-bounds write in DIBS/ISM loopback, covering root cause, affected versions, detection, and…
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 haplessidiot/ageverificationbypass
Bypass age verification service from redhat
 yagnikkrish/metasploitable-penetration-testing-lab
Controlled penetration testing lab demonstrating CVE-2011-2523 exploitation and mitigation techniques.
 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 rabakuku/cve-2026-87902-a-working-poc-for-wordpress-s-critical-path-traversal
Reference notes and mitigation configs for CVE-2026-87902, a WordPress Core unauthenticated path traversal and LFI flaw chainable to RCE, with Nginx,…