
auditd
 neo23x0/auditd
Best Practice Auditd Configuration
configuration-auditingdefensive-toolsforensics+3
neo23x0/auditdBest Practice Auditd Configuration
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 foospidy/honeypy
A low to medium interaction honeypot.
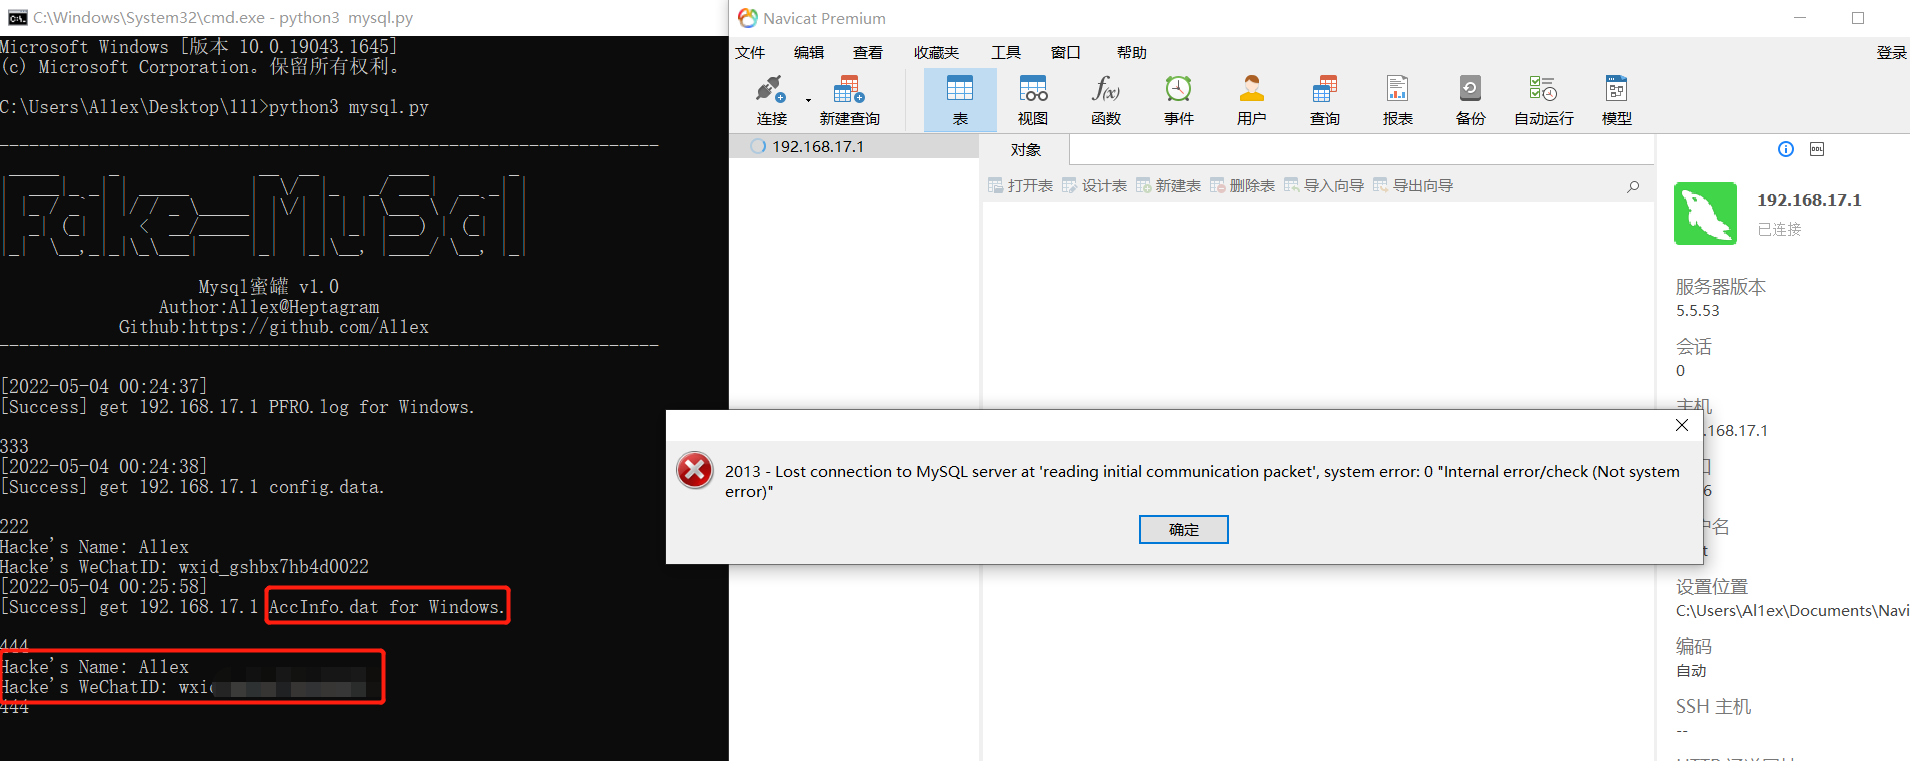 al1ex/mysqlhoneypot
MysqlHoneypot
 embee-research/sigma
A repository to release detection rules to the public
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
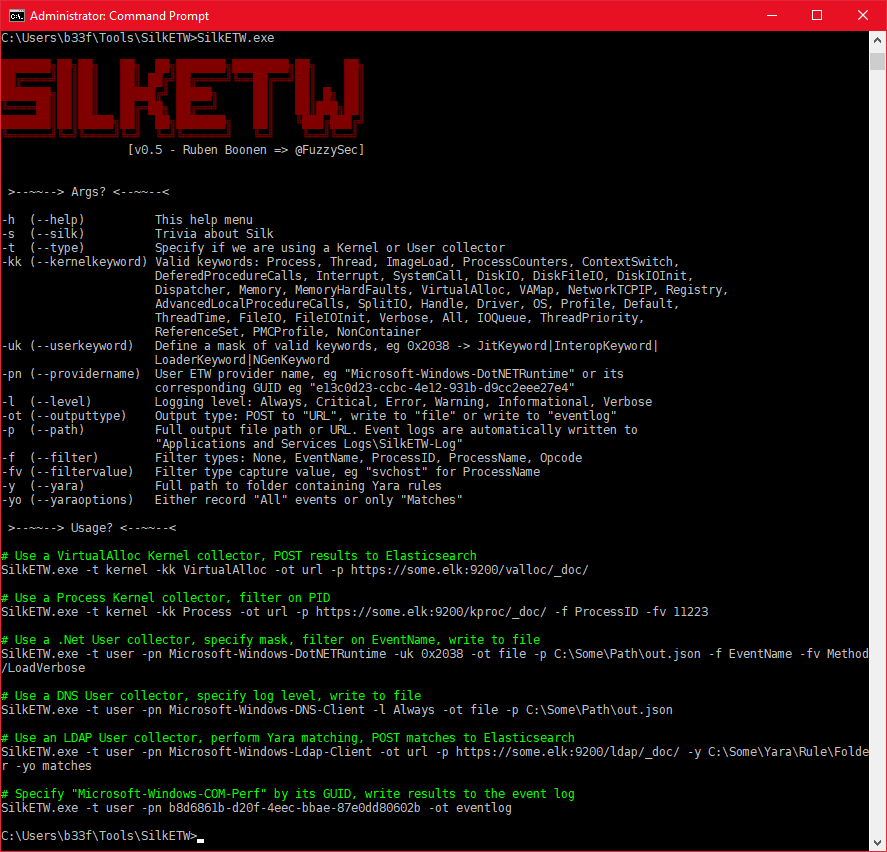 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 tsale/edr-telemetry
This project aims to compare and evaluate the telemetry of various EDR products.
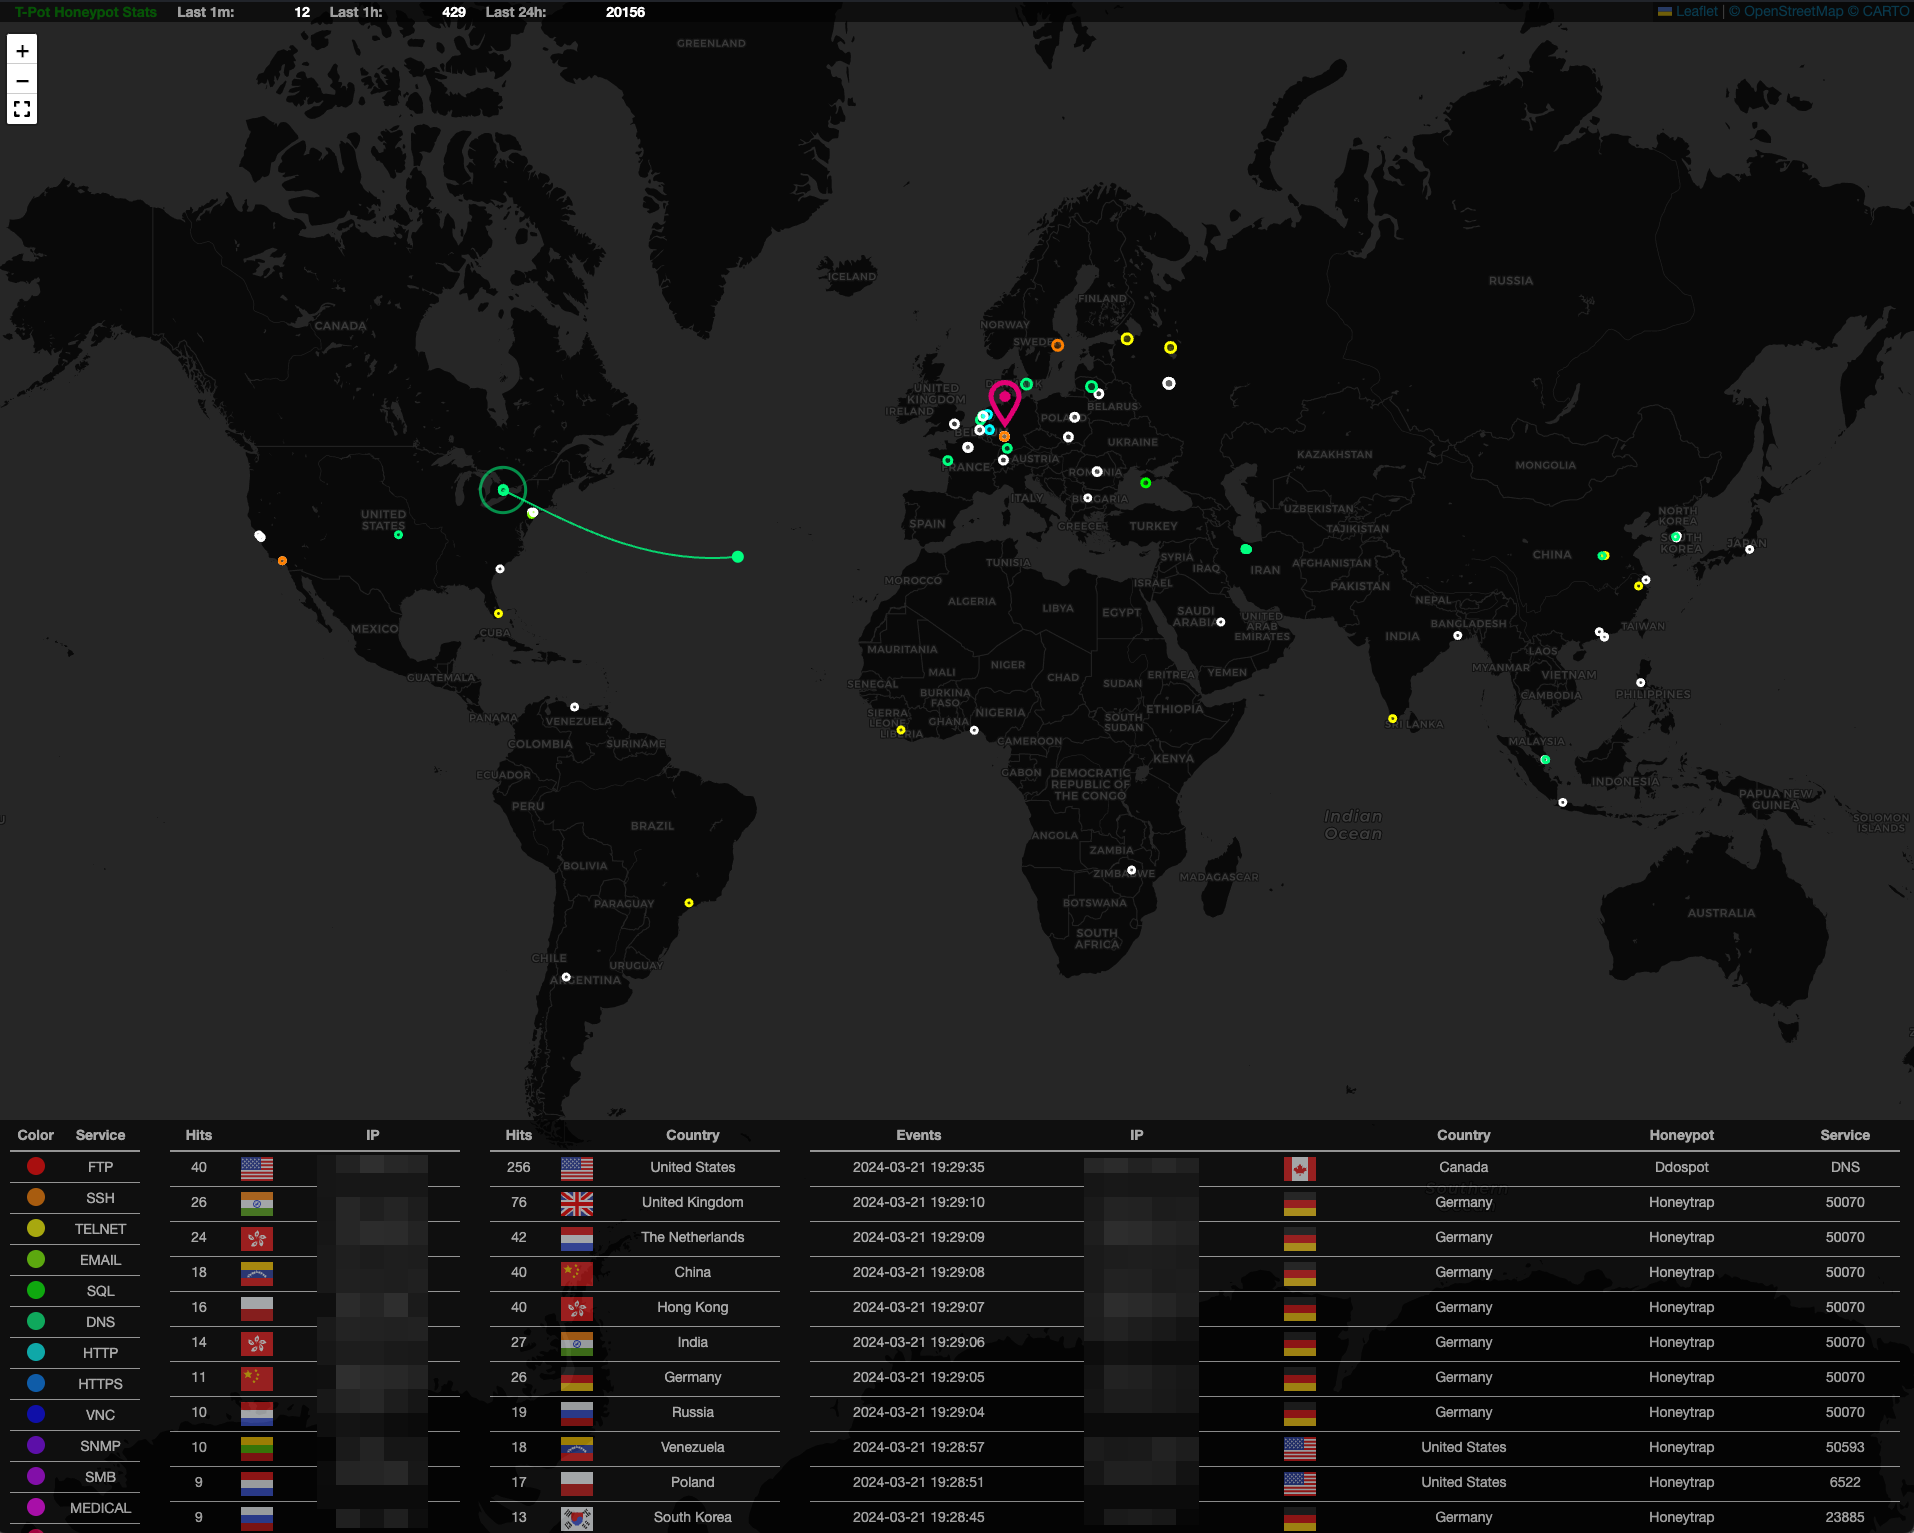 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 harendra-shakya/smart-contract-attack-vectors
A curated list of smart contract attack vectors
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 gmh5225/zeropoint
This PowerShell script detects indicators of compromise for CVE-2025-53770 — a critical RCE vulnerability in Microsoft SharePoint. Created by…
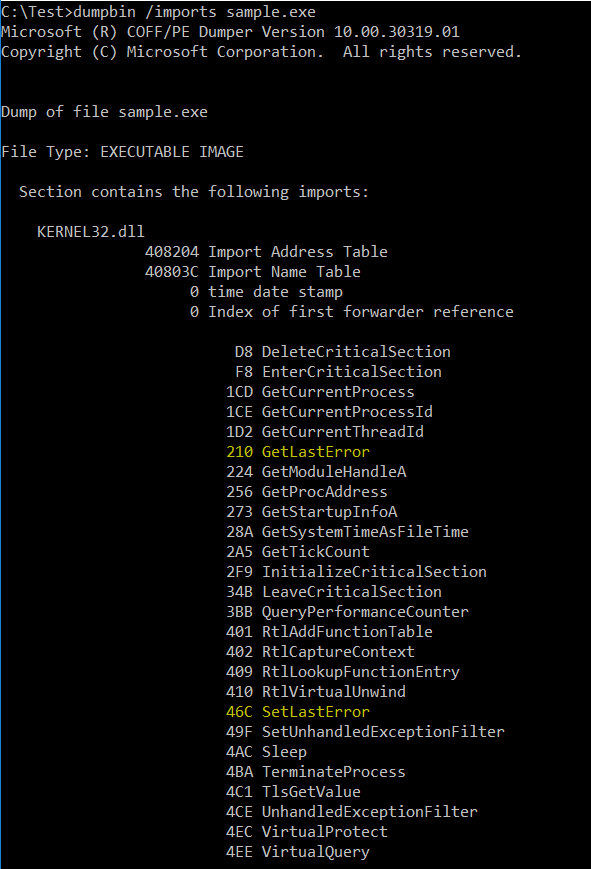 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 soteria-security/365inspect
A PowerShell script that automates the security assessment of Microsoft 365 environments.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting