sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…

Passive Linux host vulnerability scanner for CVE-2026-31694: checks running kernel, FUSE config, package metadata, and patch evidence, then generates…

Detects exposure to CVE-2026-31431 (Copy Fail) and optionally mitigates by disabling the vulnerable algif_aead kernel module, providing verdicts and…

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…

Best Practice Auditd Configuration

eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…

A tool to recover from ESXiArgs ransomware


A python package for use in generating fake data for SOC and security automation.

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container

🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

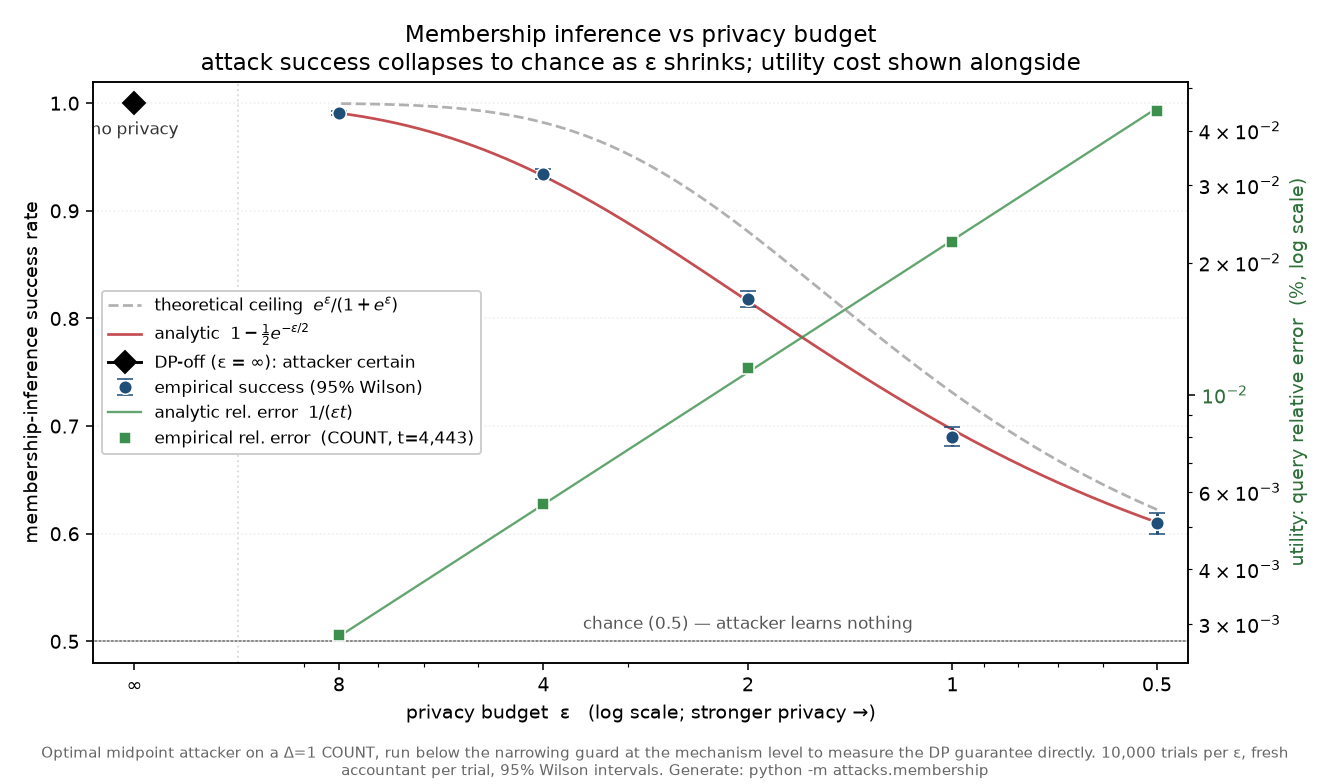
Noisegate: a differential privacy gateway that lets an untrusted LLM agent query sensitive data over MCP (Model Context Protocol), with a formal…

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…