

jev-ids
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
anomaly-detectiondefensive-toolsintrusion-detection+5
2611h 59m ago
jev-sec/jev-idsBlazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
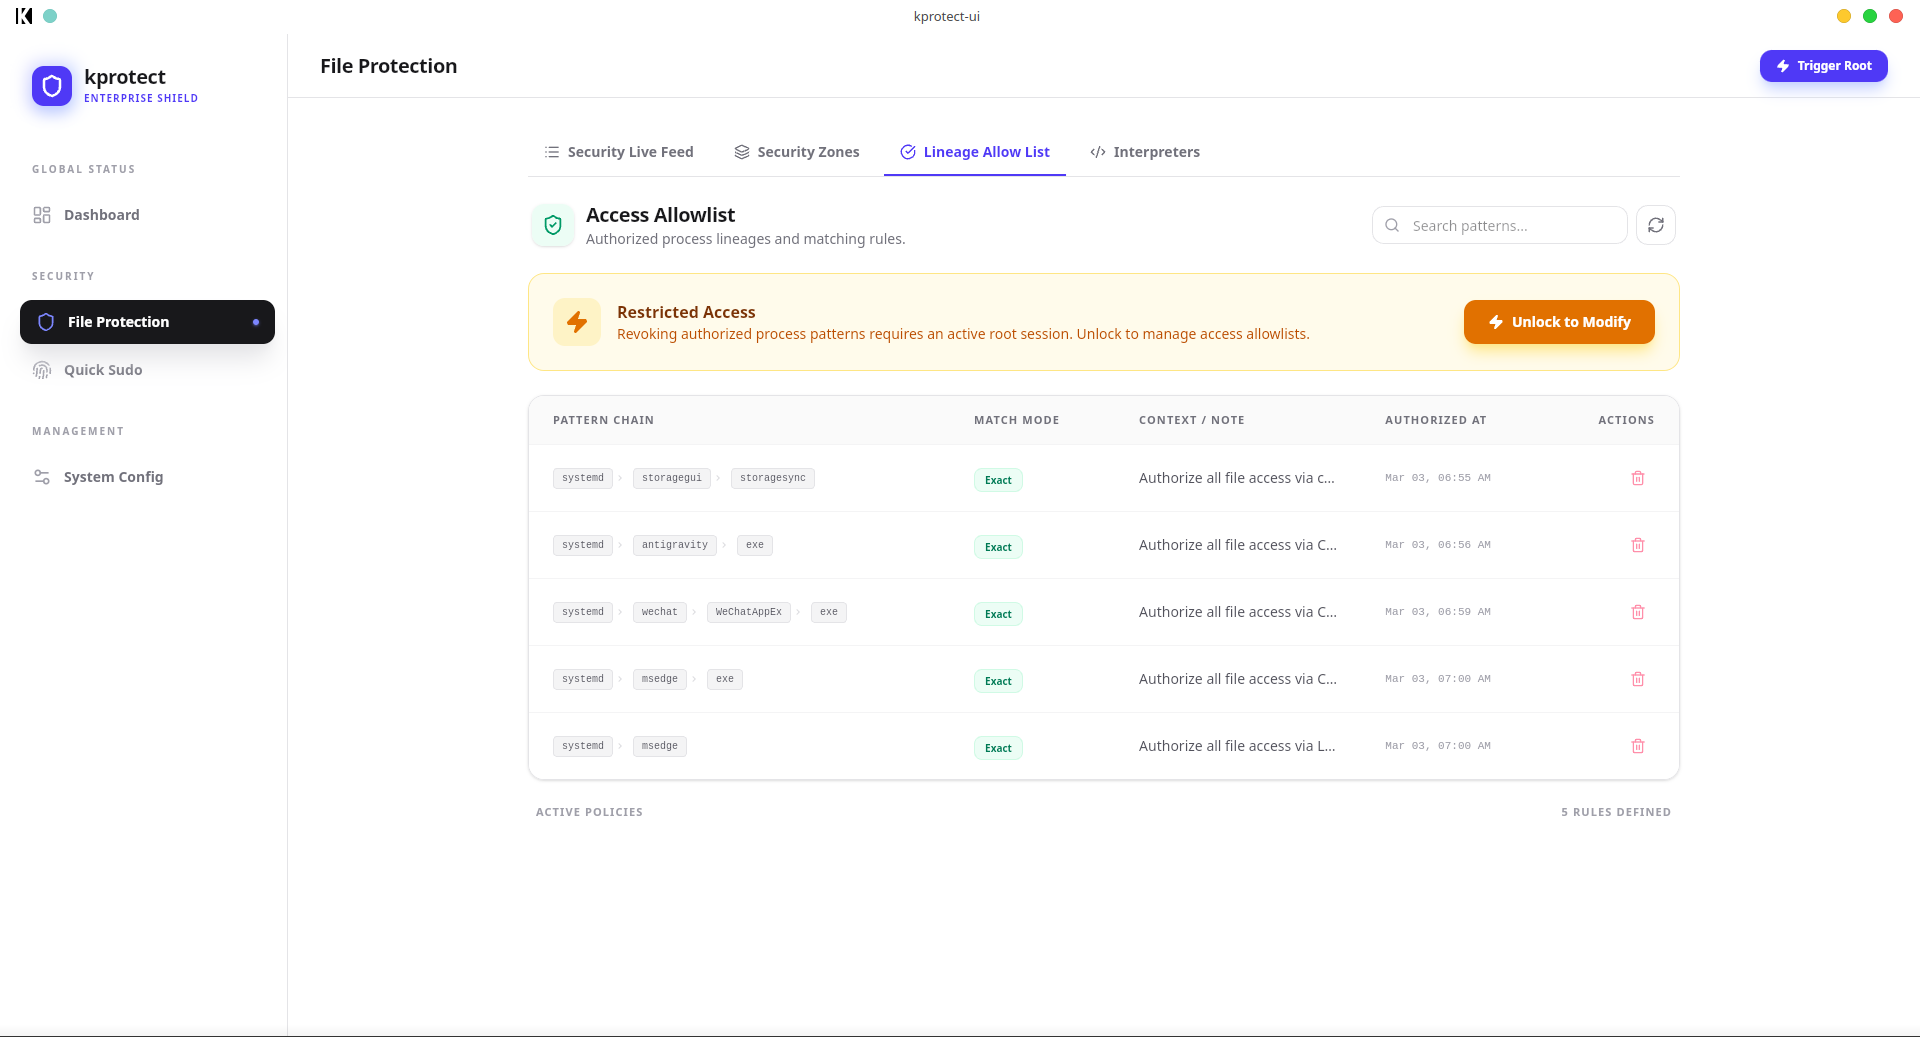 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 alperenugurlu/cmd_bypass_assessment
PowerShell script that automatically tests CMD bypass methods on Windows, evaluates results, calculates a security score, and provides hardening…
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 corelight/zeek-strrat-detector
A Zeek based STRRAT malware detector.
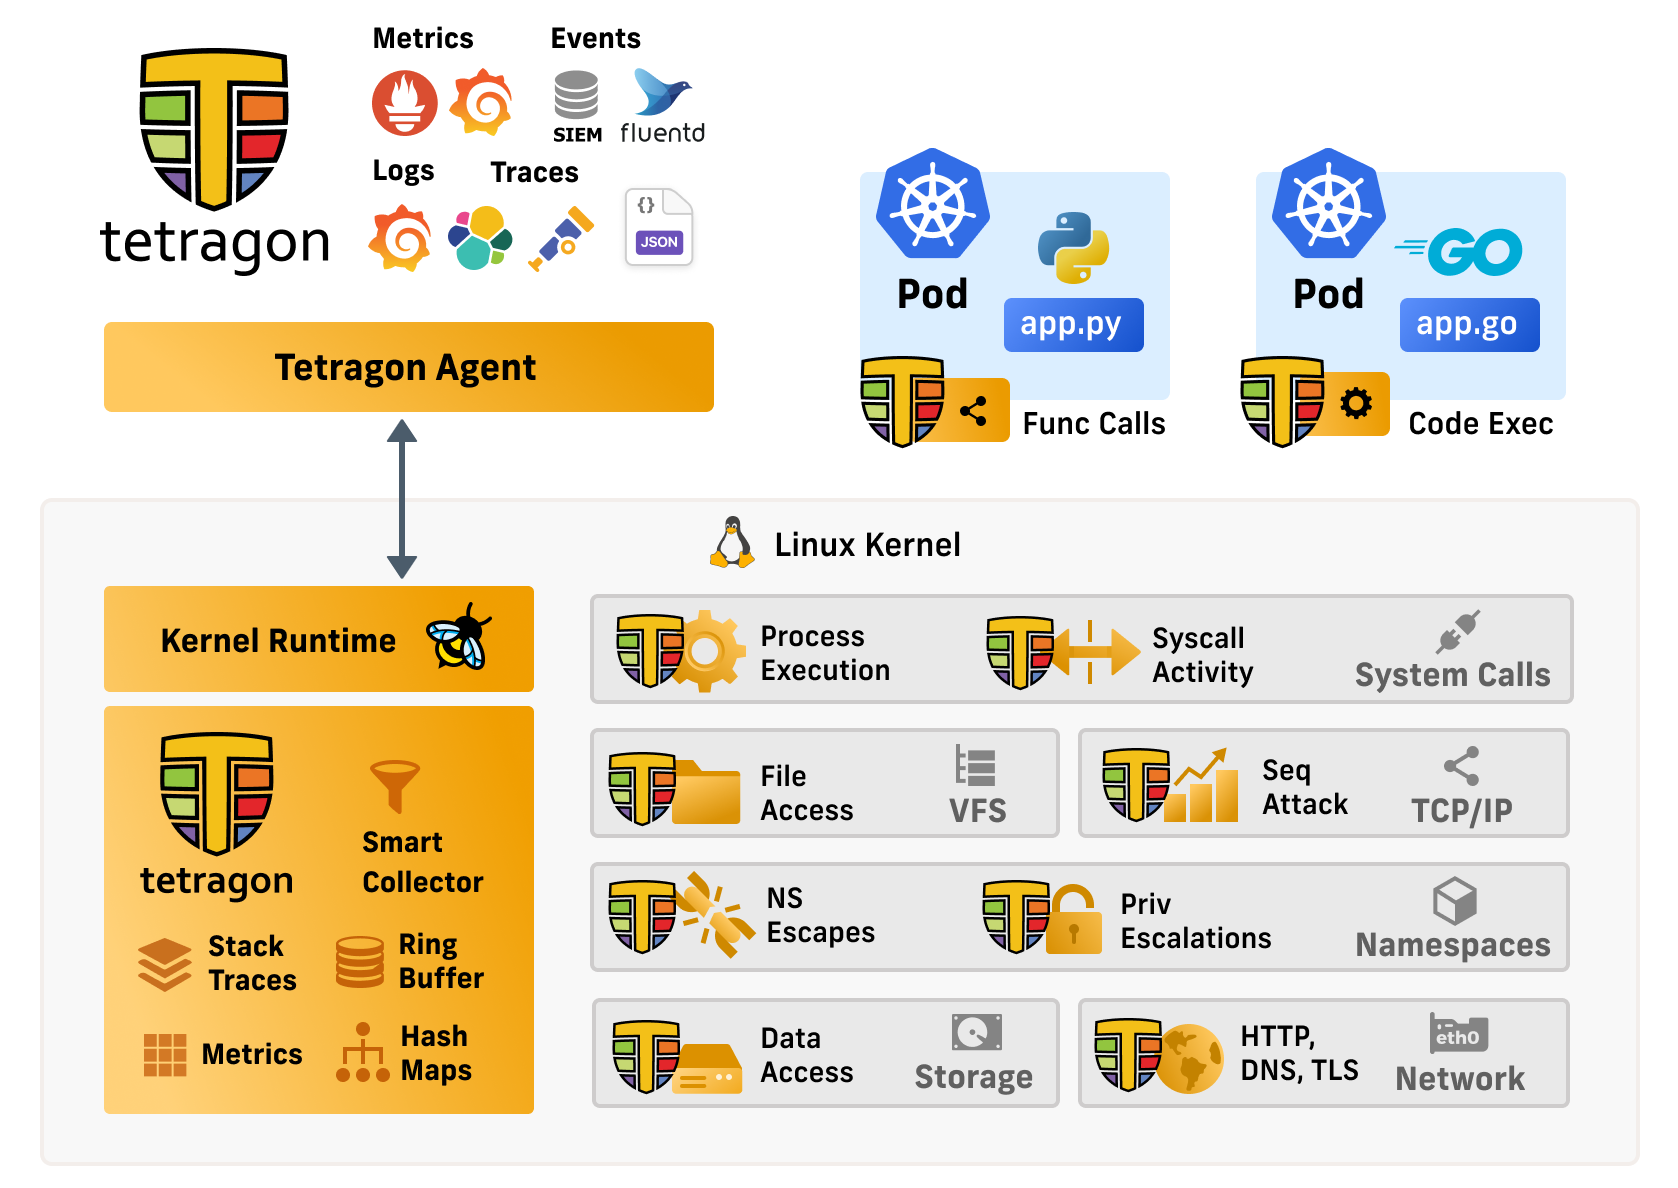 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement

 specterops/bloodhound
Six Degrees of Domain Admin
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
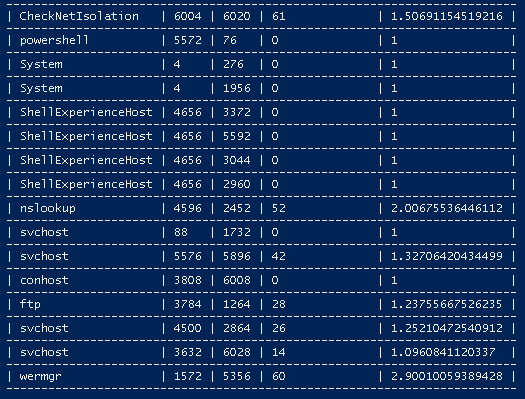 3lp4tr0n/beaconhunter
Detect and respond to Cobalt Strike beacons using ETW.
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits