
graylog2-server
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
defensive-toolsincident-responseintrusion-detection+1
8.2k
graylog2/graylog2-serverCentralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 fail2ban/fail2ban
Daemon to ban hosts that cause multiple authentication errors
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

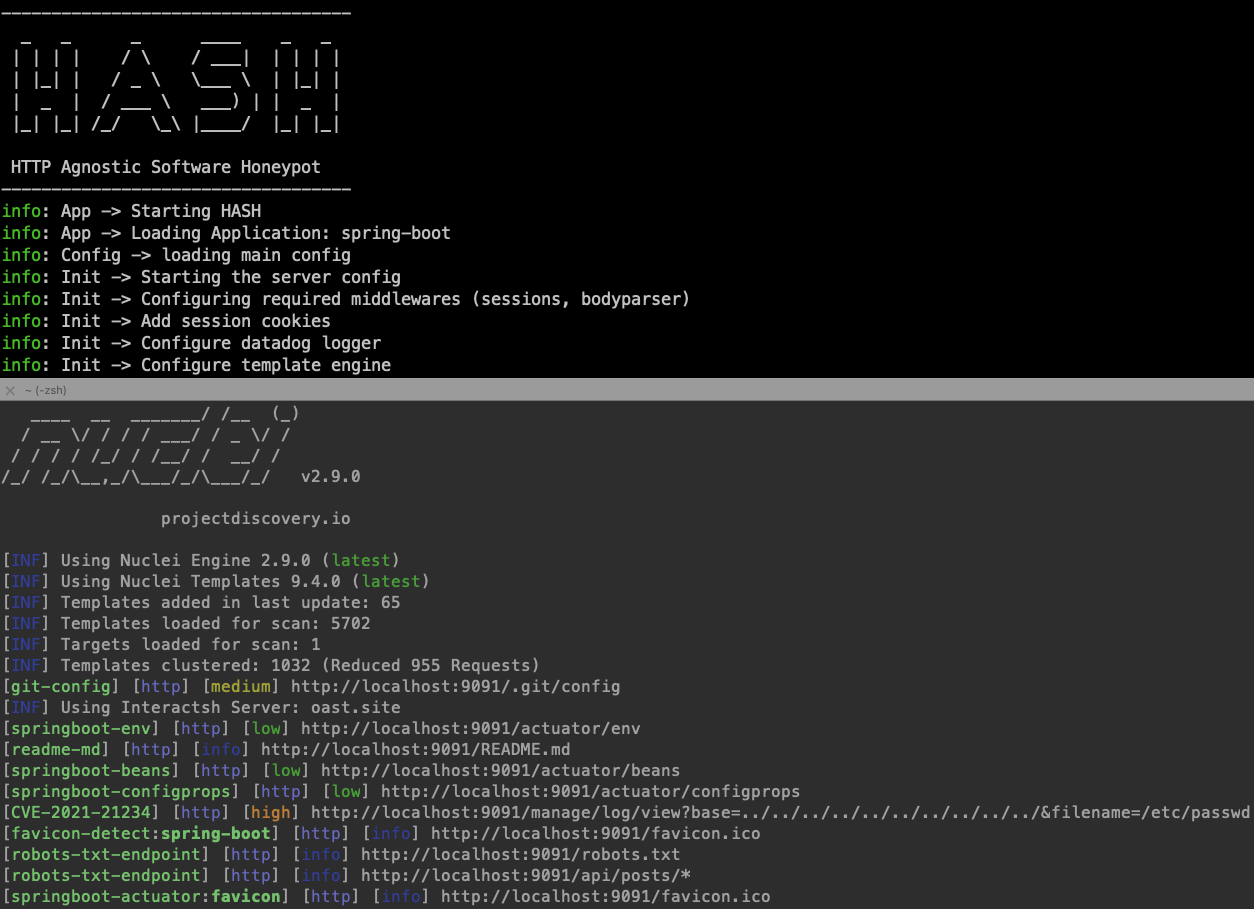 datadog/hash
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.

 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…