

OpcUaTrap
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
defensive-toolsincident-responseinformation-gathering+5
2
0xajstrike/opcuatrapHigh-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 gmh5225/offensivedriver
Windows kernel driver prototype that toggles process protection, adjusts process privileges, patches DSE policy, and manipulates AV/EDR kernel…
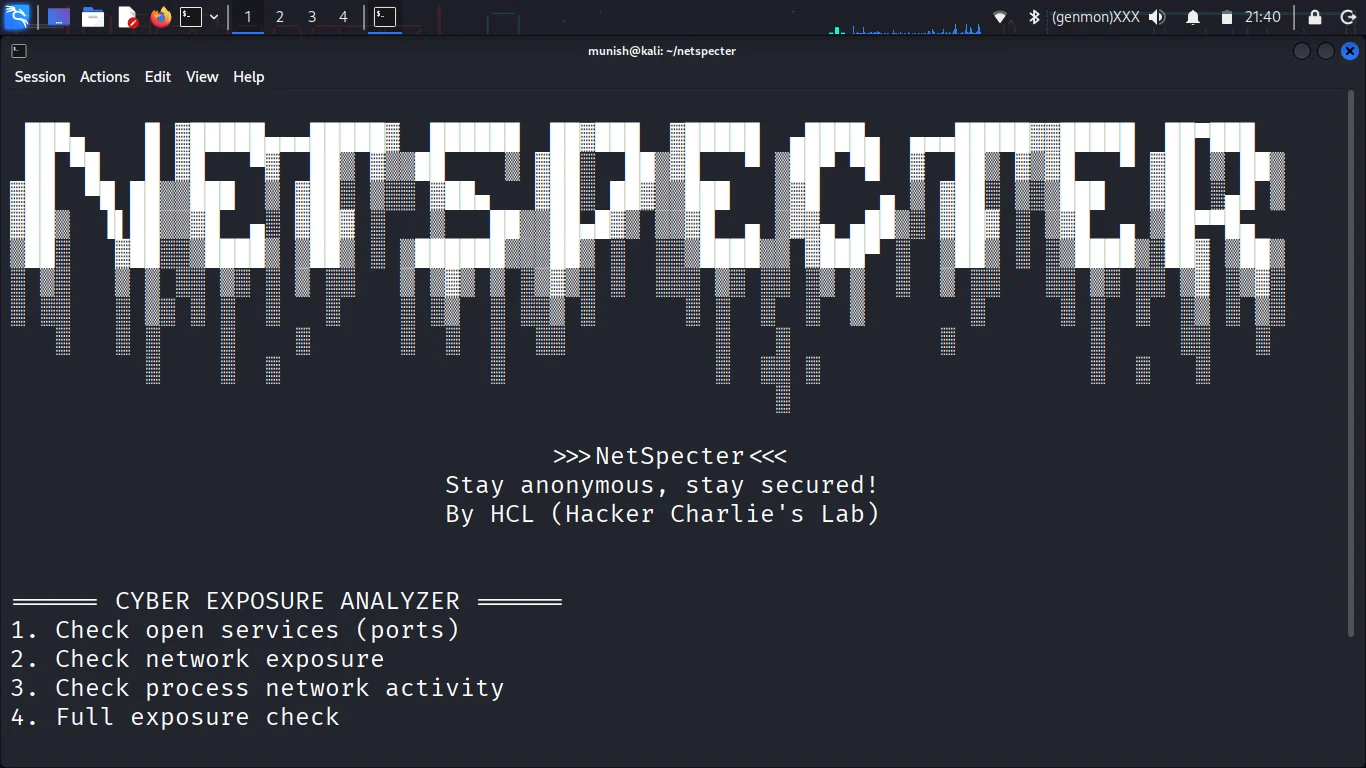 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!

 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 oscerd/cve-2026-91858
Runnable Spring Boot and Quarkus reproducer for CVE-2026-91858, an XXE in Apache Camel camel-fop via a third-party TransformerFactory, with affected…
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
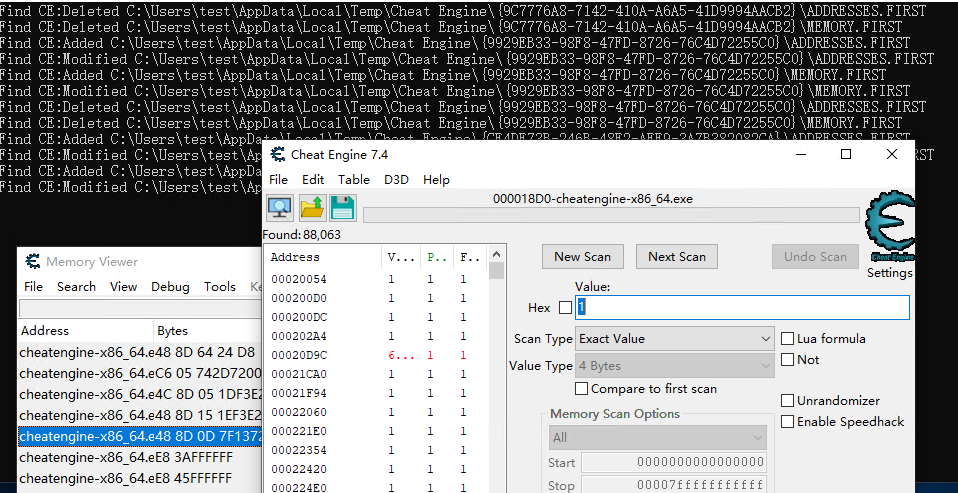 gmh5225/detection-cheatengine
Detects CheatEngine process activity by monitoring file system changes with ReadDirectoryChangesW, providing a lightweight anti-cheat mechanism for…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
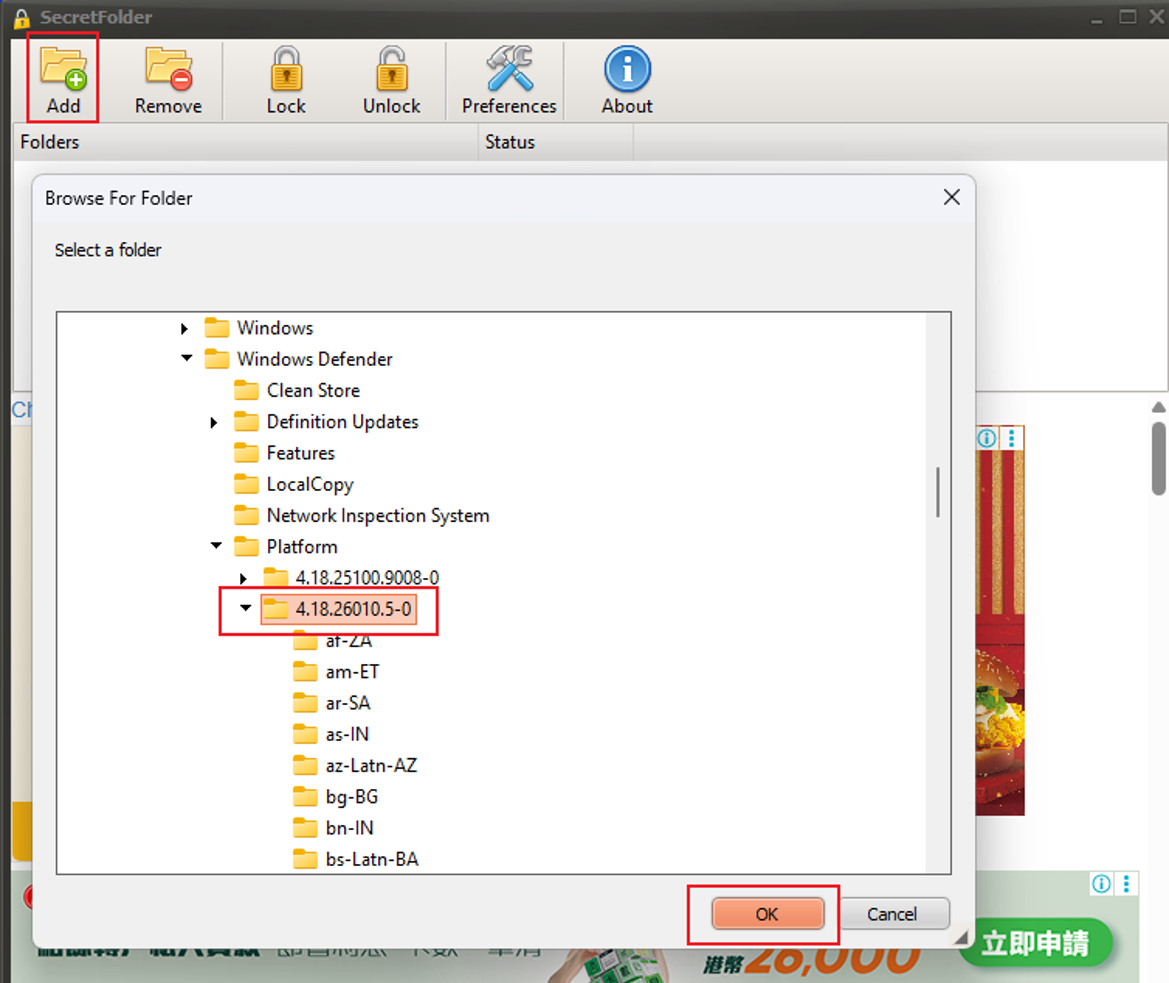 cwjchoi01/cve-2026-36130
Proof-of-concept demonstrating a vulnerability that disables Microsoft Defender (MsMpEng.exe) by locking a folder and rebooting, with screenshots…