
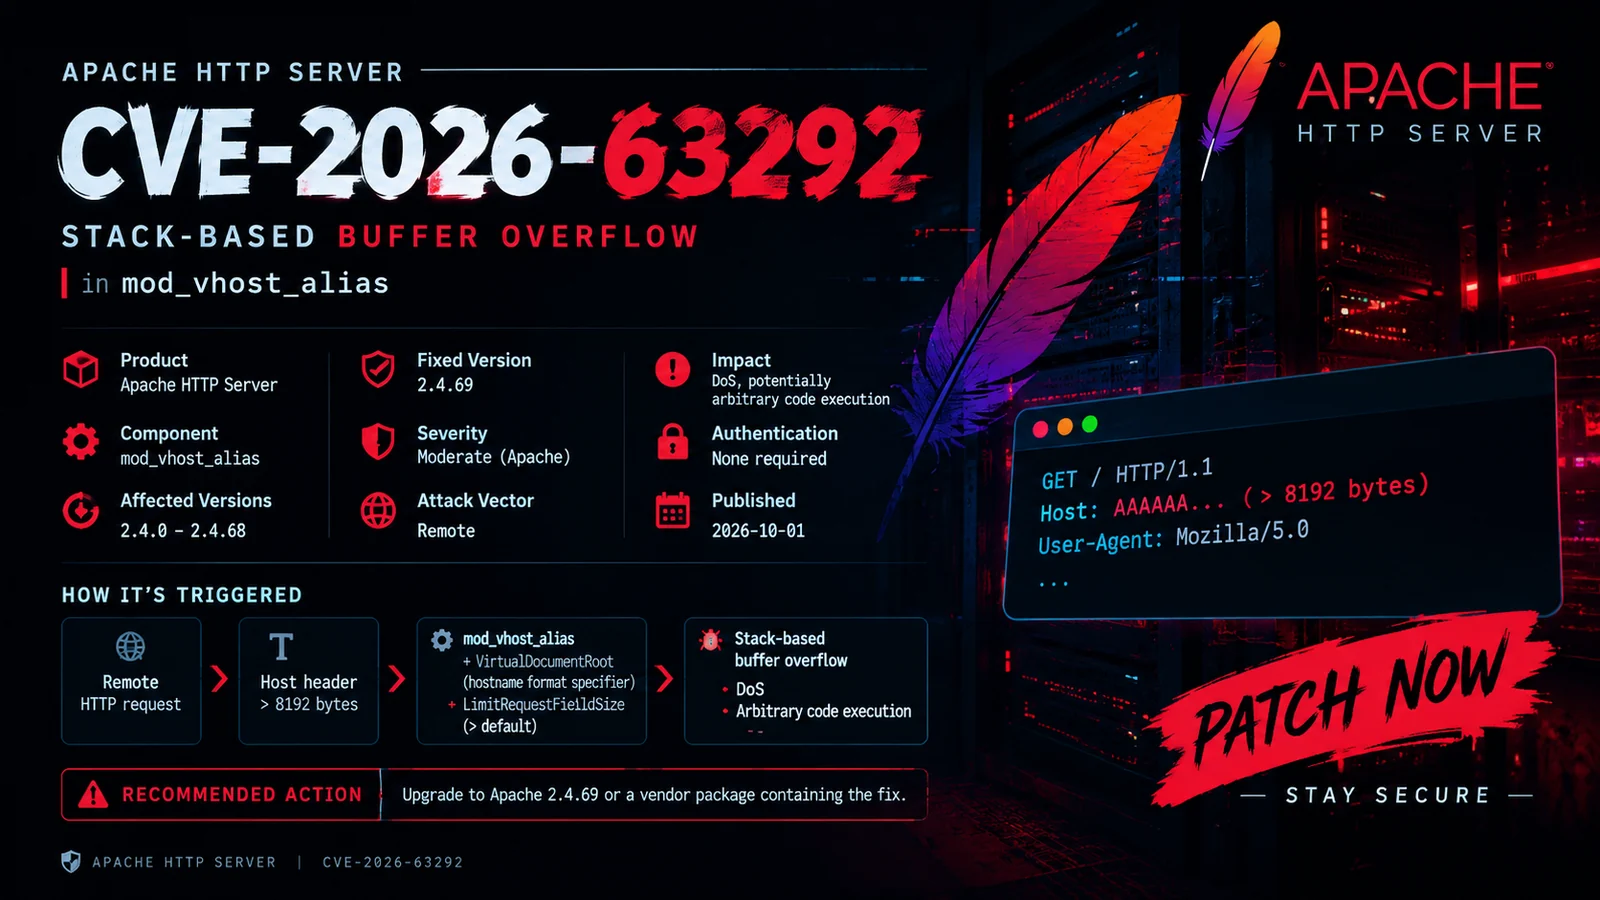
CVE-2026-63292
 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
configuration-auditingdefensive-toolseducation+4
0xblackash/cve-2026-63292Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 horkimhab/cve-2026-10817
Educational security research repository for CVE-2026-10817, providing proof-of-concept material and lab guidance for authorized vulnerability…
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
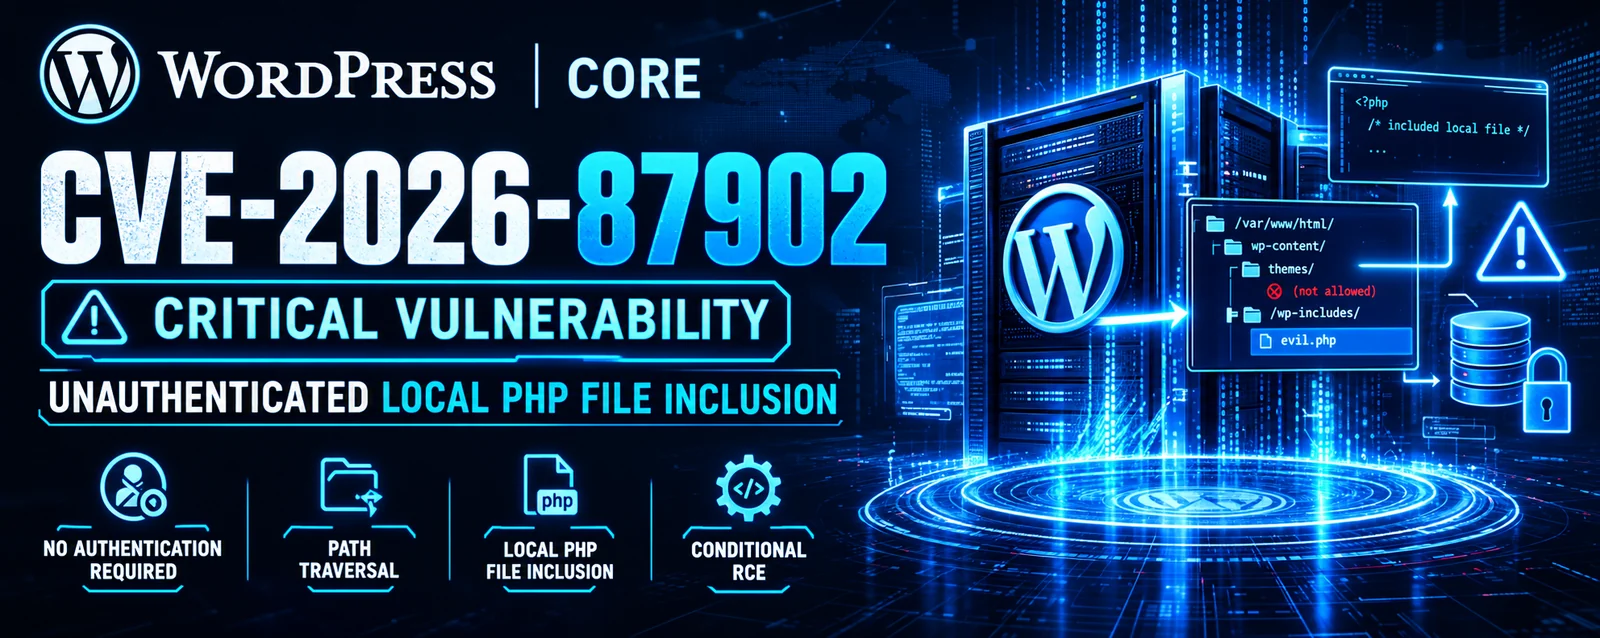 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
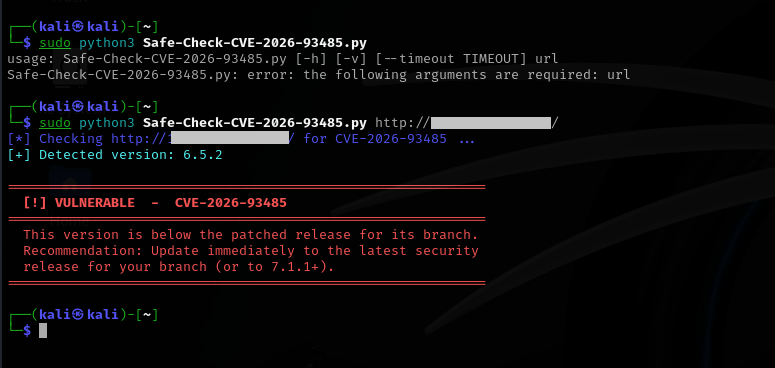 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 sangsenimanwartefak/cve-2026-5118
Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 suominen/cve-2026-53266
Single-page tracker recording which Linux distributions have shipped fixes for the CVE-2026-53266 netfilter ebtables SNAT ARP-rewrite page-cache…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 fevar54/cve-2026-76461-detection-kit-
Defensive detection kit for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, with Sigma and YARA rules, IOCs, and remediation…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…