php-eol-cve-2026-109618-109619

Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…

Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…

Repository for PHP2Shell exposure hunting and related analysis

Read-only PHP2Shell package checker for Debian 12/13 (CVE-2026-109618, CVE-2026-109619).

Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…

Runnable Spring Boot and Quarkus reproducer for CVE-2026-85300, demonstrating camel-pqc writing private keys with permissive umask-derived file…

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.

Tool for fetching/refreshing DNS Root Zone trust anchors

Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go

PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…

Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081

Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…

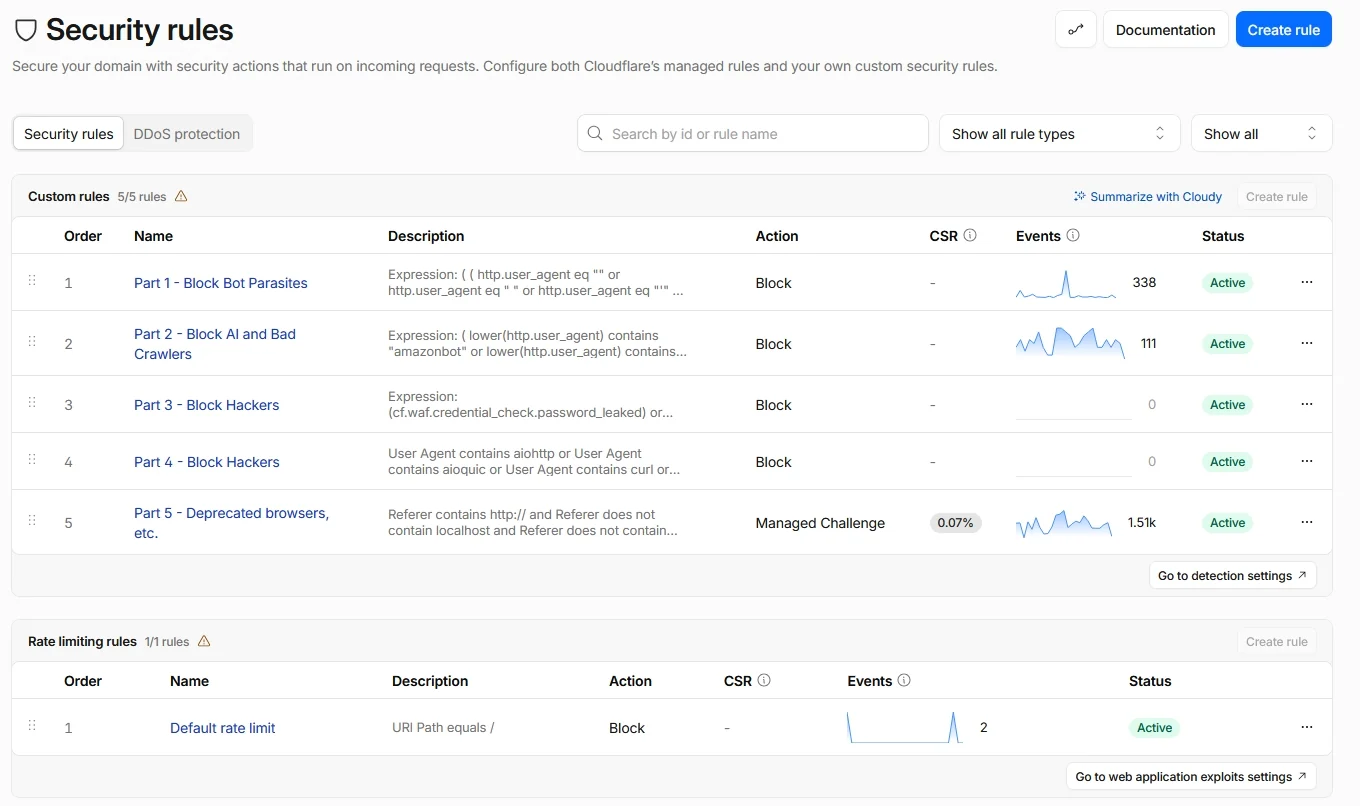
Cloudflare Free Plan security rules (Zero Trust approach) for small websites

Defensive Linux firewall toolkit combining IPTables rules and kernel configuration to protect hosts and servers against DoS, DDoS, and network…

Harden chromium (somewhat) for privacy and security (and performance)

Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…

Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…

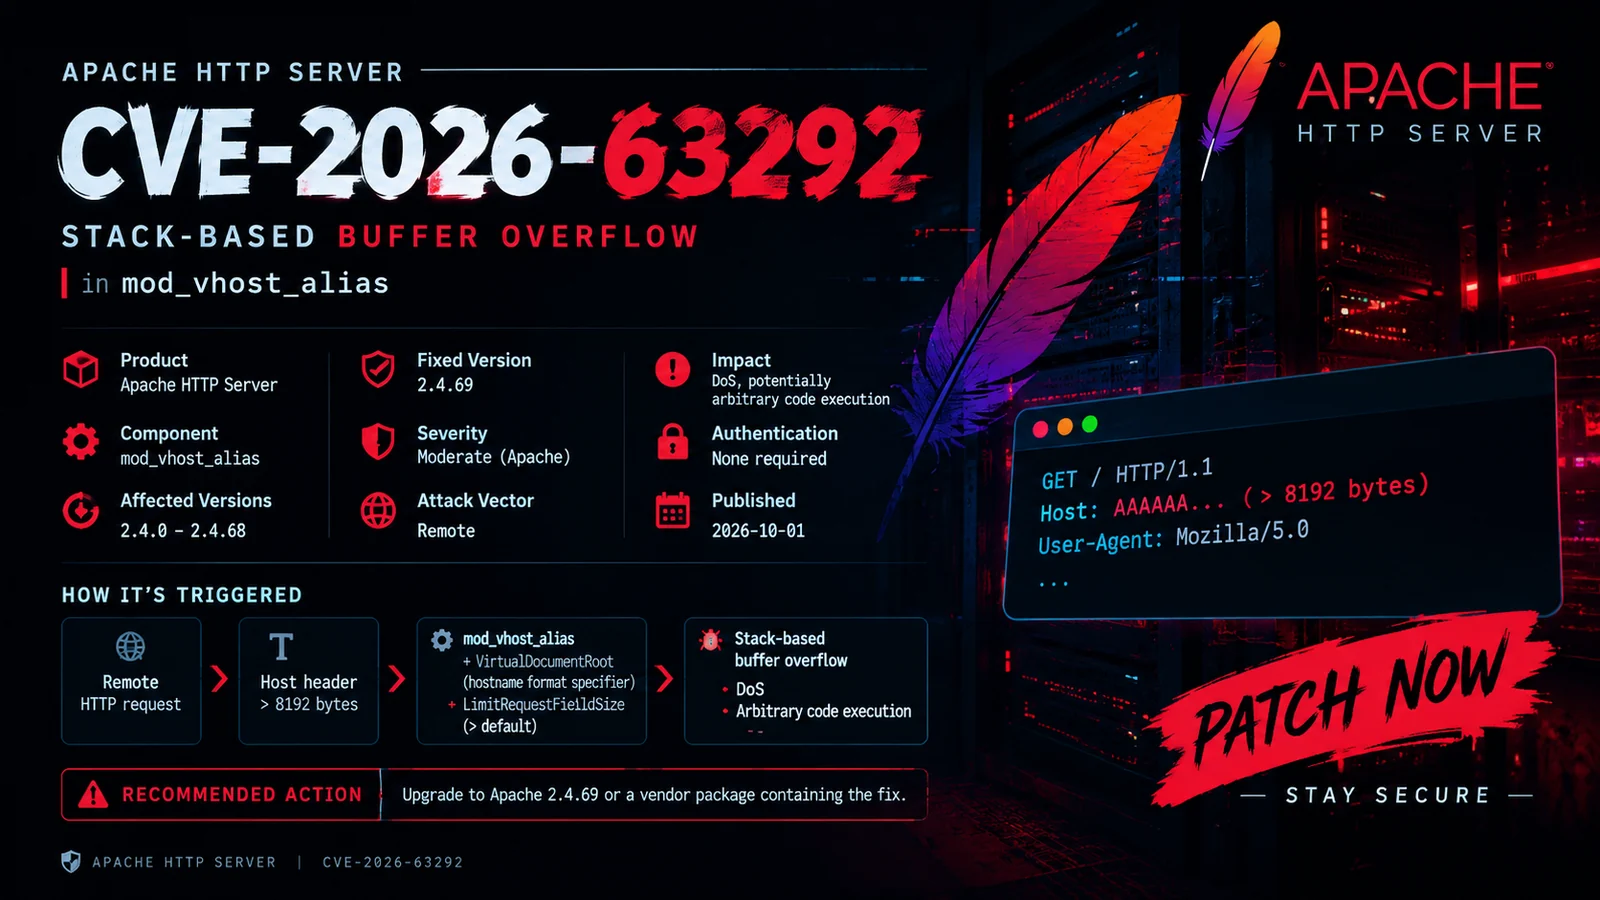
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…

Engagement Manager is a web application for tracking offensive security engagements. It features a modern UI, built with Next.js, Prisma, and…