

Barzakh
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
defensive-toolsembedded-systems-securityfirmware-analysis+6
yasindce1998/barzakhRing -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.
 foxboron/attezt
An open-source TPM device-attest-01 CA server
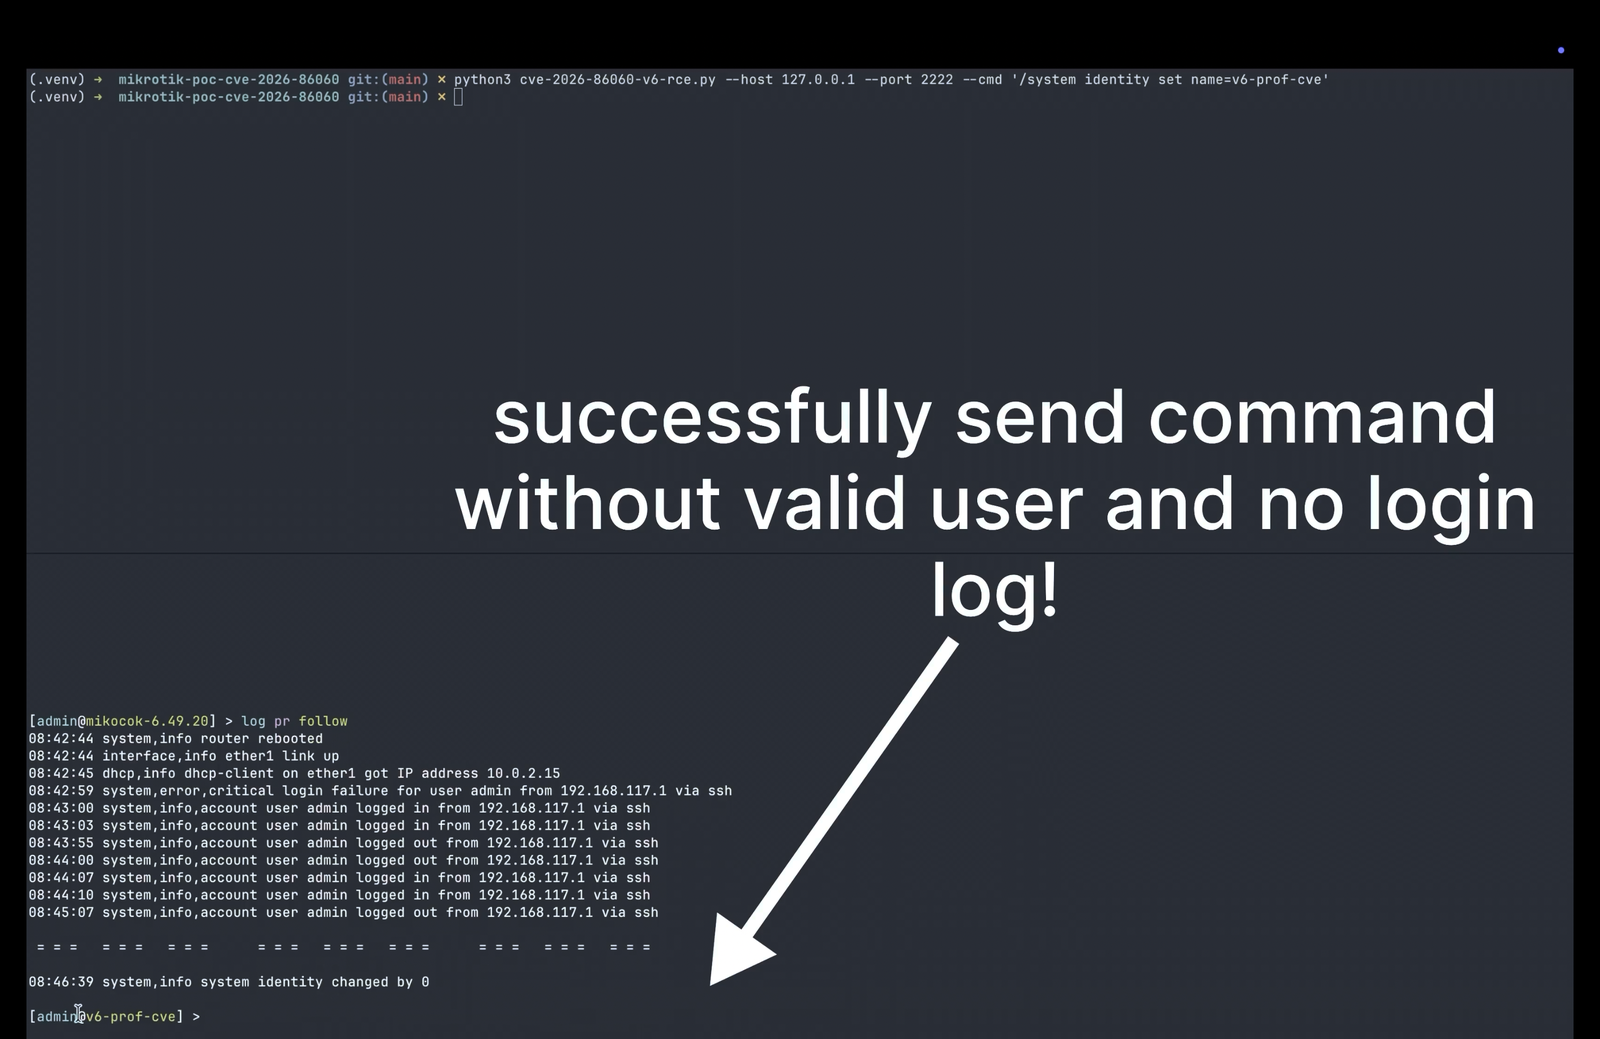 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
 gmh5225/anti_suspend
Protect process by shellcode
 intel/intel-linux-processor-microcode-data-files
Official Intel microcode data files for updating processor firmware to mitigate security vulnerabilities and address functional issues on Linux…
 at0m-b0mb/specter-flipperzero
Specter — passive 13.56 MHz NFC reader/skimmer bug-sweep for Flipper Zero. Counter-surveillance EMF meter using the onboard NFC chip. No extra…
 badrrx/wifi-spiderweb
An active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
 mlsebrell/amthoneypot
Honeypot for Intel's AMT Firmware Vulnerability CVE-2017-5689
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
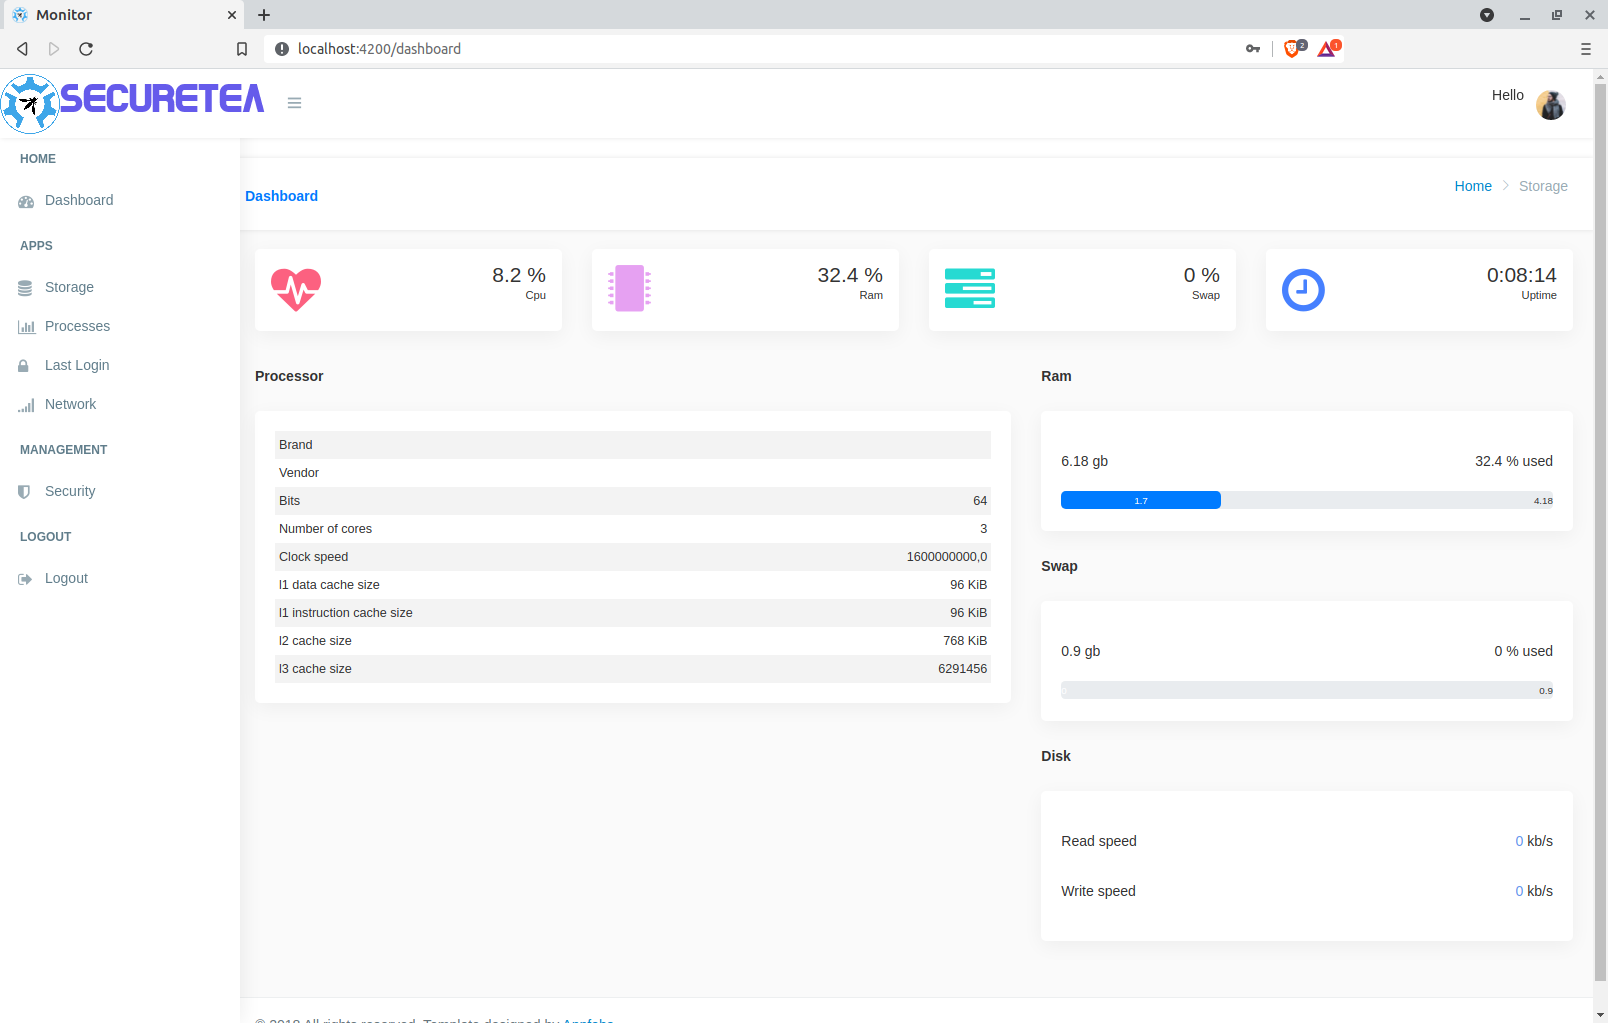 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)