


 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 specterops/bloodhound
Six Degrees of Domain Admin
 cilium/tetragon
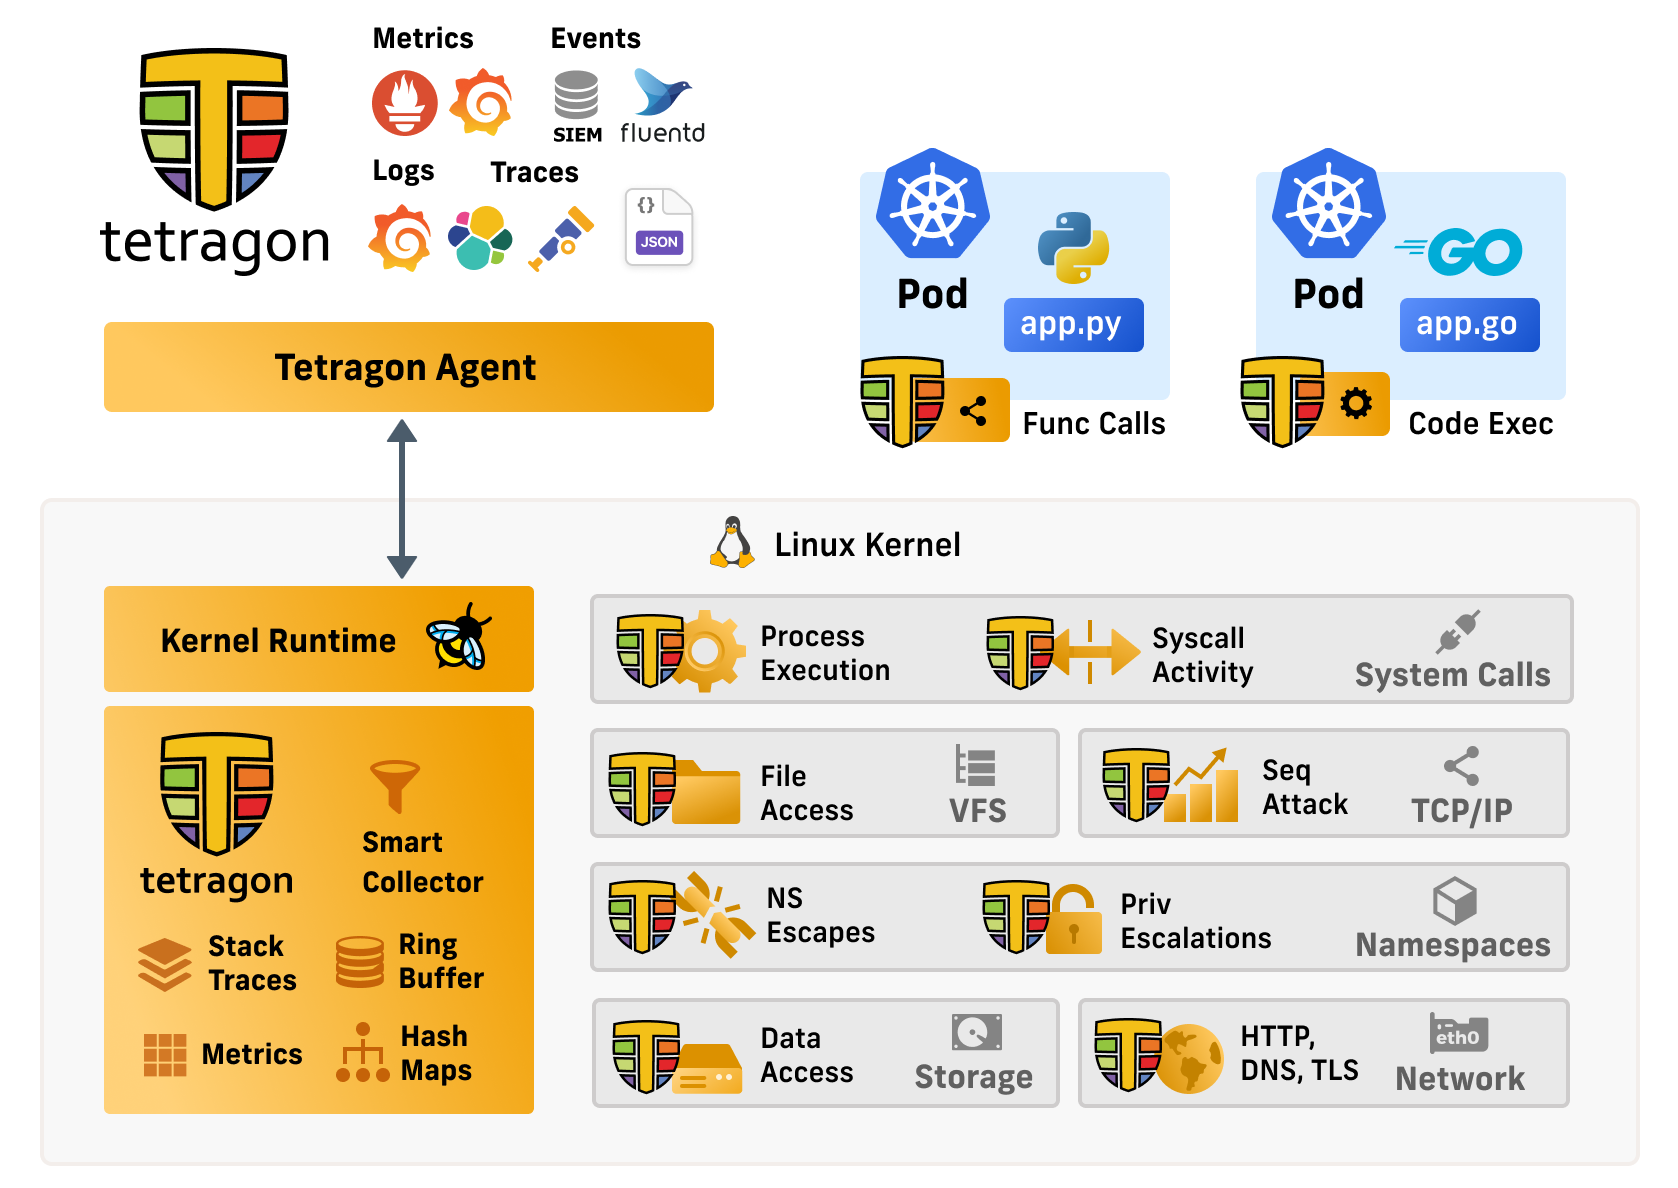
eBPF-based Security Observability and Runtime Enforcement
 suprhackersteve/crescendo
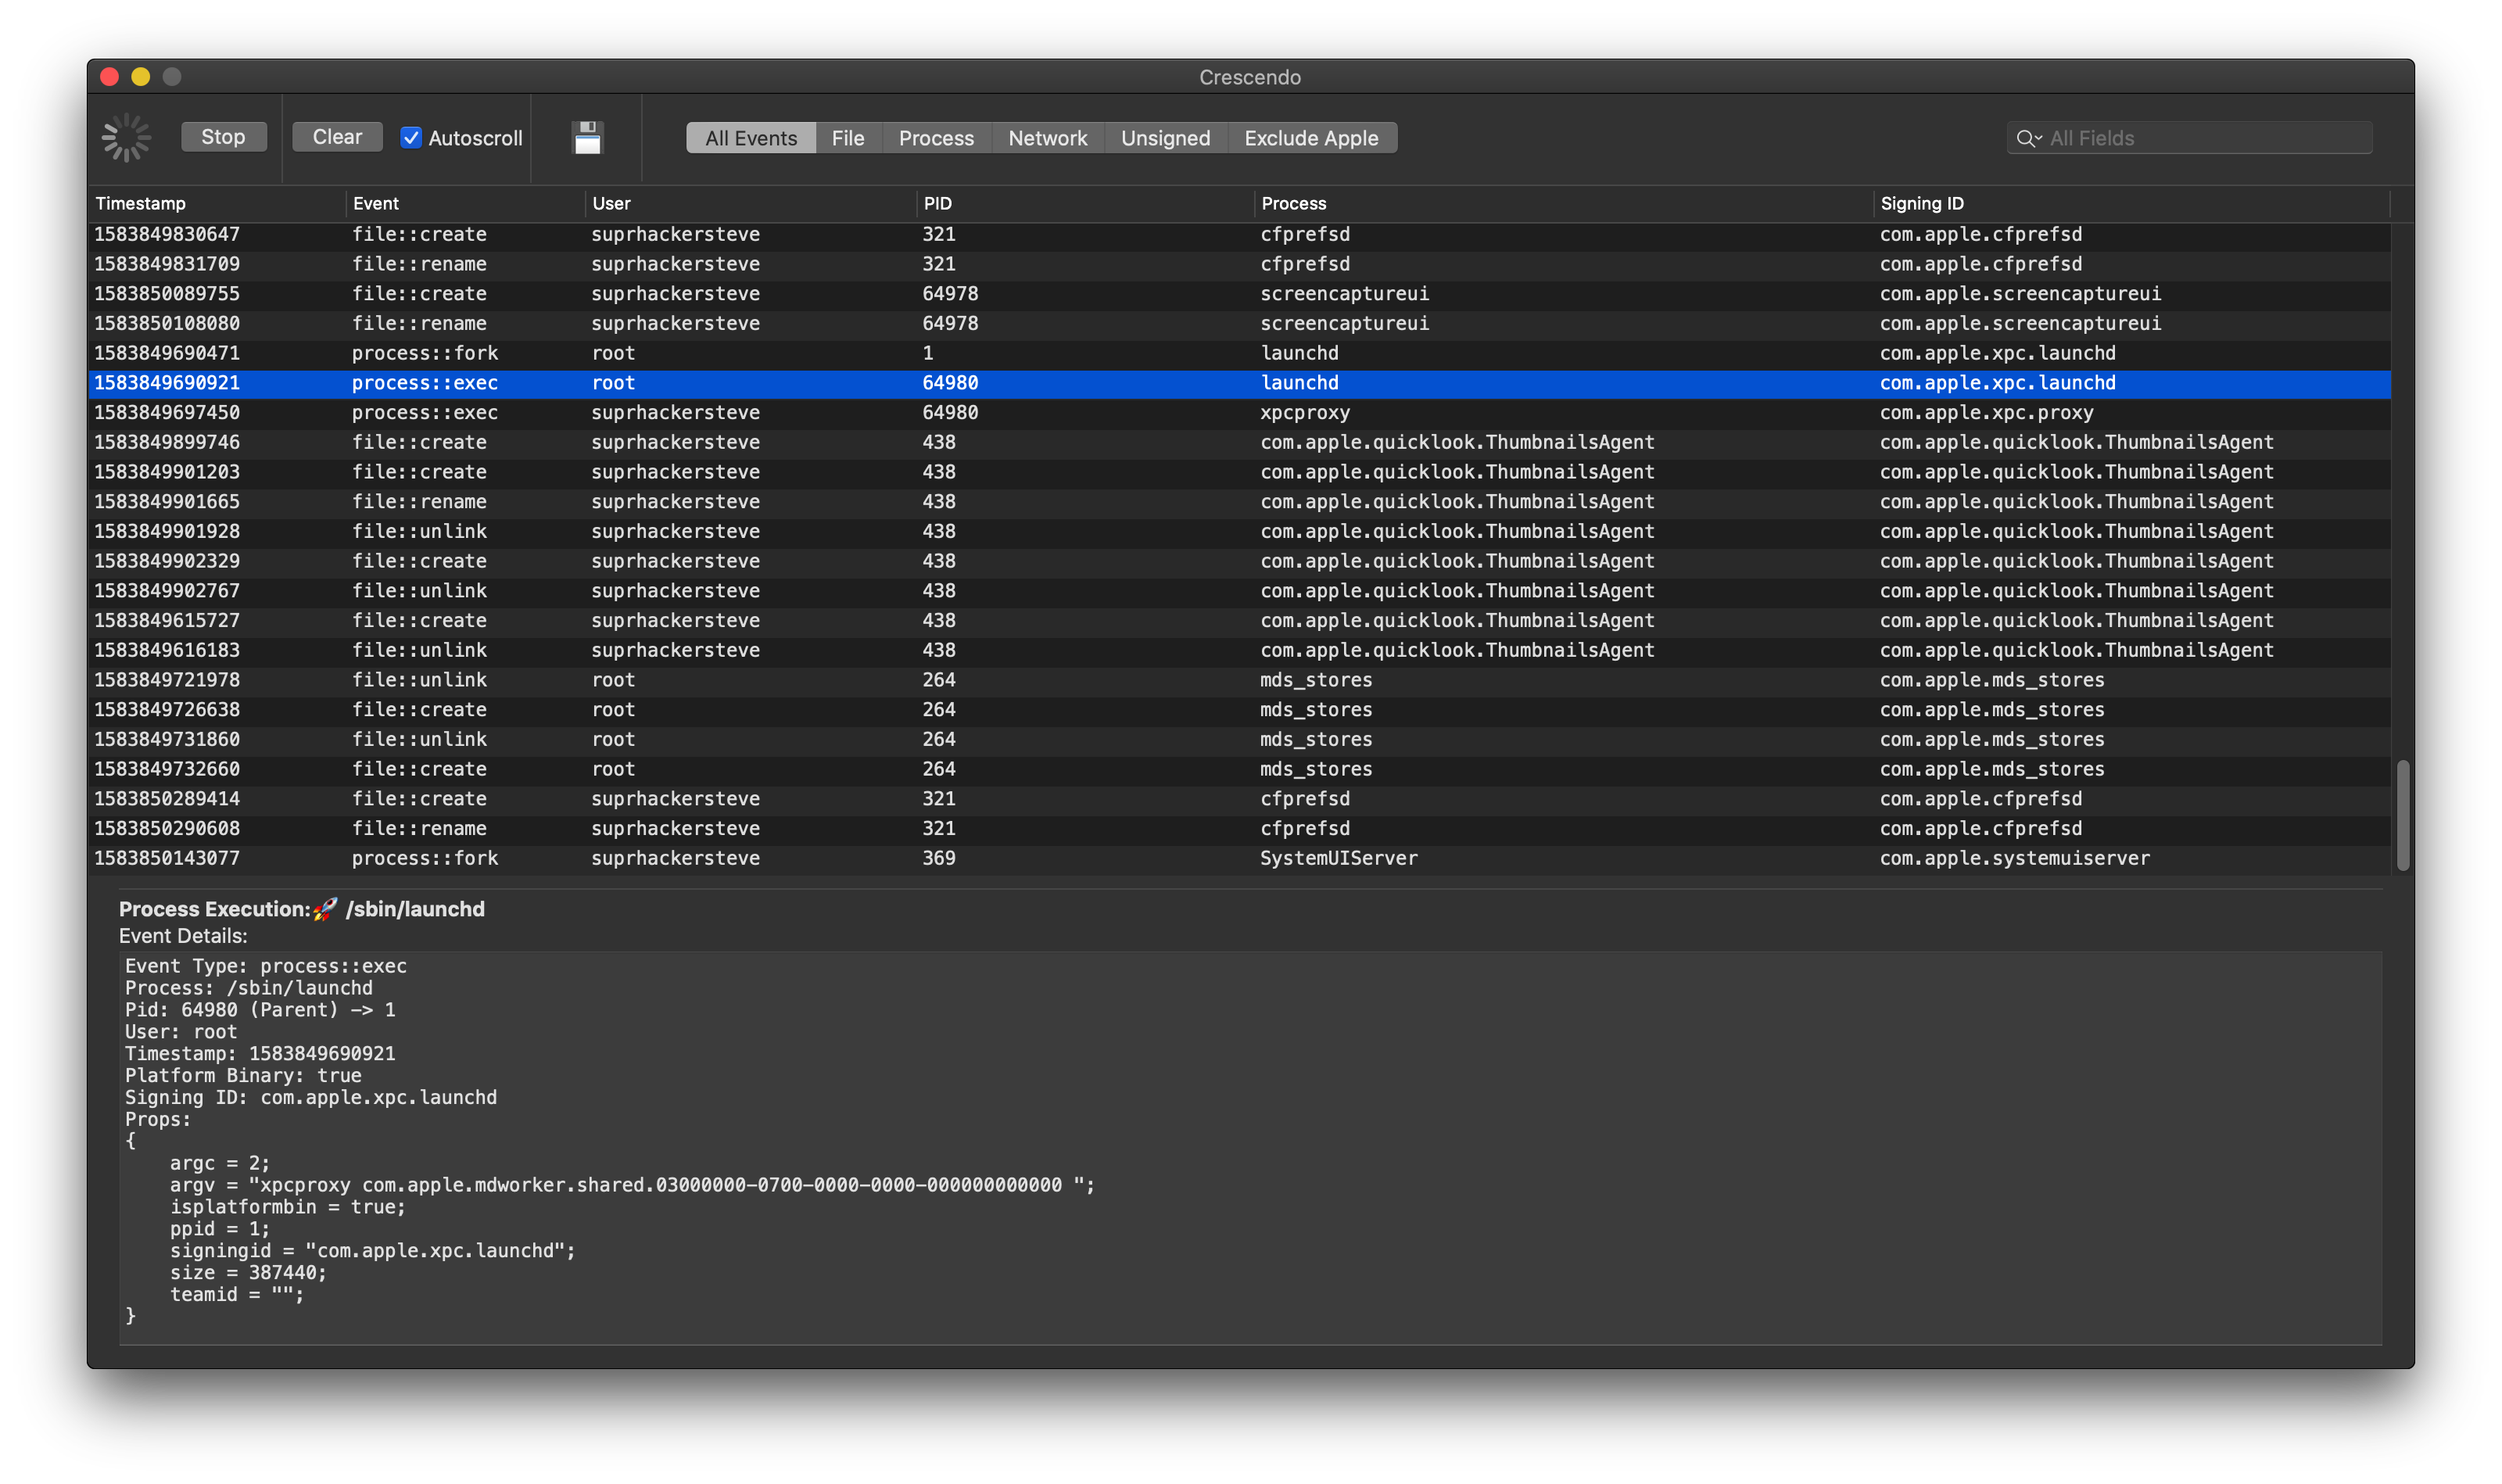
Crescendo is a swift based, real time event viewer for macOS. It utilizes Apple's Endpoint Security Framework.
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…

 kavryxdev-group/enterprise-abac-gateway
Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers