
 kavryxdev-group/enterprise-abac-gateway
Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.



High-performance, zero-trust reverse proxy and authorization gateway built in Go with an embedded Open Policy Agent (OPA) engine, sub-5ms decision latency, real-time distributed token revocation via Redis Pub/Sub, and cryptographic tamper-evident audit logging.
Modern cloud-native and multi-tenant platforms require authorization paradigms far more granular than static Role-Based Access Control (RBAC). In high-assurance environments, authorization must dynamically synthesize who the requester is (Subject), what action they seek to perform (Action), what data classification applies (Resource), and real-time operational context (Environment).
The Enterprise Fine-Grained ABAC Gateway acts as a centralized Policy Enforcement Point (PEP) and Policy Decision Point (PDP) fronting backend microservices. Engineered to comply with NIST SP 800-162 (ABAC), NIST SP 800-207 (Zero-Trust Architecture), and RFC 7519 (JSON Web Tokens), it eliminates authorization latency by compiling Rego policies directly into the Go process memory space, avoiding out-of-process network hops while maintaining distributed consistency across cluster instances.
ALLOW / DENY) is recorded in an append-only SHA-256 hash chain ($\text{Hash}n = \text{SHA-256}(\text{Hash}{n-1} + \text{Snapshot}_n)$) persisted asynchronously to PostgreSQL for SOC 2 Type II and ISO 27001 audit trails.The gateway is partitioned into an ultra-low latency Data Plane (HTTP Reverse Proxy & In-Memory PDP), an isolated Control Plane (Admin API for policy and revocation management), and resilient State & Persistence Tiers (Redis 7 & PostgreSQL 16).
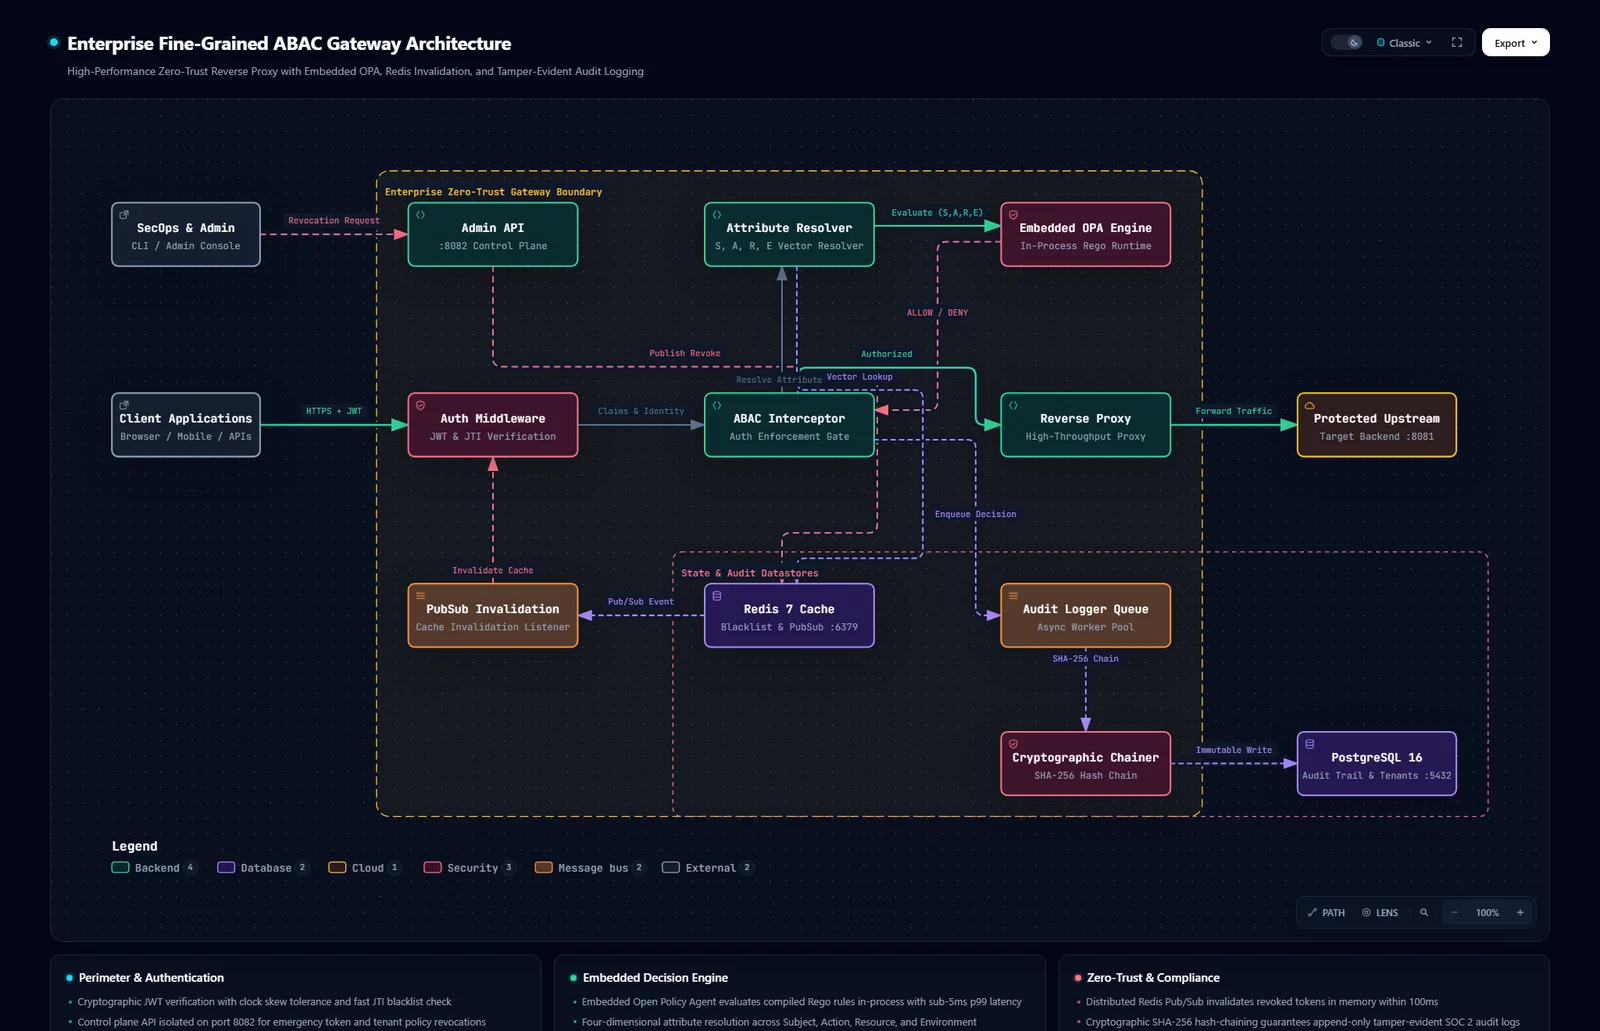
Figure 1: High-level System Architecture diagram generated with Archify.
👉 🔍 Click Here to Open Interactive Archify Diagram (Supports dark/light themes, clickable nodes, and deep component inspection)
graph TD
    subgraph Clients["Perimeter & External Consumers"]
        ClientApp["Client Applications (SPA / Mobile / Microservices)"]
        SecOps["SecOps & Admin Console"]
    end

    subgraph DataPlane["Enterprise Zero-Trust Gateway (:8080)"]
        direction TB
        AuthMid["Auth Middleware (JWT, JTI, Leeway)"]
        PEP["ABAC Interceptor (PEP Gate)"]
        Resolver["Attribute Resolver (S, A, R, E)"]
        OPA["Embedded OPA Engine (Rego Runtime)"]
        Proxy["Reverse Proxy (httputil)"]
        PubSubLis["PubSub Invalidation Listener"]
        AuditLog["Non-Blocking Audit Logger"]
        HashChain["SHA-256 Cryptographic Chainer"]
    end

    subgraph ControlPlane["Control Plane (:8082)"]
        AdminAPI["Admin API (Revocations & Health)"]
    end

    subgraph StateTier["Distributed State & Persistence"]
        Redis["Redis 7 (Vector Cache & Blacklist :6380)"]
        Postgres["PostgreSQL 16 (Ledger & Tenant DB :5433)"]
    end

    subgraph UpstreamTier["Target Services"]
        Upstream["Protected Upstream API (:8081)"]
    end

    ClientApp -->|"HTTPS + Bearer JWT"| AuthMid
    SecOps -->|"Admin Key Auth"| AdminAPI
    AdminAPI -->|"Publish JTI Revocation"| Redis
    Redis -.->|"Pub/Sub Channel (<=100ms)"| PubSubLis
    PubSubLis -->|"Invalidate Local LRU"| AuthMid

    AuthMid -->|"Verified Identity Claims"| PEP
    PEP -->|"Build Evaluation Context"| Resolver
    Resolver -.->|"Query Vectors"| Redis
    Resolver -->|"Vector (S, A, R, E)"| OPA
    OPA -->|"ALLOW / DENY (<5ms SLA)"| PEP

    PEP -->|"Authorized Traffic"| Proxy
    Proxy -->|"Reverse Proxy Forward"| Upstream
    PEP -.->|"Async Decision Record"| AuditLog
    AuditLog -->|"Hash Chain Generation"| HashChain
    HashChain -->|"Append-Only Immutable Write"| Postgres

