

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 hugsy/cfb
ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for…
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
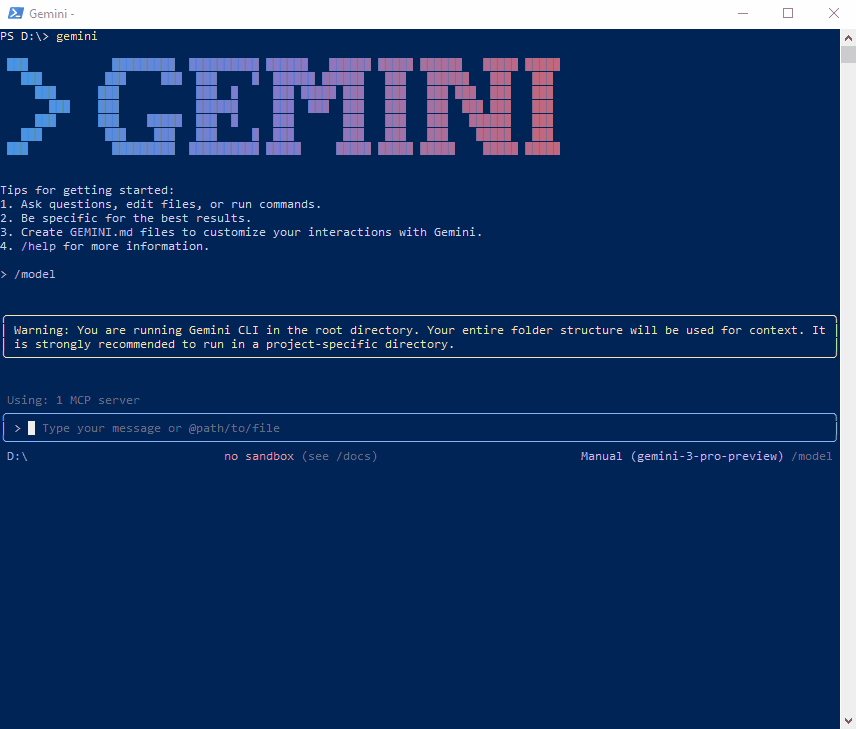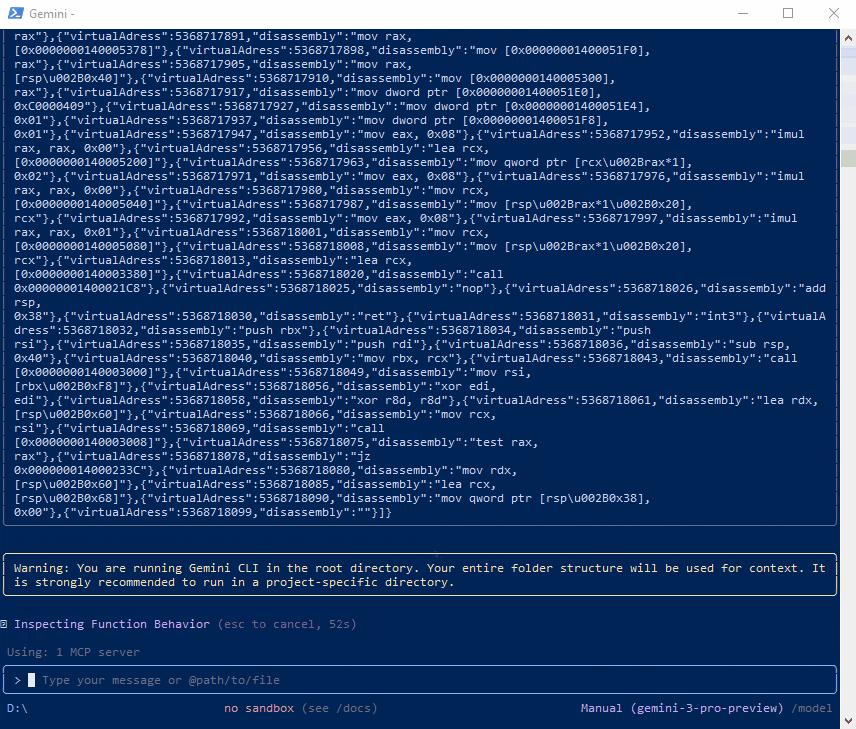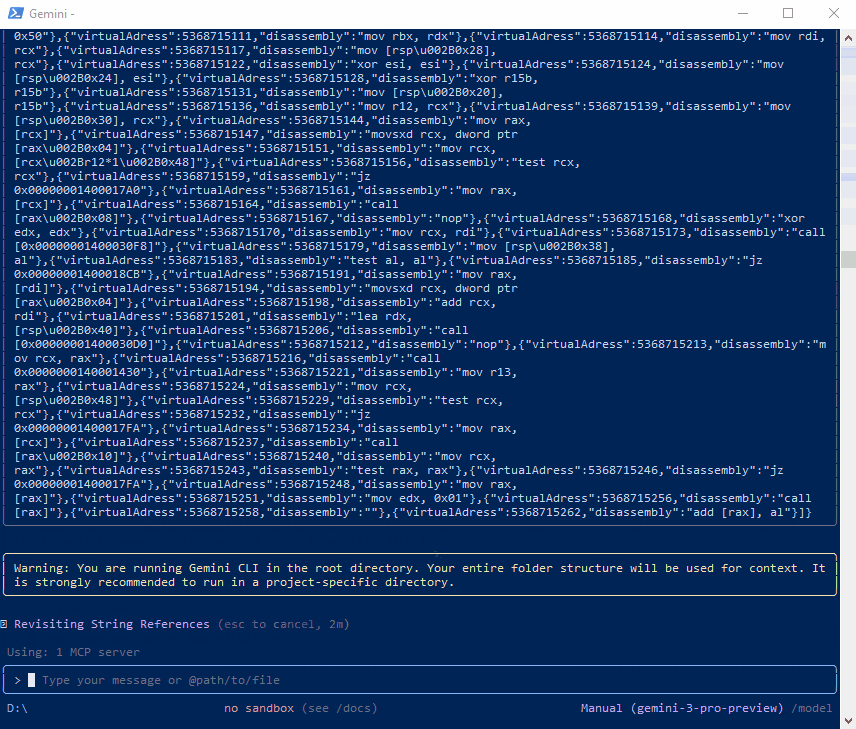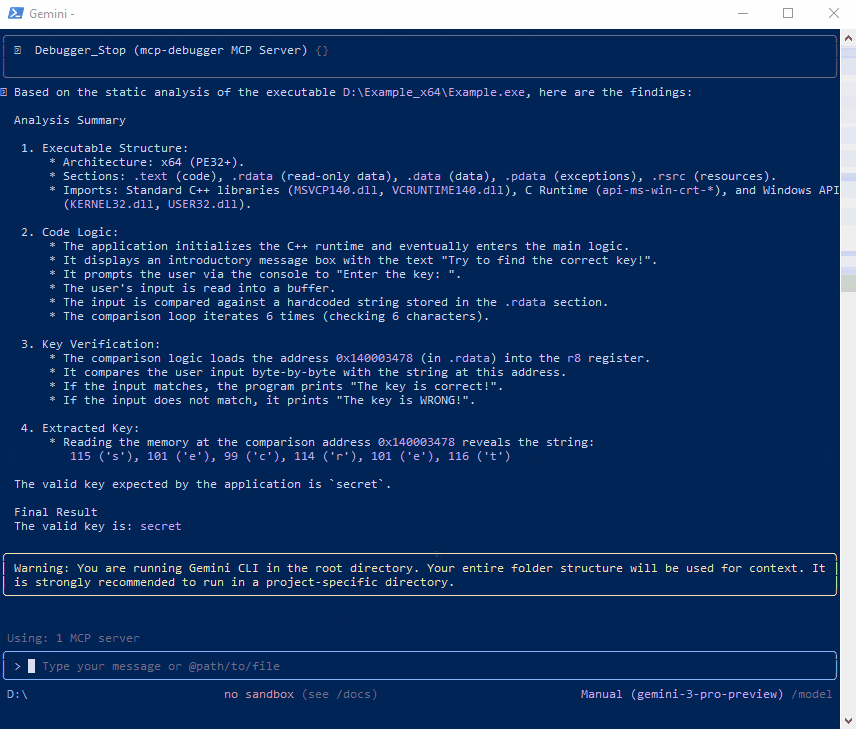 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
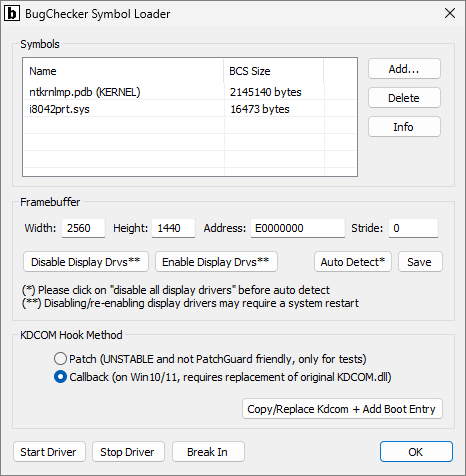 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 rad9800/hwbp4mw
Hardware breakpoint hooking engine for Windows that uses debug registers to hook functions, bypass ETW/AMSI, and evade user-land EDR monitoring.
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
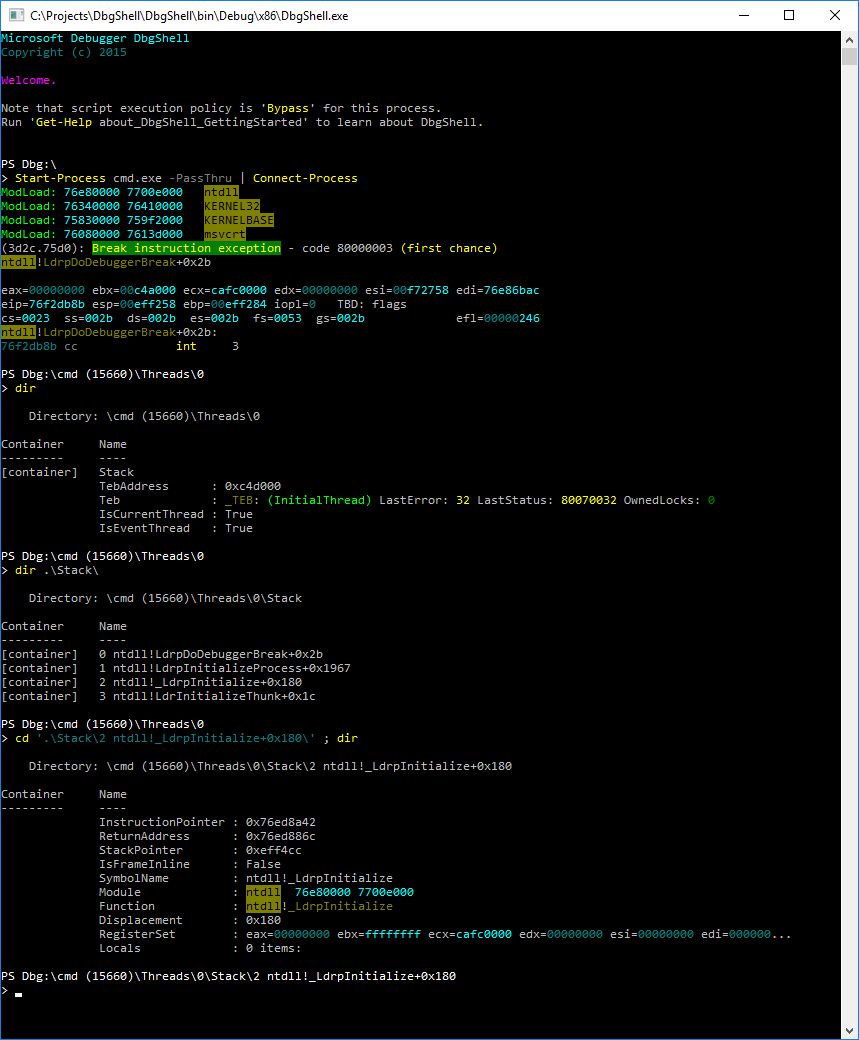 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
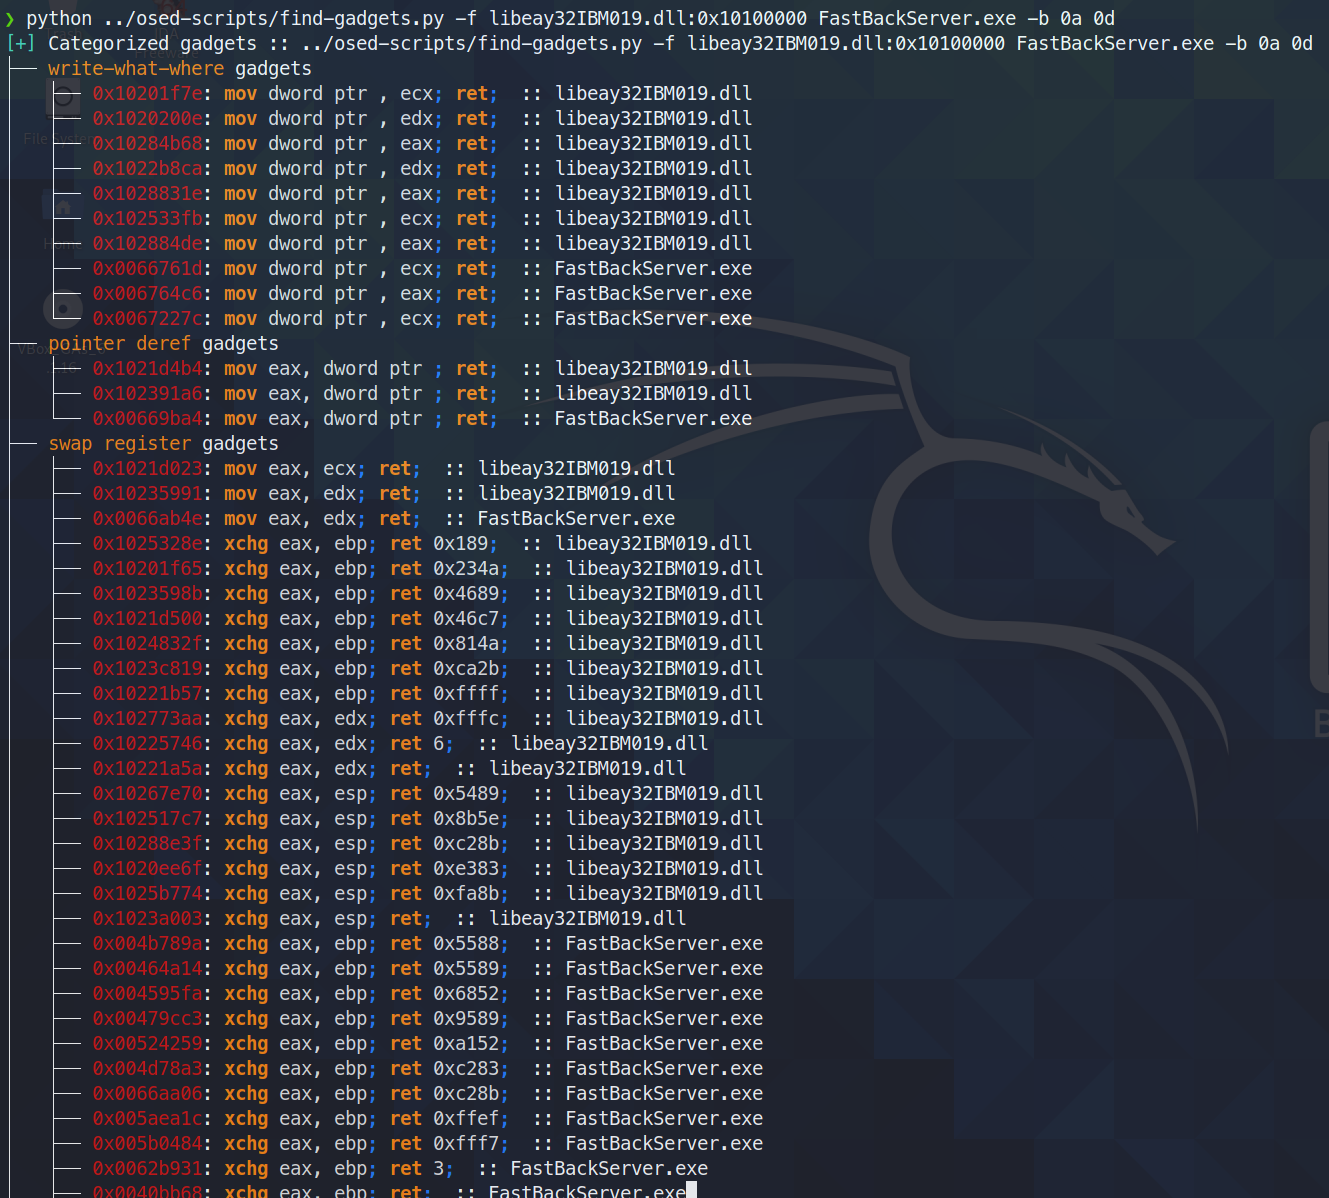 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
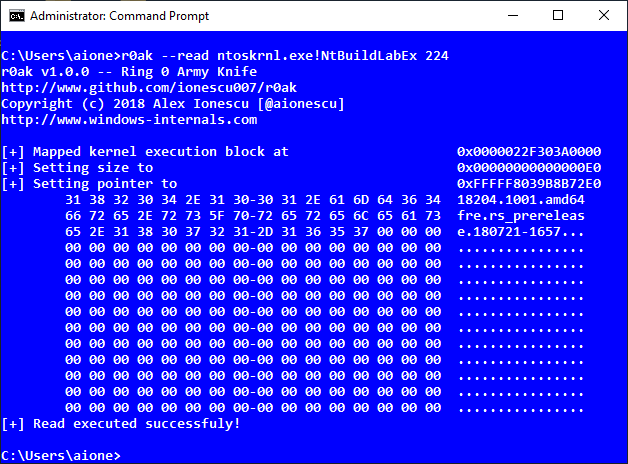 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…