
Dwarf
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
android-securitybinary-analysisdebuggers+4
igio90/dwarfFull featured multi arch/os debugger built on top of PyQt5 and frida
 mfthomps/resim
Reverse engineering software using a full system simulator
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 binaryhardening/cfgrip
Disassembles PE/ELF x86/x64 binaries, resolves indirect branches via GOT, jump tables, and register tracing, and exports the full control flow graph…
 jelasin/cve-2026-42533
Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
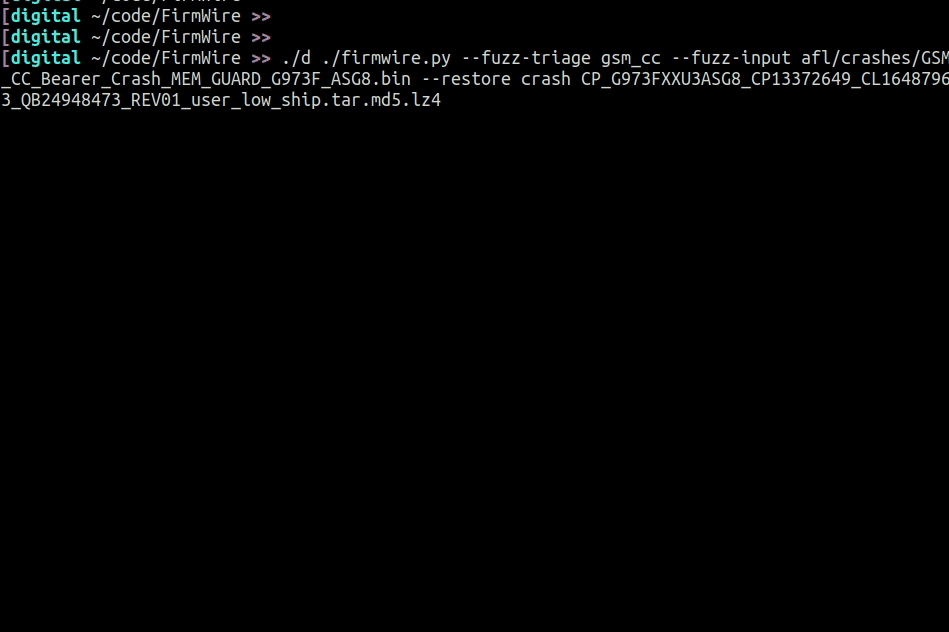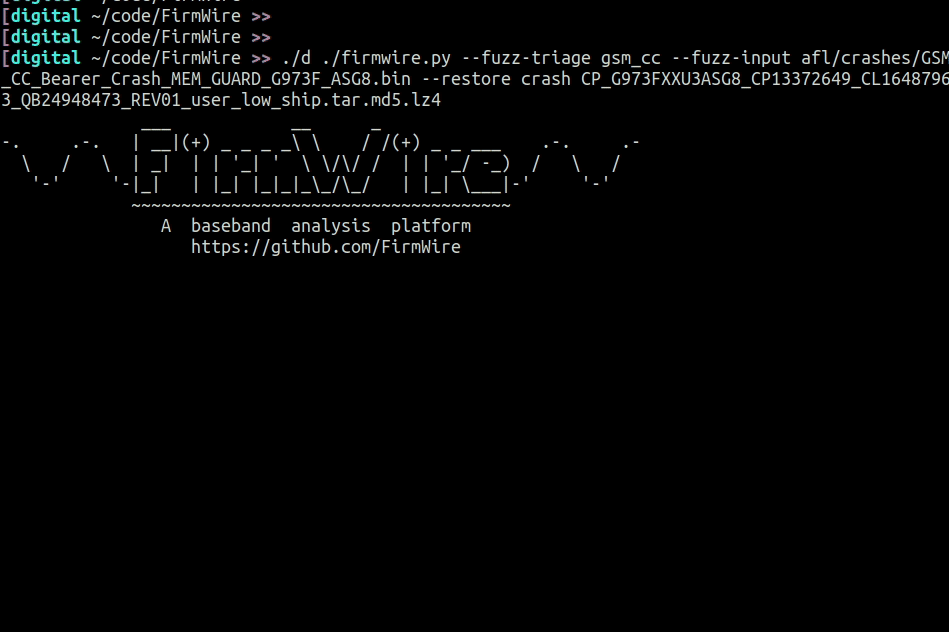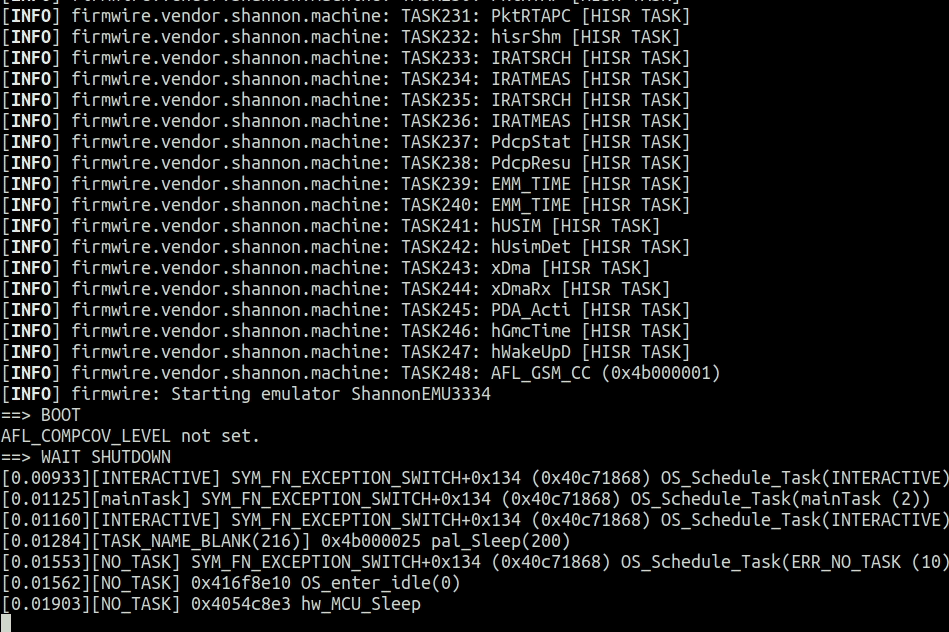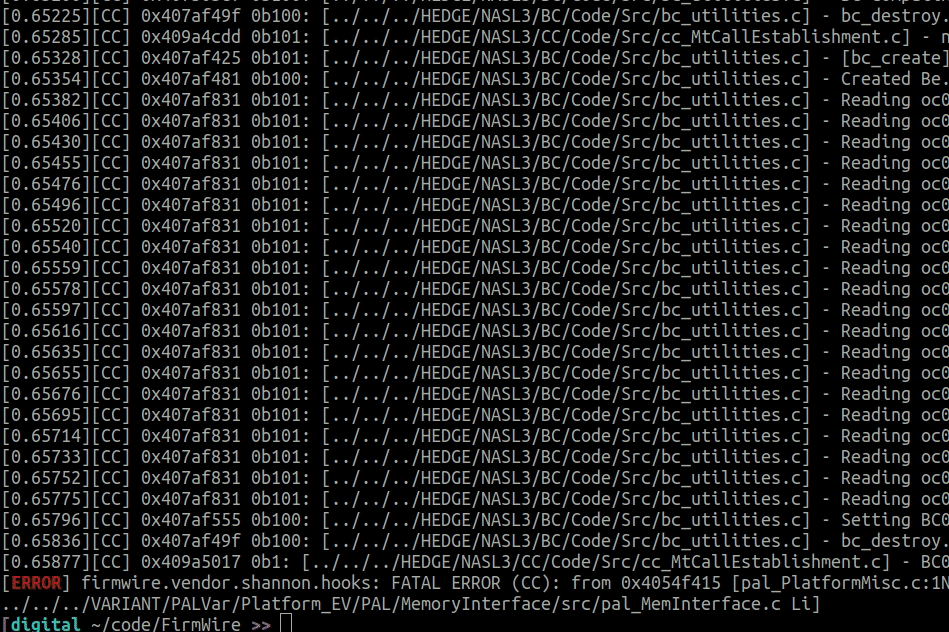 firmwire/firmwire
FirmWire is a full-system baseband firmware emulation platform for fuzzing, debugging, and root-cause analysis of smartphone baseband firmwares
 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.