

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.1k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 amossys/memitm
Tool to make in memory man in the middle
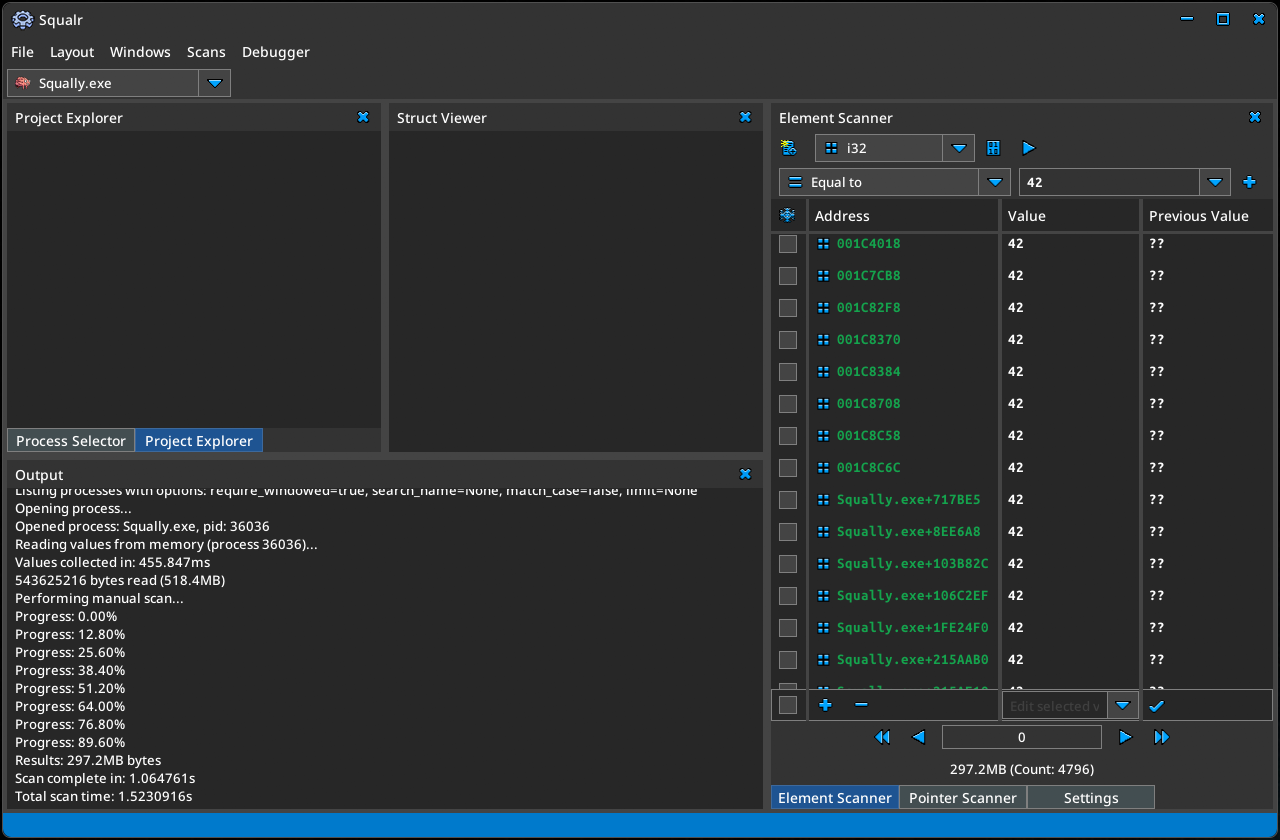 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
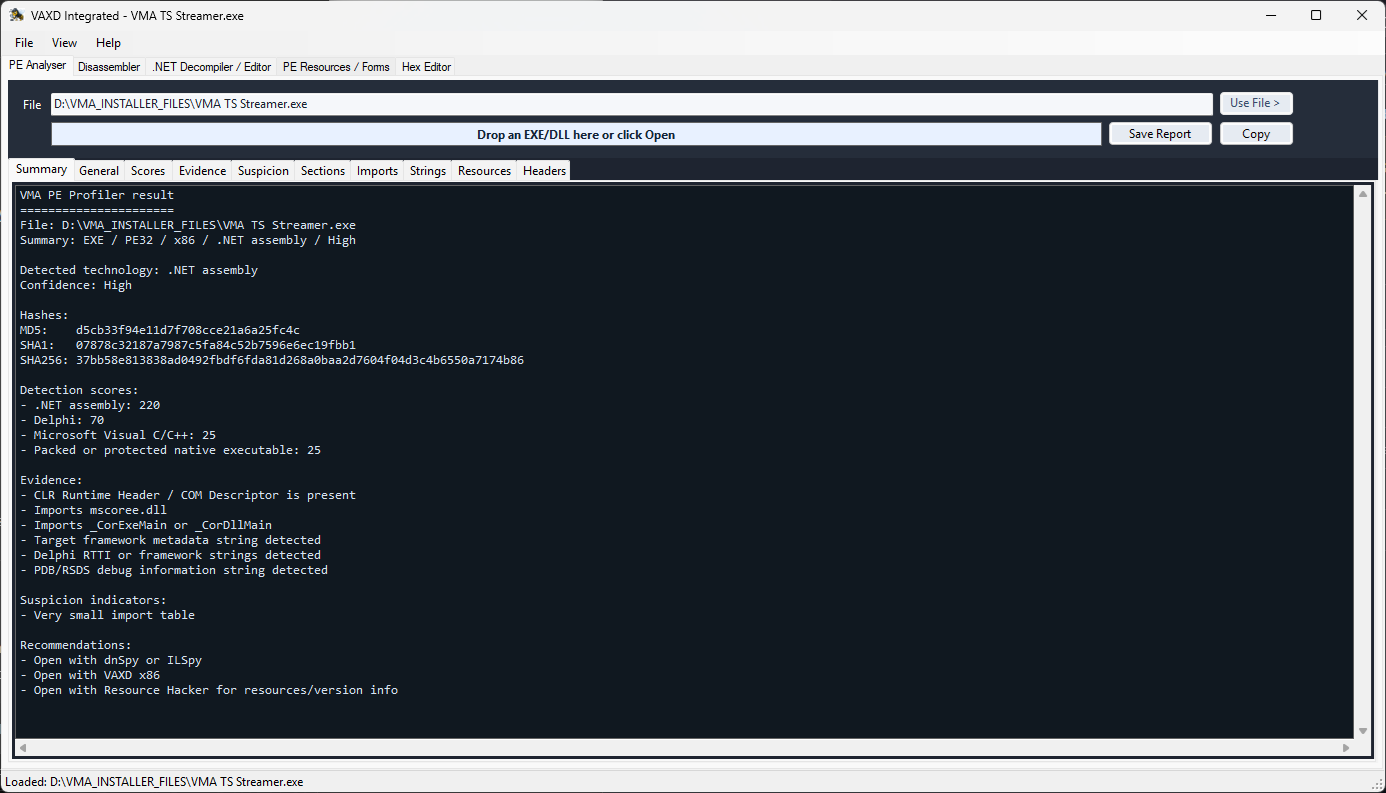 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
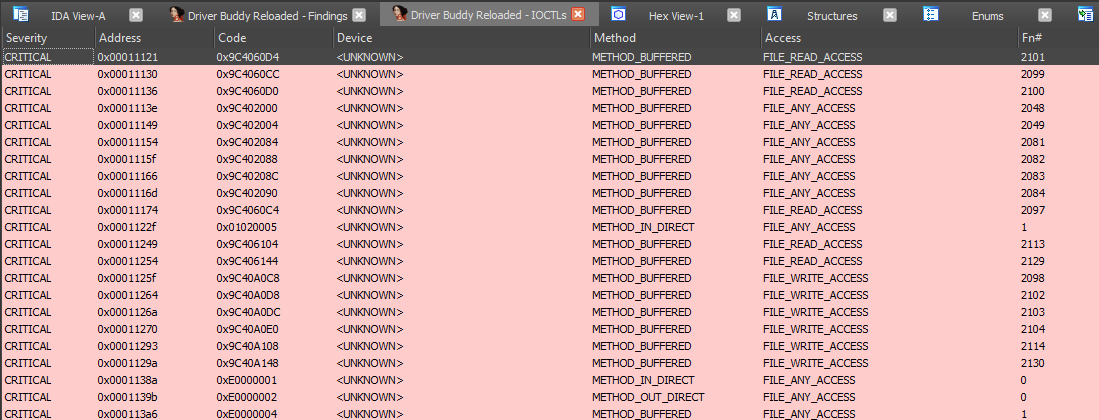 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 cocoadebug/cocoadebug
iOS Debugging Tool 🚀
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…