

PowerShellArsenal
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
binary-analysisdebuggersdynamic-analysis-sandboxing+6
902
mattifestation/powershellarsenalA PowerShell Module Dedicated to Reverse Engineering
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
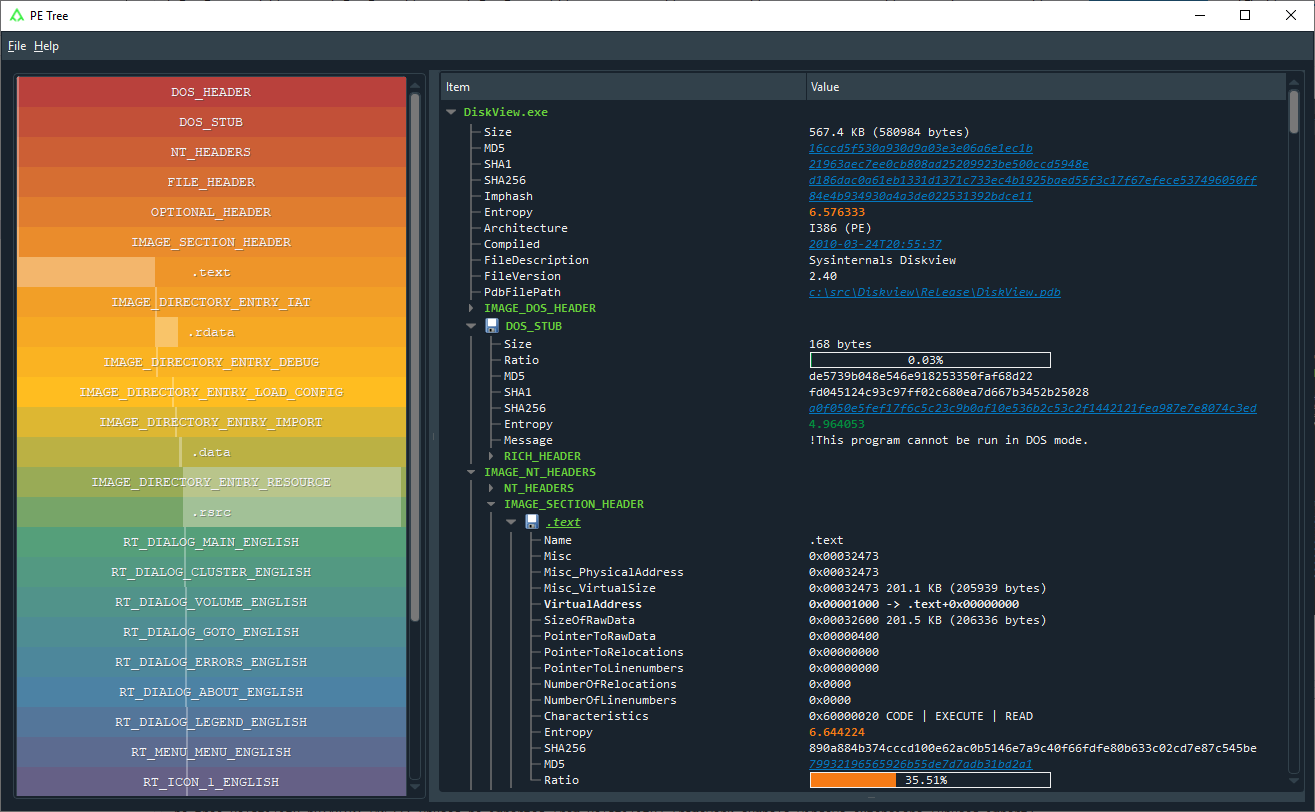 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
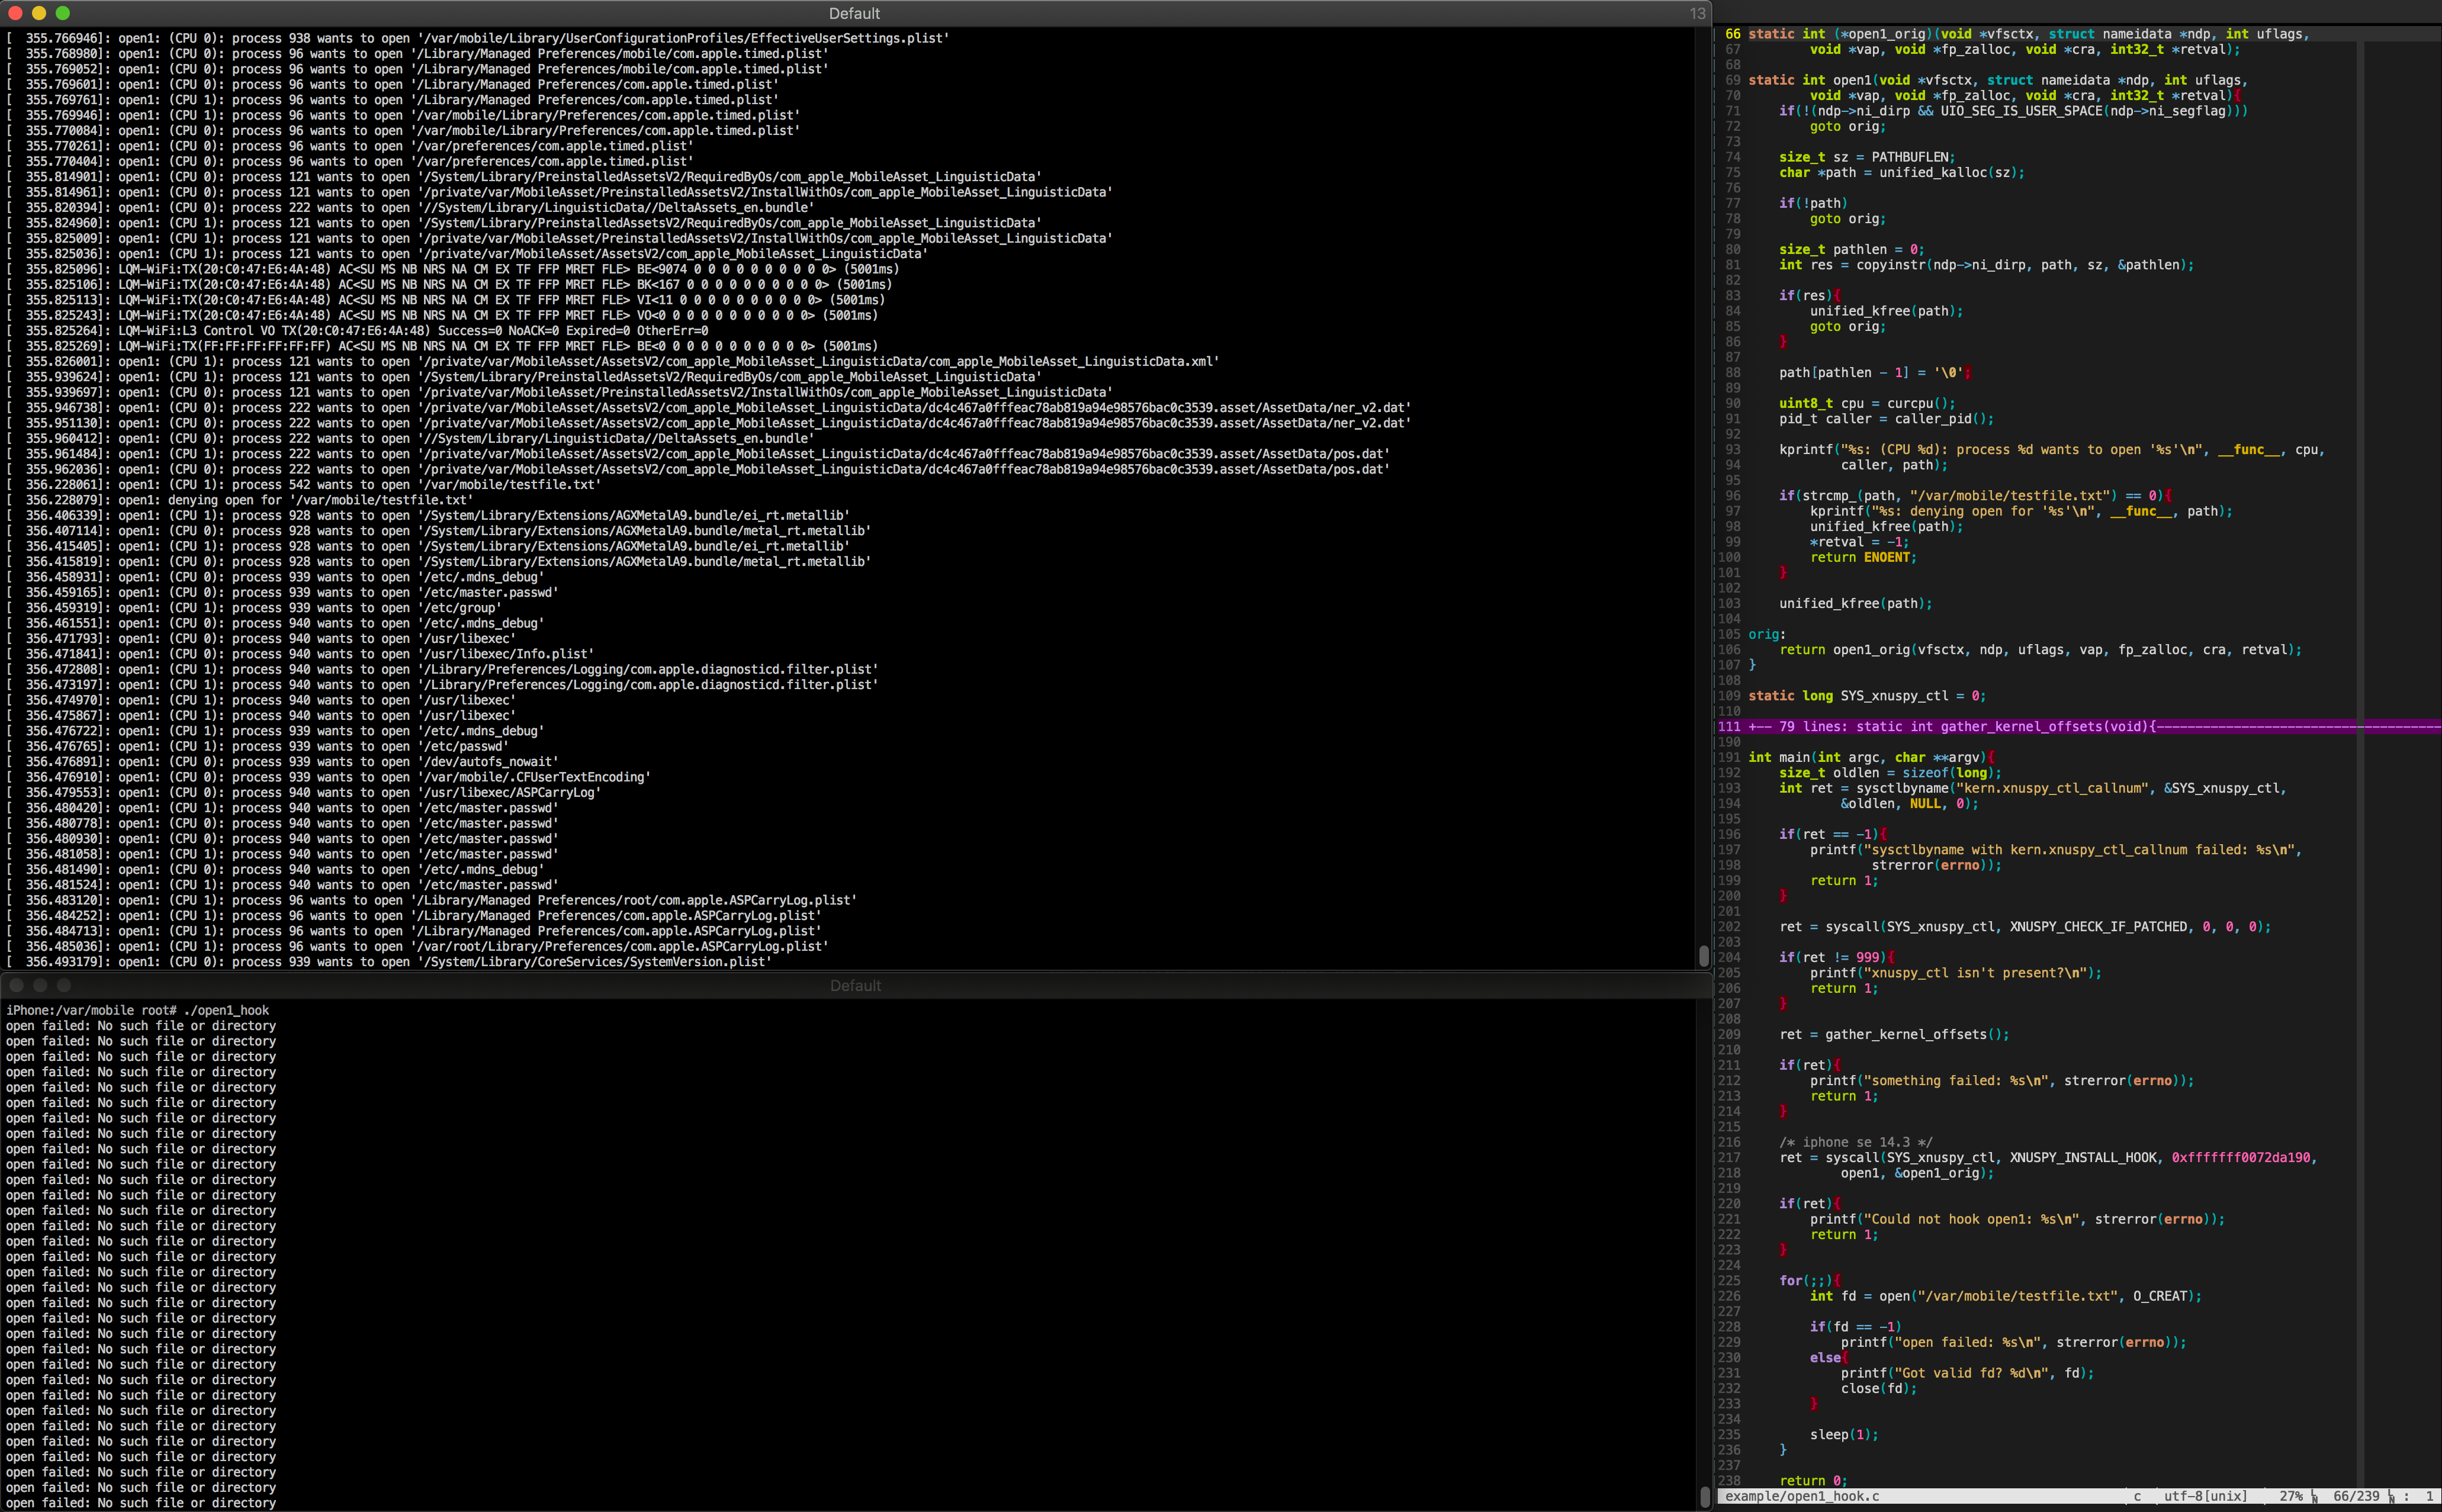 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…