

mcpsnoop
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
api-security-testingdebuggersdynamic-analysis-sandboxing+5
359
kerlenton/mcpsnoopWireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 pandaadir05/snoop
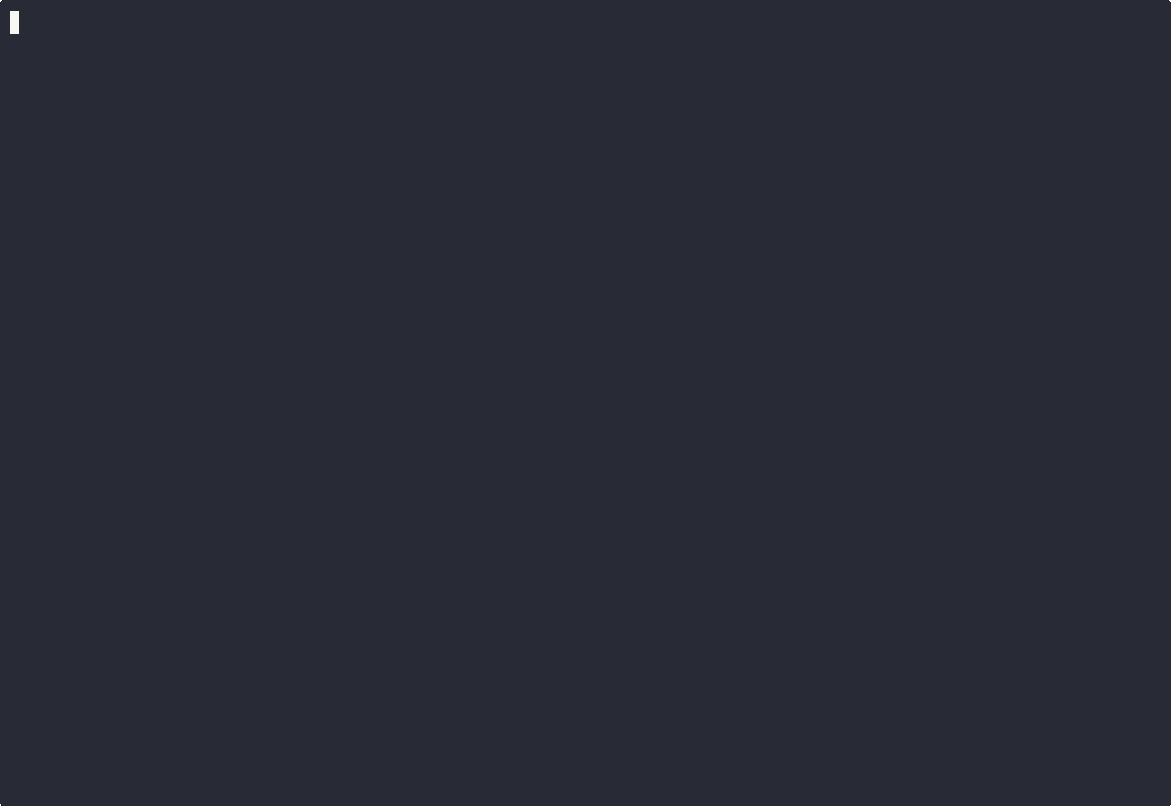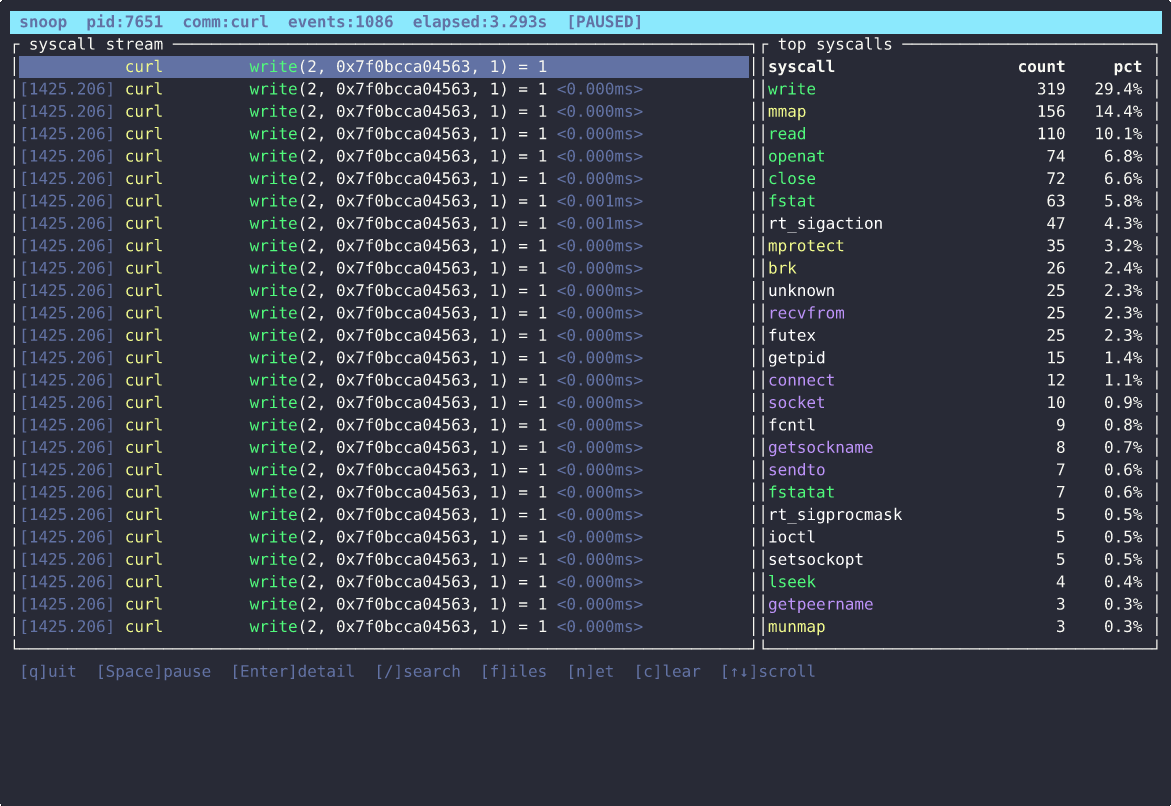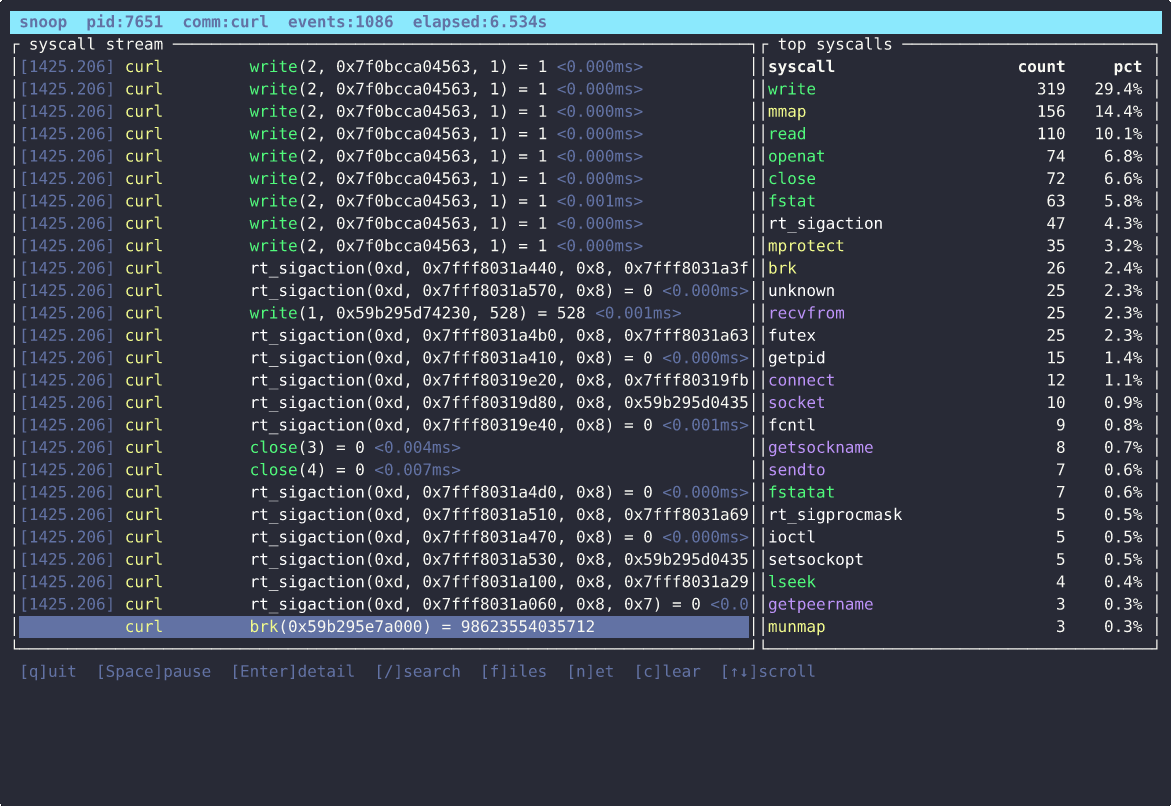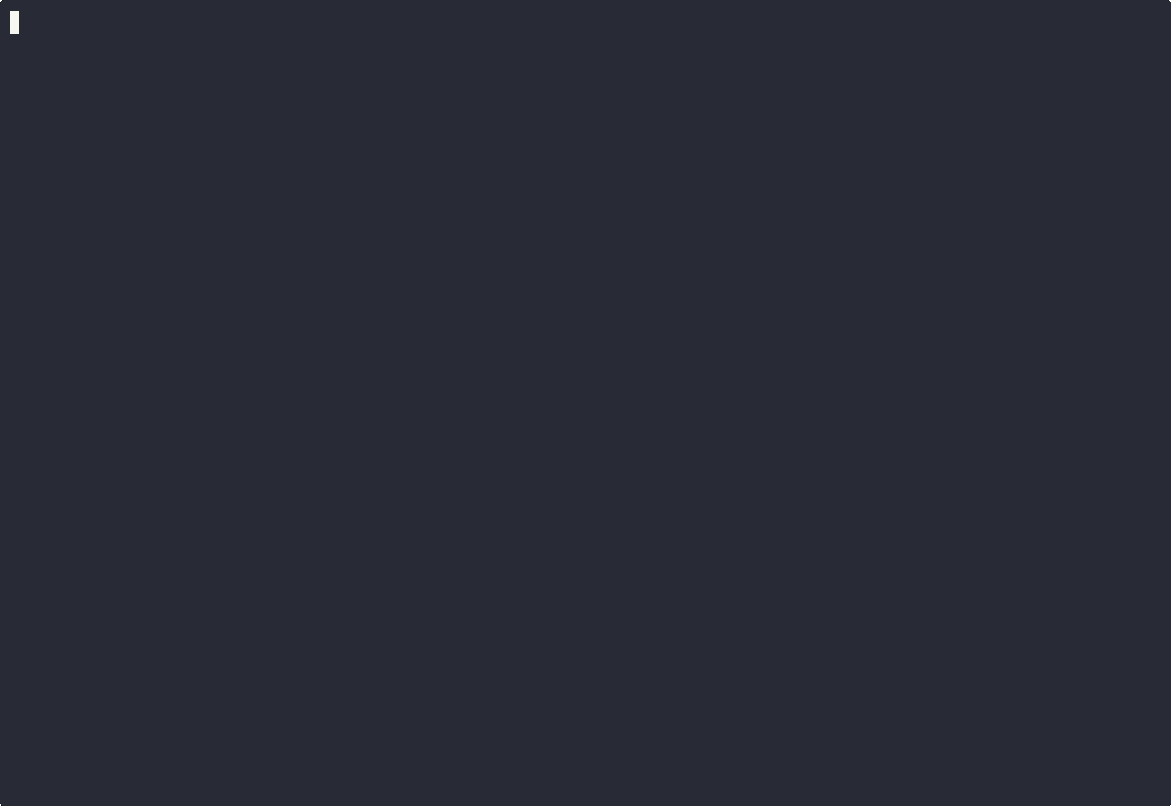
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 guardicore/ipcdump
BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 alexhude/uemu
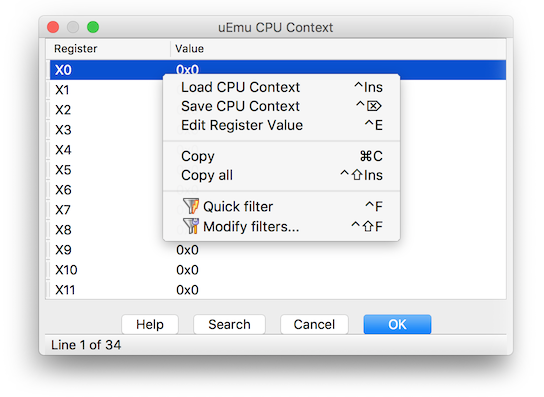
Tiny cute emulator plugin for IDA based on unicorn.
 kdzwinel/betwixt
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.
 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 mandiant/strace
A DTrace on Windows Reimplementation
 deputation/instrumentation_callbacks
A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
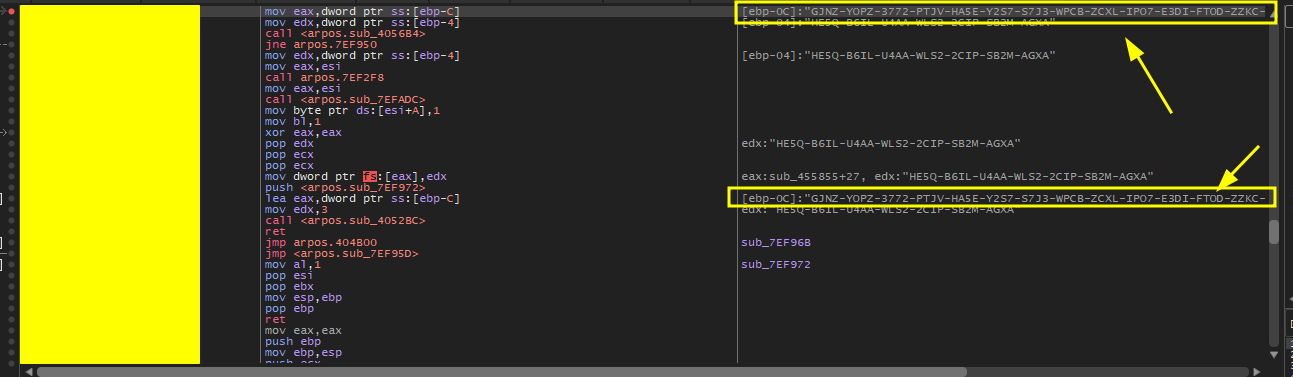 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 cdacesec/cve-2022-31902
Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…