
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
274 results
shannon-dbg preview

shannon-dbg

GitHubsynacktiv/shannon-dbg

Debugger for the Shannon Baseband

binary-analysisdebuggersembedded-systems-security+4
606 years ago
am335xbootrom preview

am335xbootrom

GitHubsjgallagher2/am335xbootrom

Reverse engineering the TI AM3358 boot ROM
binary-analysisdebuggerseducation+4
612 years ago
icicle-python preview

icicle-python

GitHubicicle-emu/icicle-python

Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
binary-analysisdebuggersdynamic-analysis-sandboxing+5
431 year ago
CVE-2025-29824 preview

CVE-2025-29824

GitHubencrypter15/cve-2025-29824

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…

binary-exploitationdebuggerseducation+7
291 year ago
vsock_poc preview

vsock_poc

GitHubjordan9001/vsock_poc

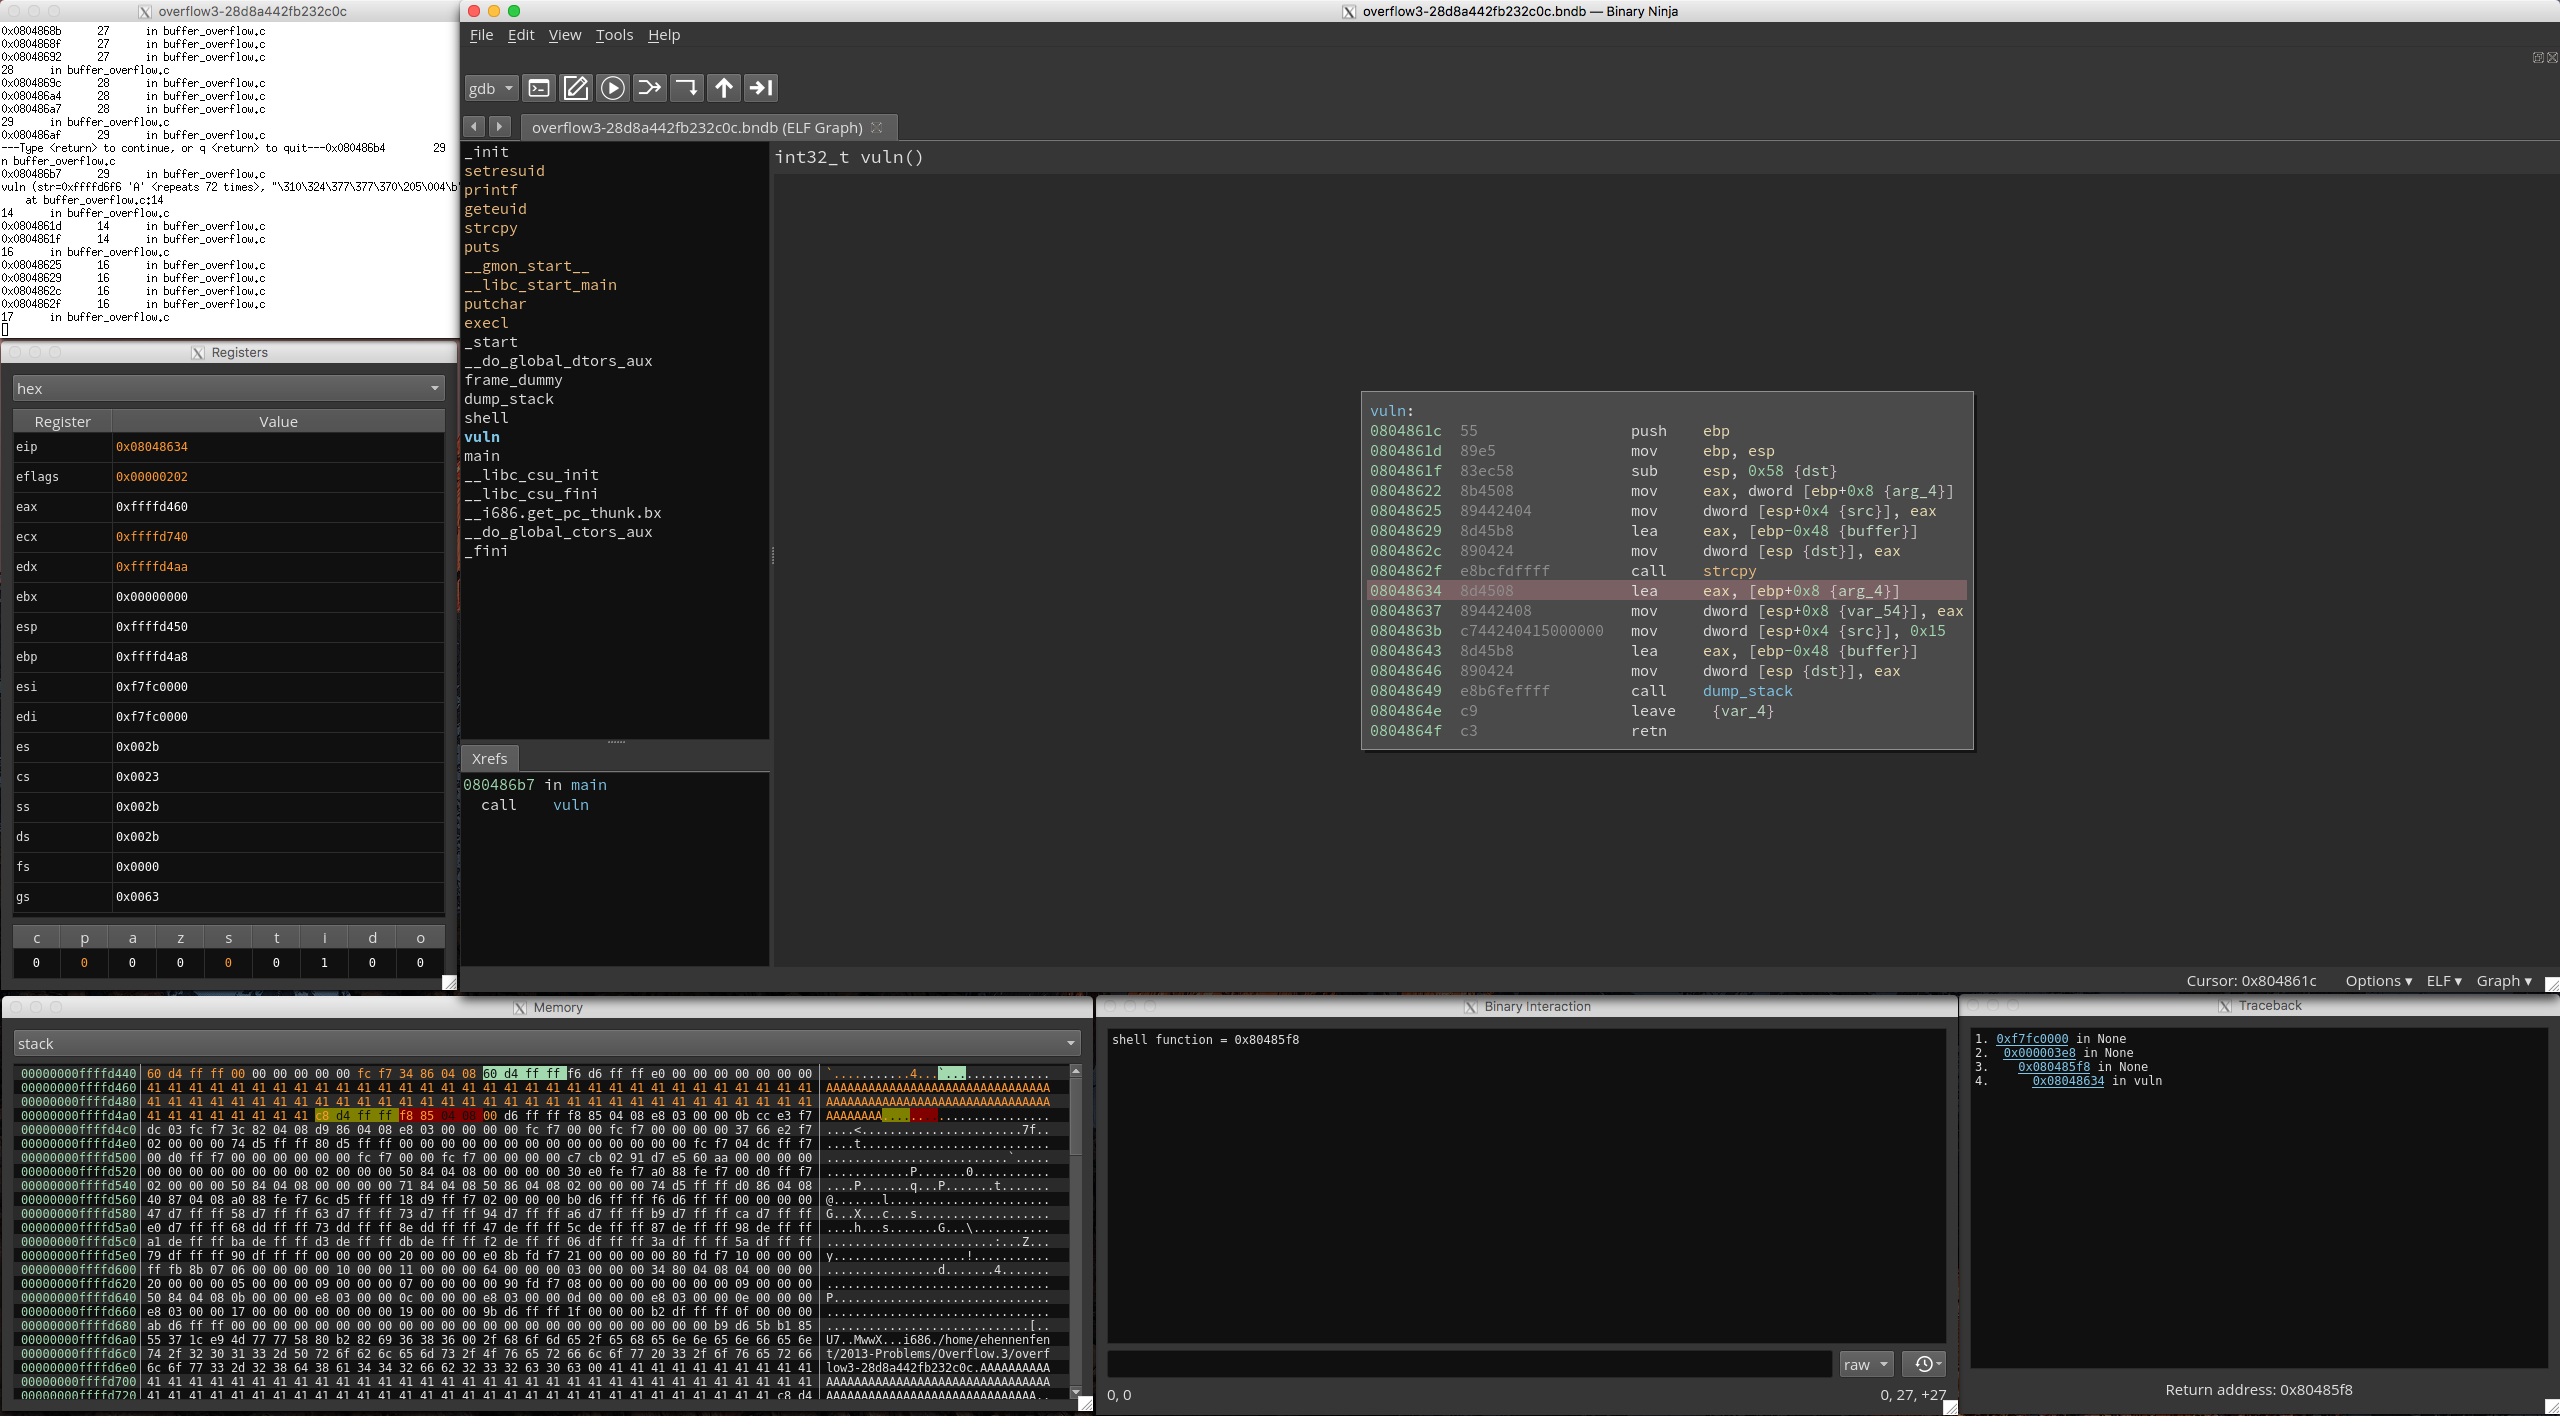
Investigating the bug behind CVE-2021-26708
binary-exploitationdebuggerseducation+3
285 years ago
binja_dynamics preview

binja_dynamics

GitHubnccgroup/binja_dynamics

A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…

binary-analysisdebuggersdynamic-analysis-sandboxing+2
259 years ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
233 months ago
UnBattletech preview

UnBattletech

GitHubvelteyn/unbattletech

BattleTech: The Crescent Hawk's Inception reverse engeneering
binary-analysisdebuggerseducation+3
820 days ago
libtalloc preview

libtalloc

GitHubnccgroup/libtalloc

libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)

binary-analysisdebuggersmemory-forensics+2
1711 years ago
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…

ai-assisted-reversingbinary-analysisdebuggers+4
137 months ago
r2gopclntabParser preview

r2gopclntabParser

GitHubasherdll/r2gopclntabparser

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.

binary-analysisdebuggersforensics+3
176 months ago
LetMeGG preview

LetMeGG

GitHubgmh5225/letmegg

Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…

anti-botbinary-analysisdebuggers+1
154 years ago
Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis preview

Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

GitHubkaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
binary-analysisdebuggersdigital-forensics+6
71 month ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

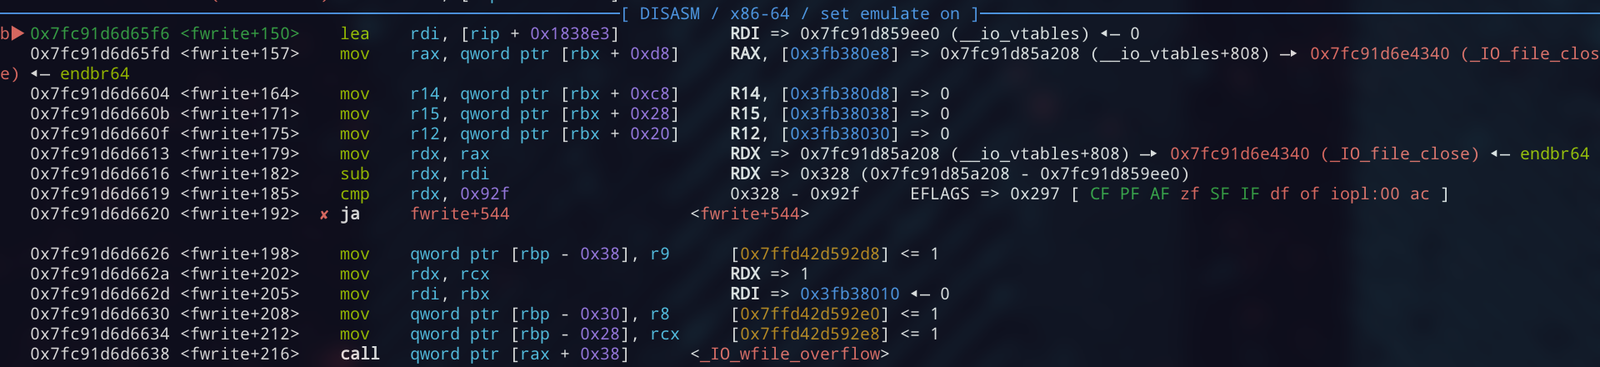
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
LiberationPlay-CVE-2025-24132-AirBourne-POC preview

LiberationPlay-CVE-2025-24132-AirBourne-POC

GitHubthegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc

POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
binary-exploitationcryptographydebuggers+7
88 months ago
CVE-2016-2334 preview

CVE-2016-2334

GitHubicewall/cve-2016-2334

Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
binary-exploitationdebuggersexploitation+3
108 years ago
Transformers-Forged-To-Fight-Offline-Version preview

Transformers-Forged-To-Fight-Offline-Version

GitHubgeamztheangrybirds727/transformers-forged-to-fight-offline-version

TRANSFORMERS: Forged to Fight is a 3D combat game where you take over some of the most charismatic troopers straight out of the Transformers…
binary-analysisbinary-exploitationcurated-resources+5
24 months ago
Linksys-WRT54GL-Exploitation preview

Linksys-WRT54GL-Exploitation

GitHubumbertodellamonica/linksys-wrt54gl-exploitation

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

binary-analysisdebuggerseducation+9
25 months ago
Previous1…345…16Next