Archived
gdbfuzz
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
binary-analysisdebuggerseducation+6
194
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
 idarlingteam/idarling
Collaborative Reverse Engineering plugin for IDA Pro & Hex-Rays
 zhuyansen/awesome-ai-reverse-engineering
Open-source AI reverse engineering tools for coding agents: Ghidra MCP, IDA Pro MCP, jadx, Frida, skills and REA. 122 repos, each read and…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 das-labor/panopticon
A libre cross-platform disassembler.
 mandiant/flare-ida
IDA Pro utilities from FLARE team
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
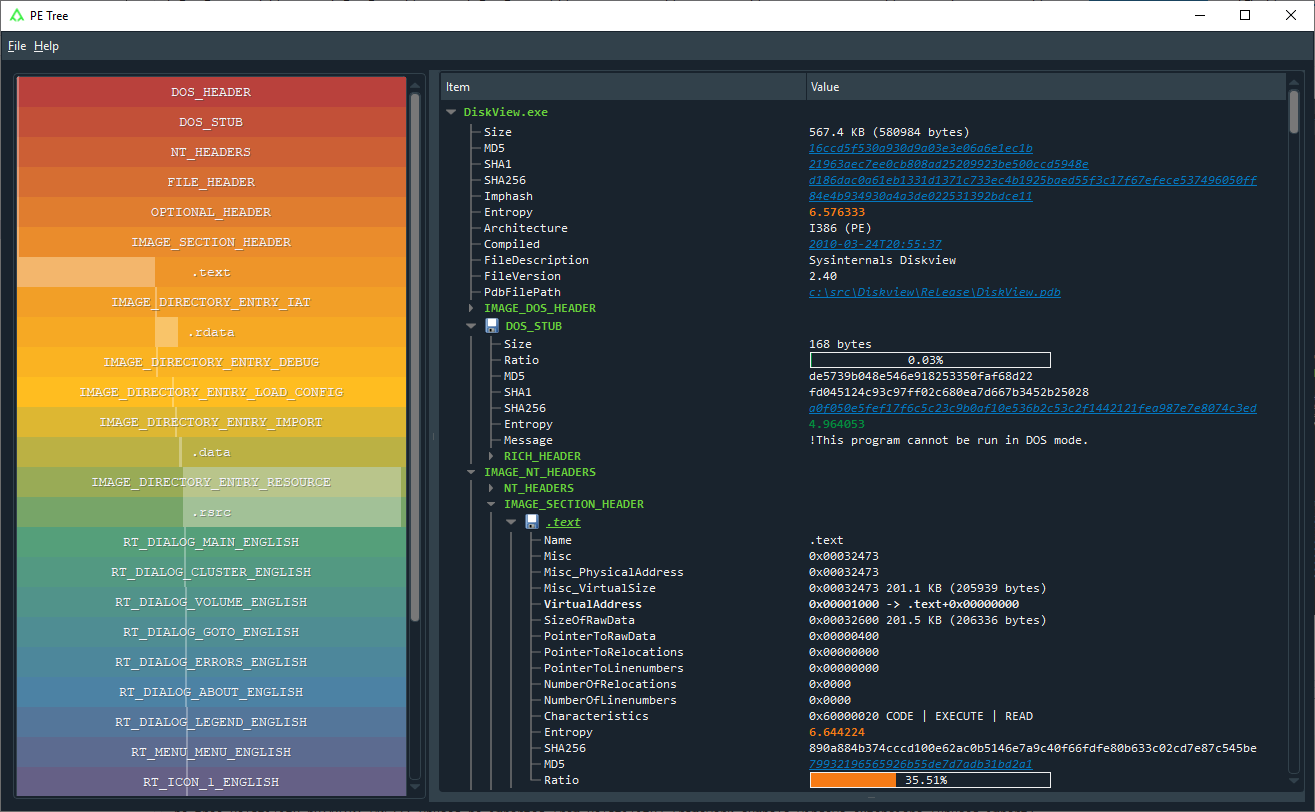 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 lauriewired/jadxecute
JADX-gui scripting plugin for dynamic decompiler manipulation
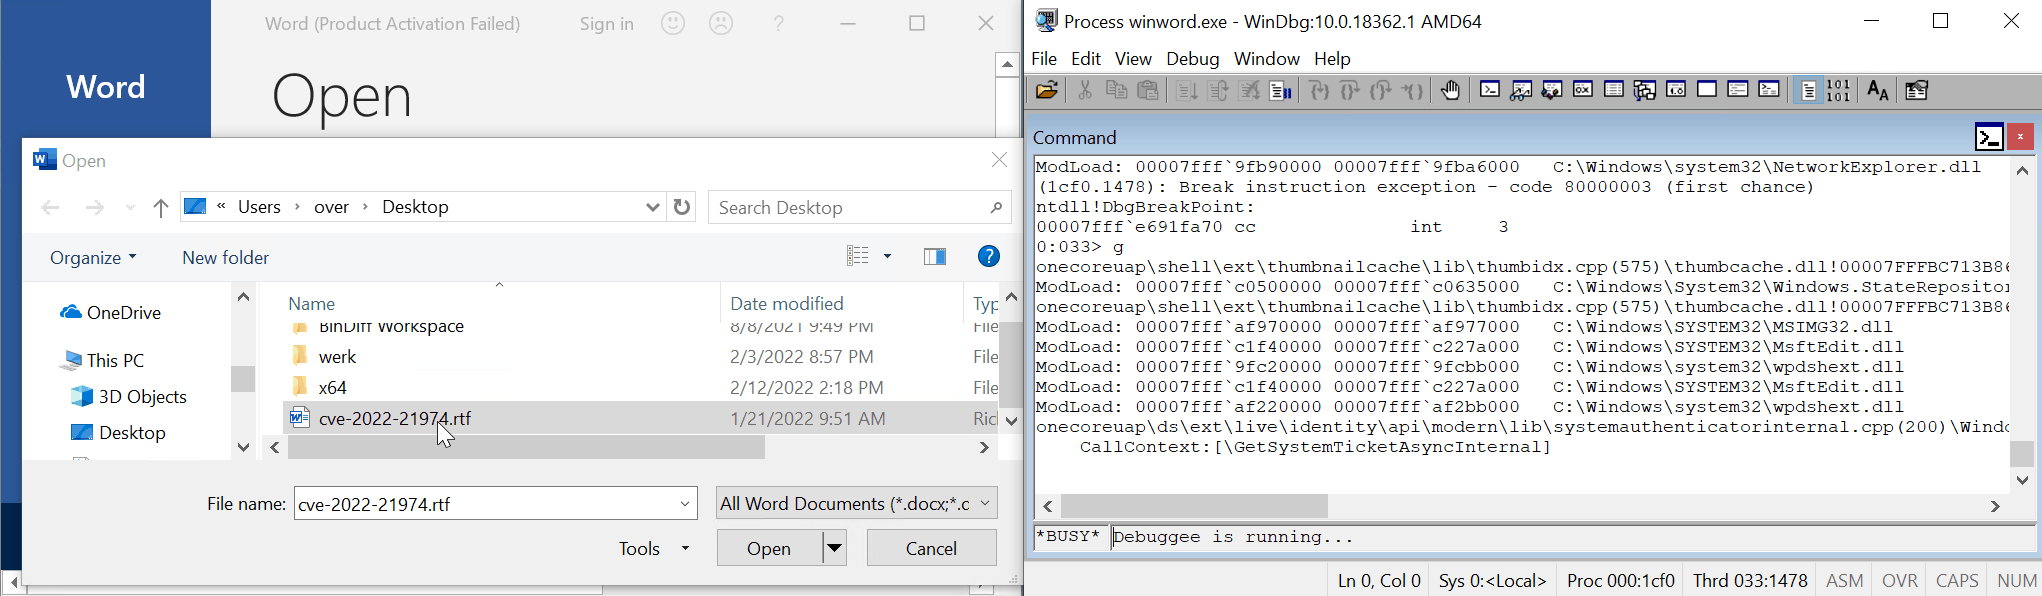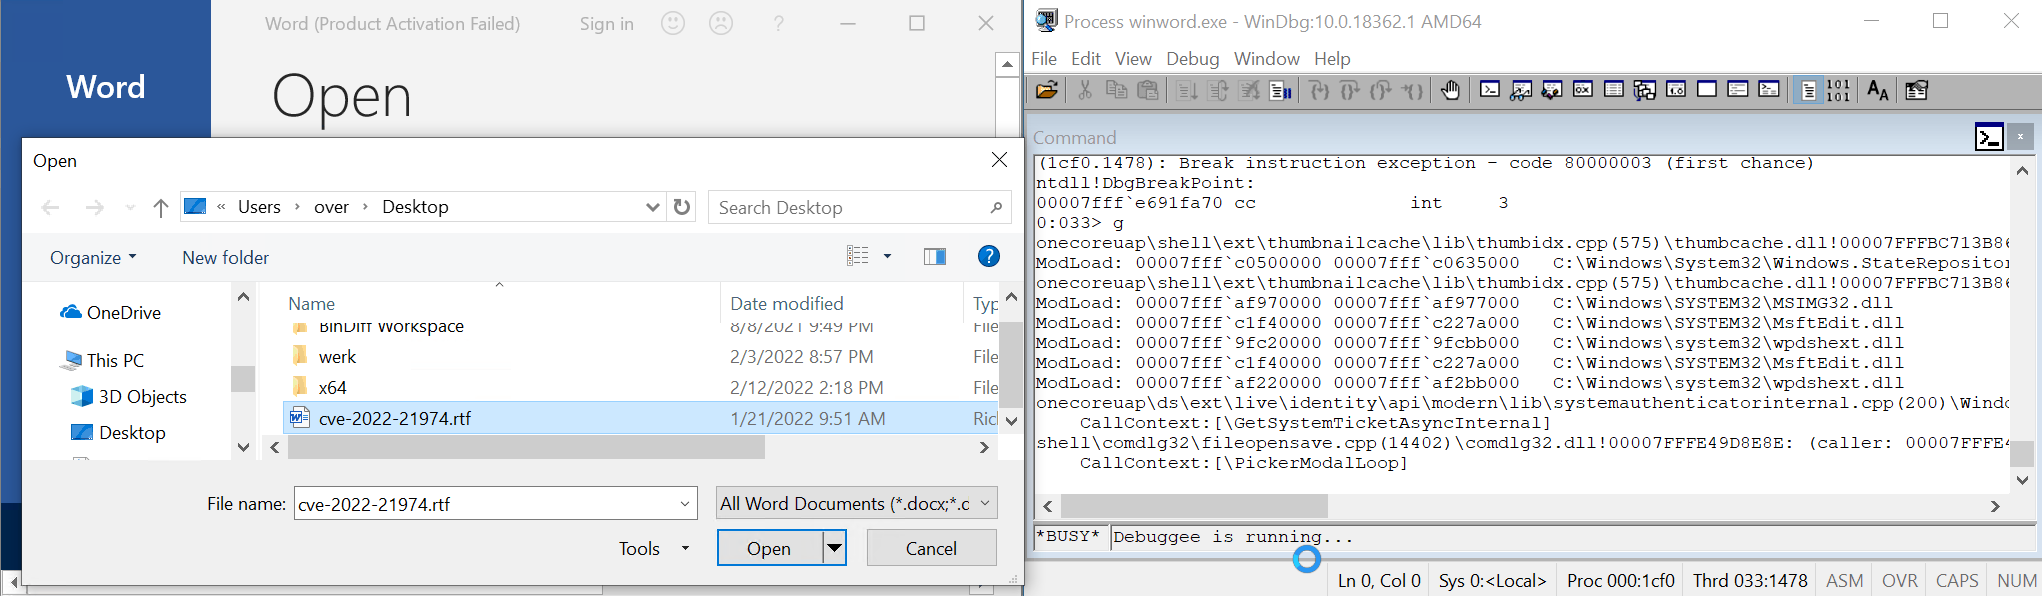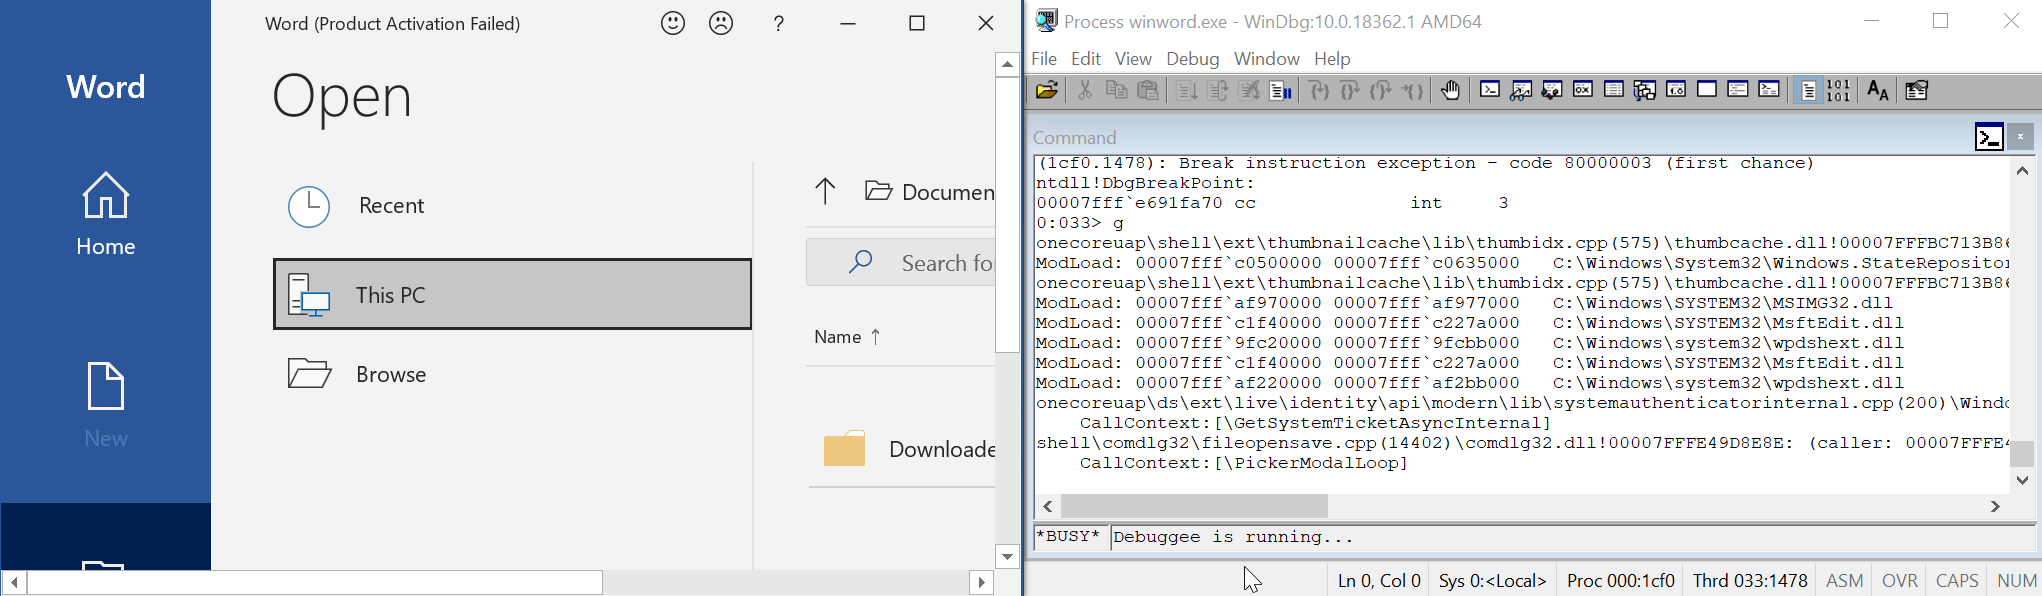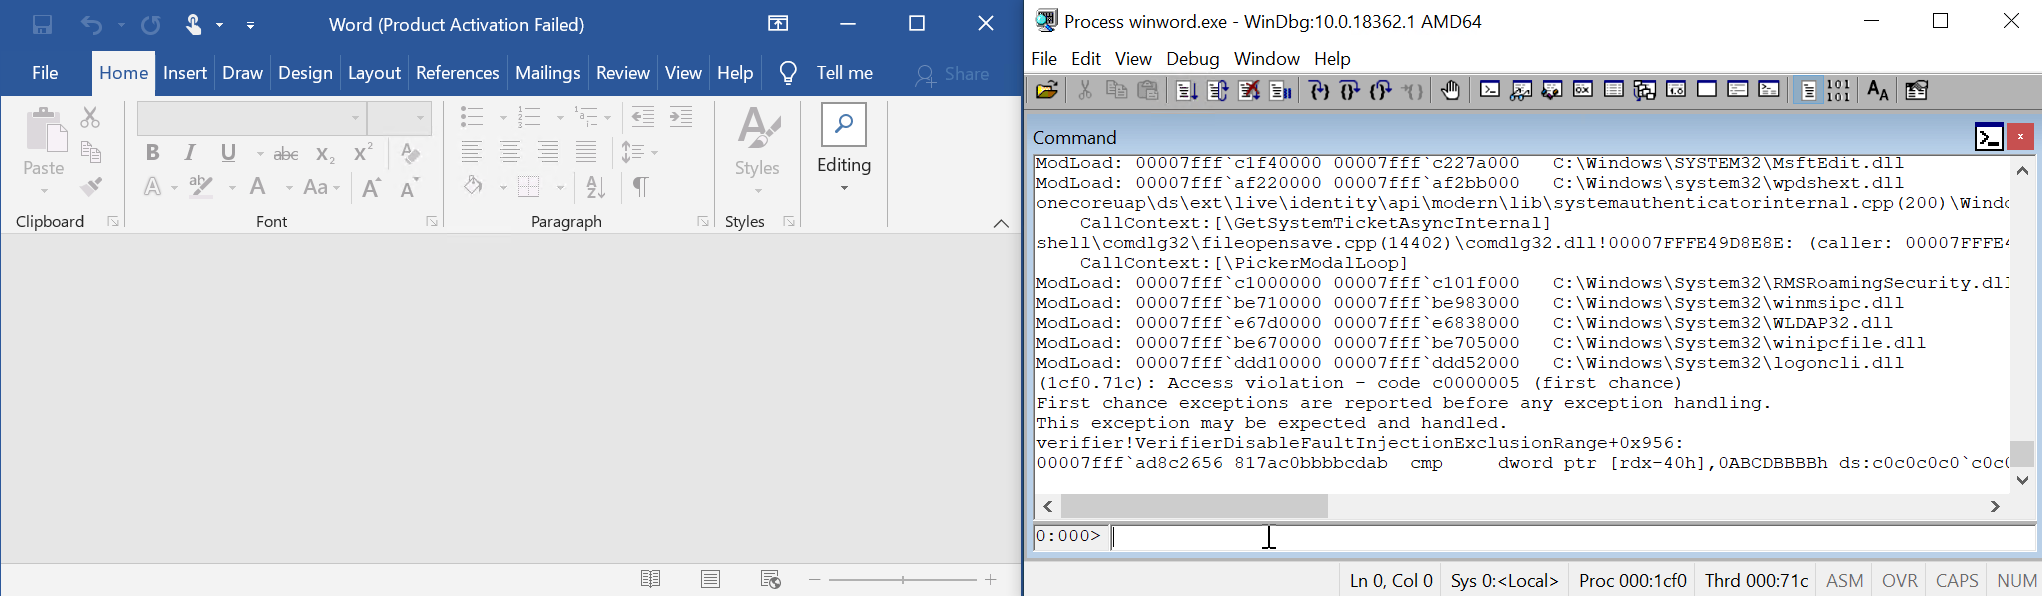 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#