

apiscope
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
kaisonox/apiscopeAn API hooking framework for intercepting and monitoring Windows applications
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 gmh5225/ollytlscatch
OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
 moniik/cve-2019-11043_env
remote debug environment for CLion
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
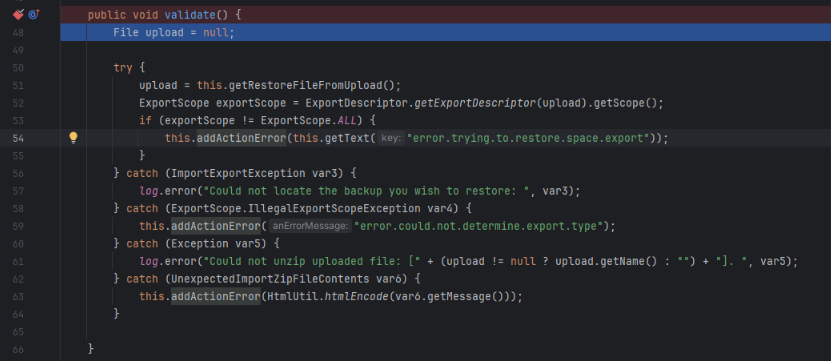 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 day6reak/cve-2014-4109
Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…
 day6reak/cve-2014-4140
Technical notes and debugger analysis for CVE-2014-4140, a use-after-free vulnerability in MSHTML's CHtmRootParseCtx::AddText leading to remote code…
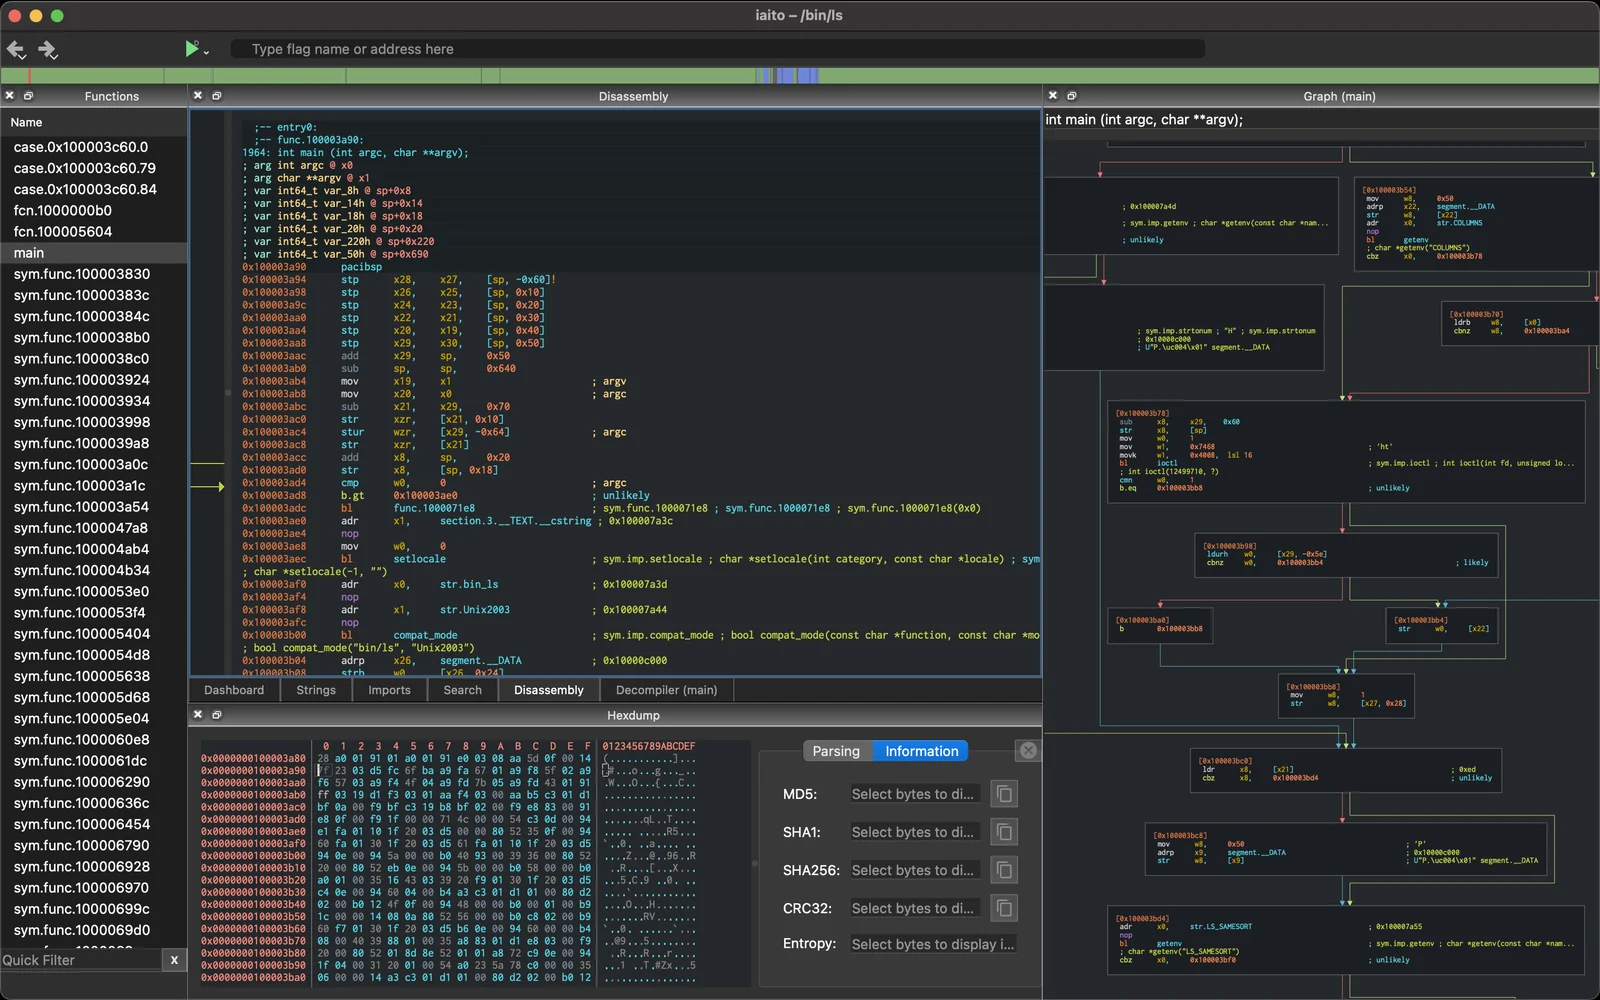 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x