

tvm-recover
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
binary-analysisbinary-exploitationcode-analysis+5
1
neurosaki987/tvm-recoverDevirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 fortra/cve-2023-28252
Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 ynwarcs/cve-2024-30052
Materials for CVE-2024-30052.
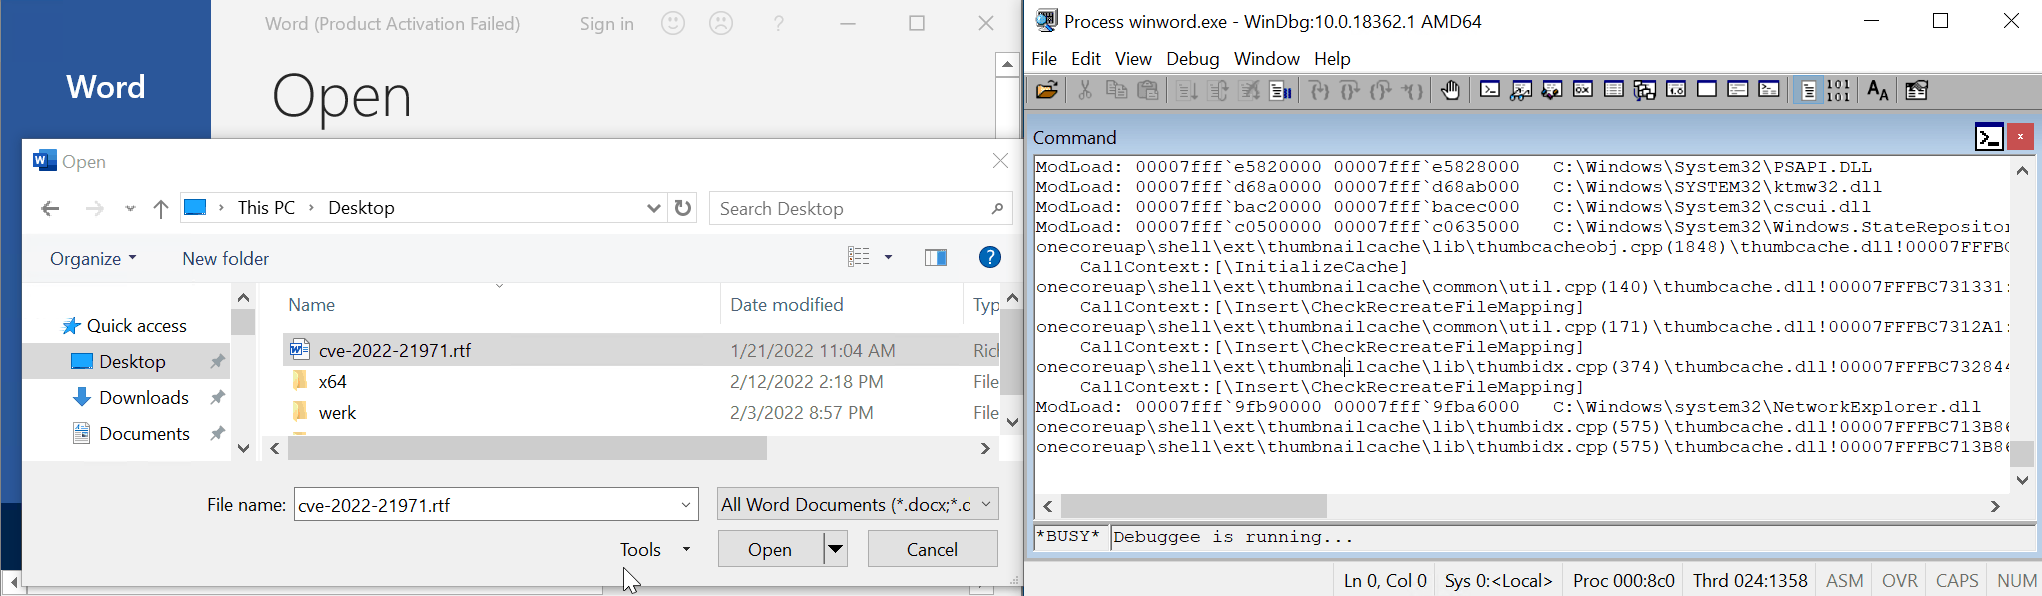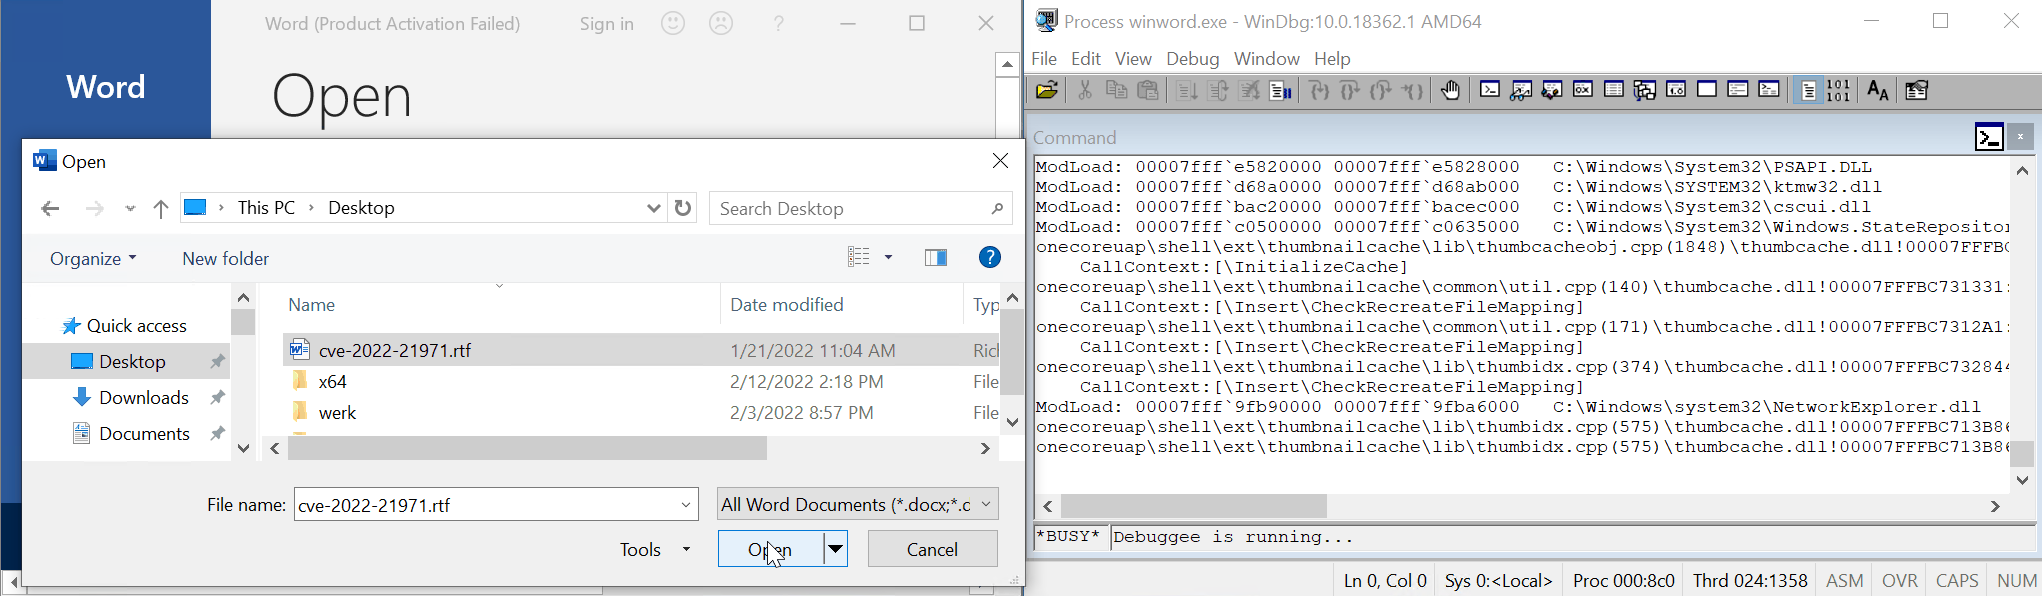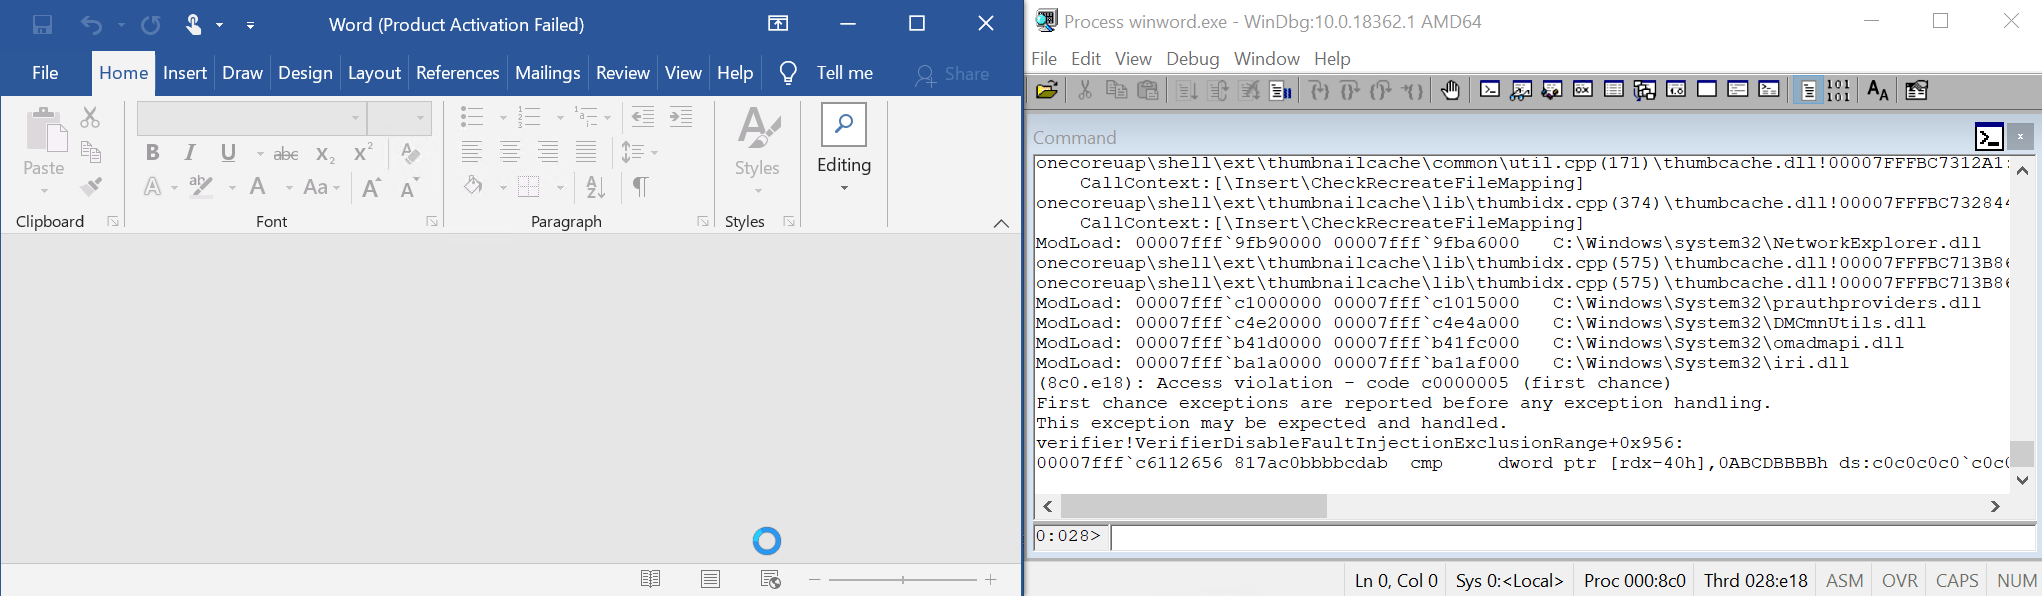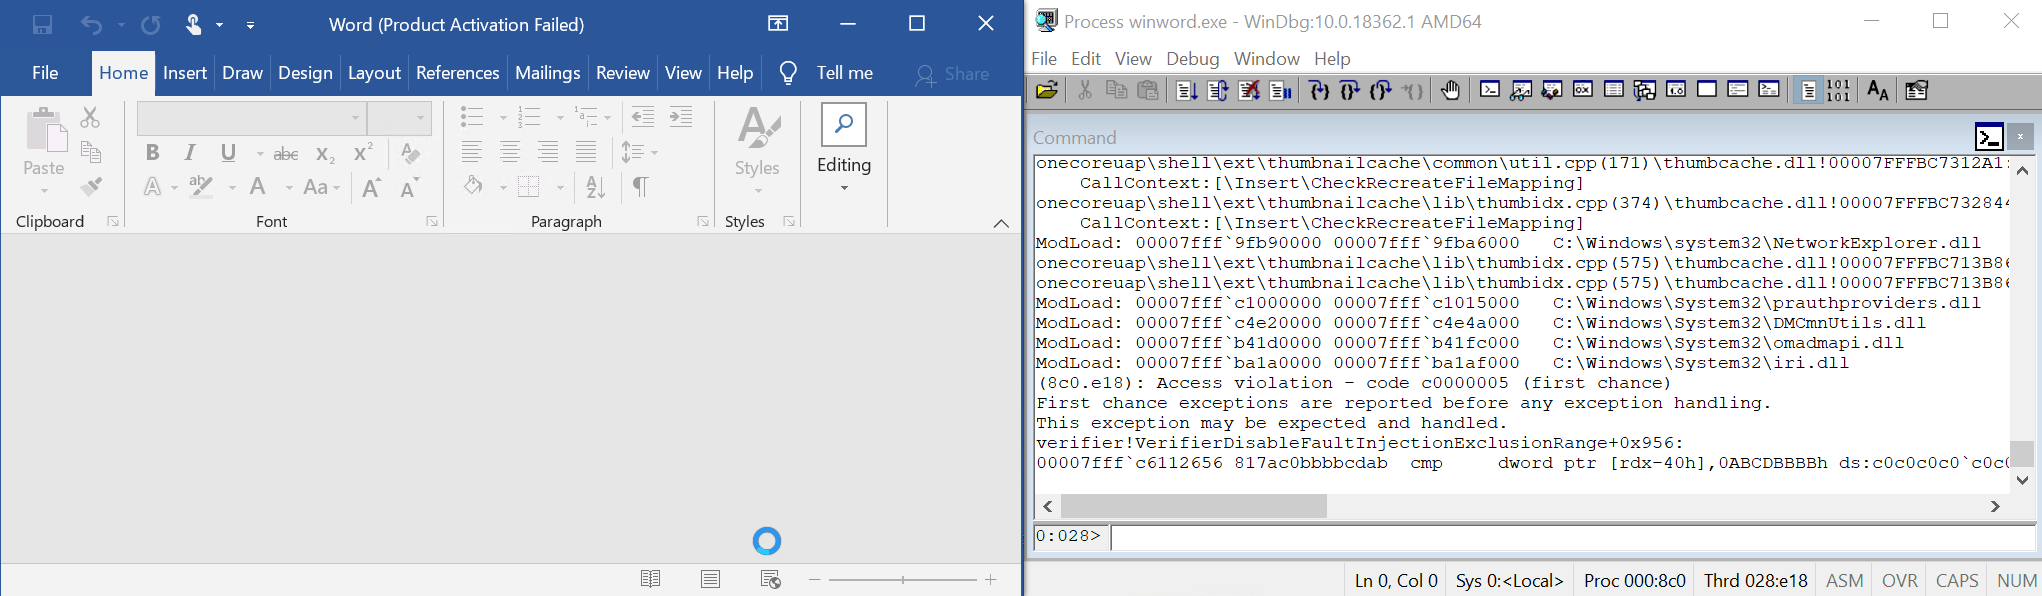 malwareman007/cve-2022-21971
POC Of CVE-2022-21971
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
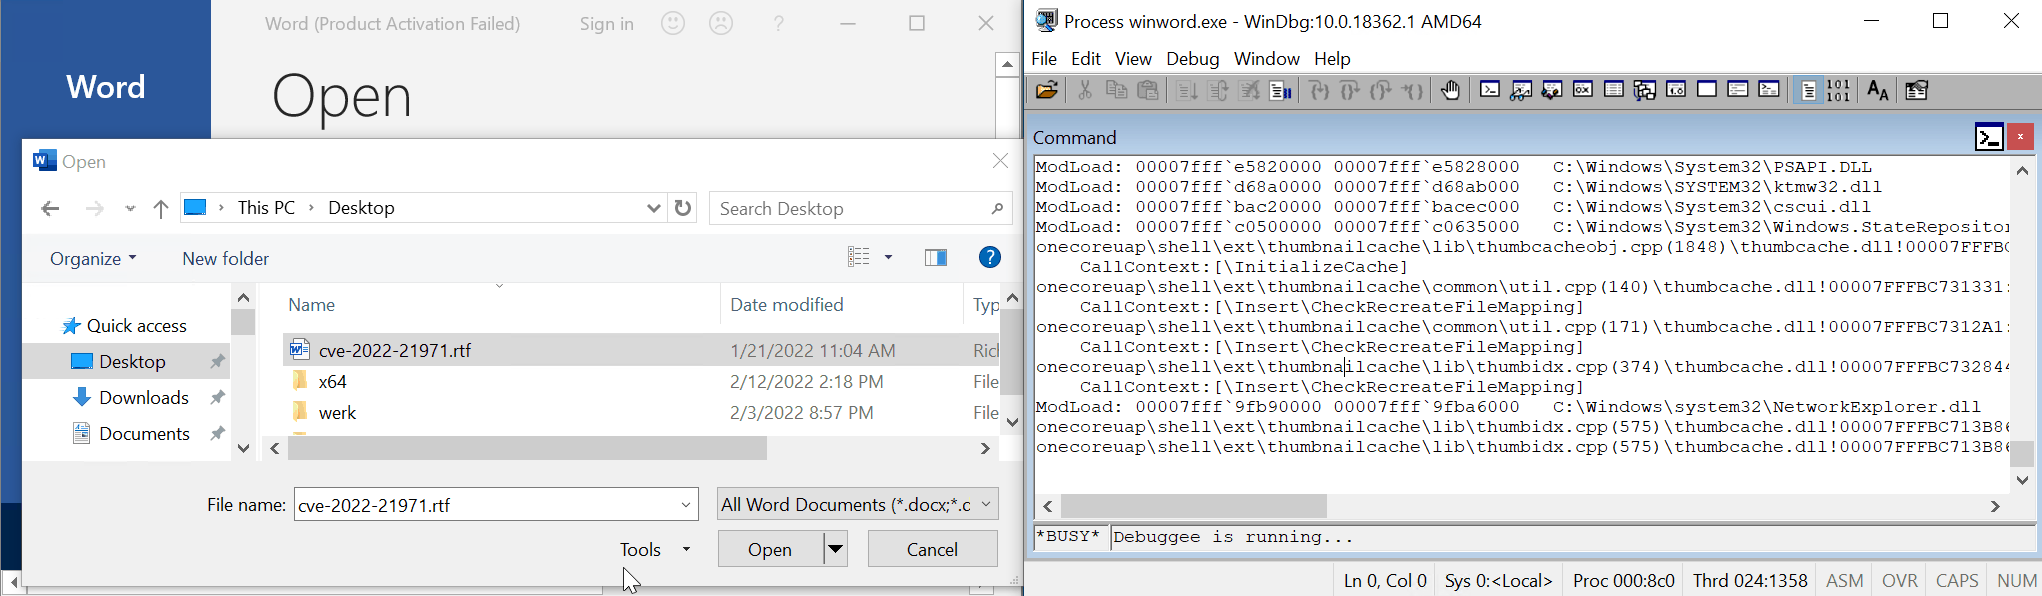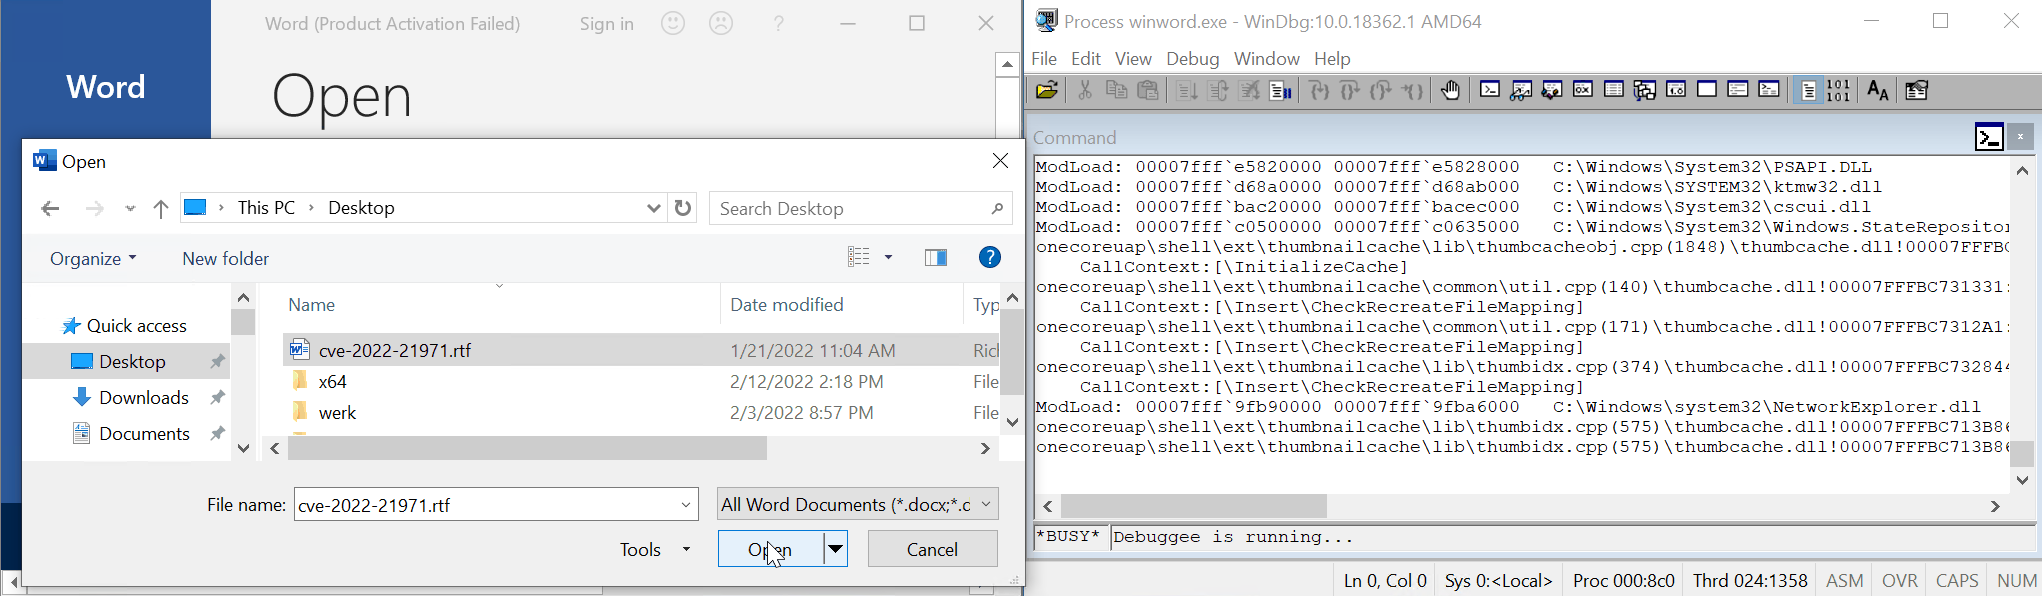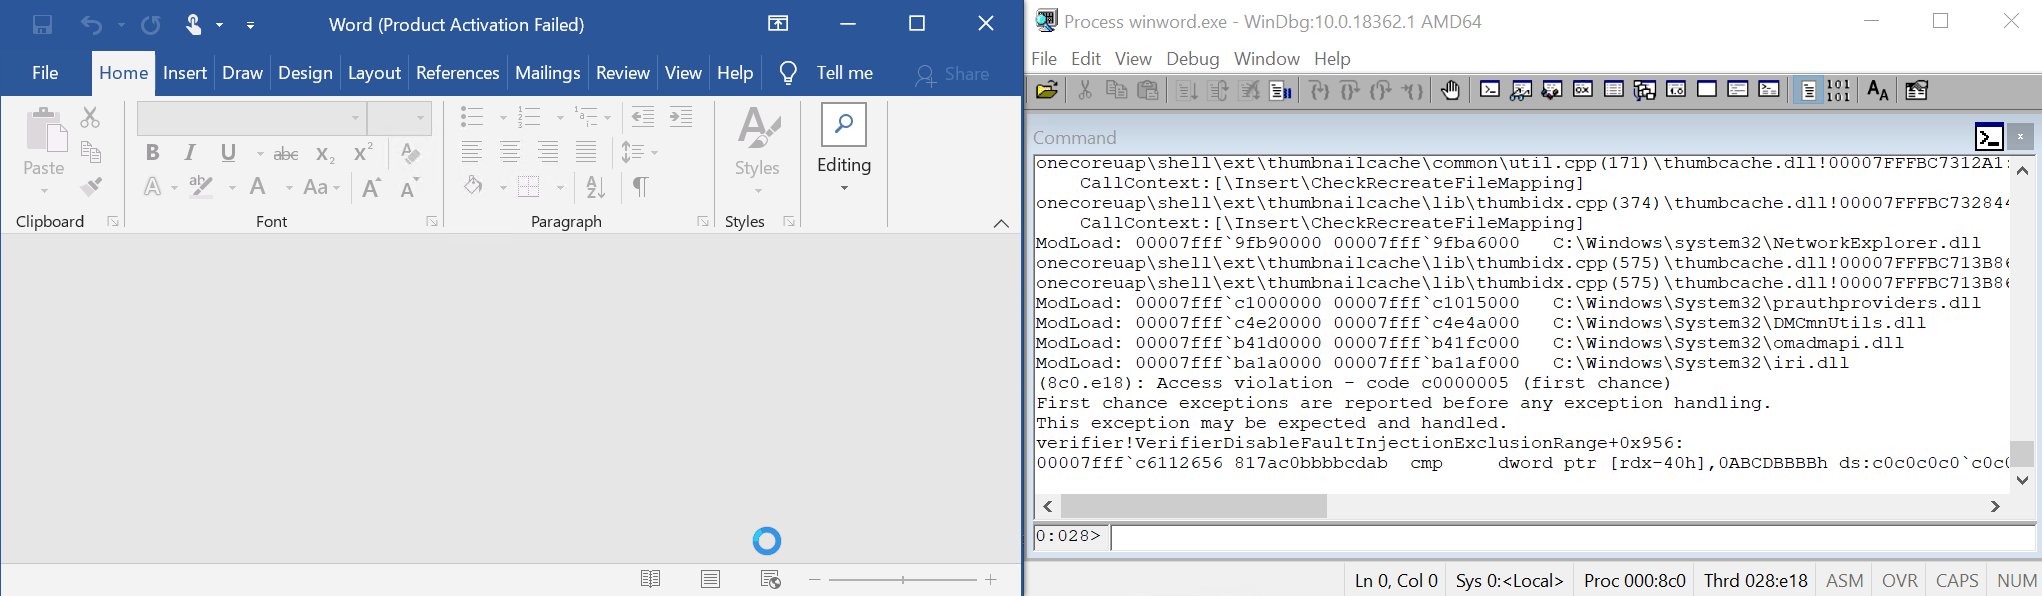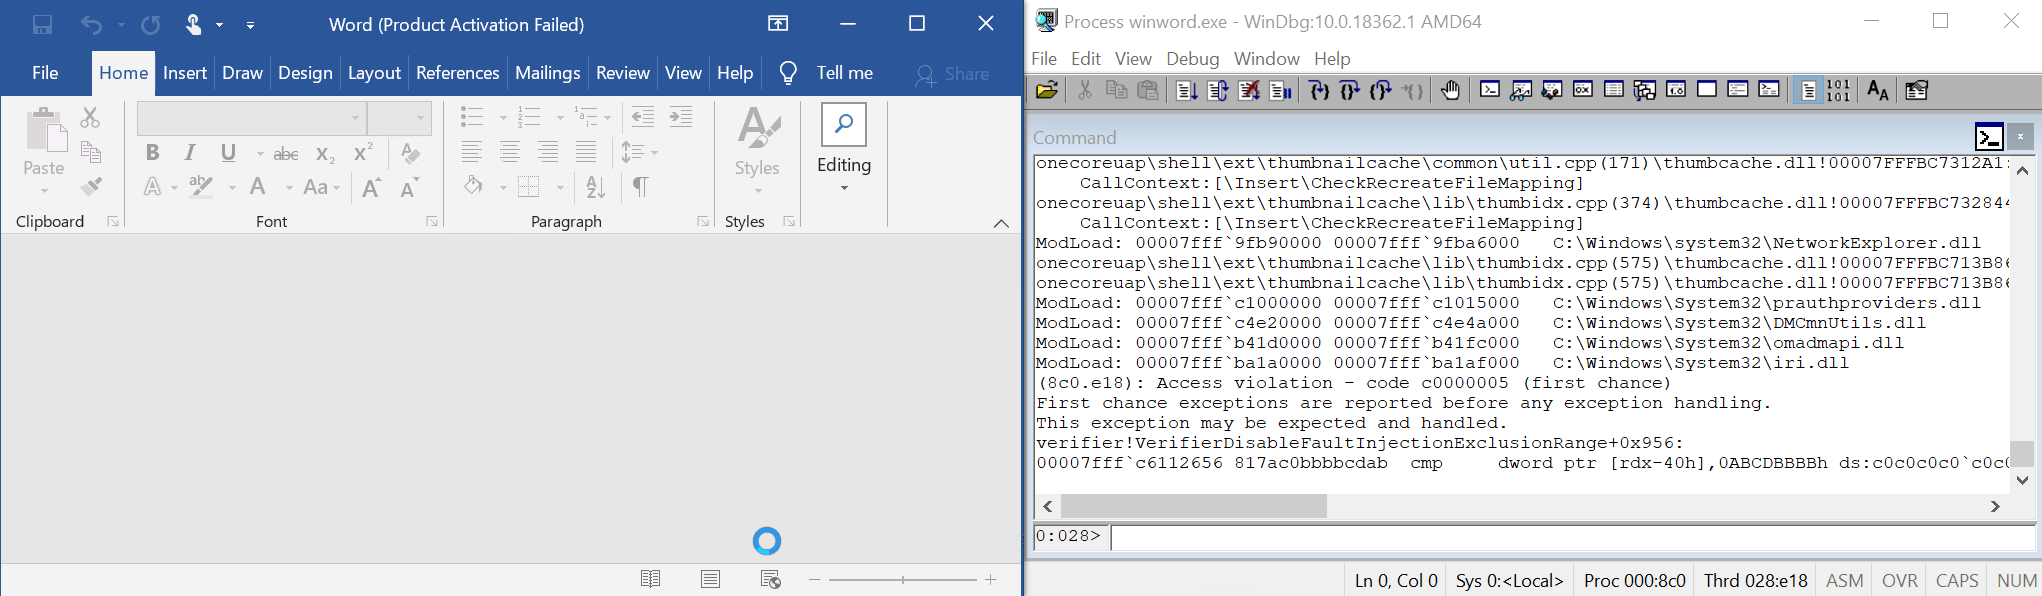 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
 jaf0rk/cve-2026-5281
Proof-of-concept exploit for CVE-2026-5281, a heap-use-after-free vulnerability in Chromium's Dawn WebGPU implementation, with ASAN log and build…
 halcy0nic/cve-2022-43343
Proof of concept for (CVE-2022-43343)
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
 q1f3/triple_fetch
This is an exploit for CVE-2017-7047, Works on 10.3.2 and below.