Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
174 results
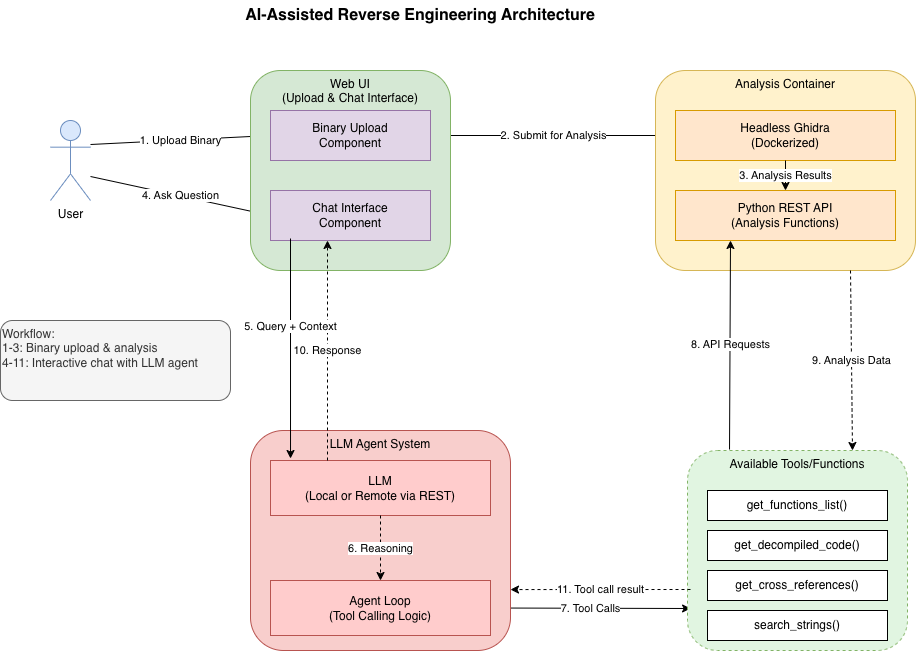
ai-reverse-engineering preview

ai-reverse-engineering

GitHubbiniamf/ai-reverse-engineering

AI-Assisted Reverse Engineering with Ghidra
ai-assisted-reversingai-securitybinary-analysis+3
158
3 months ago
idamcp preview

idamcp

GitHubidamcp/idamcp

MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
ai-assisted-reversingbinary-analysisdebuggers+3
1252 days ago
bread preview

bread

GitHubtheldus/bread

Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
binary-analysisdebuggersfirmware-analysis+2
3261 year ago
fhex preview

fhex

GitHubecho-devim/fhex

A Full-Featured HexEditor compatible with Linux/Windows/MacOS
binary-analysisdebuggersforensics+2
4371 year ago
IPCDump preview

IPCDump

GitHubguardicore/ipcdump

BPF-based Linux IPC tracer for pipes, signals, Unix sockets, loopback, and pseudoterminals with metadata and content capture, filtering, and JSON…
debuggersdynamic-analysis-sandboxingforensics+1
2475 years ago
FindFunc preview

FindFunc

GitHubfelixber/findfunc

IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…
binary-analysiscode-analysisdebuggers+2
36211 months ago
windbg_js_scripts preview

windbg_js_scripts

GitHubhugsy/windbg_js_scripts

Toy scripts for playing with WinDbg JS API

binary-analysisdebuggersdynamic-code-analysis+3
2442 years ago
pylane preview

pylane

GitHubnteseyes/pylane

An python vm injector with debug tools, based on gdb.

binary-analysisdebuggersdynamic-analysis-sandboxing+1
3593 years ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1551 day ago
idasec preview

idasec

GitHubrobindavid/idasec

IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1178 years ago
regenerator2000 preview

regenerator2000

GitHubricardoquesada/regenerator2000

An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…

binary-analysisdebuggerseducation+3
16311h 37m ago
ceasta preview

ceasta

GitHubngwg/ceasta

Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
1791 month ago
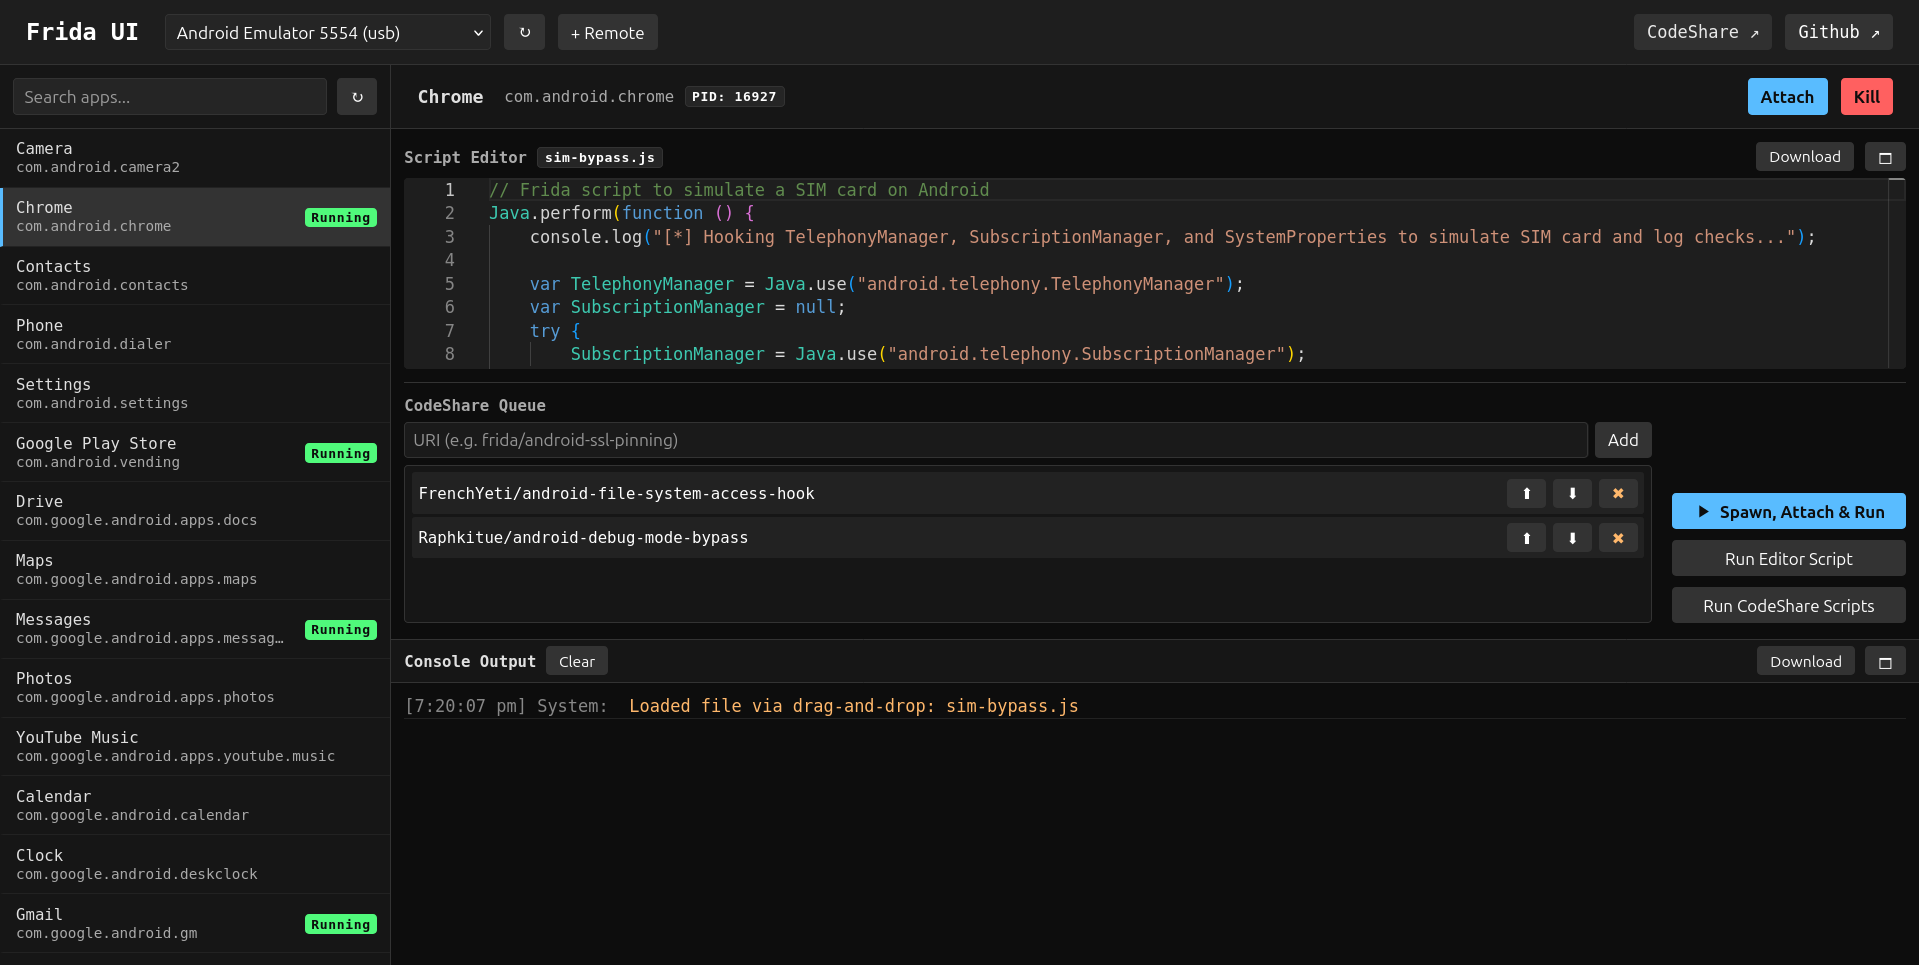
frida-ui preview

frida-ui

GitHubadityatelange/frida-ui

Interact with Frida devices, processes, and scripts directly from your browser.

android-securitydebuggersdynamic-analysis-sandboxing+5
2387 months ago
showstopper preview

showstopper

GitHubcheckpointsw/showstopper

ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…

debuggerseducationmalware-analysis+1
2244 years ago
instrumentation_callbacks preview

instrumentation_callbacks

GitHubdeputation/instrumentation_callbacks

A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1604 years ago
asafw preview

asafw

GitHubnccgroup/asafw

Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]

binary-analysisdebuggersembedded-systems-security+4
1074 years ago
grap preview

grap

GitHubquosecgmbh/grap

Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…

binary-analysisdebuggersmalware-analysis+2
1554 years ago
rea-rust preview

rea-rust

GitHubnanashili/rea-rust

Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker

ai-assisted-reversingbinary-analysisdebuggers+7
696 days ago
Previous1234…10Next