libunwind_CVE-2015-3239_After

Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.

Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.

Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…

reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…

Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…


Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…


PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

frida-stalker based system call tracer on windows(x64).

PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU

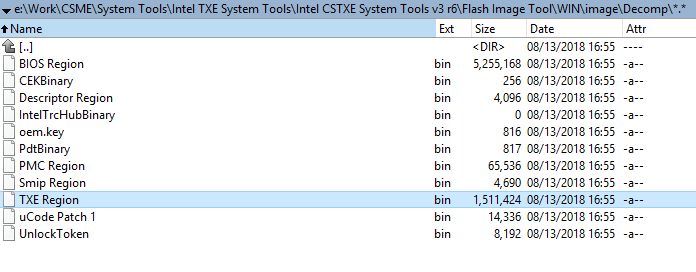
Intel Management Engine JTAG Proof of Concept