
MemITM
 amossys/memitm
Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
amossys/memitmTool to make in memory man in the middle
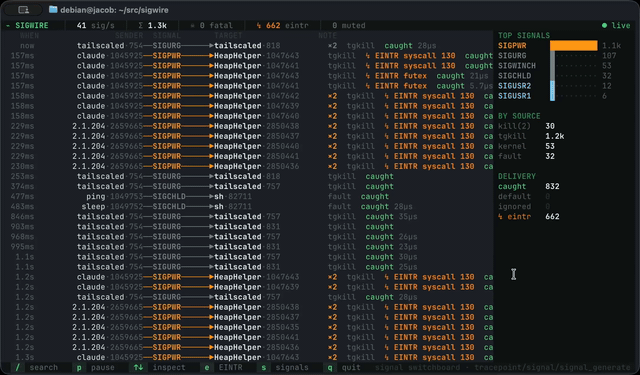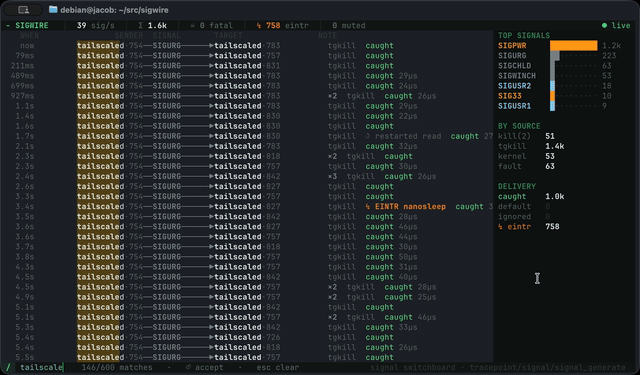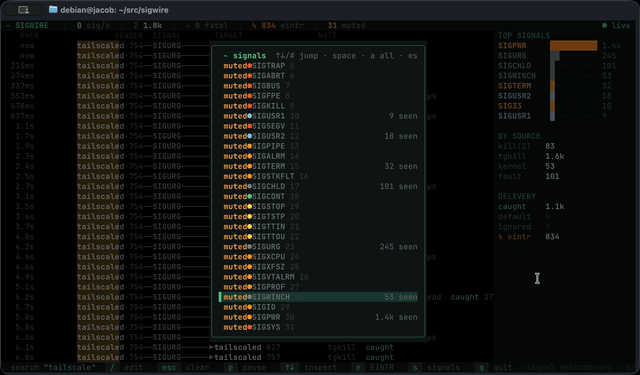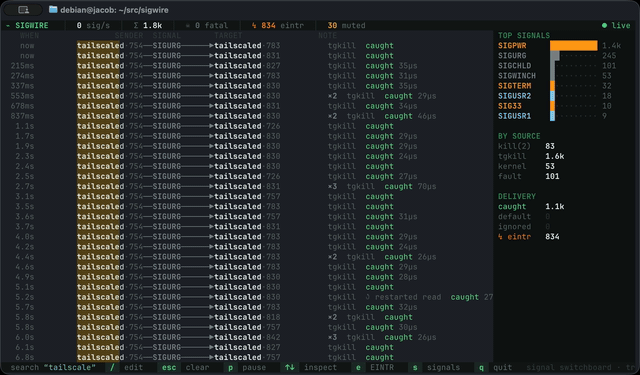 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 jhftss/ida2obj
Static binary instrumentation tool that dumps COFF object files from executables, enabling code/data insertion at any location for black-box fuzzing…
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
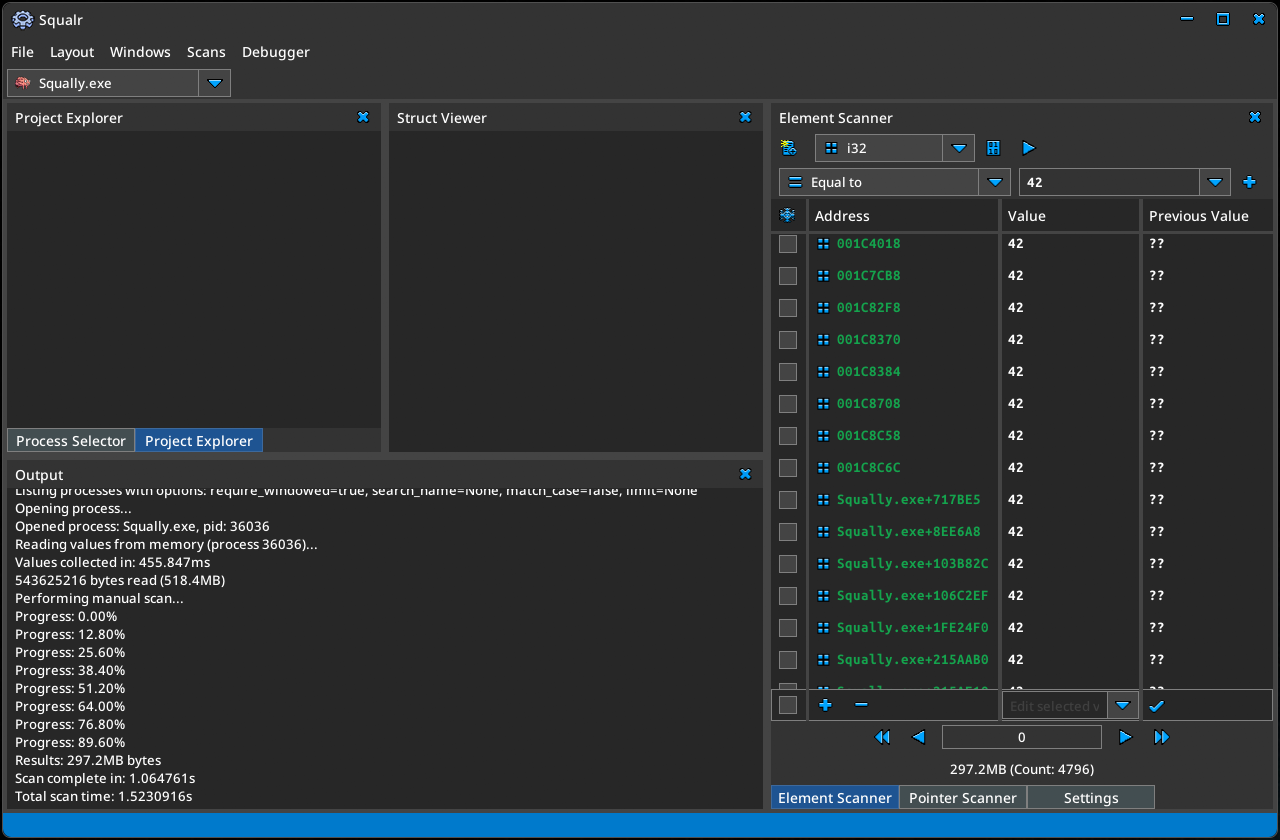 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.

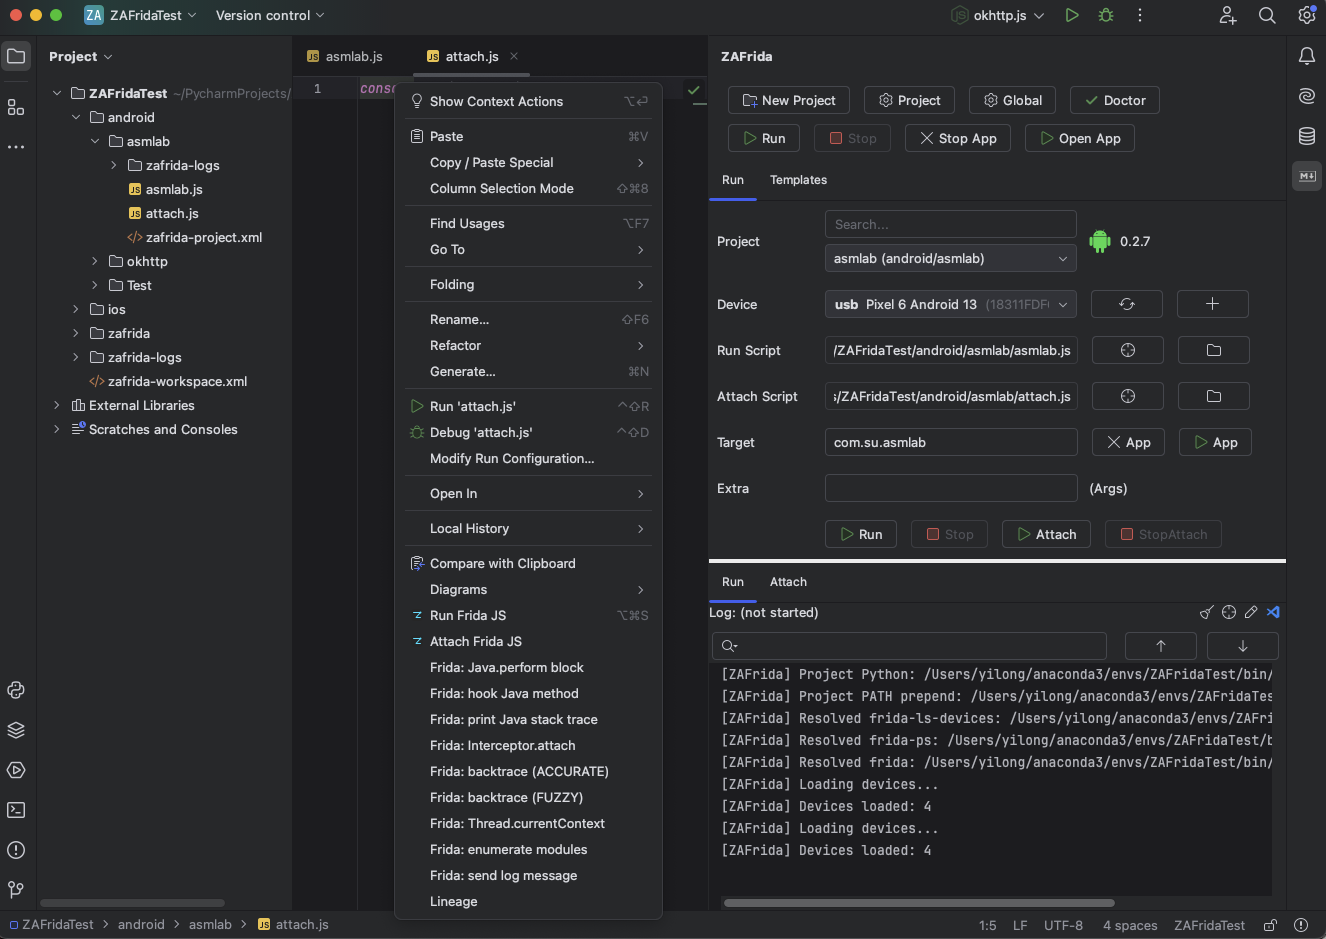 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
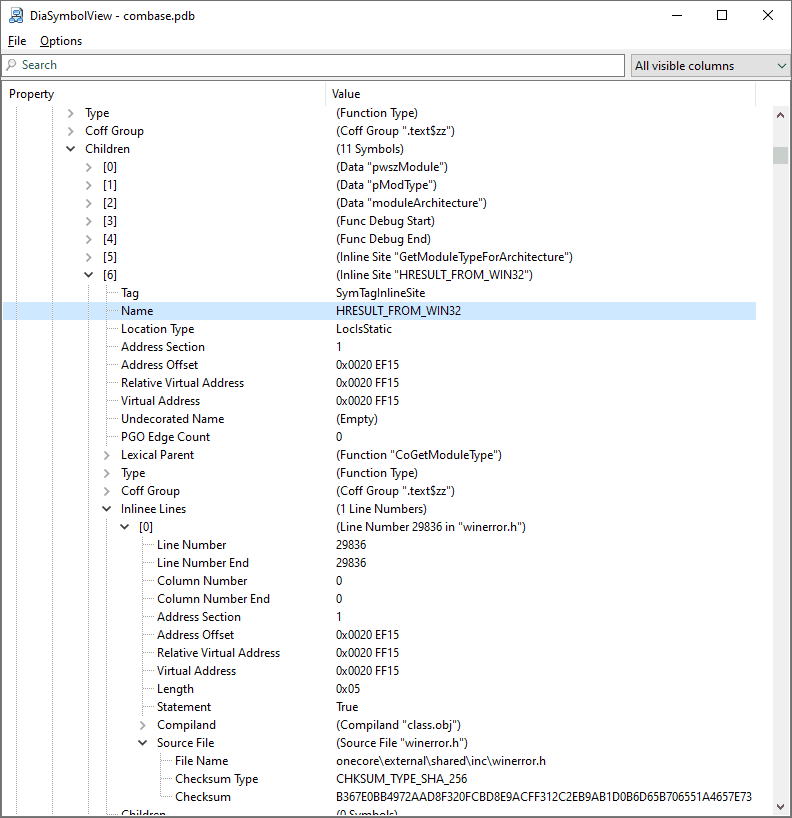 diversenok/diasymbolview
PDB file inspection tool
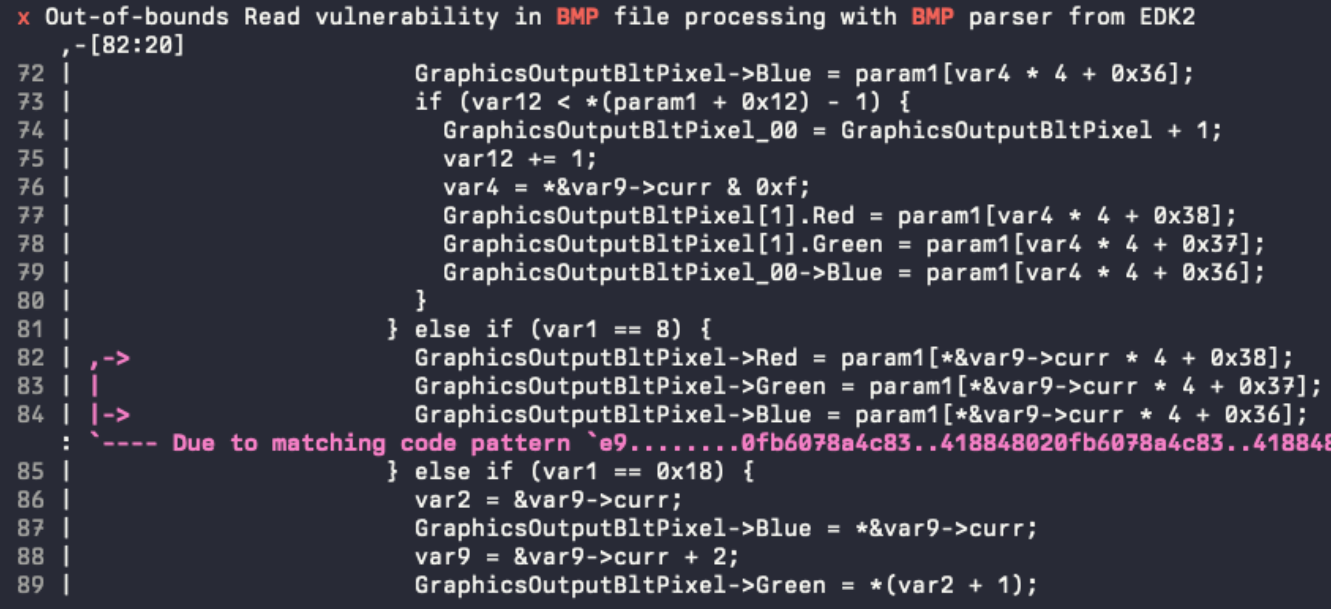 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
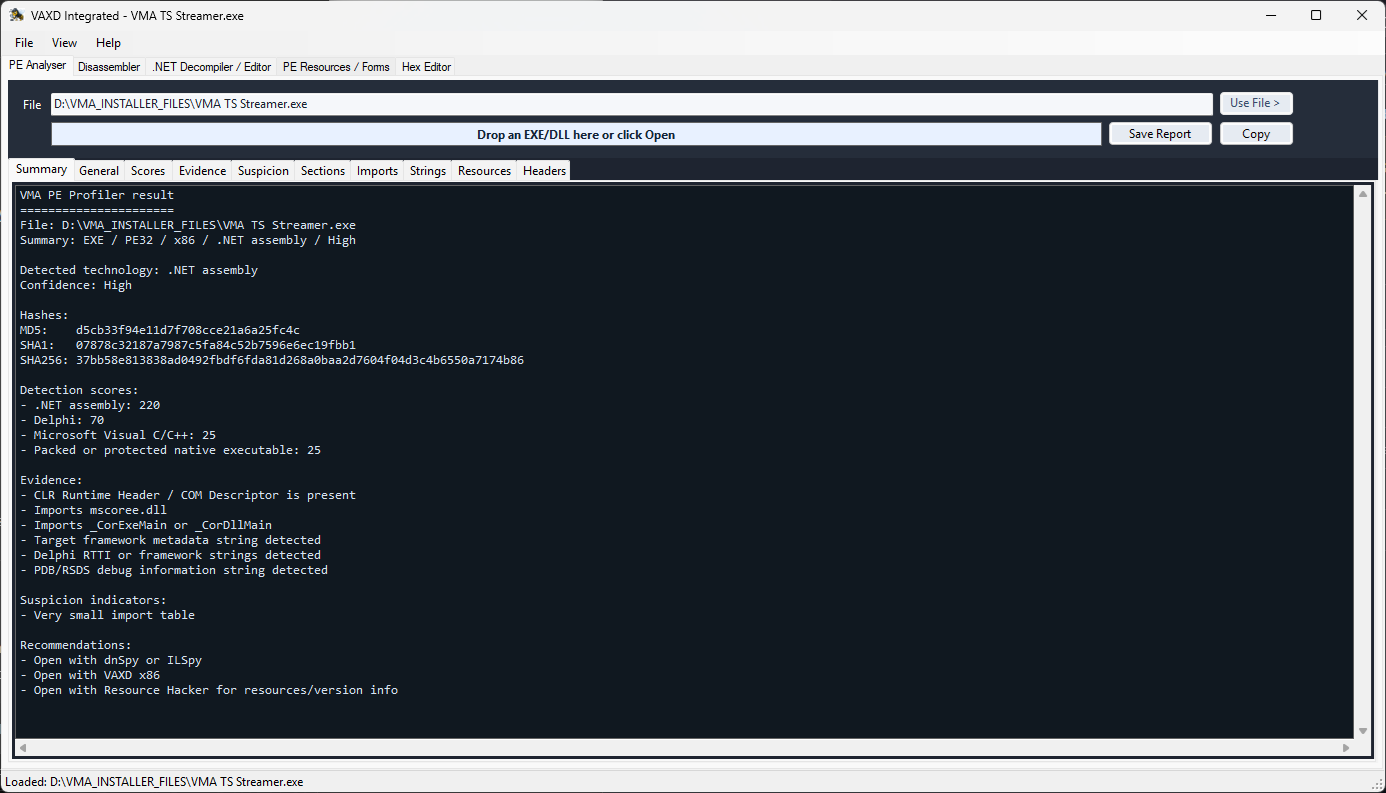 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
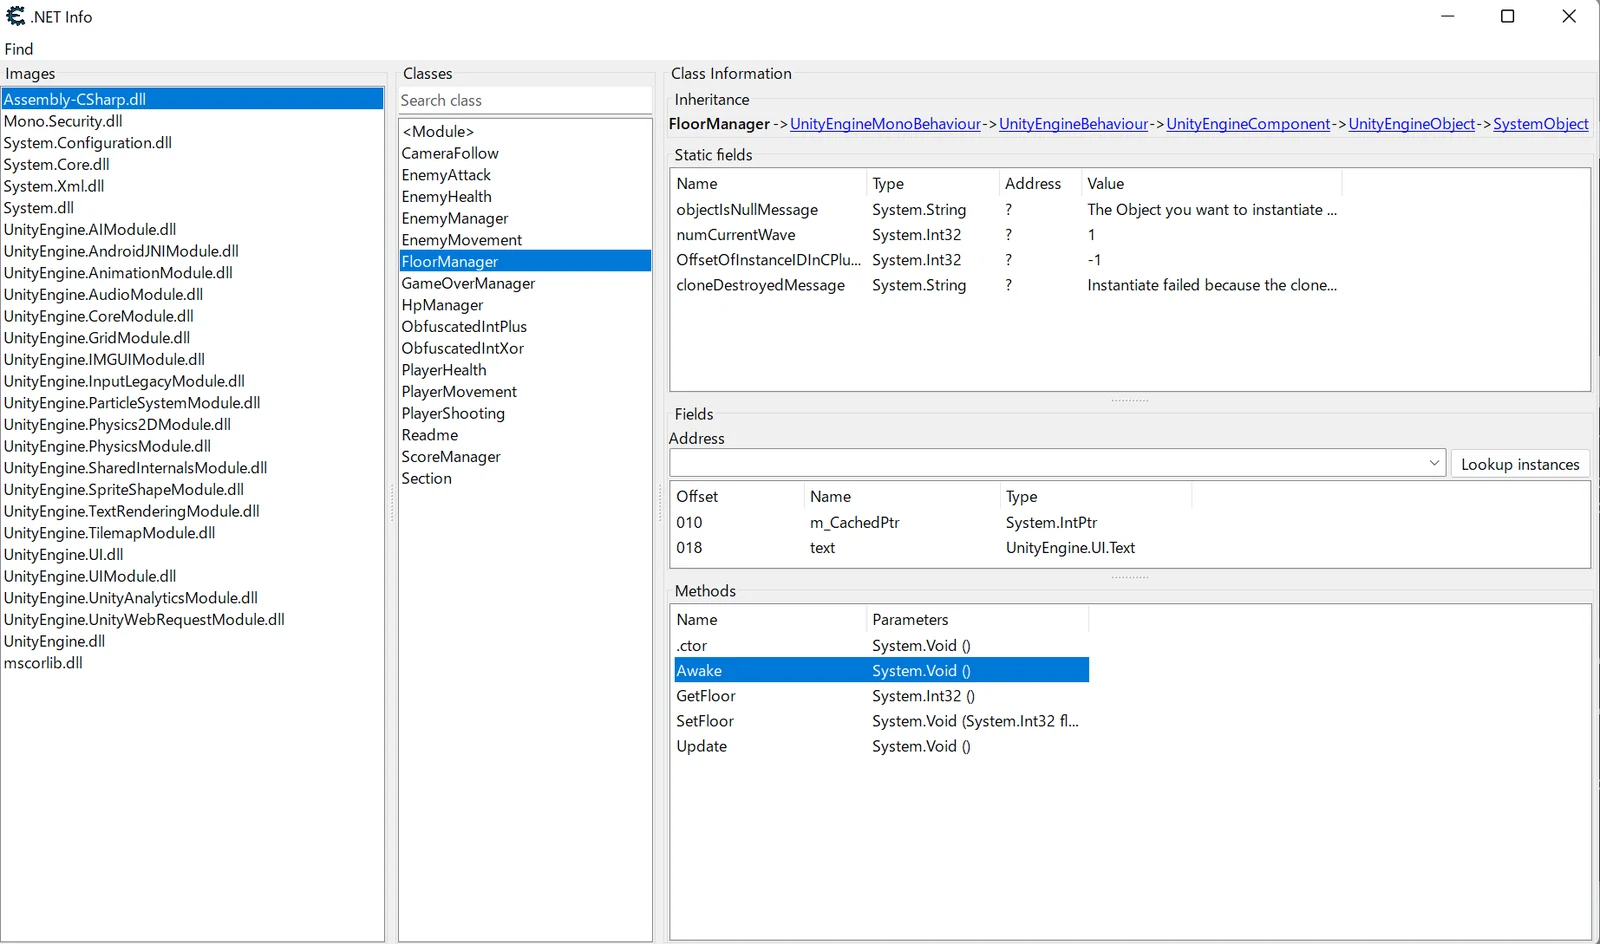 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…