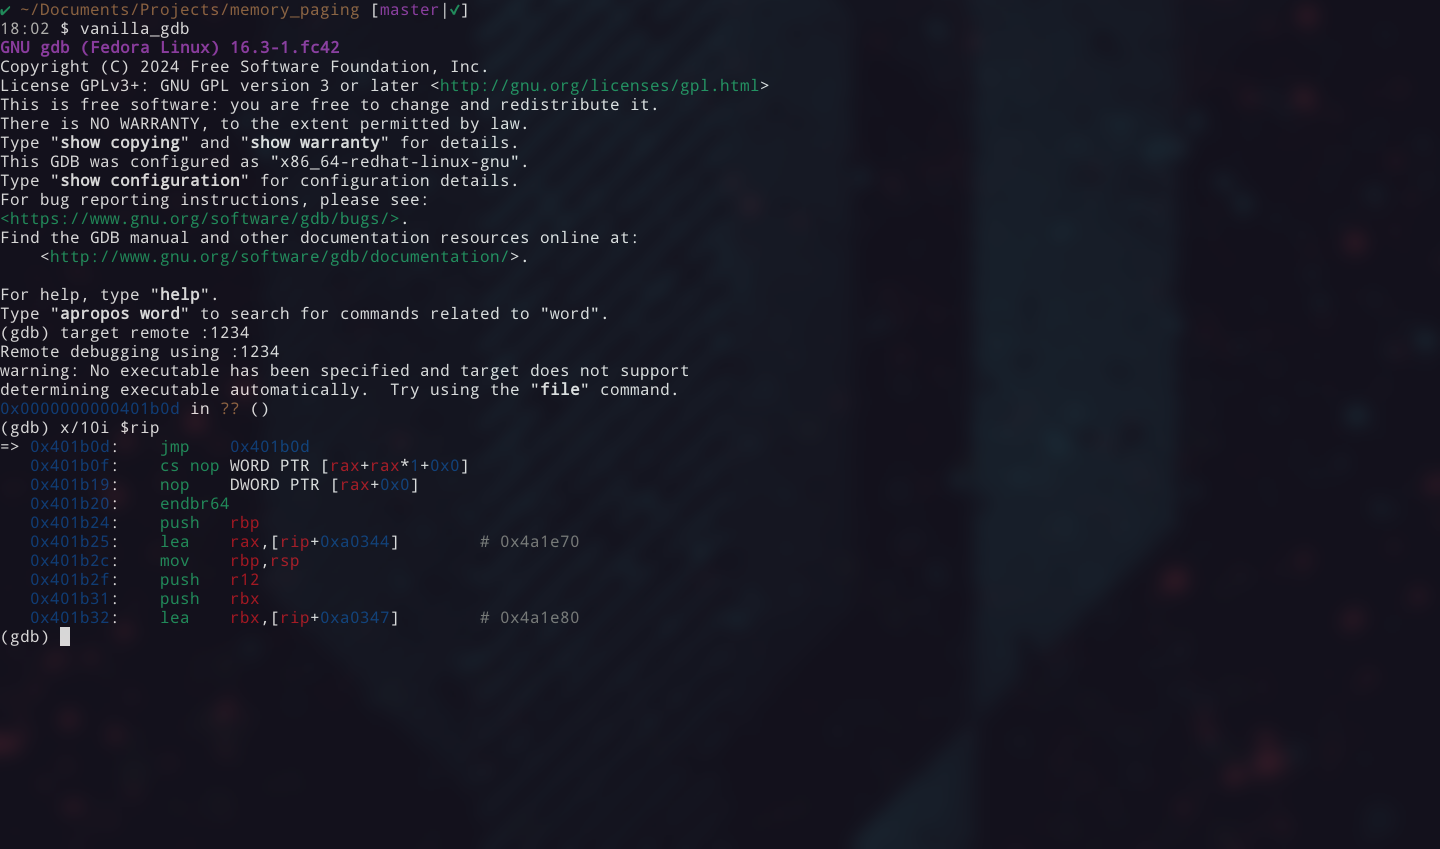
page_table_walk
 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
28
jazho76/page_table_walkWalk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 nowsecure/r2frida
Radare2 and Frida better together.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
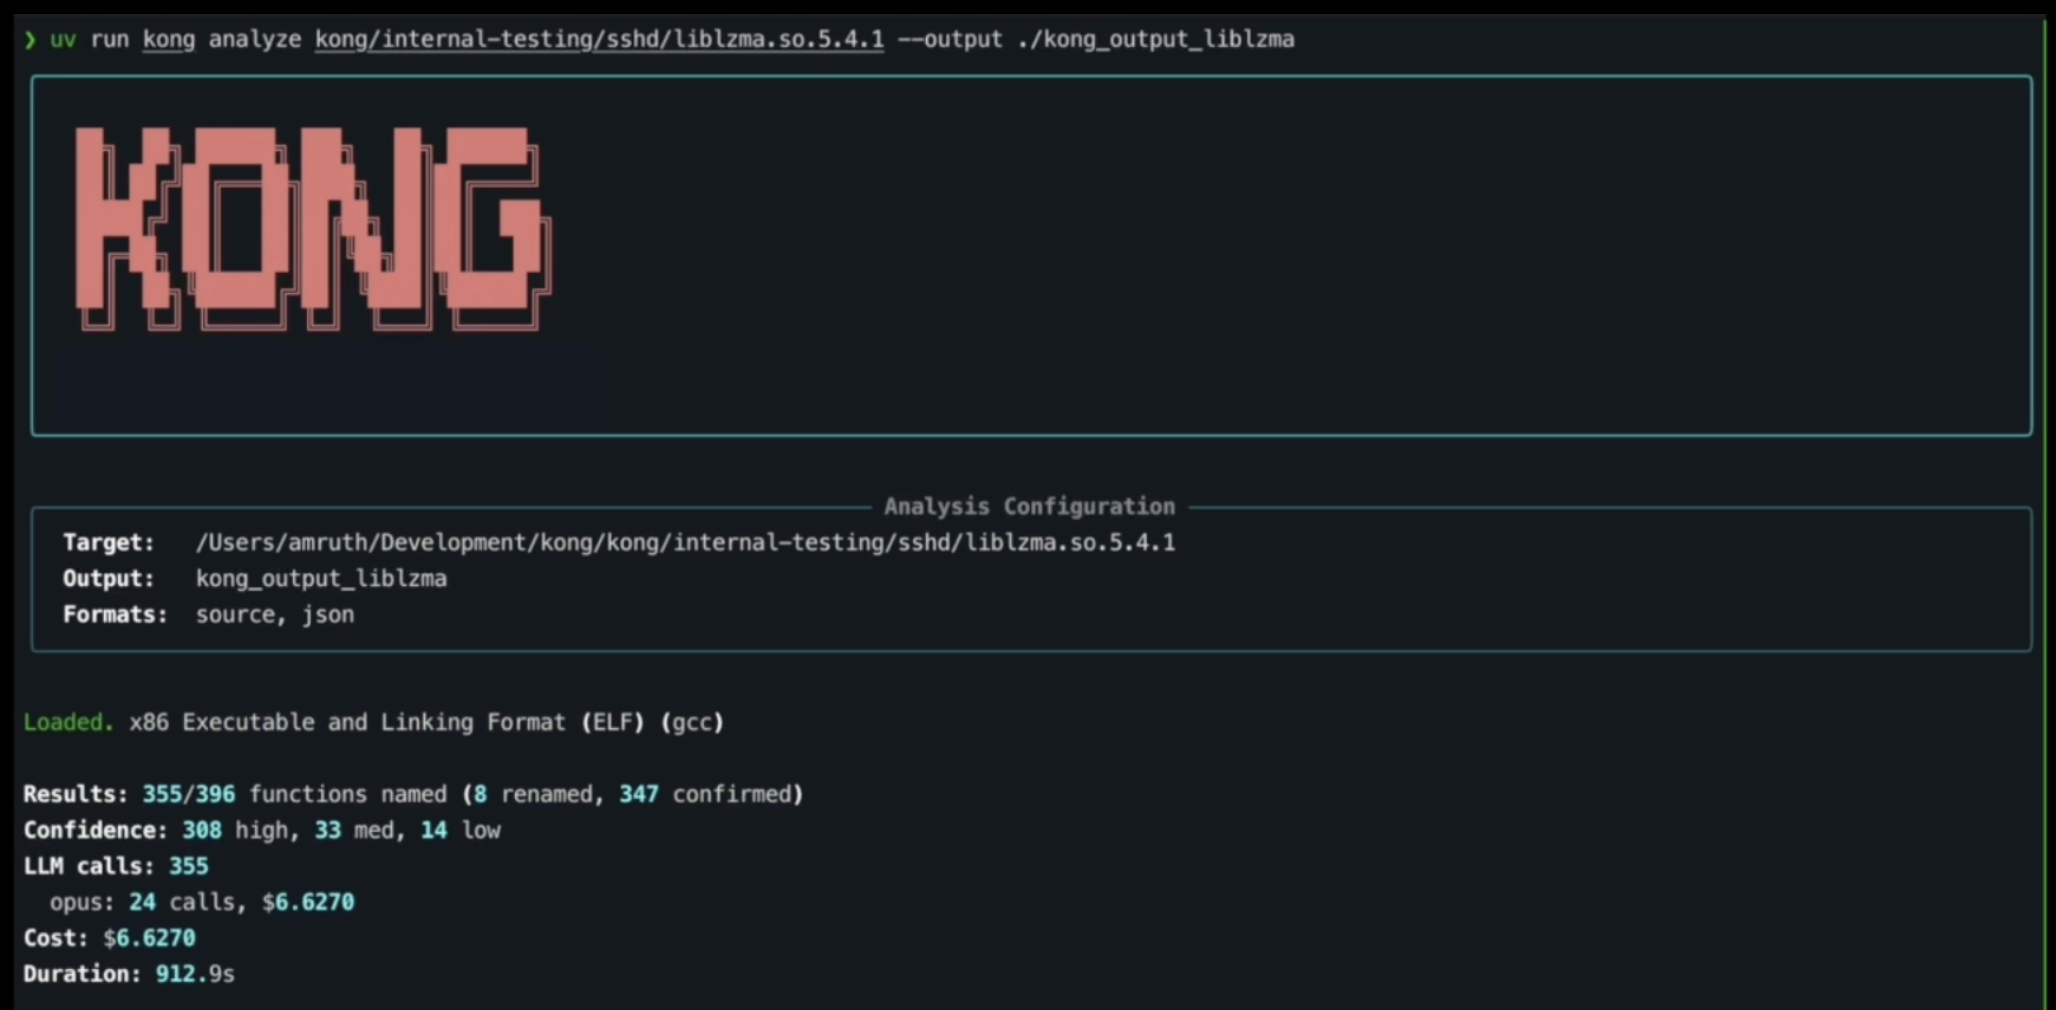 amruth-sn/kong
The world's first agentic reverse engineer.
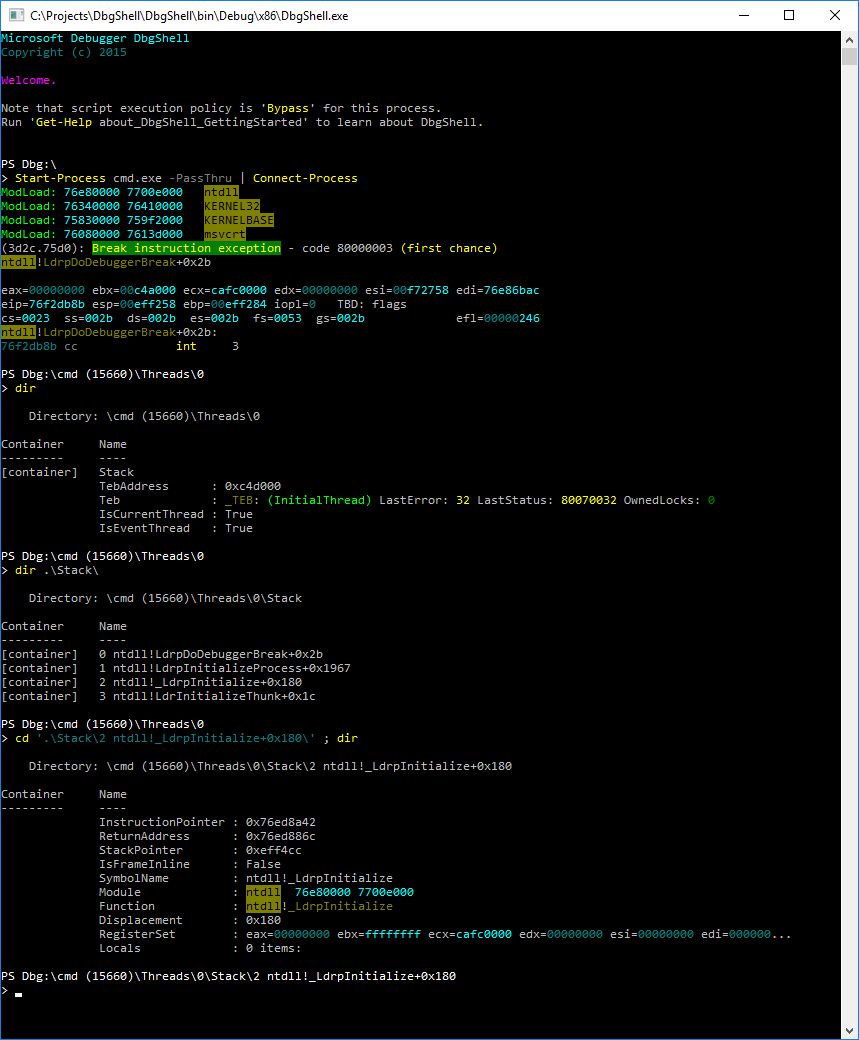 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
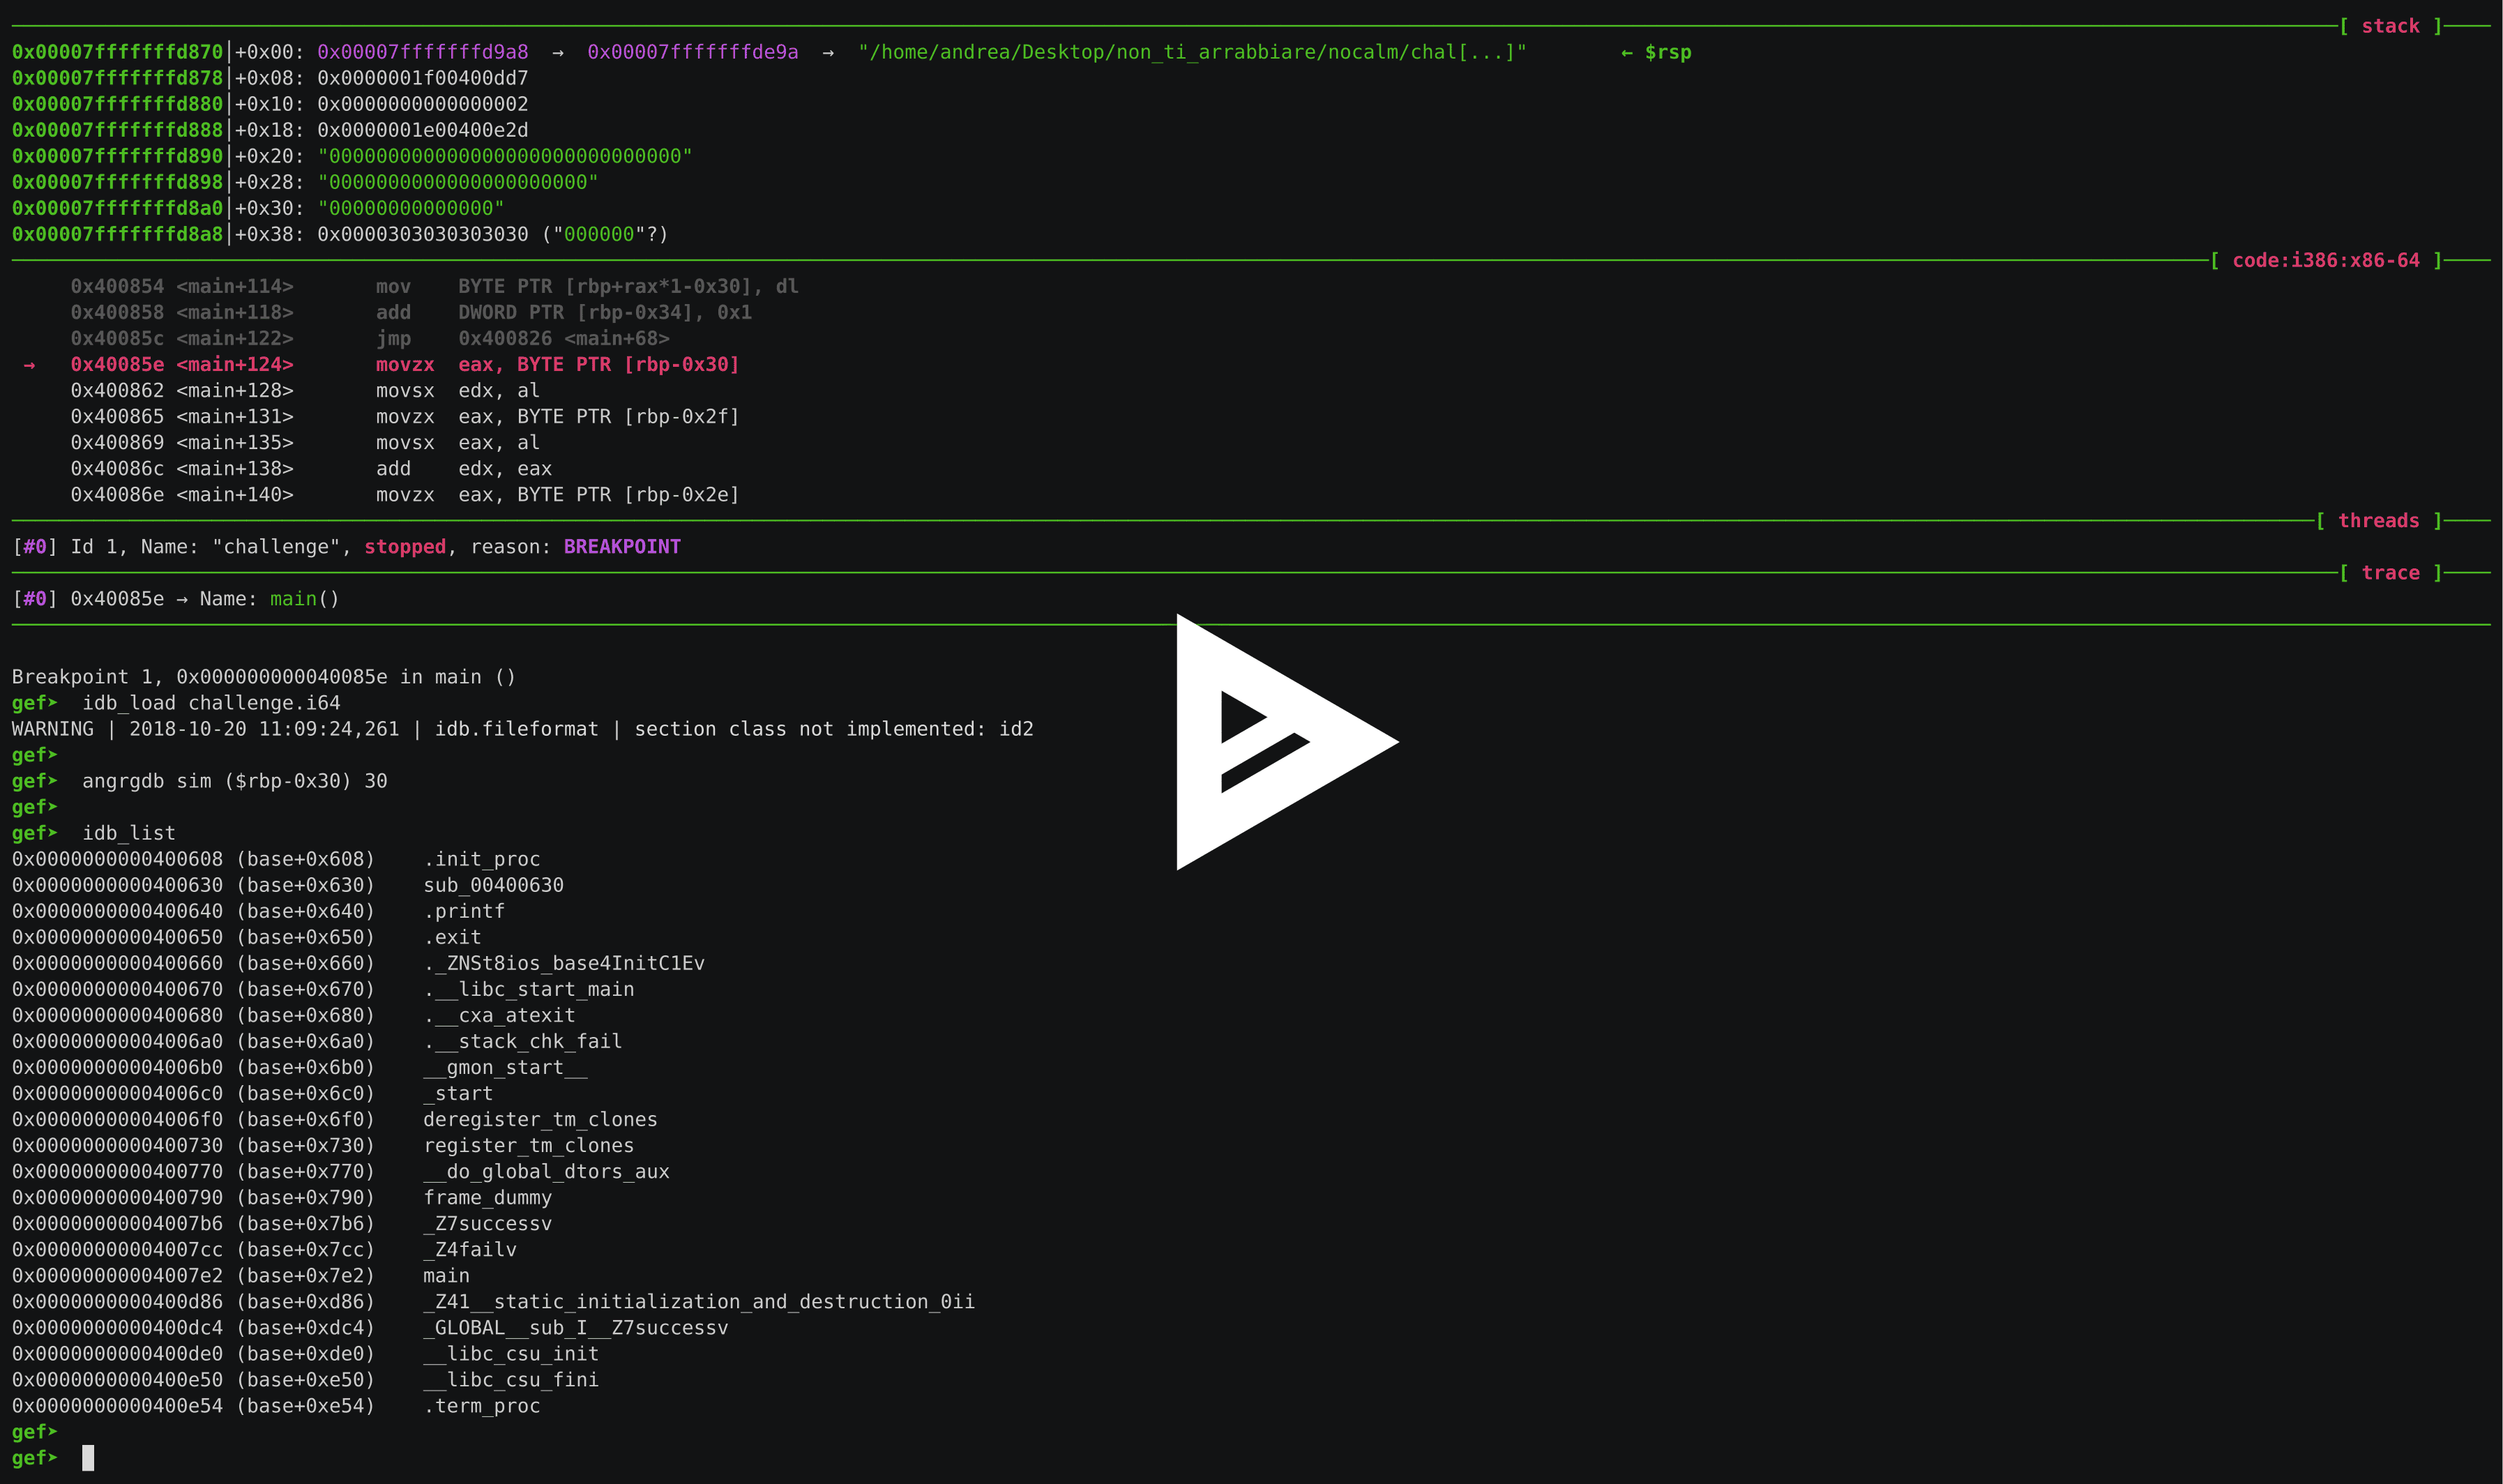 andreafioraldi/angrgdb
Use angr inside GDB. Create an angr state from the current debugger state.
 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 daniellmcguire/xboxseries
Personal research into the Xbox Series Architecture
 nccgroup/iodide
The Cisco IOS Debugger and Integrated Disassembler Environment