

GhidraMCP
 lauriewired/ghidramcp
MCP Server for Ghidra
ai-assisted-reversingbinary-analysiscode-analysis+4
9.7k1 month ago
lauriewired/ghidramcpMCP Server for Ghidra
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 darthton/blackbone
Windows memory hacking library
 momo5502/sogen
🪅 Userspace emulator for Windows, Linux & macOS
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
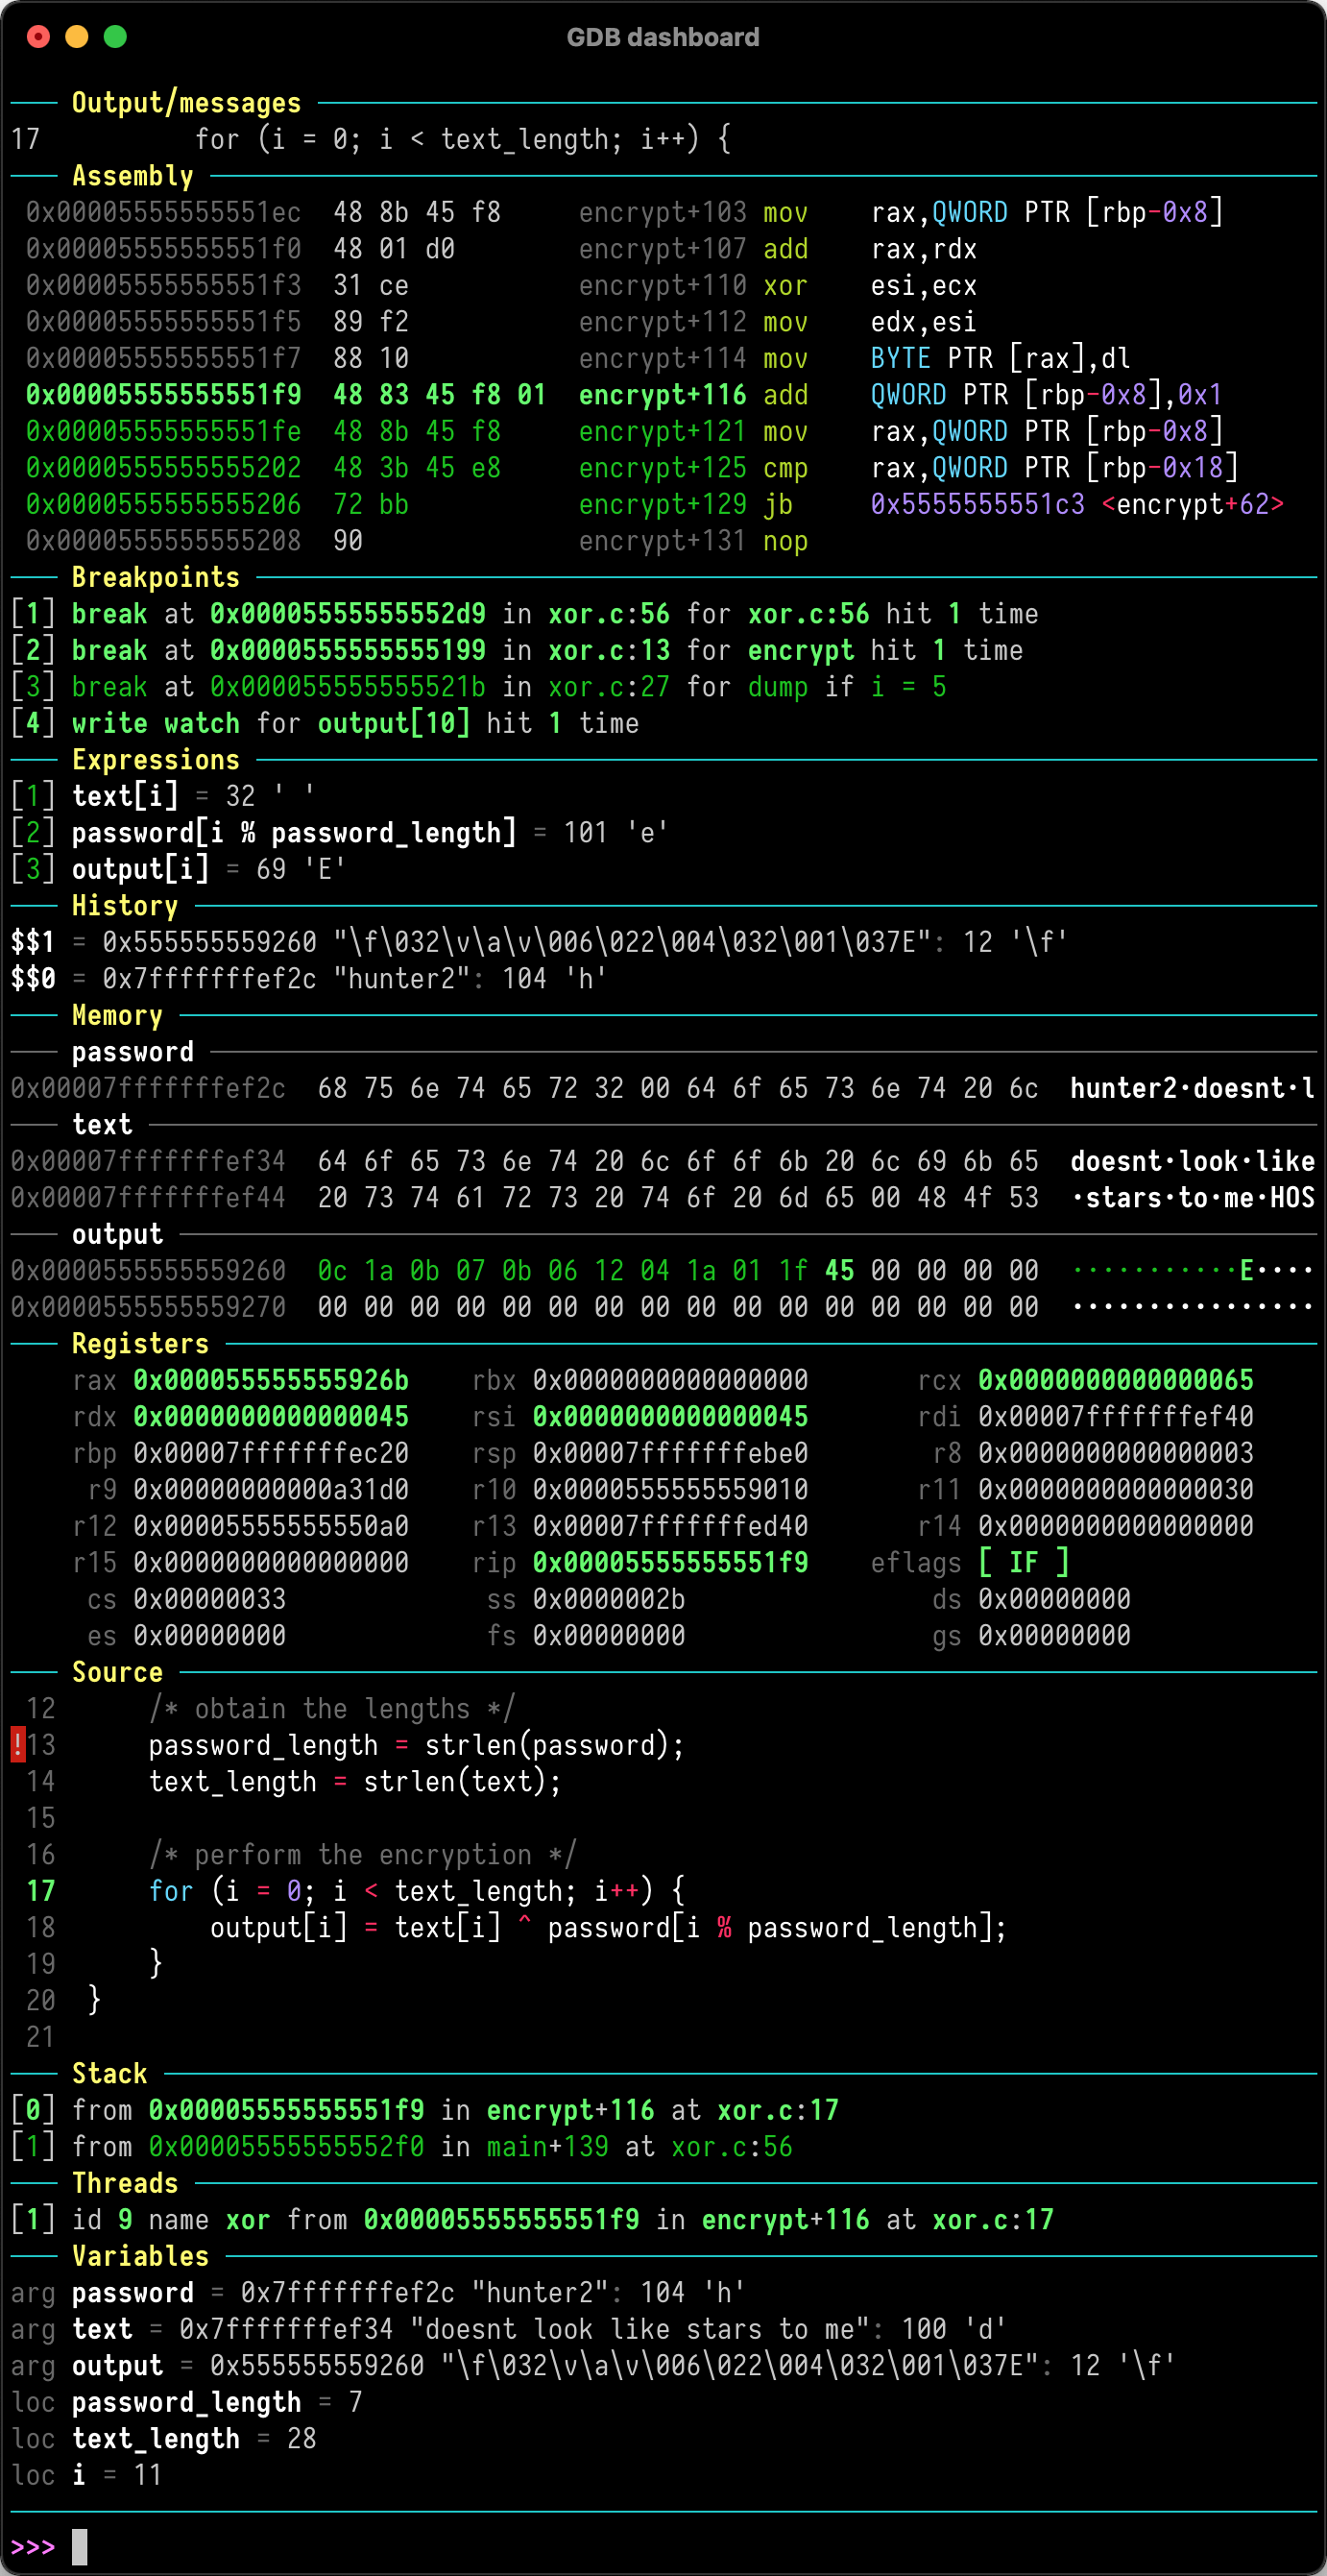 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 cea-sec/miasm
Reverse engineering framework in Python
 morluto/awesome-reverse-engineering
Curated reverse-engineering tools and learning resources for binaries, apps, firmware, formats, and protocols.
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 minglink/dsh-infinite-gen-5
DeepSeek v4.1 flash 最强逆向工具(无限五代) 求 Star 收藏 ⭐欢迎大家提交项目的改进